
 #1
Hardware security modules, TPM, secure enclave, and hardware trust tools.
Kitploit recommended
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
 a13xp0p0v/kernel-hardening-checker
A tool for checking the security hardening options of the Linux kernel
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 theldus/bread
Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
 bishopfox/mellon
OSDP attack tool (and the Elvish word for friend)
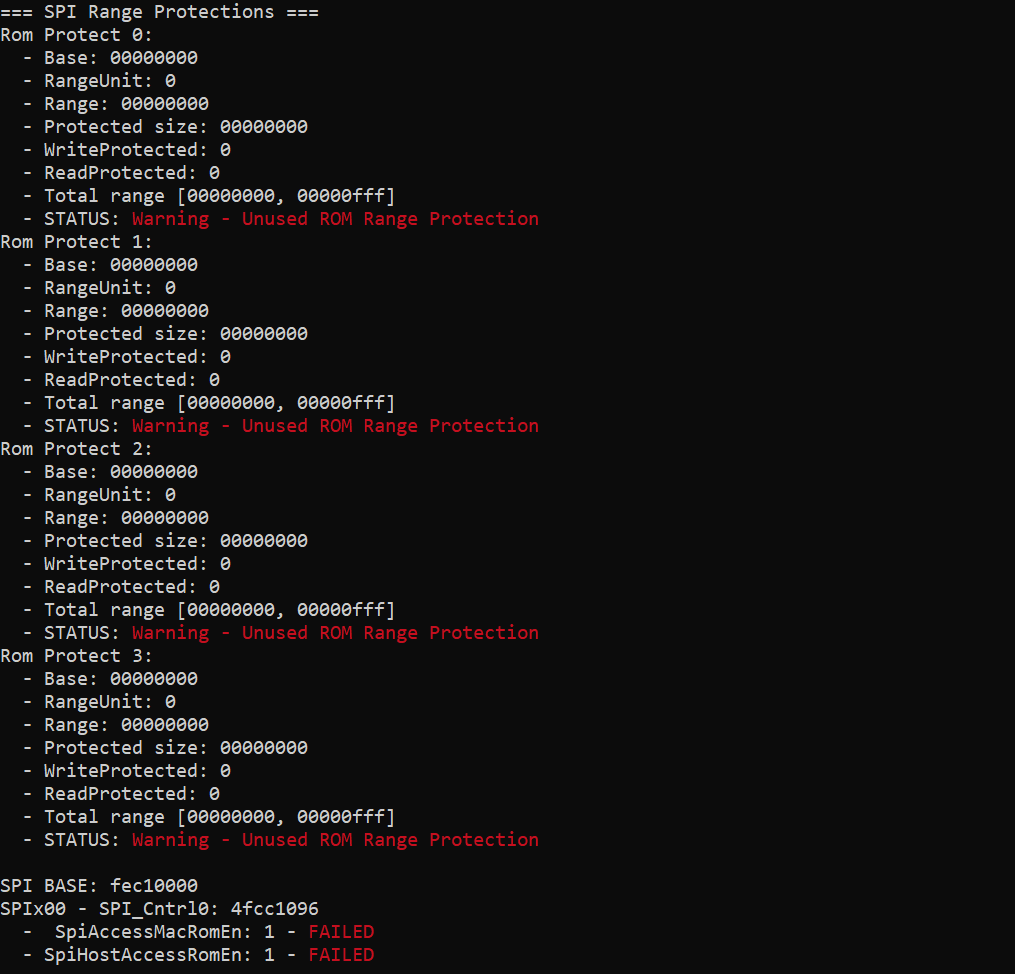 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 nonamecoder/cve-2022-27254
Proof-of-concept demonstrating RF replay attack on Honda's remote keyless entry system (CVE-2022-27254) using HackRF One and GNU Radio for signal…
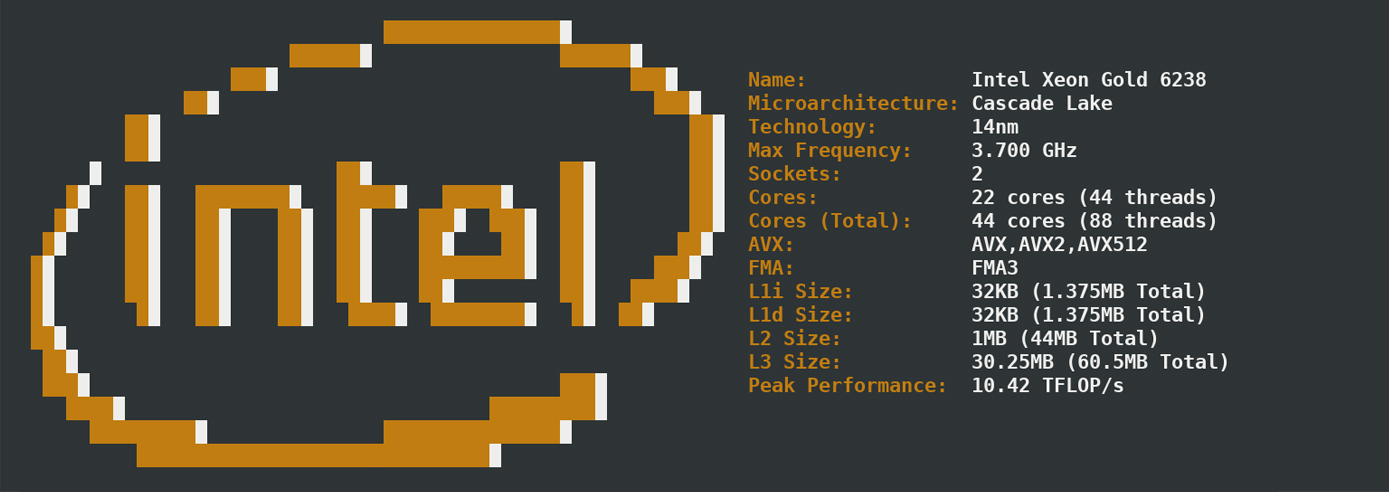 dr-noob/cpufetch
Simple yet fancy CPU architecture fetching tool
 e-m-b-a/emba
EMBA - The firmware security analyzer
 cryptoadvocate/cryptohackfirm
The firmware engineering home of the Cryptohack electronic badge project.
 cryptoadvocate/cryptohackapp
The mobile engineering home of the Cryptohack Badge project.
 cryptoadvocate/dcsgonefwbsp
The firmware board support package home of the Circuit Crafters first electronic badge project.
 cryptoadvocate/dcsgonefirm
The firmware engineering home of the Circuit Crafters first electronic badge project.
 roxanne_ardary/ai-and-the-automobile
Curated collection of open specifications for AI-integrated vehicle systems, covering autonomy, perception, navigation, energy management, safety,…
 cryptoadvocate/dcsgonebadge
The hardware engineering home of the Circuit Crafters first electronic badge project.
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 devnw/zig/hsm
Zig Hardware Security Module library for PIV, CAC, and YubiKey tokens via PC/SC. Supports certificates, PIN management, signing, and decryption.







