
 #1
Hardware security modules, TPM, secure enclave, and hardware trust tools.
Kitploit recommended
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 oneplusoss/android_kernel_modules_and_devicetree_oneplus_sm8550
Low-level kernel modules and device tree source for the OnePlus 11 (sm8550), enabling hardware bring-up, driver analysis, and embedded system…
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 sunnypatell/basalt
World's first hazard checker for NVIDIA Blackwell (sm_120), with an assembler and scheduler matched against their own compiler byte for byte. The…

 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 ioallocate/immapper
Demonstration of Abusing the Vulnerable driver AmdTools64.sys for Physical R/W.
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 e-m-b-a/emba
EMBA - The firmware security analyzer
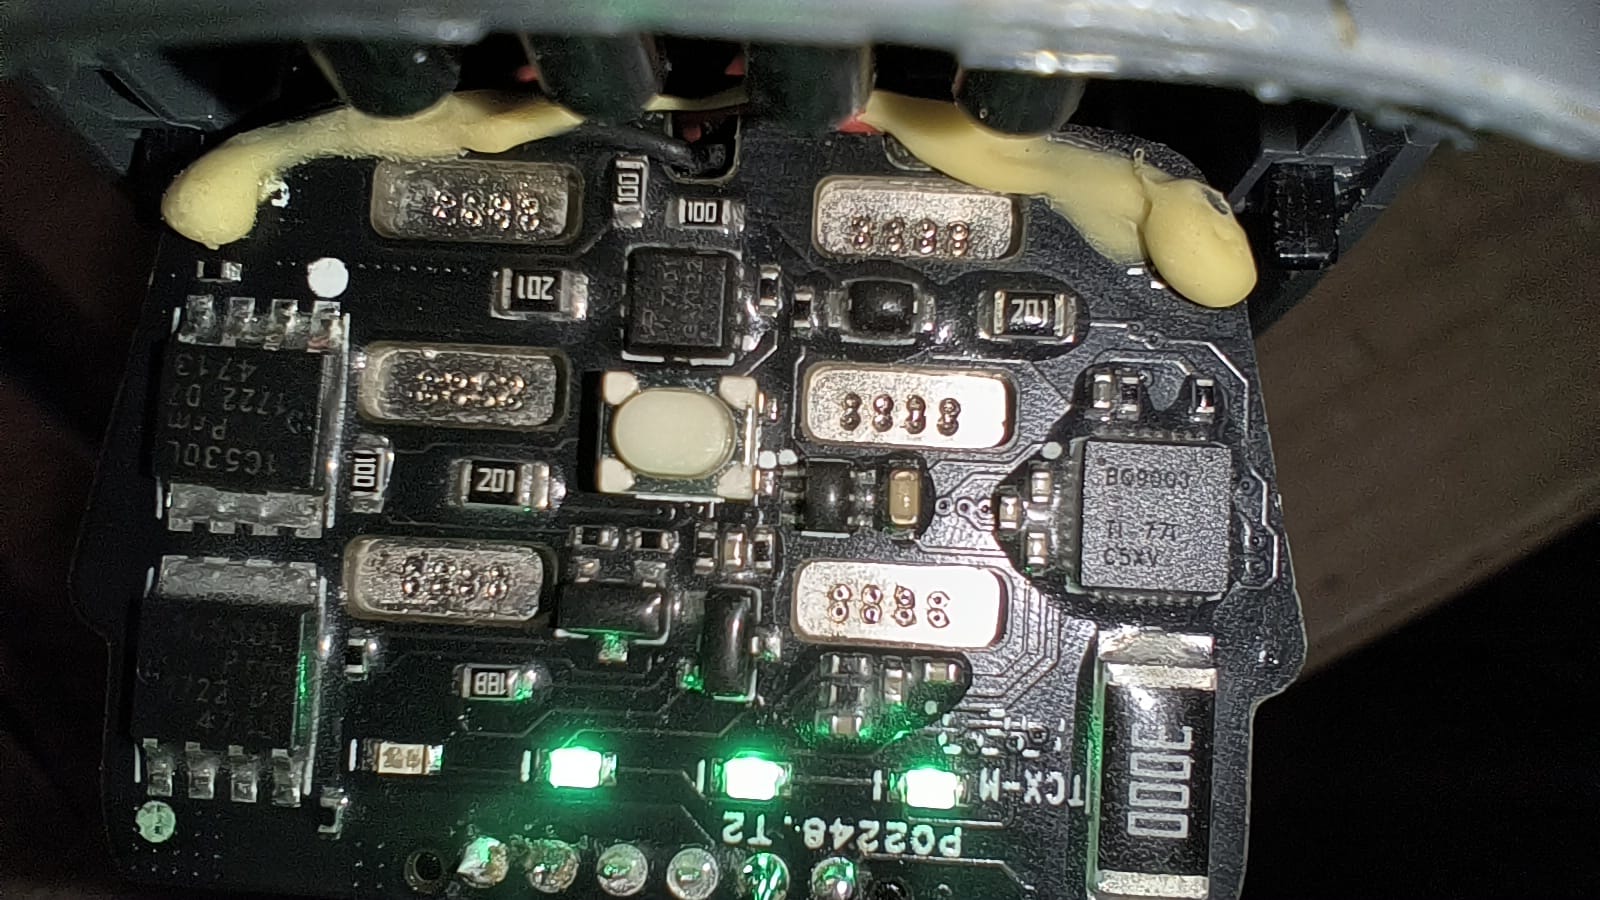 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.





