
 #1
Tools for assessing the security of physical hardware, embedded systems, and IoT devices.
Kitploit recommended

 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 aengussong/hikvision_probe
Identify hikvision ip and probe for cve-s (CVE-2017-7921, CVE-2022-28171, CVE-2021-36260)
 astrowmist/poc-cve-2012-1831
Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability
 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 theos/sdks
Patched sdks that include private framework tbds
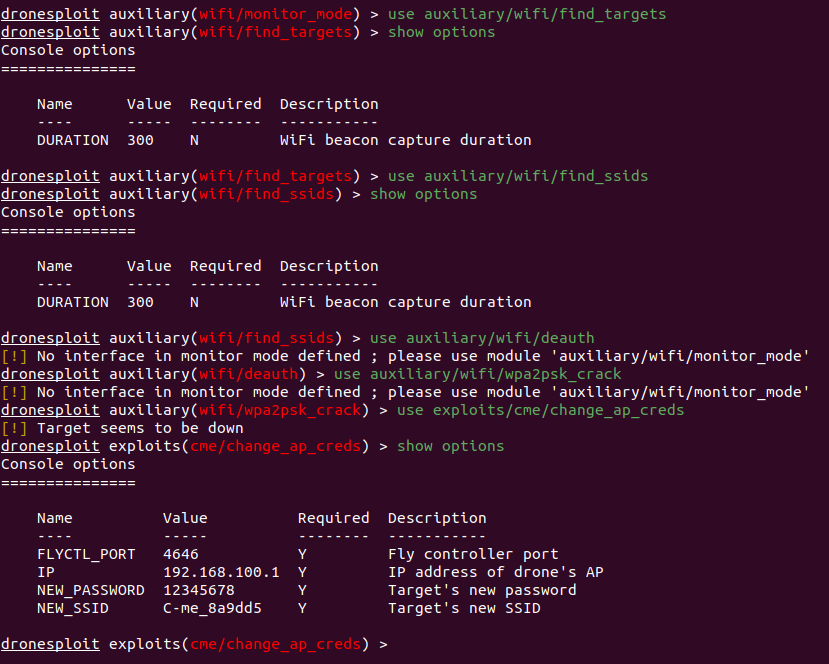 dronesploit/dronesploit
Metasploit-style console framework for pentesting commercial drones, featuring modular exploits for wireless attacks, SSID/password manipulation, and…
 lukejenkins/cve-2022-24693
Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
 bu0ucat/d-link-nas-cve-2024-10914-
这是一个D-Link rce漏洞 检测程序
 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383
 jimilinuxguy/customer-assistance-buttons-sdr
This repository houses the work that ive put into reversing the various encoders and protocols used for customer service buttons in retail shops such…
 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 ospg/binwalk
Firmware Analysis Tool
 uthrasri/cve-2021-21401_nanopb-c_aosp10_r33
Lightweight Protocol Buffers implementation in ANSI C for microcontrollers and memory-restricted embedded systems, enabling efficient serialization…
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
 dhammerg/cve-2023-33669
Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.

 ps5dev/byepervisor
A PS5 hypervisor exploit for 1.xx-2xx firmwares.








