
 #1
Hardware hacking, modding, JTAG, UART, SPI, and embedded device exploitation tools.
Kitploit recommended
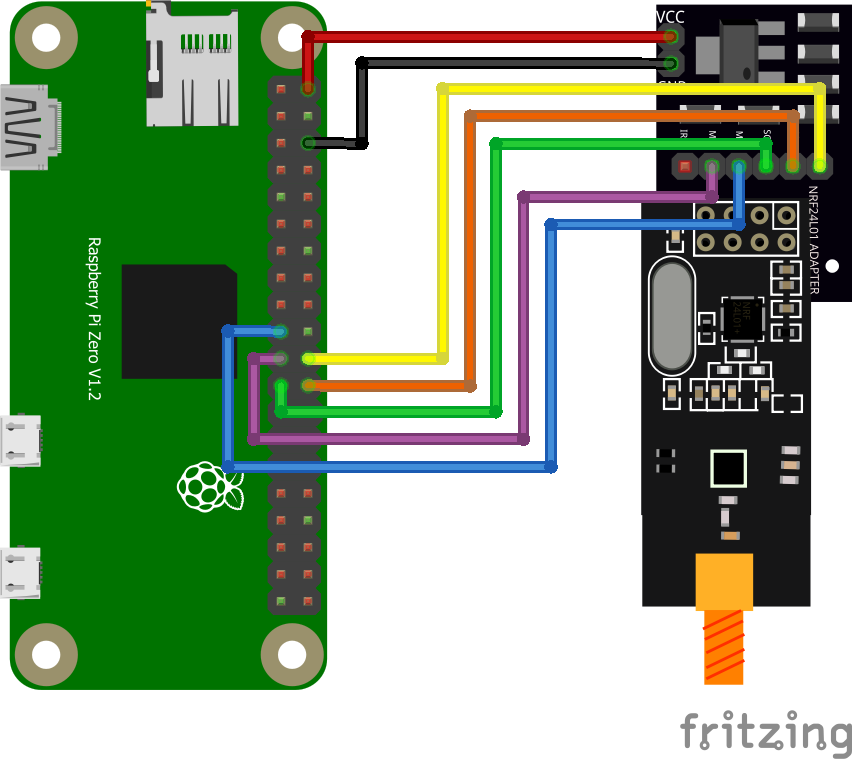
 b1narygl1tch/zerojack
A tool for performing MouseJack keystrokes injection attack.
 esperto-input/esperto-wiimote
Advanced Wiimote remapping software
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 tonixtoolkitofficial-afk/esp32-blue-ducky
ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.
 owasp/robotics-security-testing-guide
OWASP guide defining a standardized penetration testing methodology for humanoid, industrial, and autonomous robots, covering ROS/ROS2, DDS, CAN bus,…
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
 xun404/spd_dump-macos
UNISOC BootROM/FDL flasher for macOS: patched spd_dump with CVE-2022-38694 exec_addr2, protocol reference, partition rules, backup verification…
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 xsanflip/dangdut
Passive wireless intrusion detection system for ESP32-S3 and Flipper Zero that detects Wi-Fi deauthentication and disassociation attacks in real…
 sunrayvision/vision-msi-thermal-control
MSI Modern 15H AI C1MGT-096IT Linux thermal management - Reverse engineered EC control with fan profiles and battery threshold
 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 infobyte/symax5sw-rx-tx
Syma X5SW Telemetry and Transmissor
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.

 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 drmnsamoliu/cve-2019-17147_practice_material
This repo contains dumped flash partitions with firmware version vulnerable to CVE-2019-17147, and some useful binaries to downgrade and debug your…
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.








