
 #1
Digital forensics, evidence collection, timeline analysis, and incident investigation tools.
Kitploit recommended
 smtimesiwndr/gdid-reversal
Reverse-engineered analysis of Microsoft's Global Device Identifier (GDID) revealing its generation as a server-assigned MSA Device PUID, storage in…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 lazza/recuperabit
A tool for forensic file system reconstruction.
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 ashemery/linuxforensics
Everything related to Linux Forensics

 cristianzsh/forensictools
Collection of forensic tools
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
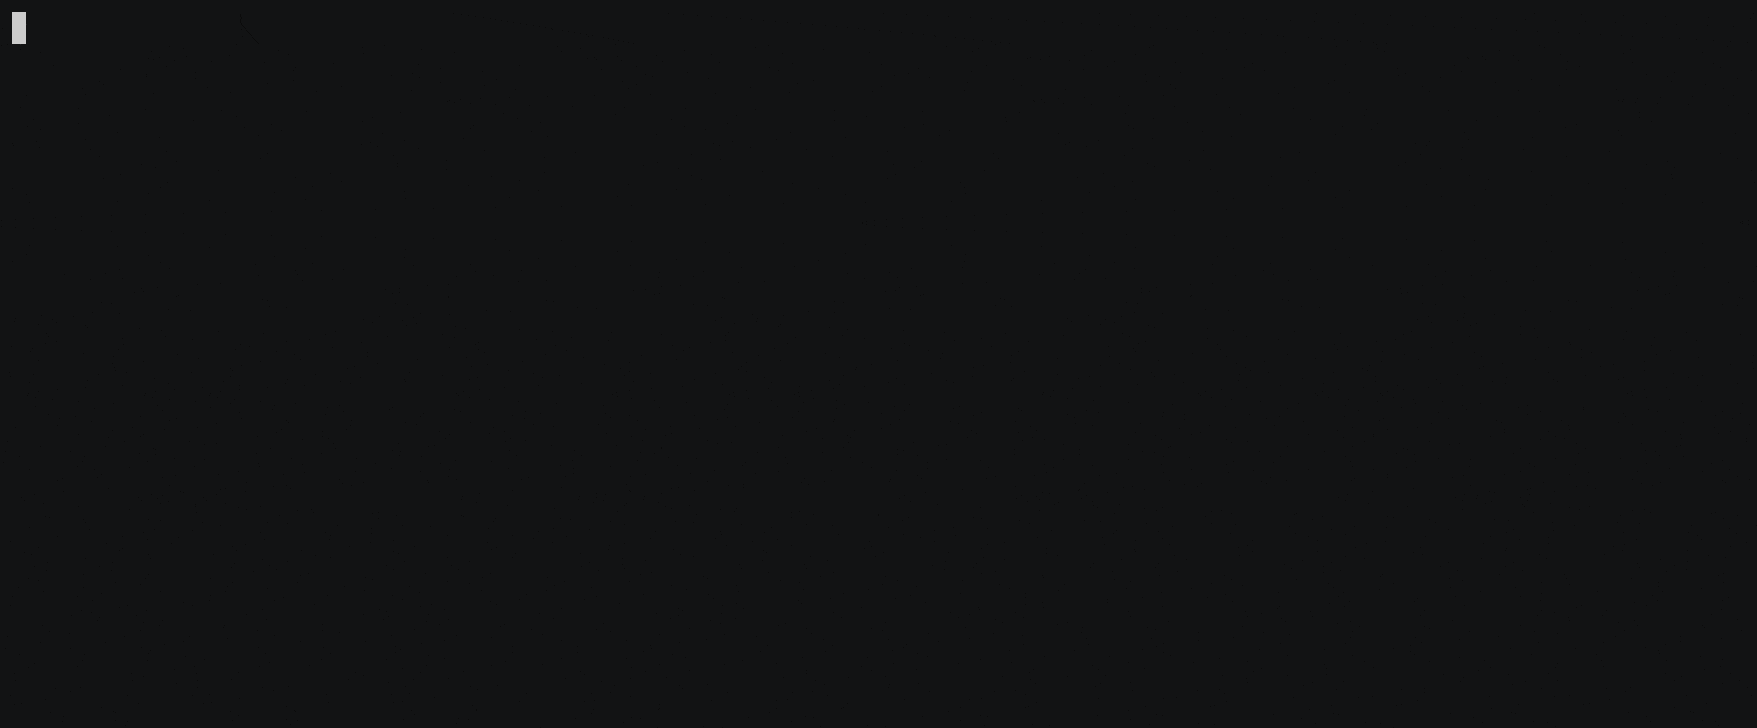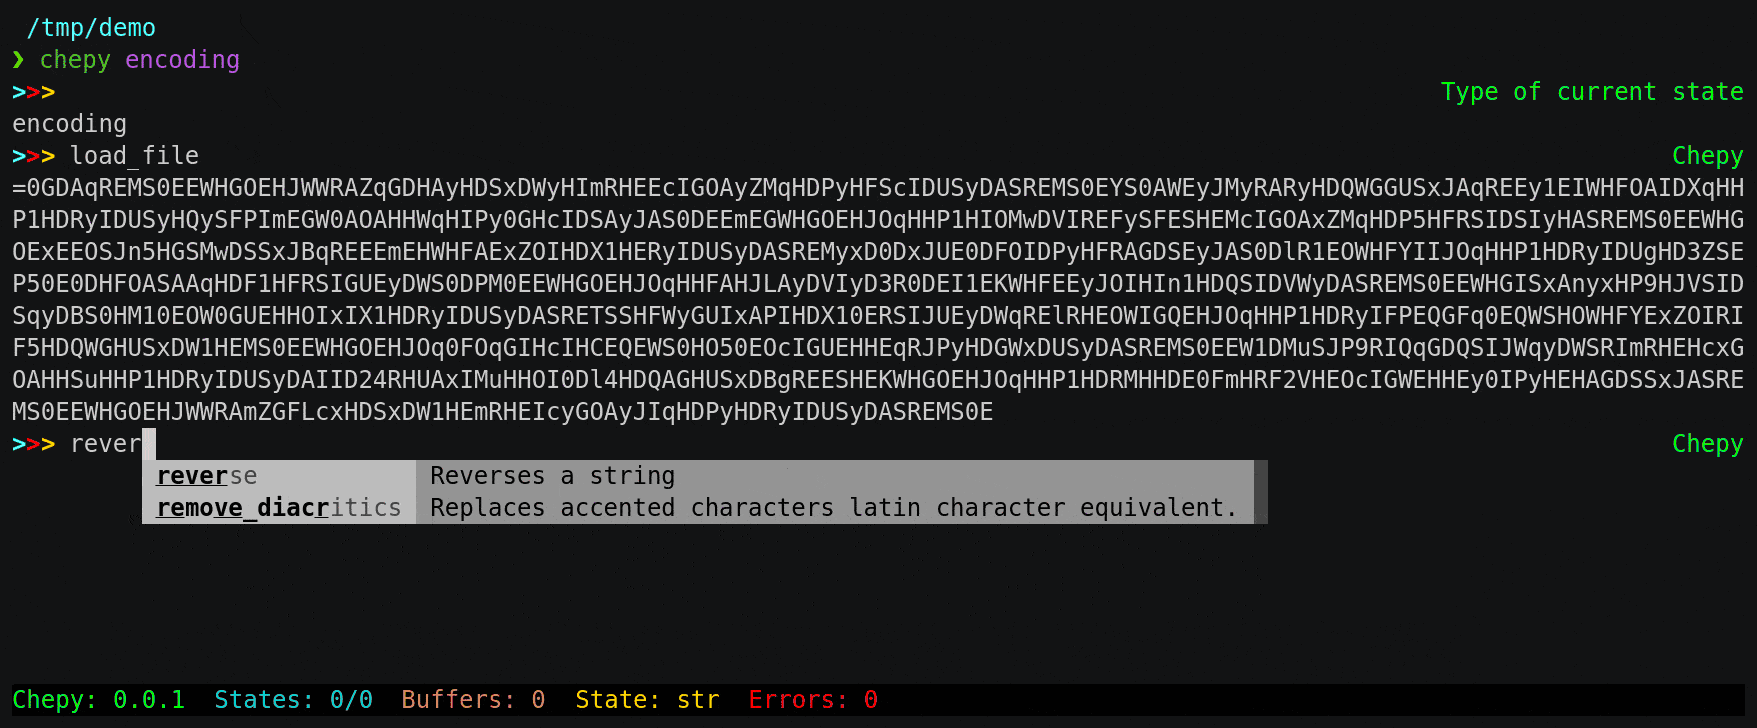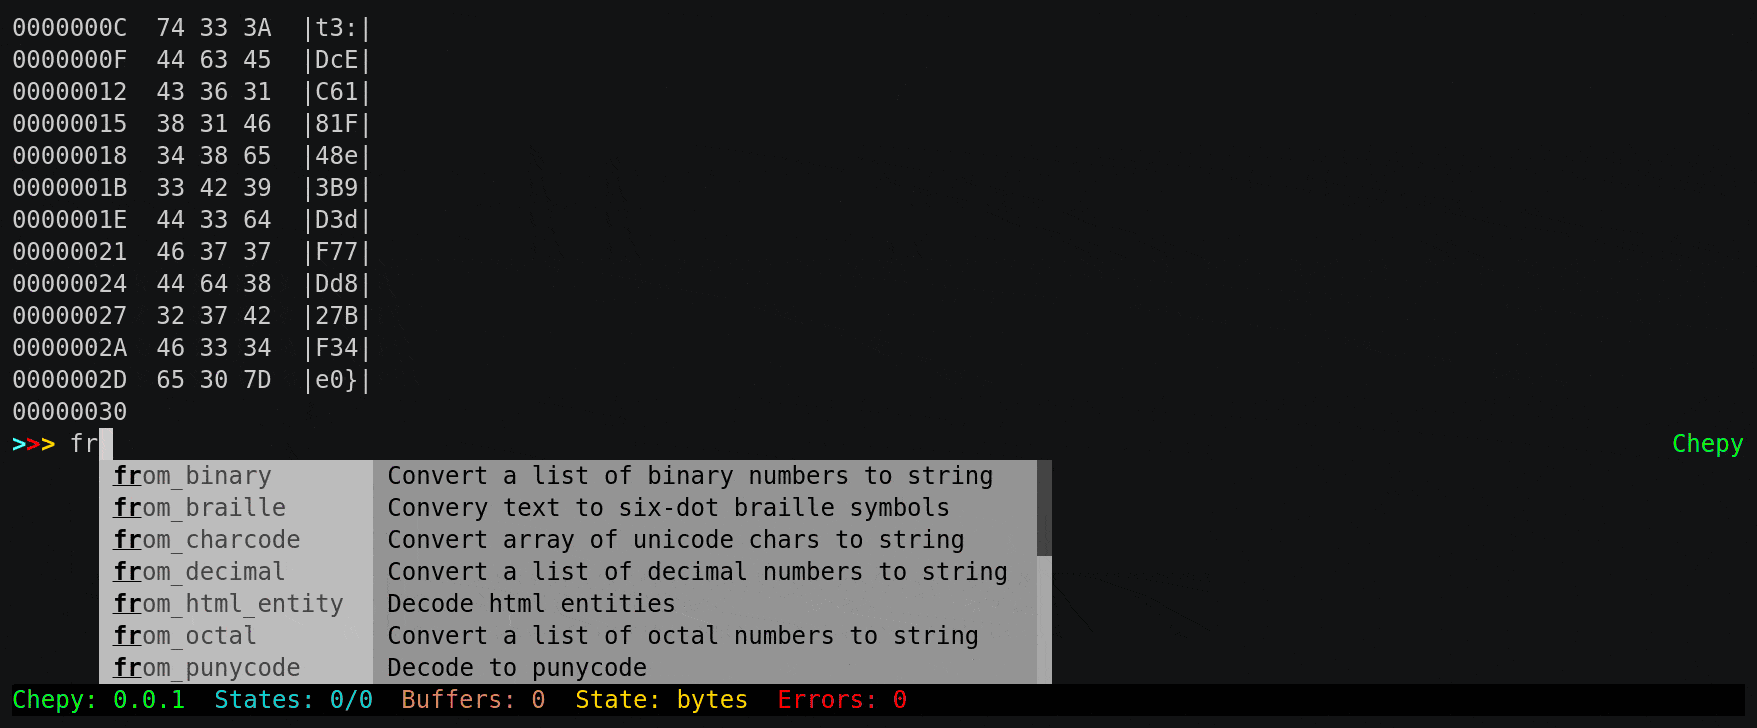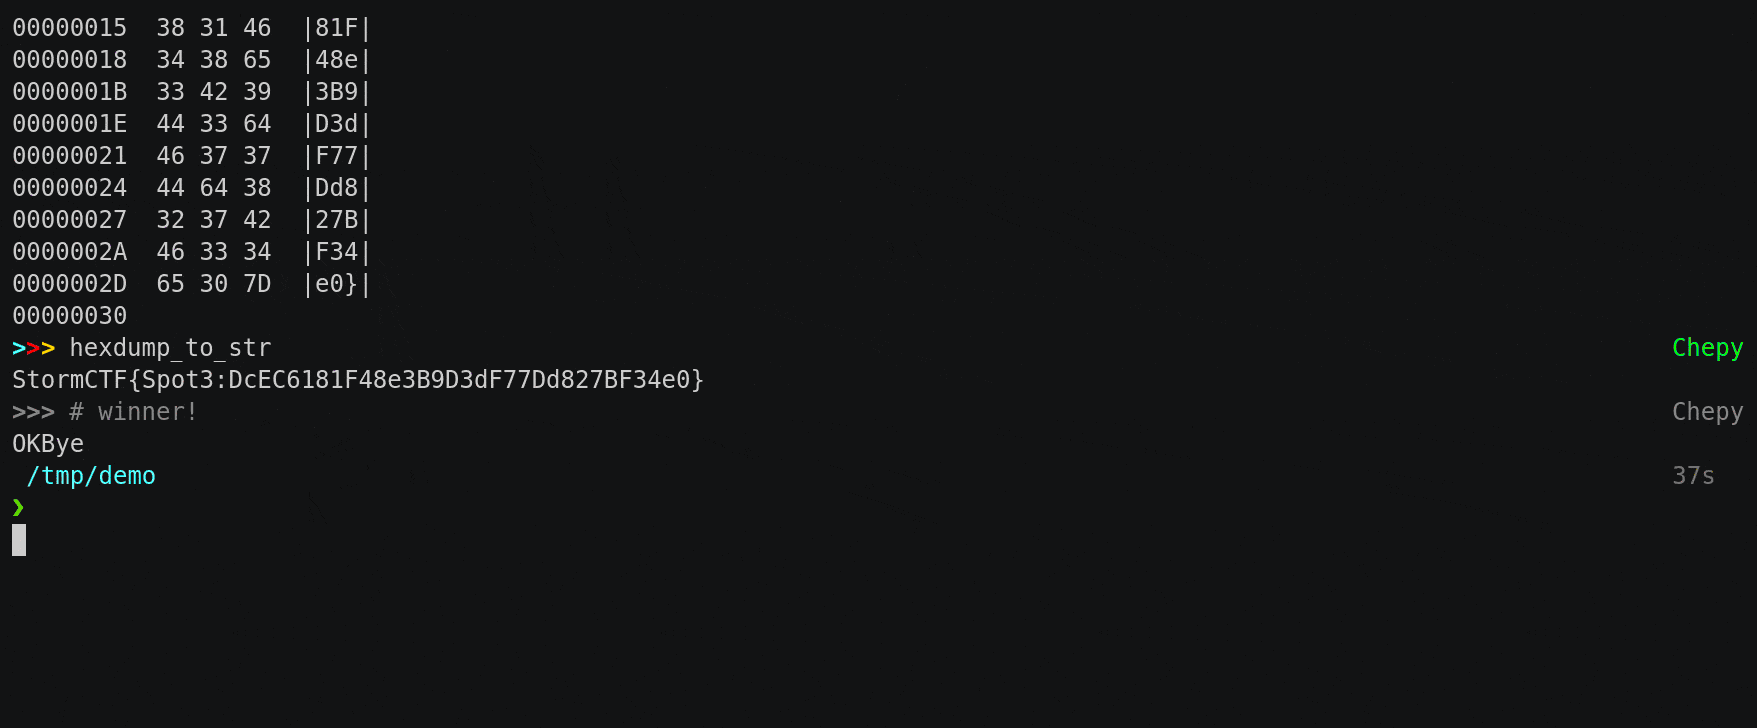 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
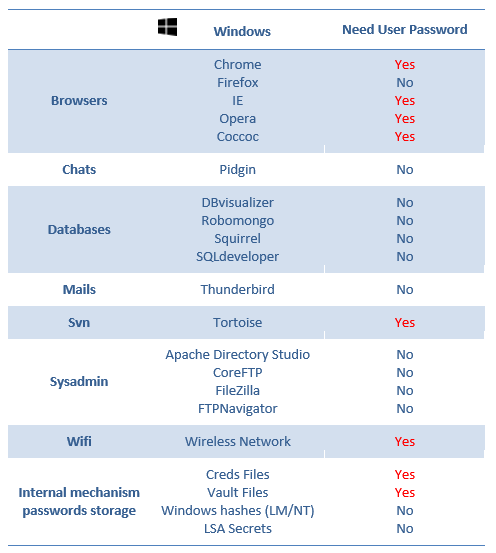 alessandroz/lazagneforensic
Windows passwords decryption from dump files
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 capacitorset/box-js
A tool for studying JavaScript malware.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.








