
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended

 arinerron/cve-2022-0847-dirtypipe-exploit
A root exploit for CVE-2022-0847 (Dirty Pipe)
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 calebstewart/cve-2021-1675
Pure PowerShell implementation of CVE-2021-1675 Print Spooler Local Privilege Escalation (PrintNightmare)
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 1n3/privesc
A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.
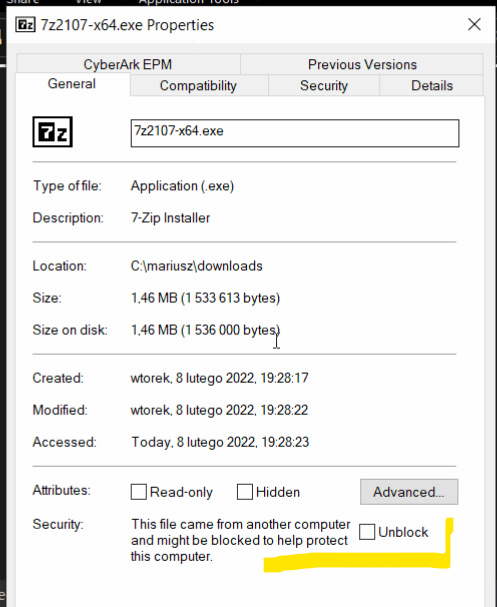 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 github/securitylab
Resources related to GitHub Security Lab








