
 #1
Comprehensive frameworks for exploit development, testing, and execution.
Kitploit recommended
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 nishantiyer/cve-2020-15215-discord-poc
Proof-of-concept validation harness for Electron boundary hardening, modeling renderer/main-process isolation, IPC policy enforcement, and navigation…
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 m-cetin/cve-2023-29336
Proof-of-concept exploit for CVE-2023-29336, a Win32k elevation of privilege vulnerability enabling SYSTEM-level access on affected Windows systems.
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…
 poliva/root-zte-open
exploit for CVE-2012-4220 working on zte-open
 smarttfoxx/copyfail
CVE-2026-31431 (Copy Fail) PoC - Linux kernel page cache corruption via authencesn AF_ALG + splice()
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)
 ma4the/omae-wa-cheese-da
CVE-2025-21479 PoC for ZFlip5 with Knox in the way!(˶˃ ᵕ ˂˶)
 crackercat/cve-2024-35250
PoC for the Untrusted Pointer Dereference in the ks.sys driver
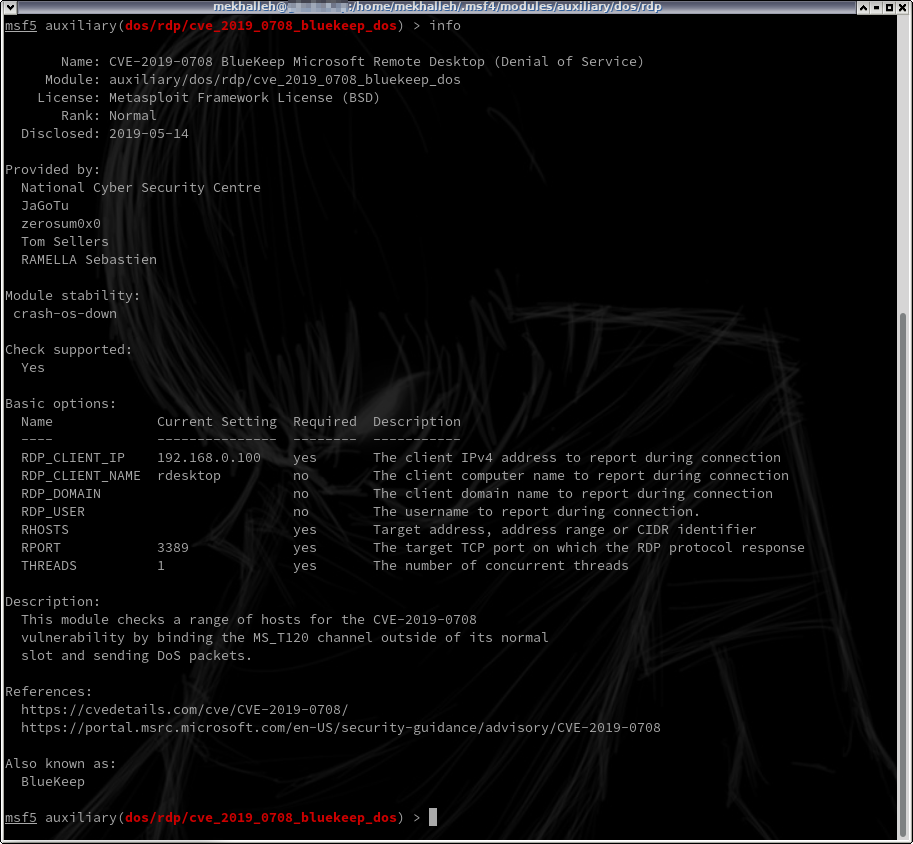 mekhalleh/cve-2019-0708
Metasploit module for massive Denial of Service using #Bluekeep vector.
 darksh3llgr/autoscan
Automated Scanning, Pentesting , Exploiting and Reporting
 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 doyensec/ksmbd-cve-2025-37947
Exploit for CVE-2025-37947 in ksmbd, a Linux kernel SMB server, causing an out-of-bounds write. Includes BPF tracer, QEMU setup, and minimal PoC…
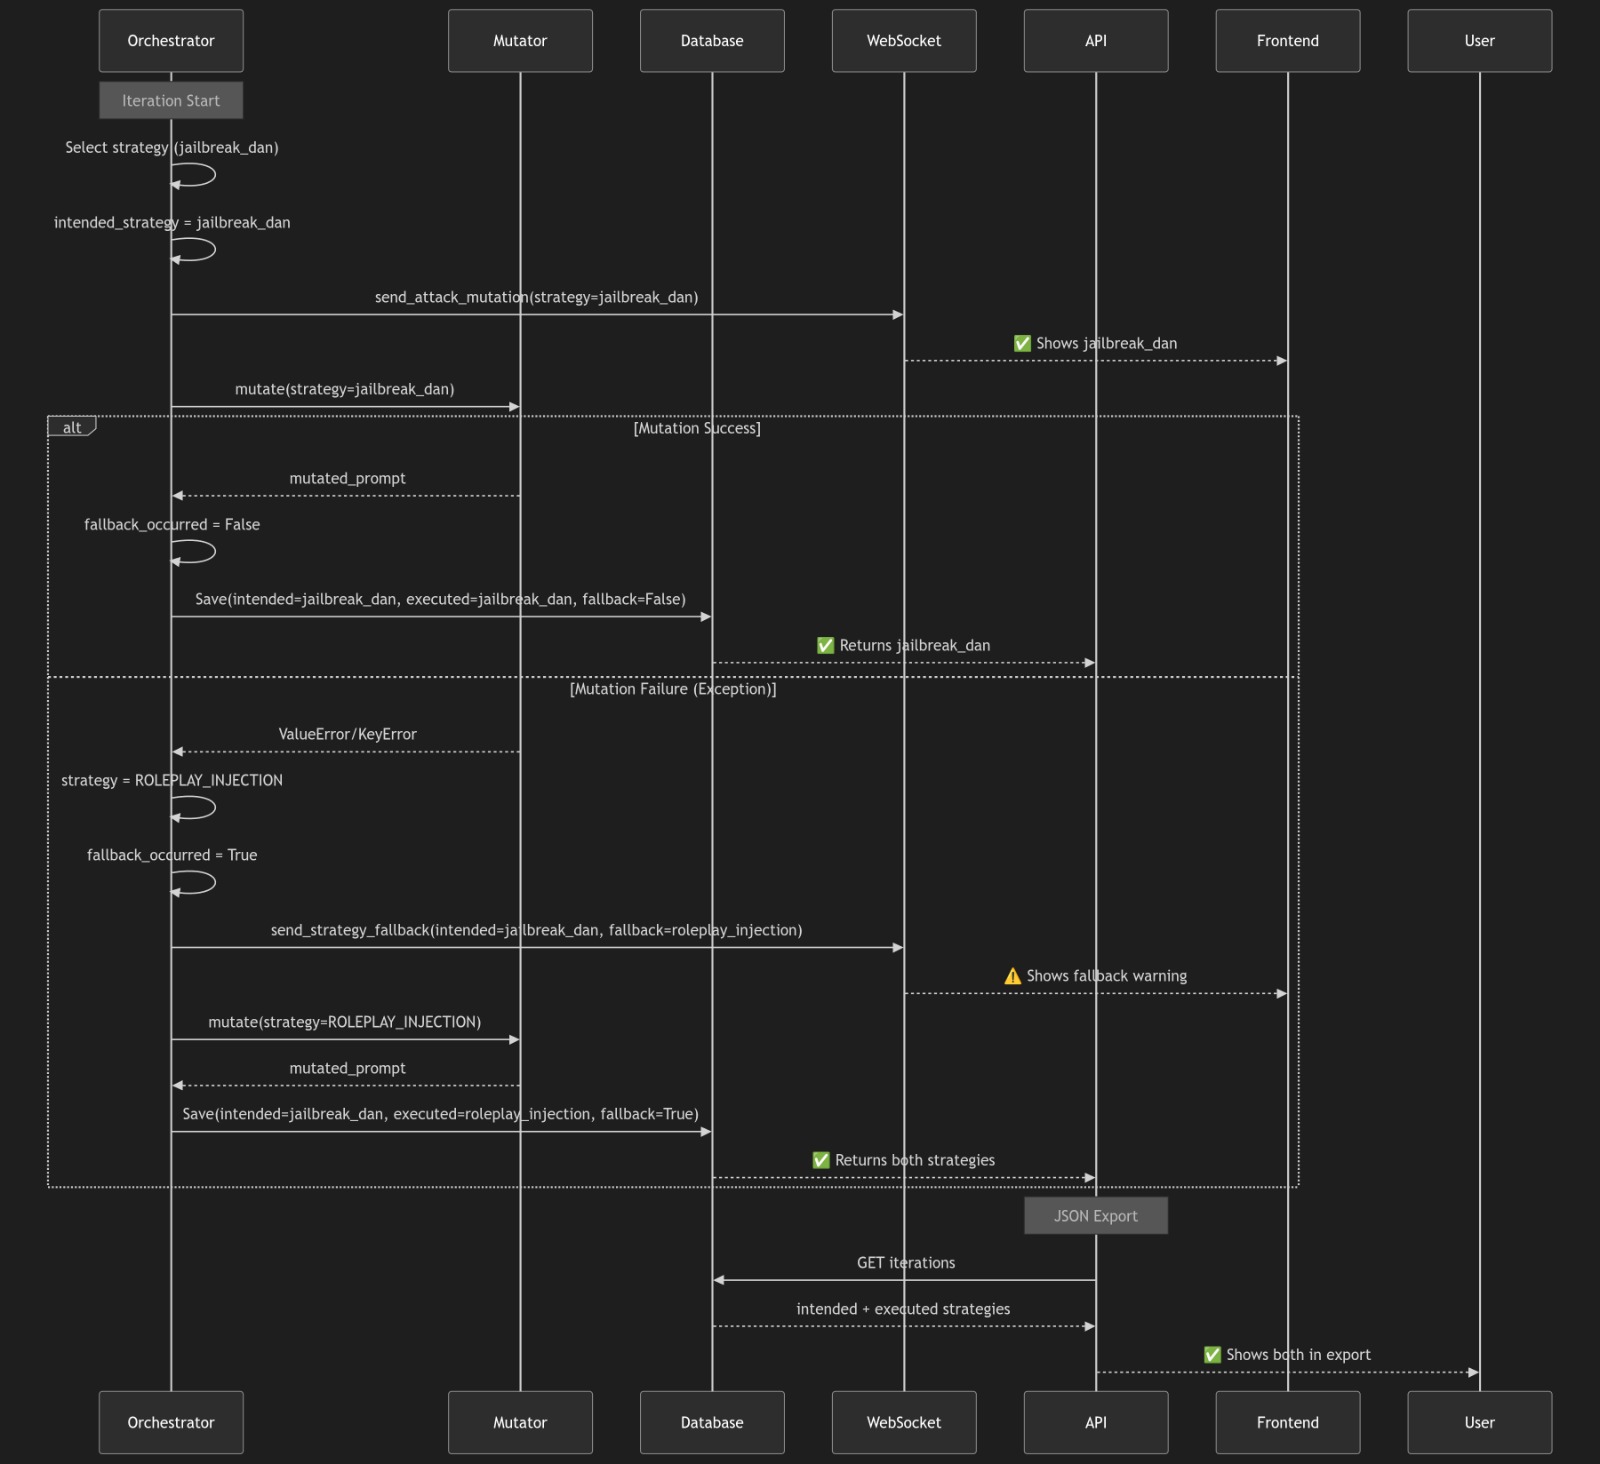 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 expliot-framework/expliot
Read only mirror - No pull requests








