#1
Email filtering, DKIM/DMARC/SPF, anti-spam, phishing detection, and email gateway tools.
Kitploit recommended
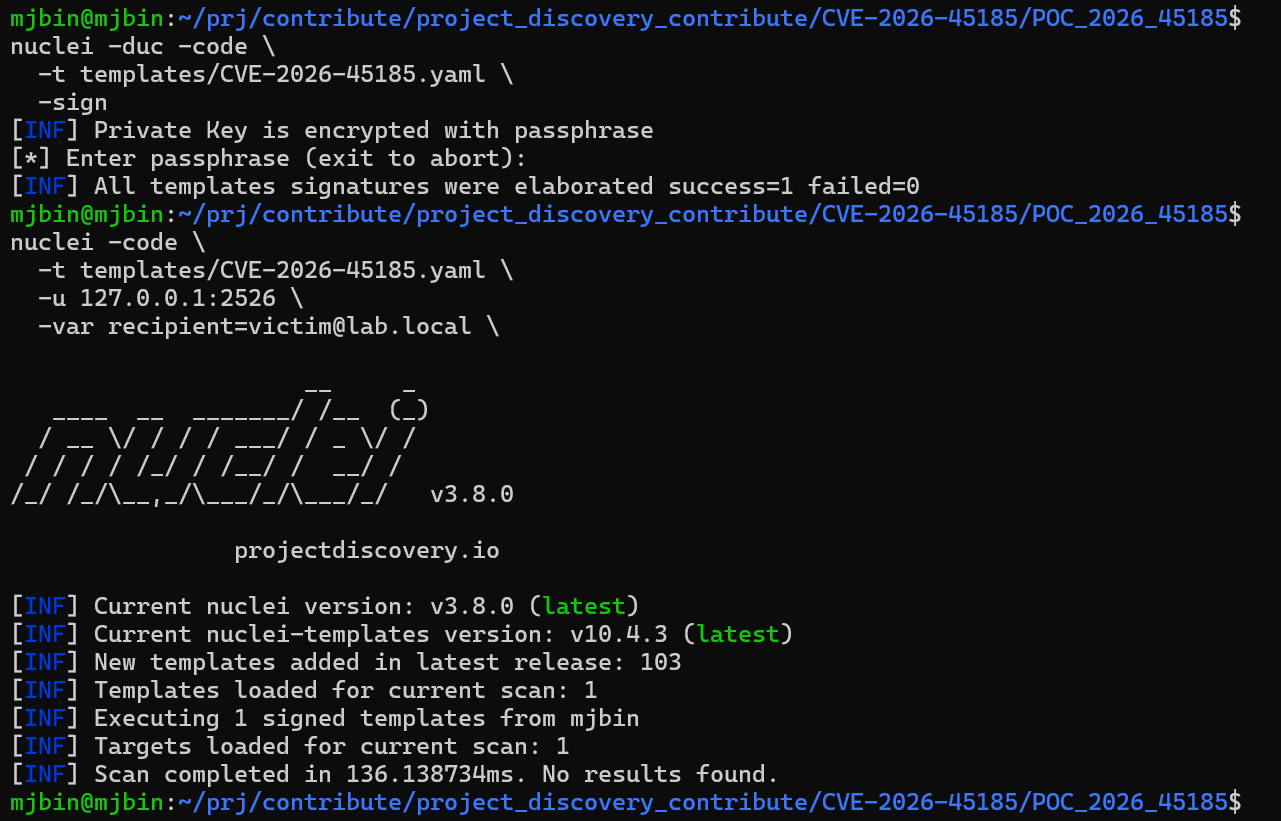
 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 dev-lu/osint_toolkit
Open source platform for cyber security analysts with many features for threat intelligence and detection engineering.
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 mailgun/flanker
Python email address and Mime parsing library
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
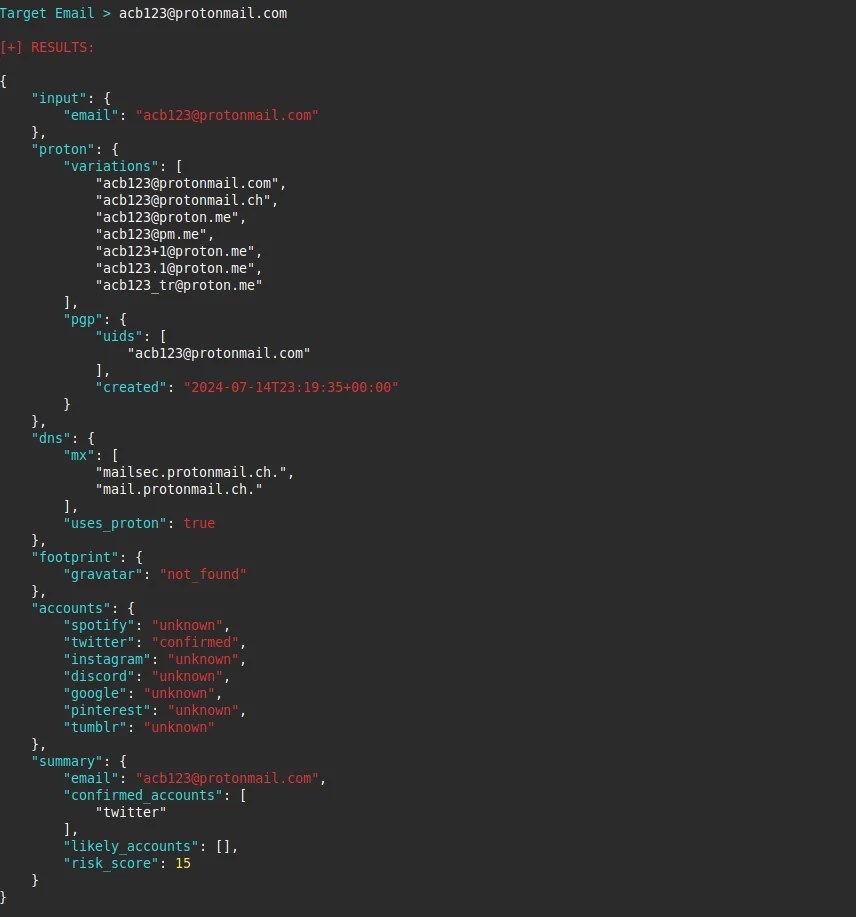 emrekybs/protonscope
Lightweight Python OSINT tool that analyzes email addresses to extract intelligence and digital footprint data, with a focus on ProtonMail…
 0xblackash/cve-2026-28289
CVE-2026-28289
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.