
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended
 0xblackash/cve-2026-63072
Technical analysis of CVE-2026-63072, a heap buffer overflow in OpenSSL CMS key unwrapping, covering root cause, affected versions, detection, and…
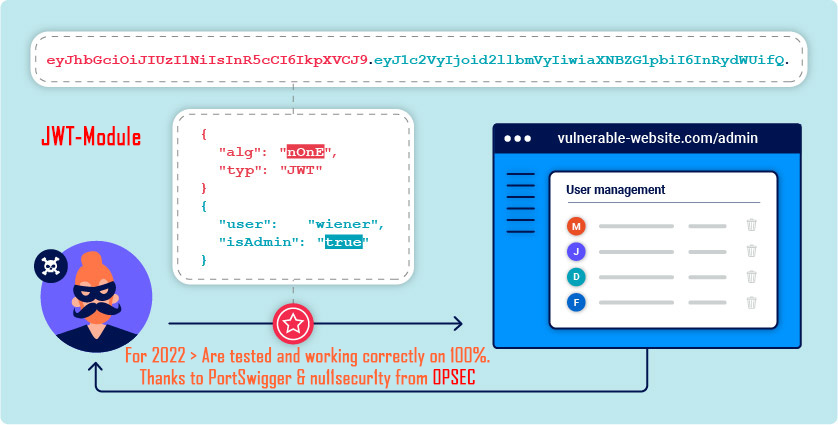 nu11secur1ty/portswigger-web-security-academy
Curated solutions and walkthroughs for PortSwigger Web Security Academy labs, covering web vulnerabilities, JWT attacks, and exploitation techniques…
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 dinosn/log4j-4255
End-to-end Docker lab reproducing Apache log4j2 #4255 — FilteredObjectInputStream allowlist bypass via java.rmi.MarshalledObject (unfiltered…
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 deeptempo/socbench
An Open Harness and Benchmark for AI in Cybersecurity Operations.
 fevar54/cve-2026-72530-trueconf-sandbox-escape-
Este repositorio contiene una demostración educativa de la mitigación y detección para **CVE-2026-72530**, una vulnerabilidad crítica de **Code…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 horkimhab/cve-2026-35273
CVE-2026-35273
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…
 fevar54/cve-2026-32635-angular-xss-mitigation-
Demostracion educativa de mitigacion y deteccion de CVE-2026-32635: XSS en atributos i18n de Angular.
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
 gh0stuncle/cve-2018-16763_fuel_cms_exploit
A fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.








