
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 alphacrack/readme2demo
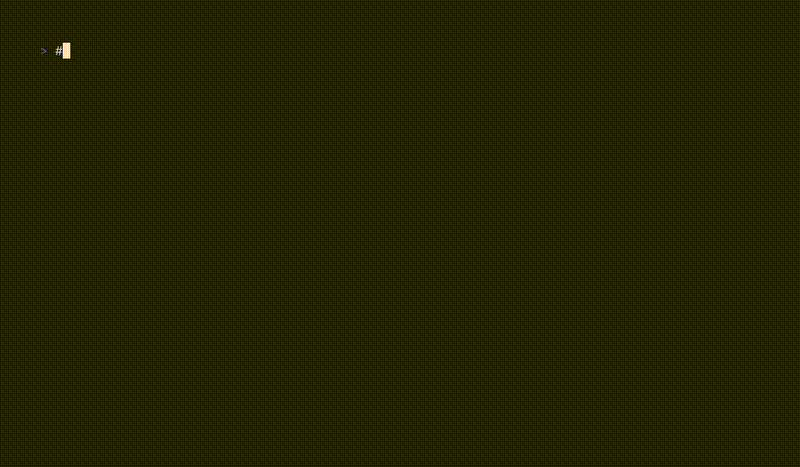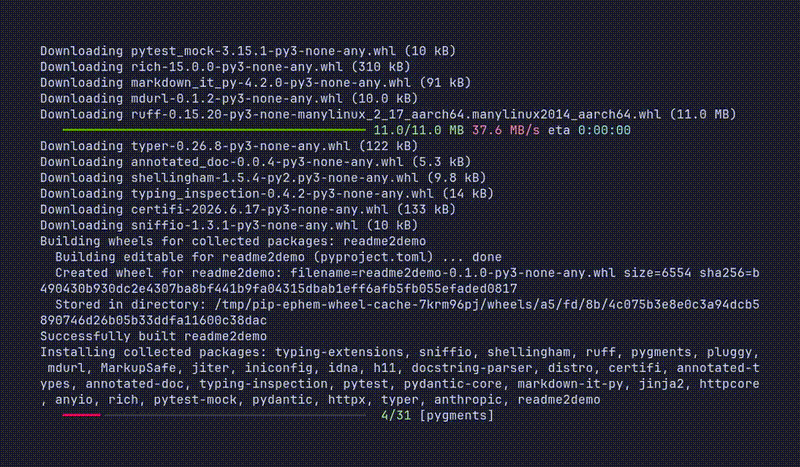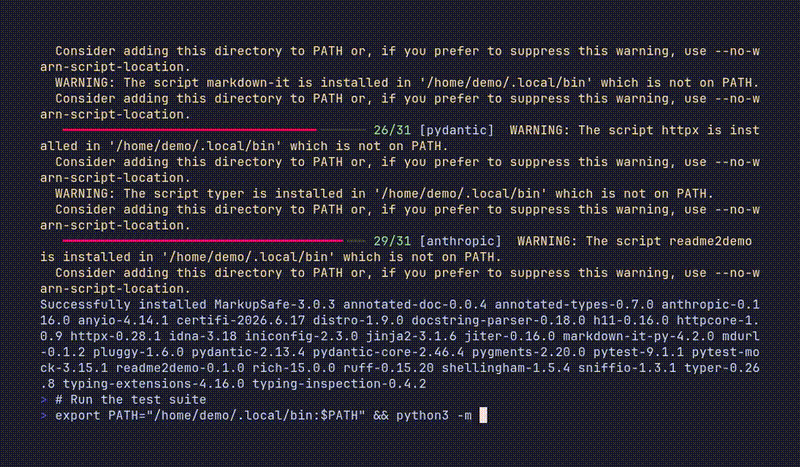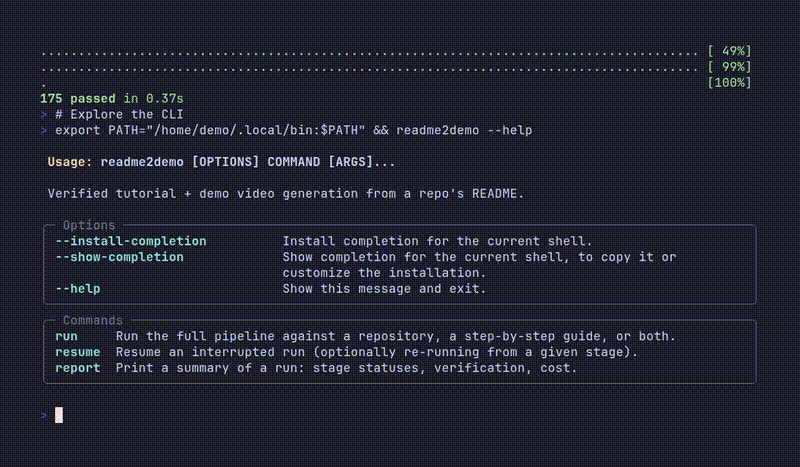
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 sfaci/masc
A Web Malware Scanner
 epfl-vlsc/memoro
Memoro: A Detailed Heap Profiler
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 mitre/multiscanner
Modular file scanning/analysis framework
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 cea-sec/miasm
Reverse engineering framework in Python








