#2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
 t0thkr1s/frida
Frida scripts for mobile application dynamic-analysis.
 dxc-strikeforce/burp-log4j-hammertime
Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 chilliwebs/cve-2021-44228_example
Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
 captain4554/captain4554.github.io
🔍 Scan for CVE-2025-55182 vulnerabilities with a hybrid tool that combines static and dynamic analysis for improved security assessments.
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
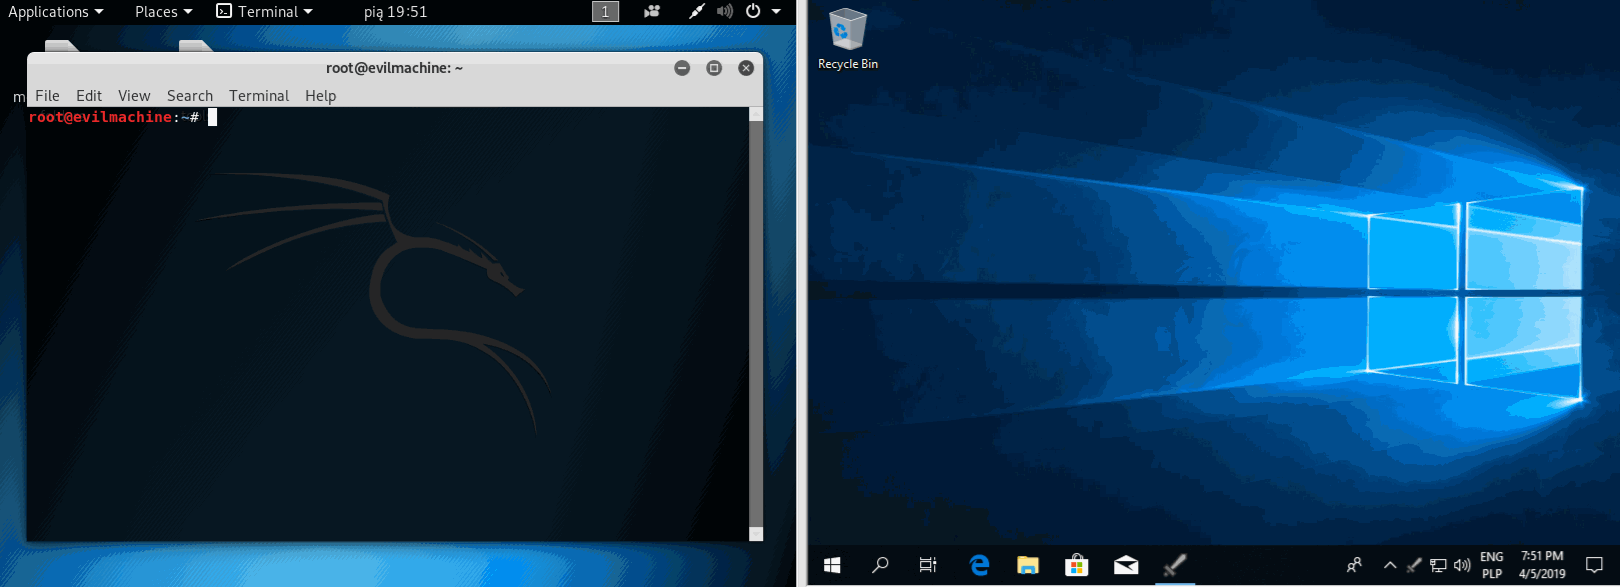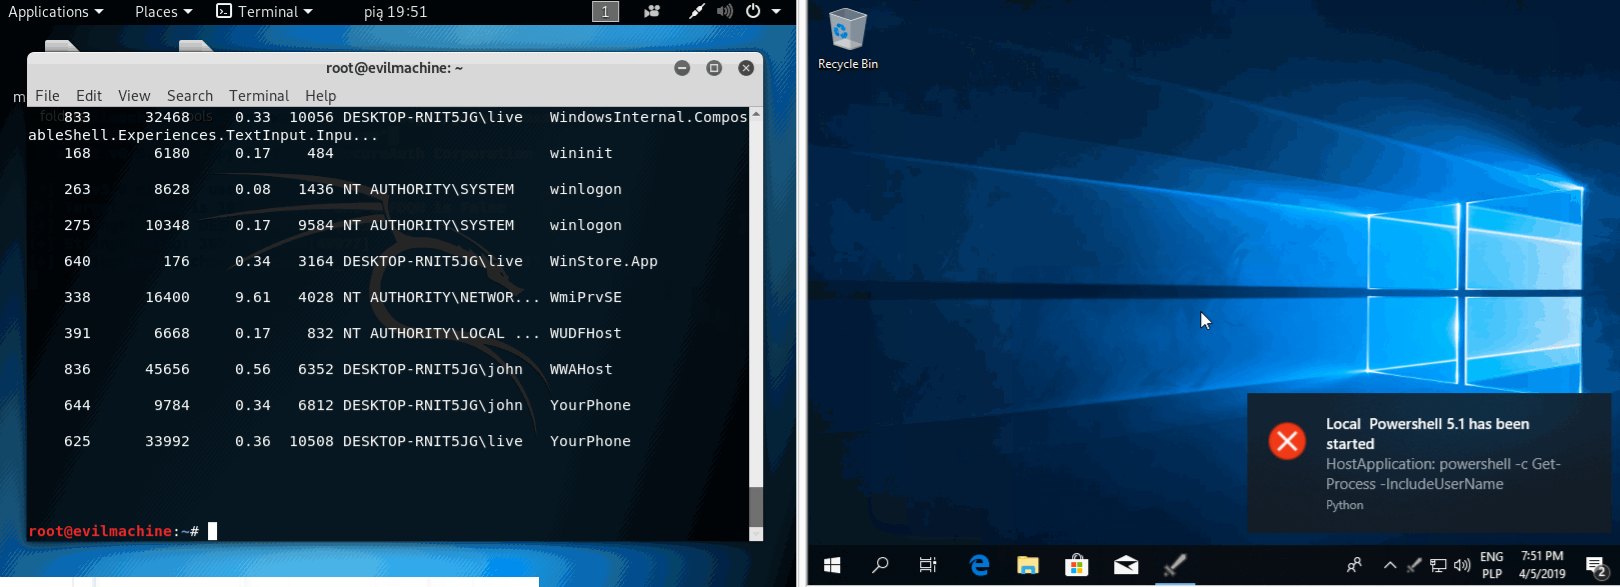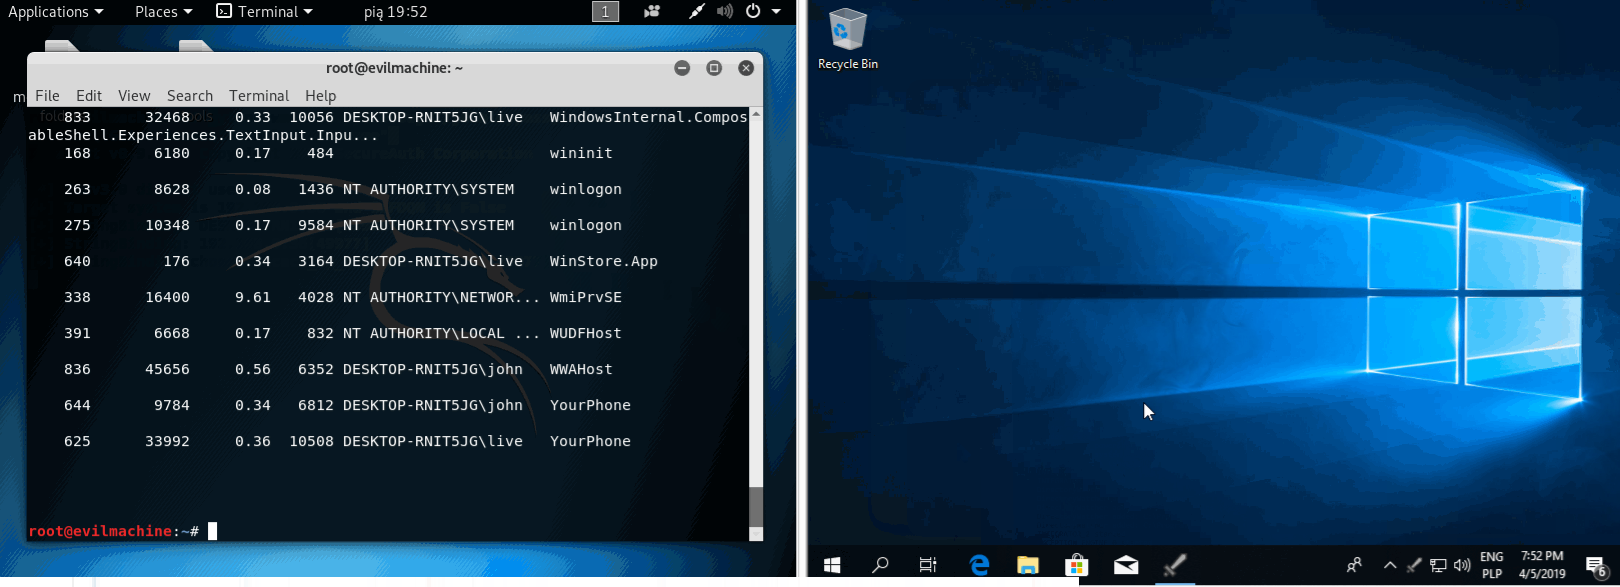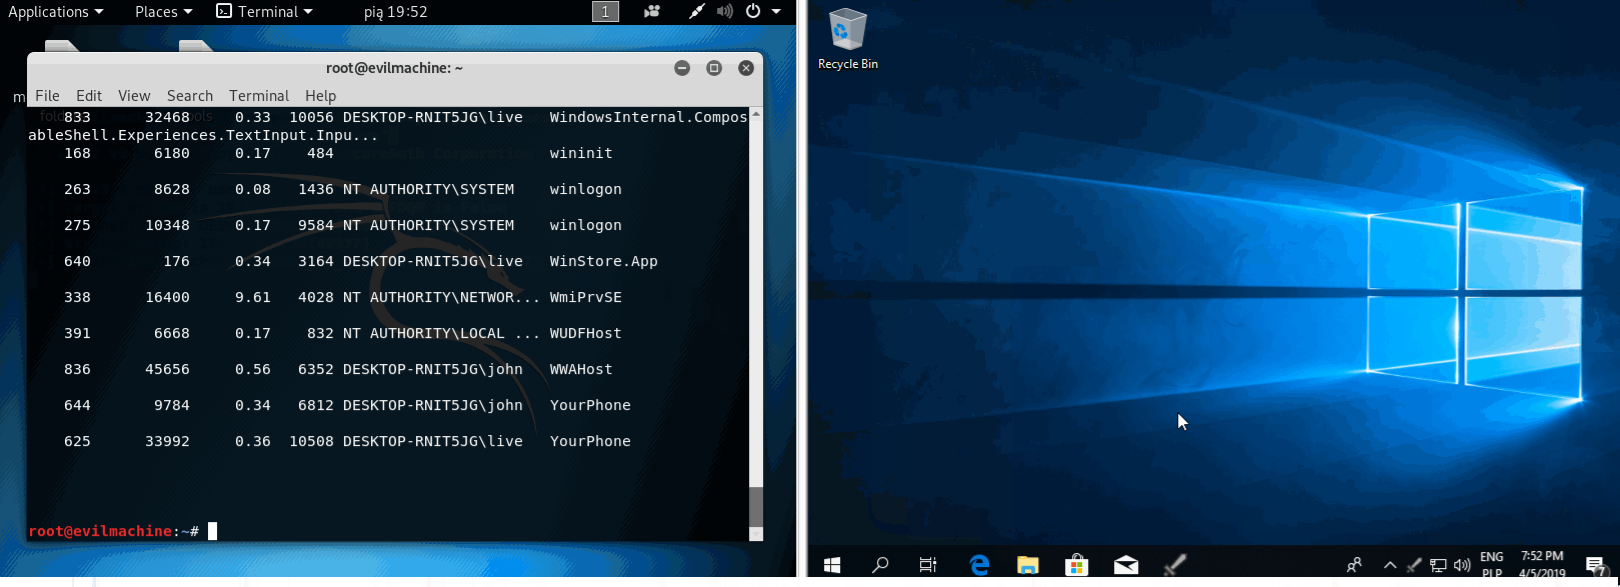 yarox24/attack_monitor
Endpoint detection & Malware analysis software
 charis3306/cve-2025-24813
CVE-2025-24813利用工具
 egkritsis/cve-2025-61301
CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…
 gmh5225/fracture-
🐈⬛ WIP Suite for reverse engineering JVM applications
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery