
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
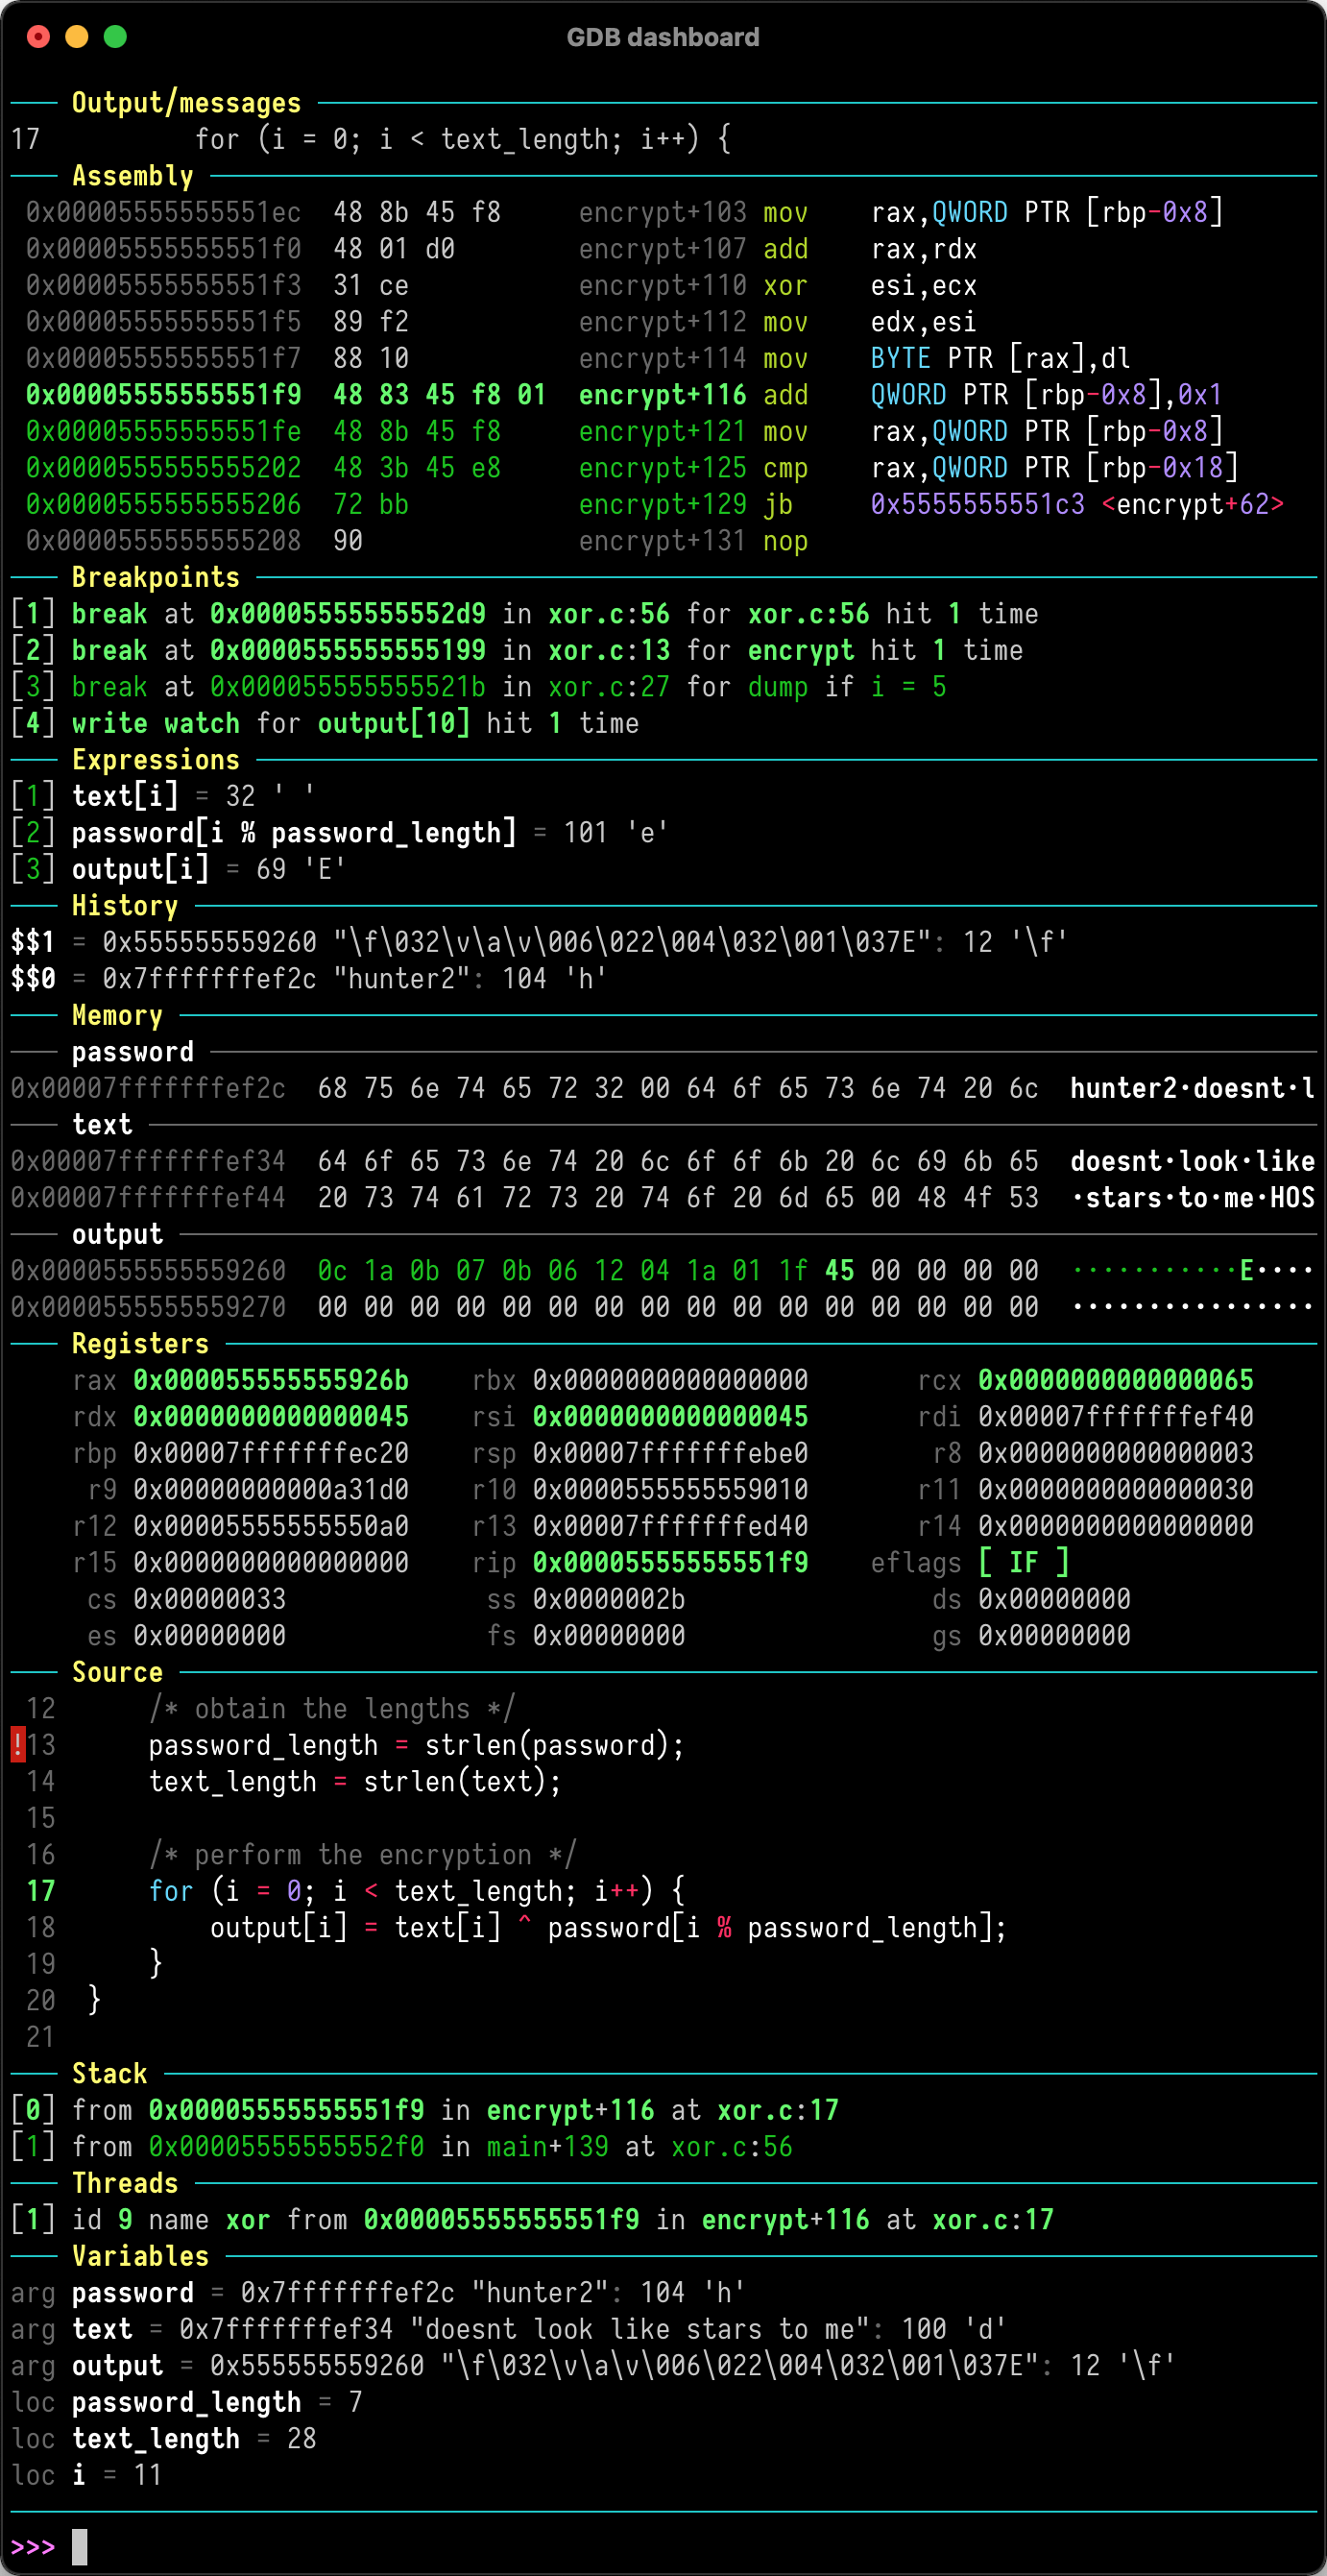 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 zrax/pycdc
C++ python bytecode disassembler and decompiler

 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 cea-sec/miasm
Reverse engineering framework in Python
 hyperdbg/hyperdbg
State-of-the-art native debugging tools
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 rocky/python-uncompyle6
A cross-version Python bytecode decompiler
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
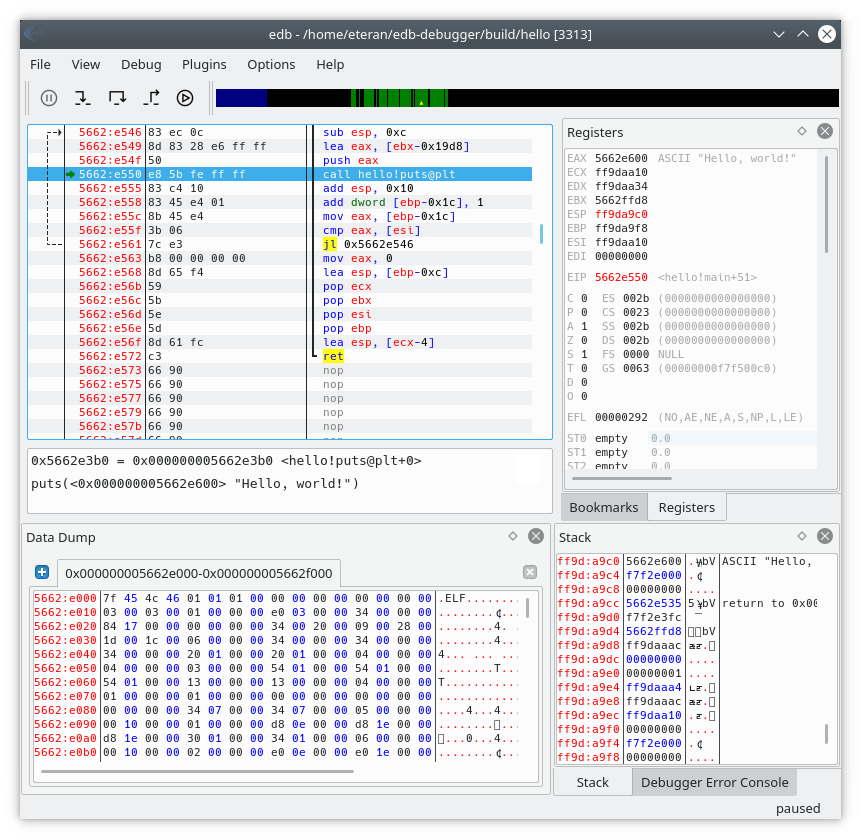 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)







