
 #1
File recovery, disk recovery, deleted data restoration, and forensic carving tools.
Kitploit recommended
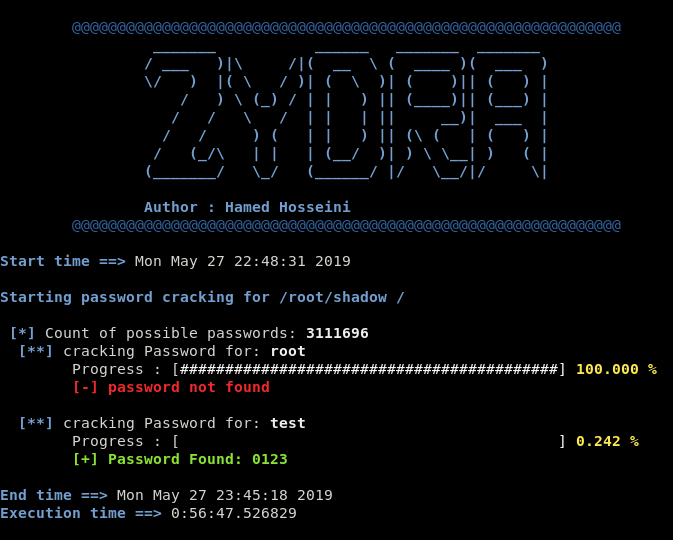
 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…

 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 cea-sec/usbsas
Tool and framework for securely reading untrusted USB mass storage devices.
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
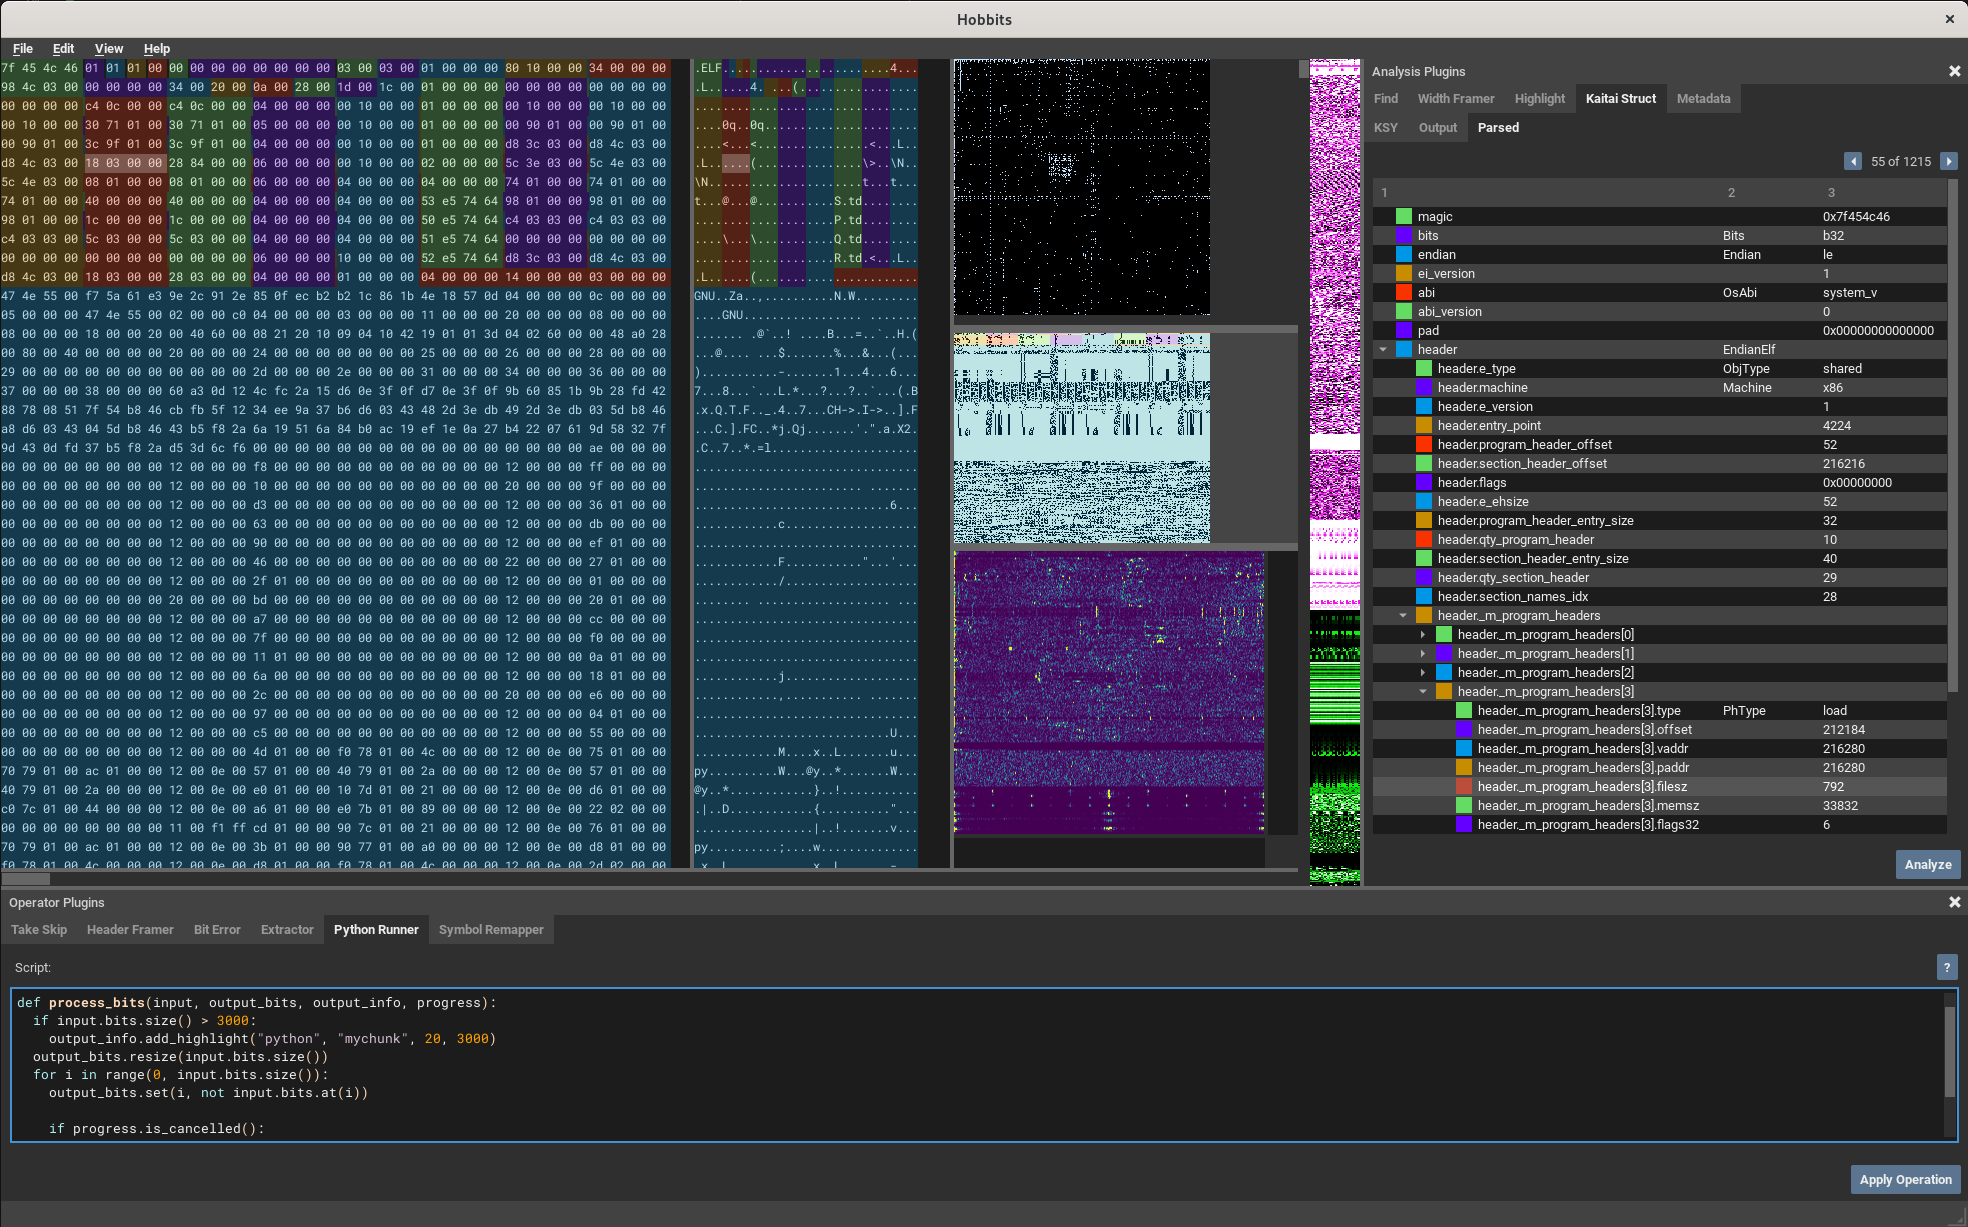 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
 rockwellshah/filekey
Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…
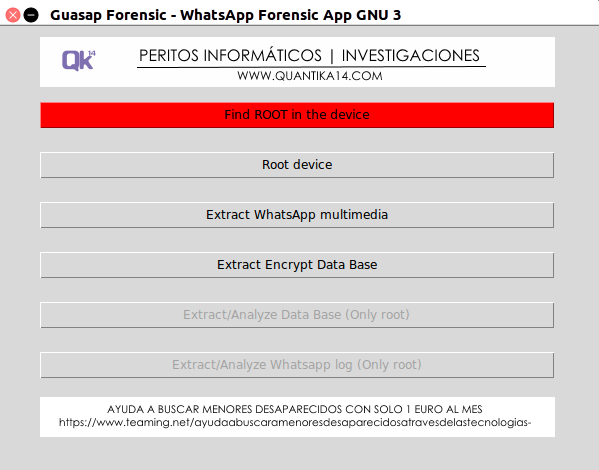 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
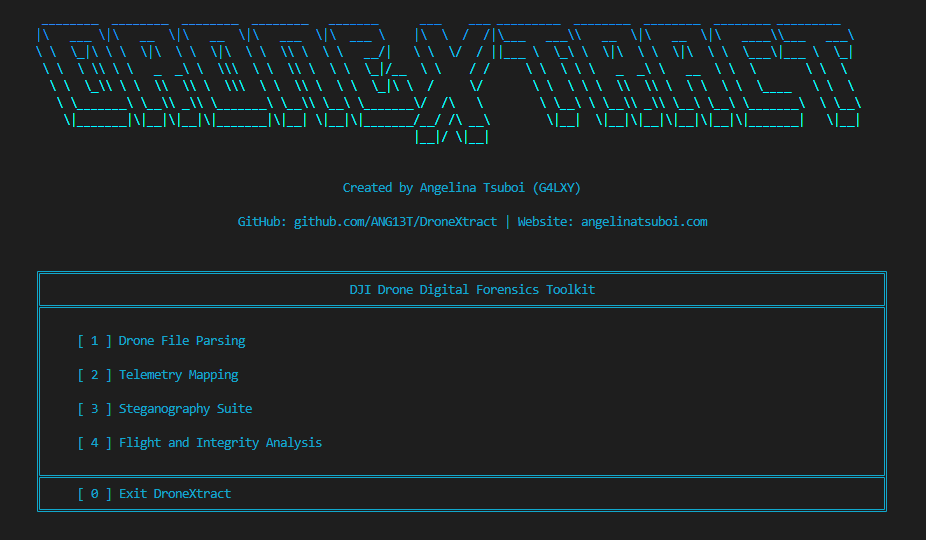 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format

 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool






