
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Data Recovery — Page 3 | Kitploit
Categories

Data Recovery

File recovery, disk recovery, deleted data restoration, and forensic carving tools.

Kitploit recommended

Top tools

10 selected
testdisk preview#1

testdisk

GitHubcgsecurity/testdisk
2.6k20 days ago
autopsy preview#2

autopsy

GitHubsleuthkit/autopsy
3.3k5 months ago
sleuthkit preview#3

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k4 days ago
bulk_extractor preview#4

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k12 days ago
foremost preview#5

foremost

GitHubkorczis/foremost
3819 years ago
scalpel preview#6

scalpel

GitHubsleuthkit/scalpel
6905 years ago
libewf preview#7

libewf

GitHublibyal/libewf
31811 days ago
libfsntfs preview#8

libfsntfs

GitHublibyal/libfsntfs
23812 days ago
libvshadow preview#9

libvshadow

GitHublibyal/libvshadow
11912 days ago
libqcow preview#10

libqcow

GitHublibyal/libqcow
623 months ago
NewestRelevanceMost popularRecently updated
155 results
libewf preview

libewf

GitHublibyal/libewf

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
disk-forensicsforensicsdata-recovery+1
31811 days ago
xlsx preview

xlsx

GitHubweareu/xlsx

SheetJS xlsx 0.18.5 fork with CVE-2023-30533 and CVE-2024-22363 fixes
general-purpose-utilitiesencryption-decryption-toolsdata-recovery+1
8 months ago
YellowKey-Bitlocker-CVE-2026-45585 preview

YellowKey-Bitlocker-CVE-2026-45585

GitHubneccie/yellowkey-bitlocker-cve-2026-45585

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.

encryption-decryption-toolsvulnerability-analysisdata-recovery+1
2 months ago
plaso preview

plaso

GitHublog2timeline/plaso

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

disk-forensicsioc-managementforensics+5
2.2k15h 30m ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format

disk-forensicsforensicsdata-recovery+2
11912 days ago
testdisk preview

testdisk

GitHubcgsecurity/testdisk

Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
disk-forensicsforensicsdata-recovery+1
2.6k20 days ago
mboxshell preview

mboxshell

GitHubdcarrero/mboxshell

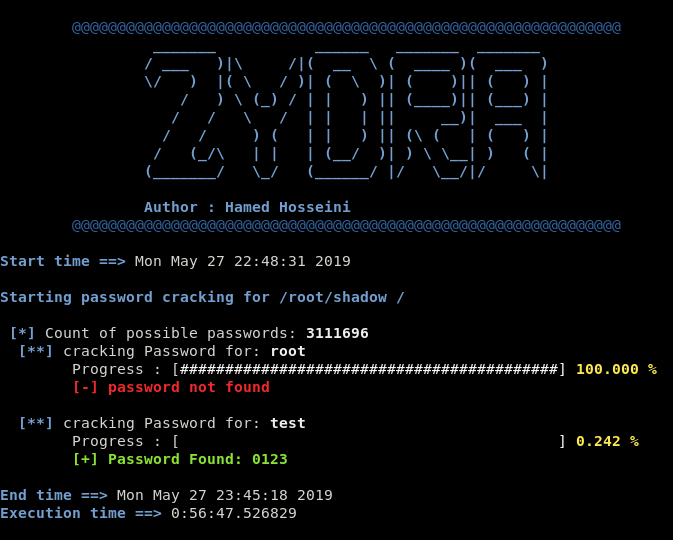
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
general-purpose-utilitiesscripting-automationforensics+4
315 days ago
Zydra preview

Zydra

GitHubhameda2/zydra

Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…


password-crackingpassword-attacksdata-recovery
4356 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

defensive-toolsdisk-forensicsioc-management+14
1.2k10h 10m ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)

disk-forensicsforensicsdata-recovery+1
23812 days ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

ioc-managementmemory-forensicsnetwork-forensics+7
122 months ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format

disk-forensicsforensicsdata-recovery+1
14929 days ago
FAMA preview
Archived

FAMA

GitHublabcif/fama

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
android-securityforensicsinformation-gathering+3
1532 years ago
psa-2026-00043-recovery preview

psa-2026-00043-recovery

GitHubdisqualifier/psa-2026-00043-recovery

Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
cloud-infrastructure-securityvulnerability-analysisforensics+3
1 month ago
Total-Commander-FTP-Password-Recovery-Tool-Python preview

Total-Commander-FTP-Password-Recovery-Tool-Python

GitHubpelock/total-commander-ftp-password-recovery-tool-python

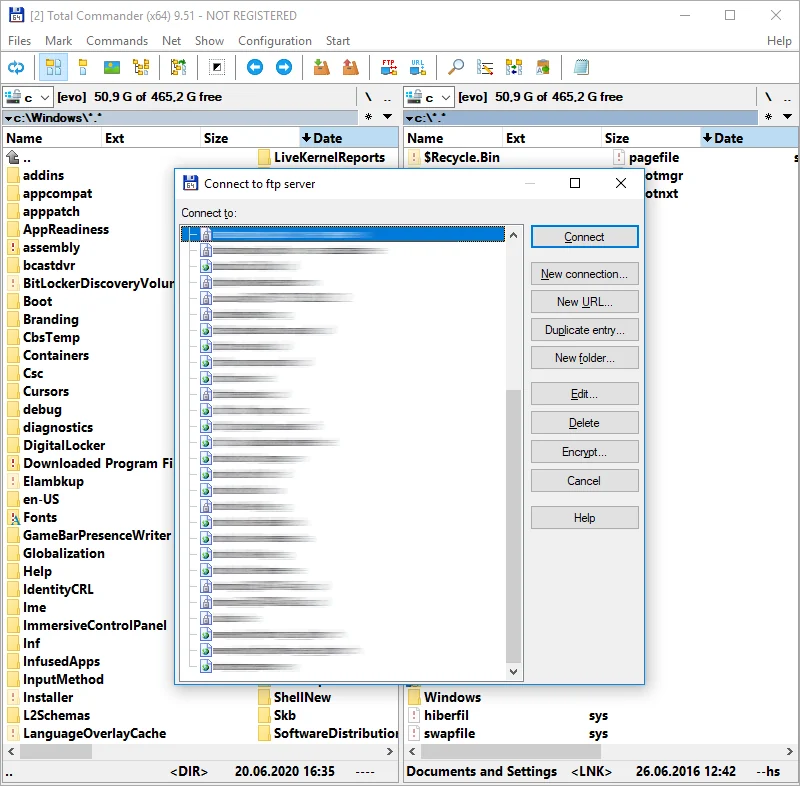
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
password-crackingencryption-decryption-toolsreverse-engineering+2
15 months ago
filekey preview

filekey

GitHubrockwellshah/filekey

Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…

encryption-decryption-toolsdata-recoverycryptography+2
4862 months ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

disk-forensicsmemory-forensicsnetwork-forensics+5
1.1k1 day ago
libqcow preview

libqcow

GitHublibyal/libqcow

Library and tools to access the QEMU Copy-On-Write (QCOW) image format

disk-forensicsencryption-decryption-toolsdata-recovery+2
623 months ago
Previous1234…9Next




