
 #1
Tools for extracting sensitive data from compromised systems without detection.
Kitploit recommended

 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
 mythicagents/xenon
A Mythic agent for Windows written in C
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
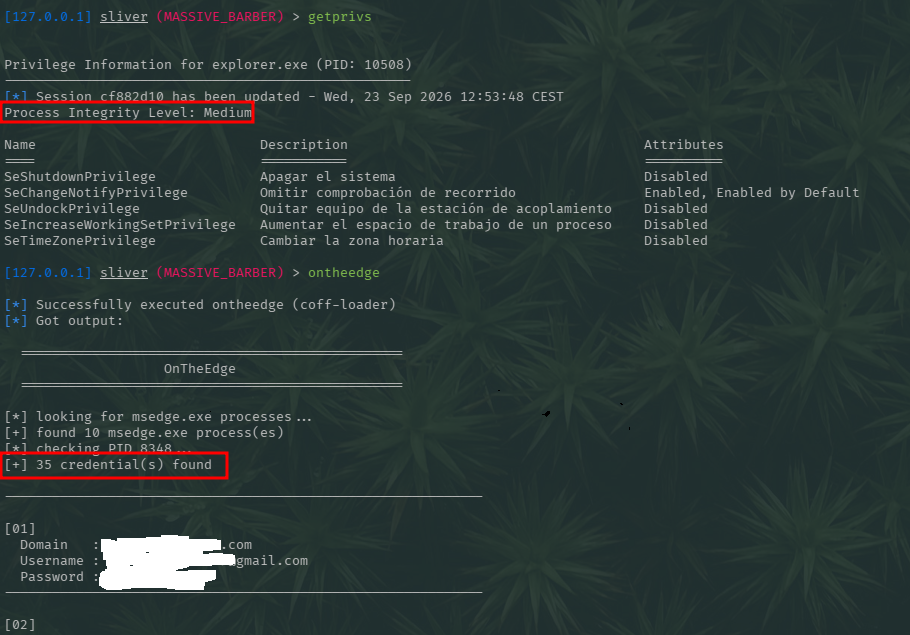 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…








