
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 synacktiv/lehack-2026-challenge
Sources of Synacktiv's challenge for leHack 2026
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 hxuu/moodle-cve
Web CTF challenge highlighting moodle CVE-2025-26529 (in 2 flavors)
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 aalex954/jwt-key-confusion-poc
JWT Key Confusion PoC (CVE-2015-9235) Written for the Hack the Box challenge - Under Construction
 shen771/blackash-cve-2025-55182
CVE-2025-55182
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
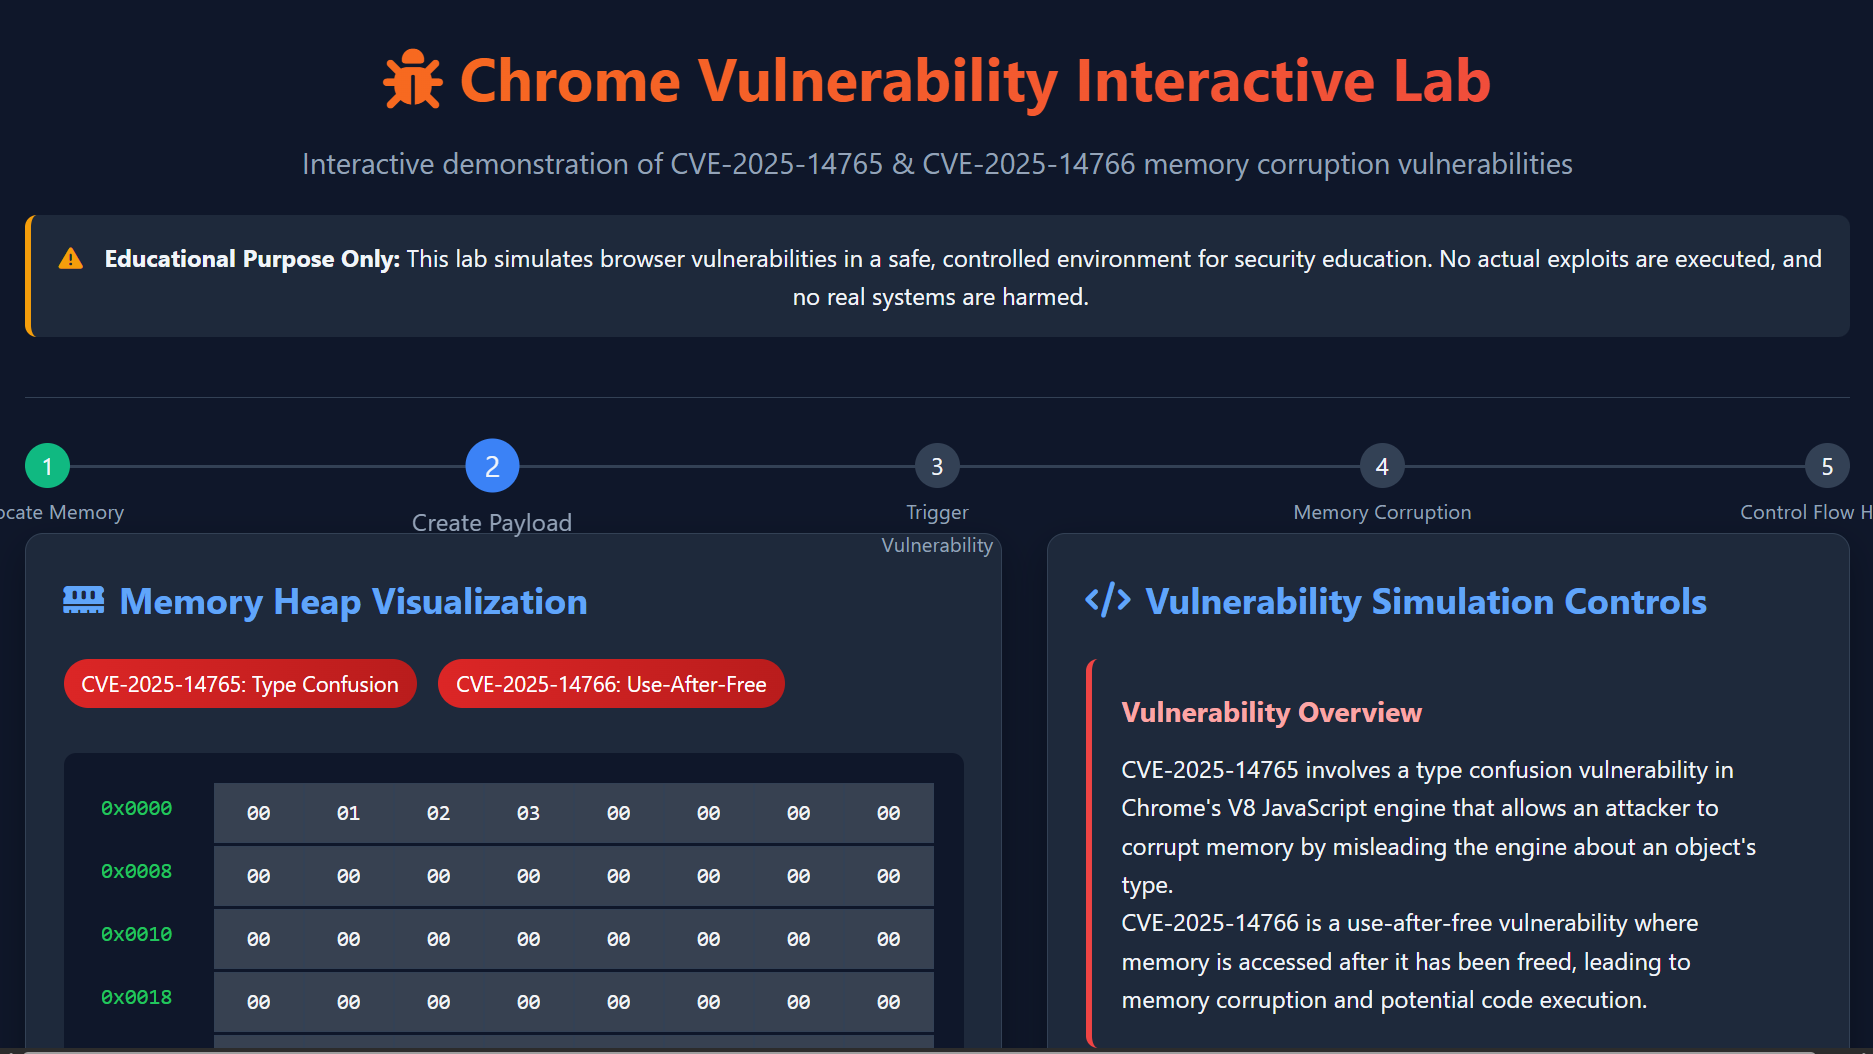 infosecantara/cve-2025-14765-and-cve-2025-14766
Interactive browser-based lab simulating Chrome memory corruption vulnerabilities (CVE-2025-14765/14766) for safe security training, featuring…
 drackyjr/cve-2025-8018
Python PoC exploit for CVE-2025-8018, a critical unauthenticated SQL injection in Food Ordering Review System v1.0. Supports time-based blind and…
 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 4xura/php_filter_chain_oracle_poc
PoC scripts to exploit LFR (Local File Read) via PHP filters chain oracle (php://filter), especially for CTF purposes or the exploit of…
 nkwenti-severian-ndongtsop/poc_react2shell_cve-2025-55182
Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…
 shashivanth009/cve-2022-46364---apache-cxf-xop-include-lfi-poc
Proof-of-concept exploit for CVE-2022-46364, a local file inclusion vulnerability in Apache CXF via crafted XOP Include elements in SOAP requests,…
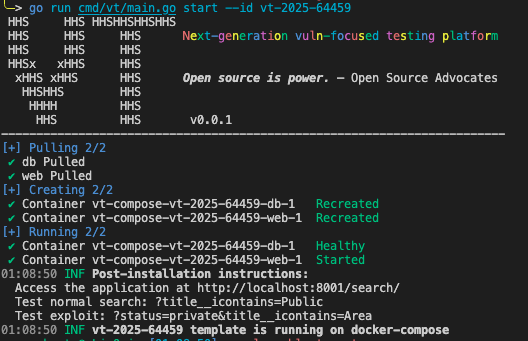 omarkurt/django-connector-cve-2025-64459-testbed
A self-contained testbed for Django CVE-2025-64459. Demonstrates QuerySet.filter() parameter injection via dictionary expansion using Docker.
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…








