
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 isaca0315/cve-2026-44578-next-js-ssrf
este laboratorio puede estar bien o mal esta el pruebas pero debe funcionar preguntale a la IA hahah
 gbuyssens/cve-2026-41651
Local privilege escalation via TOCTOU race condition in PackageKit's.
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
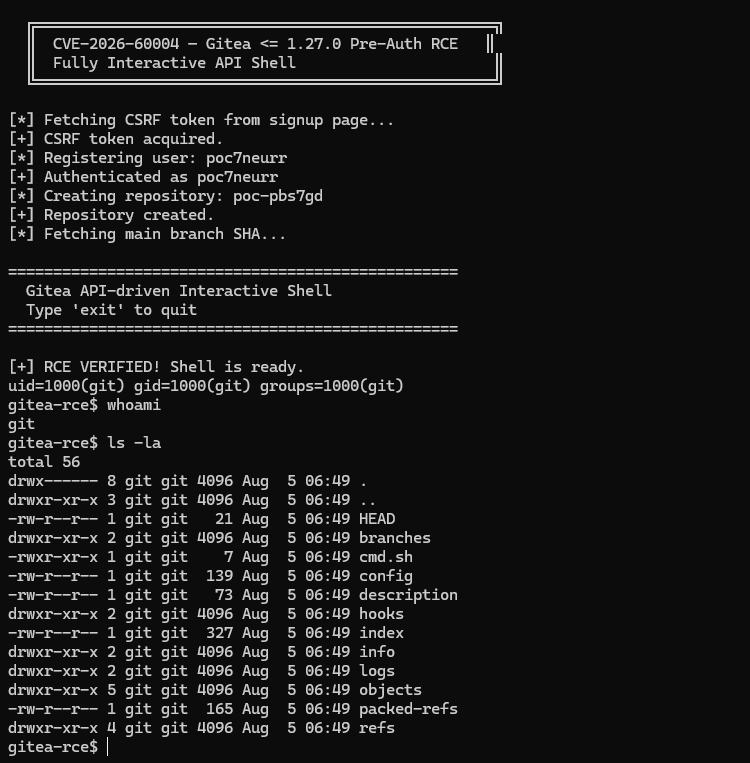 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 qinglove777/cve-2024-2961-xxe-exploit
CVE-2024-2961 (CNEXT) PHP file-read to RCE exploit adapted to an XXE/CTF channel
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 alreadyclosed/cve-2026-39987
CVE-2026-39987 for marimo 0.20.4 PoC
 beraphin/cve-2018-6789
Exploit for CVE-2018-6789, a heap buffer overflow in Exim's base64 decoding, achieving remote code execution via chunk overlap and ACL string…
 byt3quester/cve-2023-20938-poc
Local privilege escalation proof-of-concept for CVE-2023-20938, a use-after-free in Android binder, achieving root and disabling SELinux on…
 ywh-jfellus/cve-2026-9198
Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 cd-ratel/cve-2025-32432
Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning
 giordy0424/cve-2023-25690_lab
HTTP Request Smuggling lab: Apache 2.4.55 CRLF injection
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…








