
 #1
Tools for implementing, analyzing, breaking, and implementing cryptographic systems and algorithms.
Kitploit recommended

 roxanne_ardary/e2eauth
Cross-platform TOTP/HOTP authenticator specification with end-to-end encrypted vault sync, local-first storage, device management, and threshold…

 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet

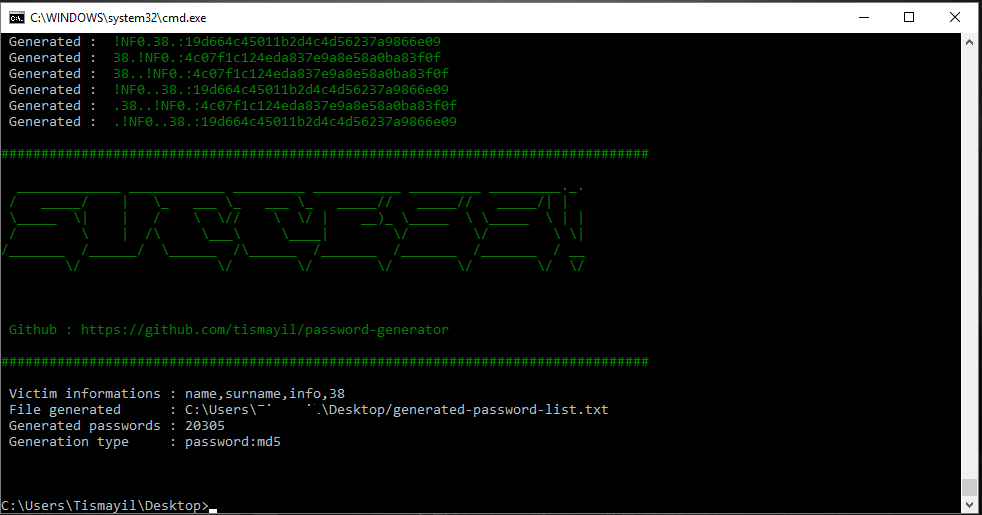 tismayil/password-generator
-> Password List Generator for Brute Force.
 krishsharma0413/syncord
Syncord is a CLI-based file synchronization and storage tool that uses Discord as an encrypted file storage.
 0xxon/cve-2020-0601-plugin
Zeek package that uses OpenSSL to detect CVE-2020-0601 exploit attempts
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 anthophilee/a2sv--ssl-vul-scan
A2SV = Auto Scanning to SSL Vulnerability HeartBleed, CCS Injection, SSLv3 POODLE, FREAK... etc Support Vulnerability [CVE-2007-1858] Anonymous…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
 balgan/cve-2025-15467
Working DoS for CVE-2025-15467 and a docker container to test against
 roninreilly/wazuh-unauth-chain
Wazuh PoC chaining CVE-2026-74034 file read and CVE-2026-74041 command execution; fixed in 4.14.8. Python standard library only.
 wvllxe/cve-2026-104356-pictshare-weak-delete-code
Predictable delete_code via rand() in PictShare < 3.7.1 (CWE-338). PoC + advisory writeup.
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 chakshugupta13/lab
Code artifacts from research paper implementations








