
 #1
Tools for scanning, securing, and hardening Docker, Kubernetes, and containerized environments.
Kitploit recommended
 knqyf263/cve-2018-1111
Docker-based lab environment to reproduce and exploit CVE-2018-1111 (DynoRoot) with automated attacker and victim scripts for hands-on security…
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 t0kx/privesc-cve-2015-5602
Sudo <= 1.8.14 Local Privilege Escalation and vulnerable container
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 xvnpw/k8s-cve-2021-43557-poc
PoC for CVE-2021-43557
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 bhdresh/cve-2018-11776
Vulnerable docker container for CVE-2018-11776
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 tabbysable/poc-2020-8559
Proof of Concept exploit for Kubernetes CVE-2020-8559
 ugurrates/teampcp-supply-chain-attack
CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
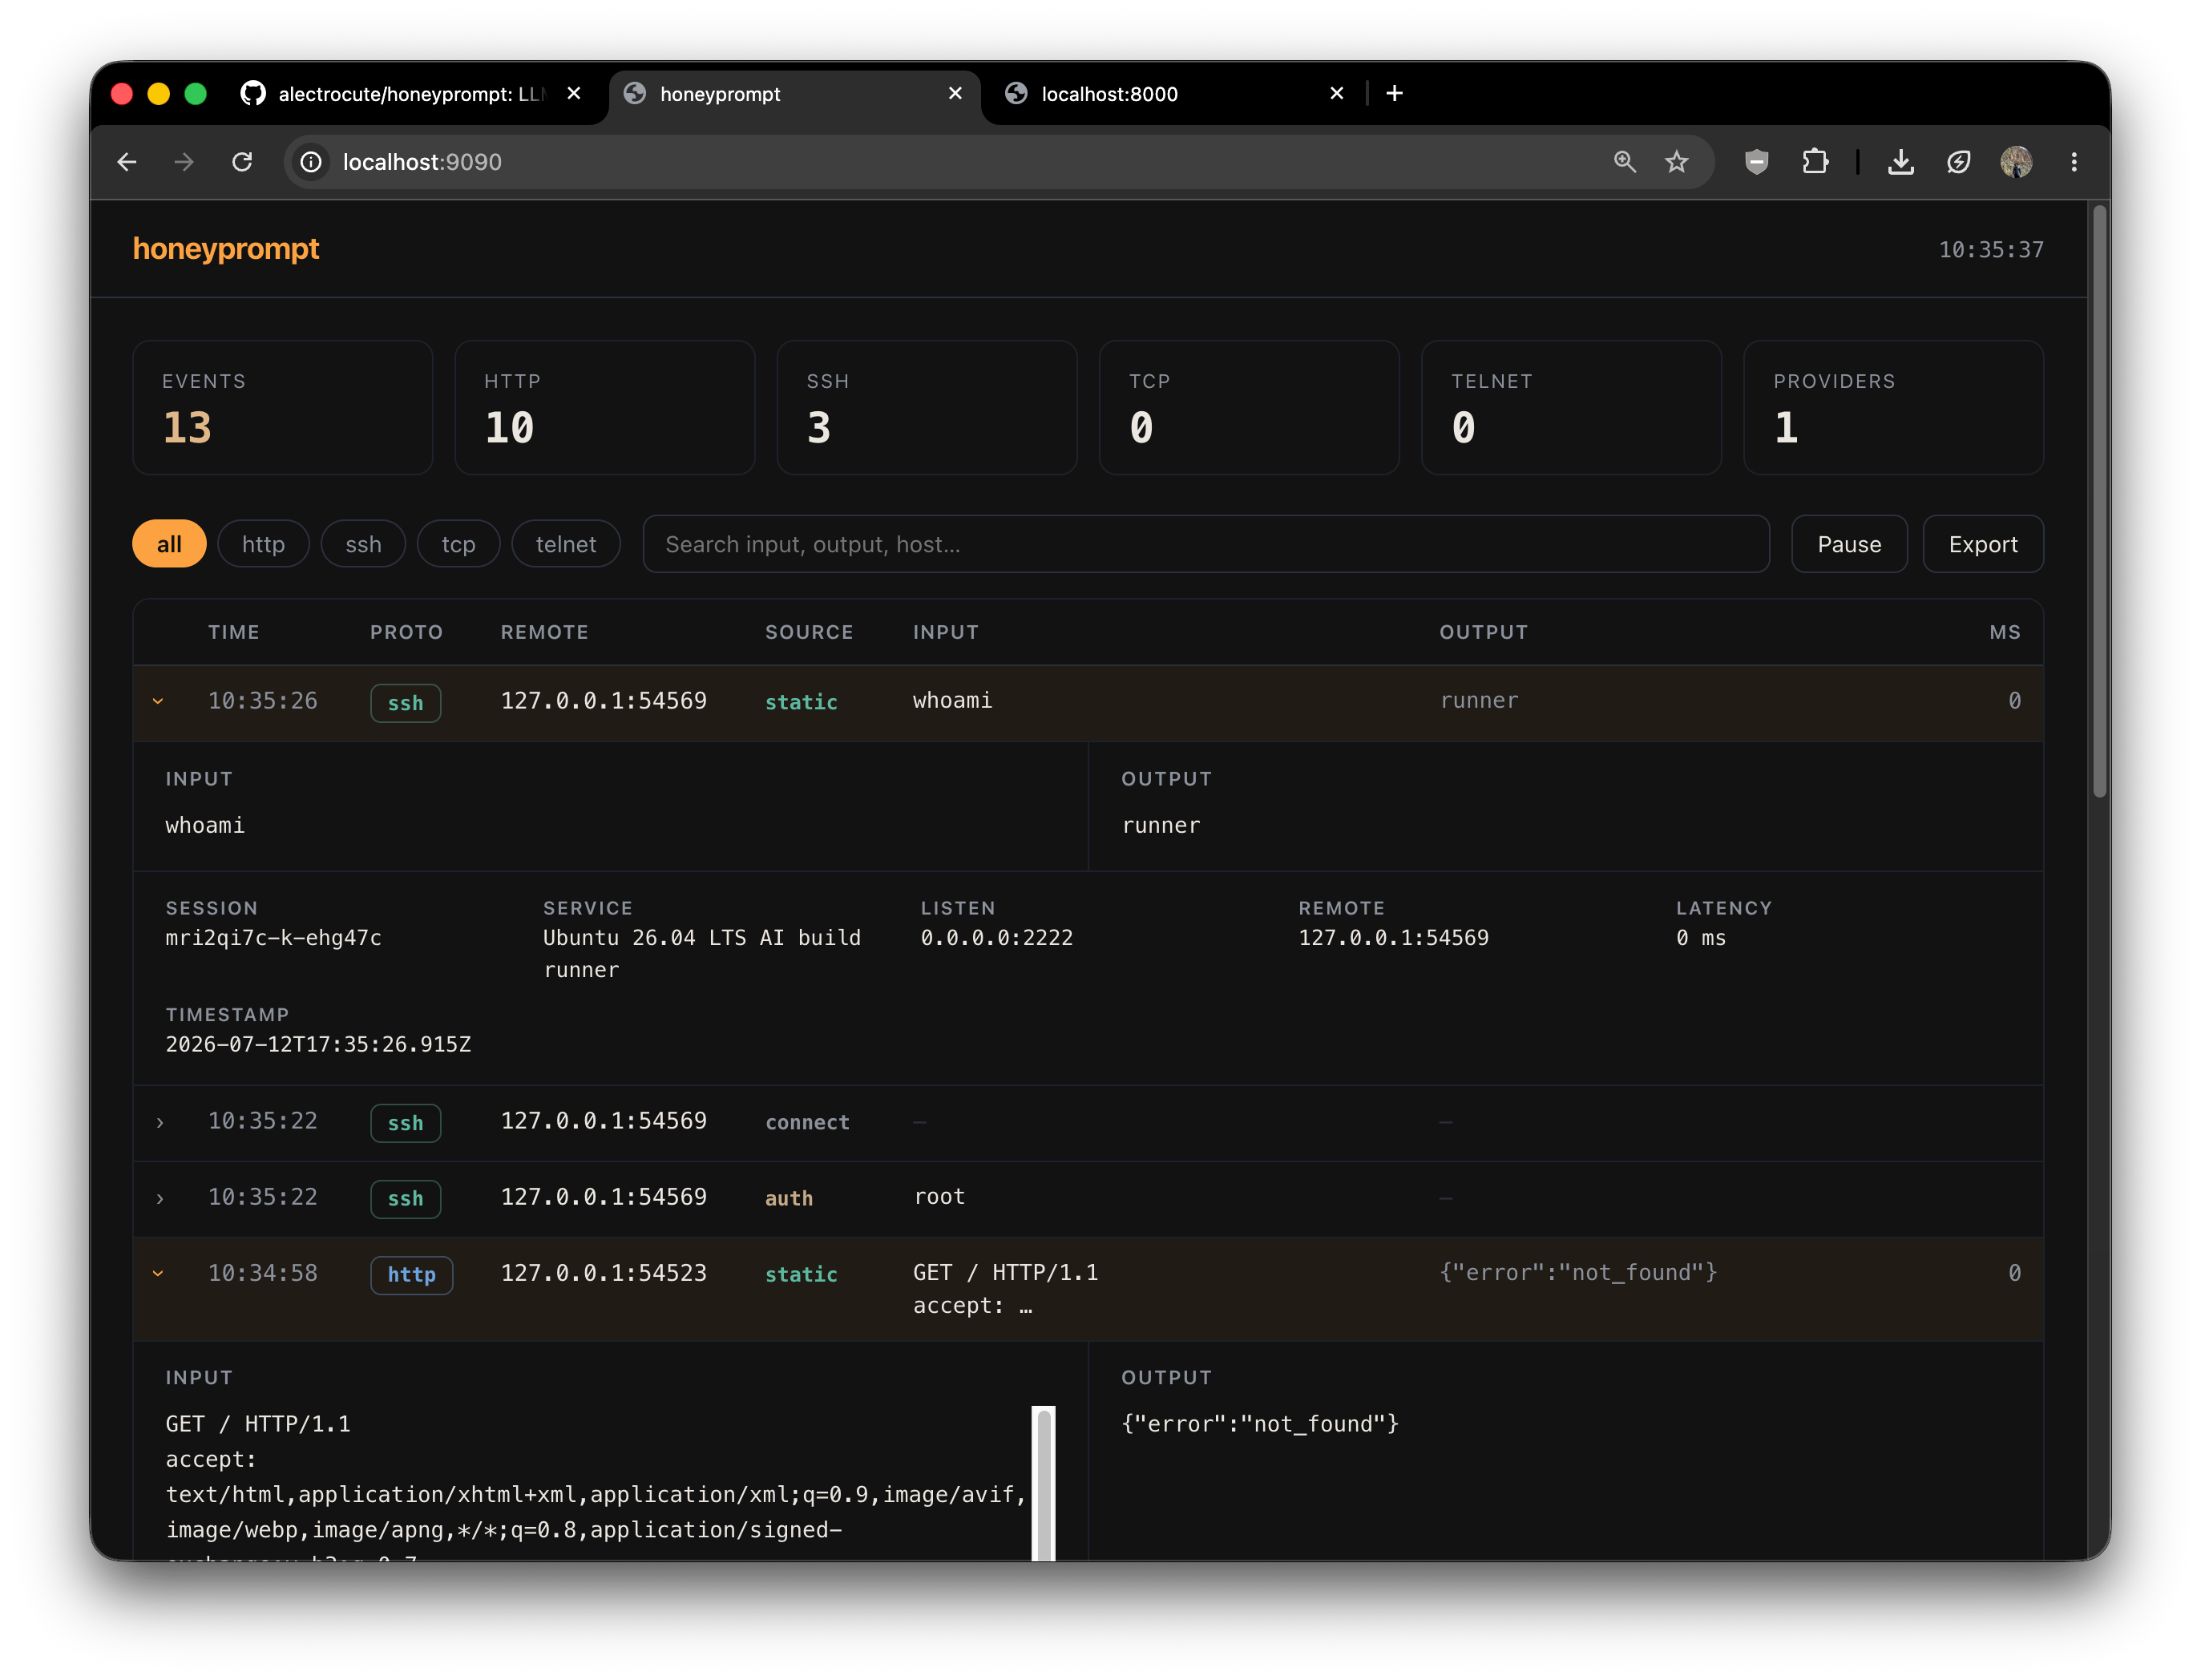 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
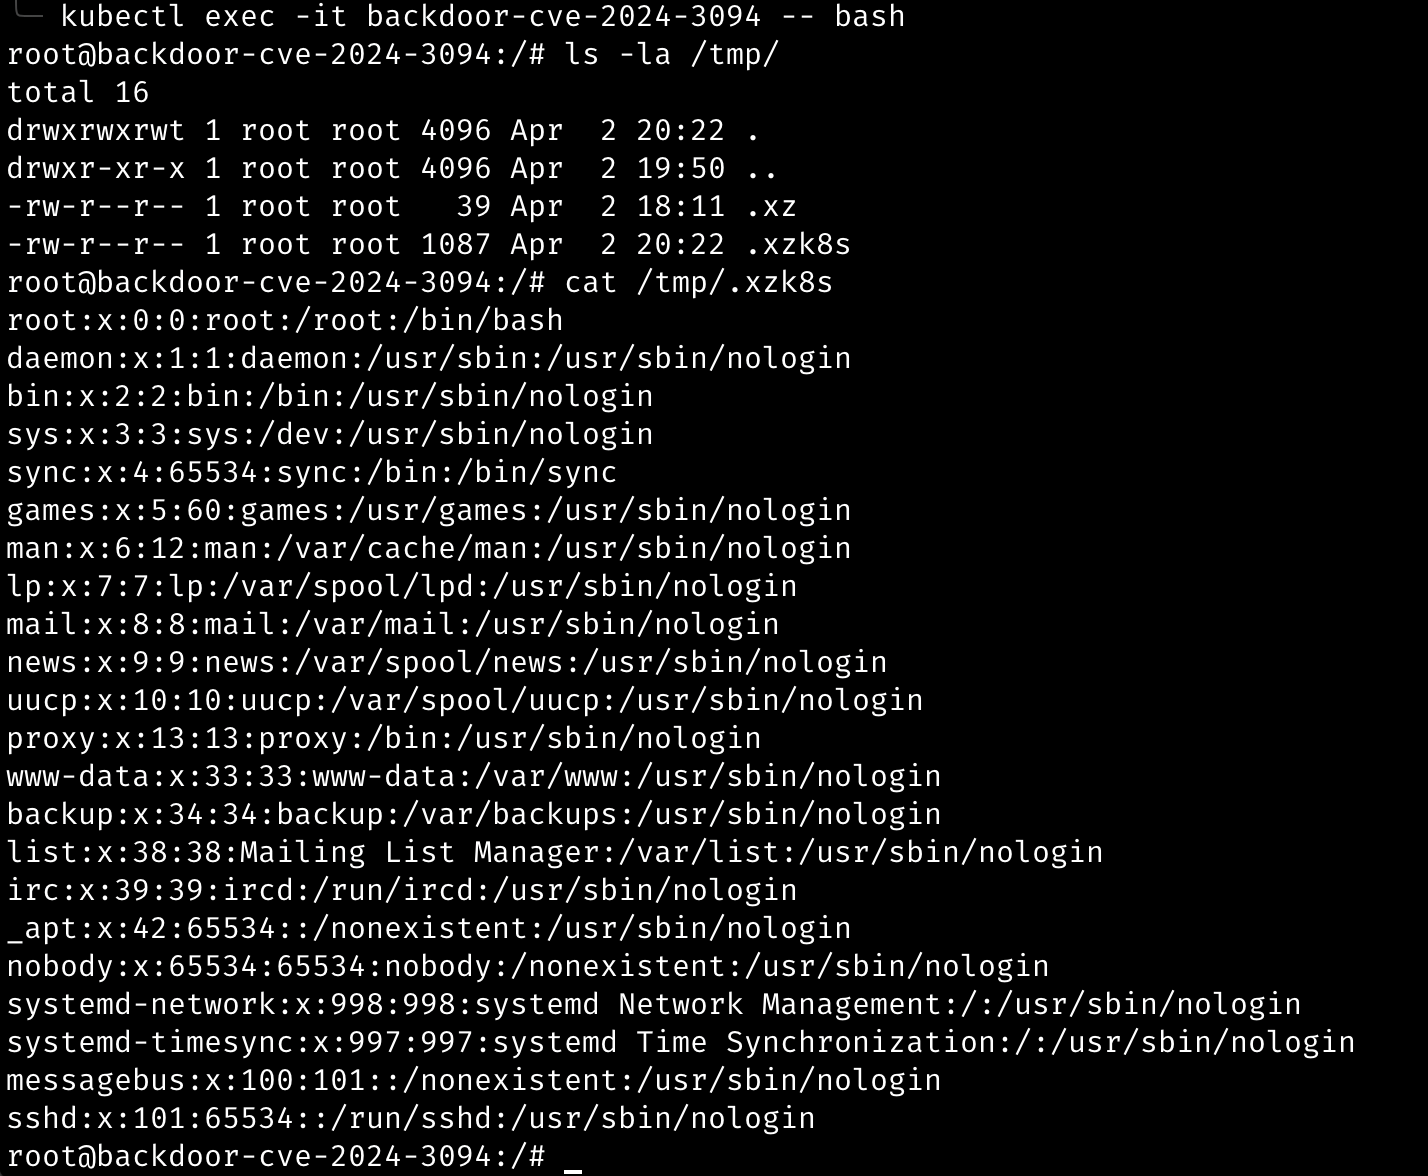 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;








