
 #1
Container breakout techniques, privilege escalation, and sandbox escape testing tools.
Kitploit recommended
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 jpts/cve-2022-0847-dirtypipe-container-breakout
Proof-of-concept exploit for CVE-2022-0847 (DirtyPipe) enabling container breakout via kernel privilege escalation. Includes demonstration and…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
stealthcopter/deepceDocker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
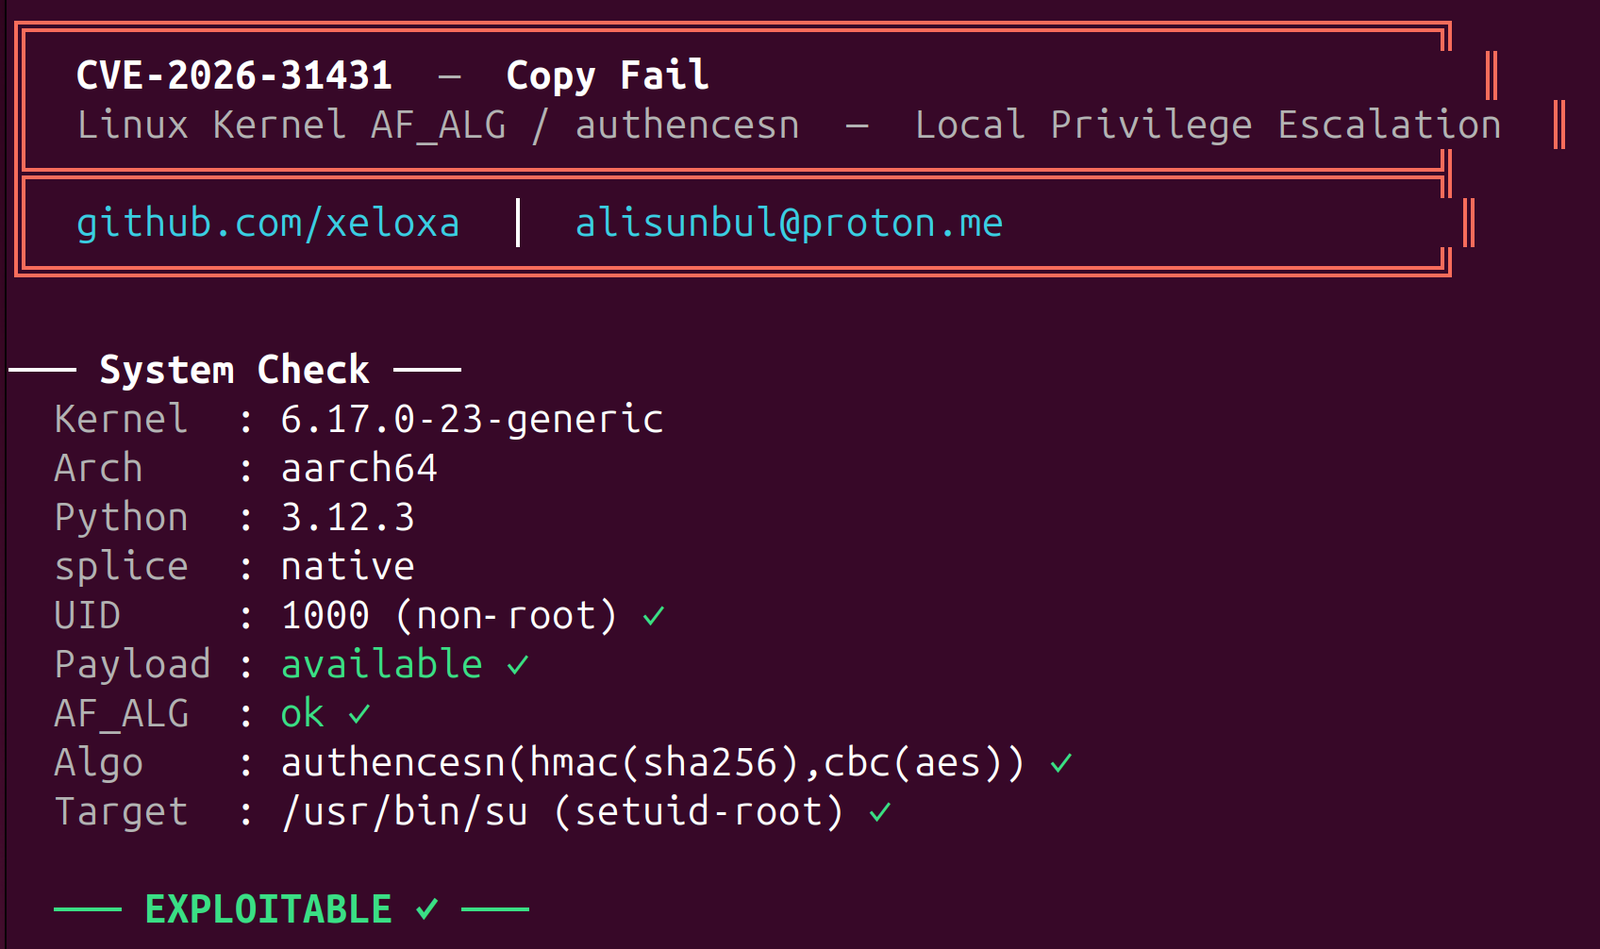 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.






