
 #1
Tools for reviewing system and application configurations for security weaknesses and compliance.
Kitploit recommended

 sibersan/apache_audit_cve-2026-23918
Python toolkit to audit Apache HTTP Server against CVE-2026-23918 (HTTP/2 double-free RCE) and 4 related CVEs. Passive scanner with ALPN verification…
 bjbakker1984/yellowkey-mitigation
PowerShell script that automates the WinRE mitigation workflow for CVE-2026-45585, with verification steps and conditional commit to avoid…
 srkyn/nginx-map-risk-audit
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.
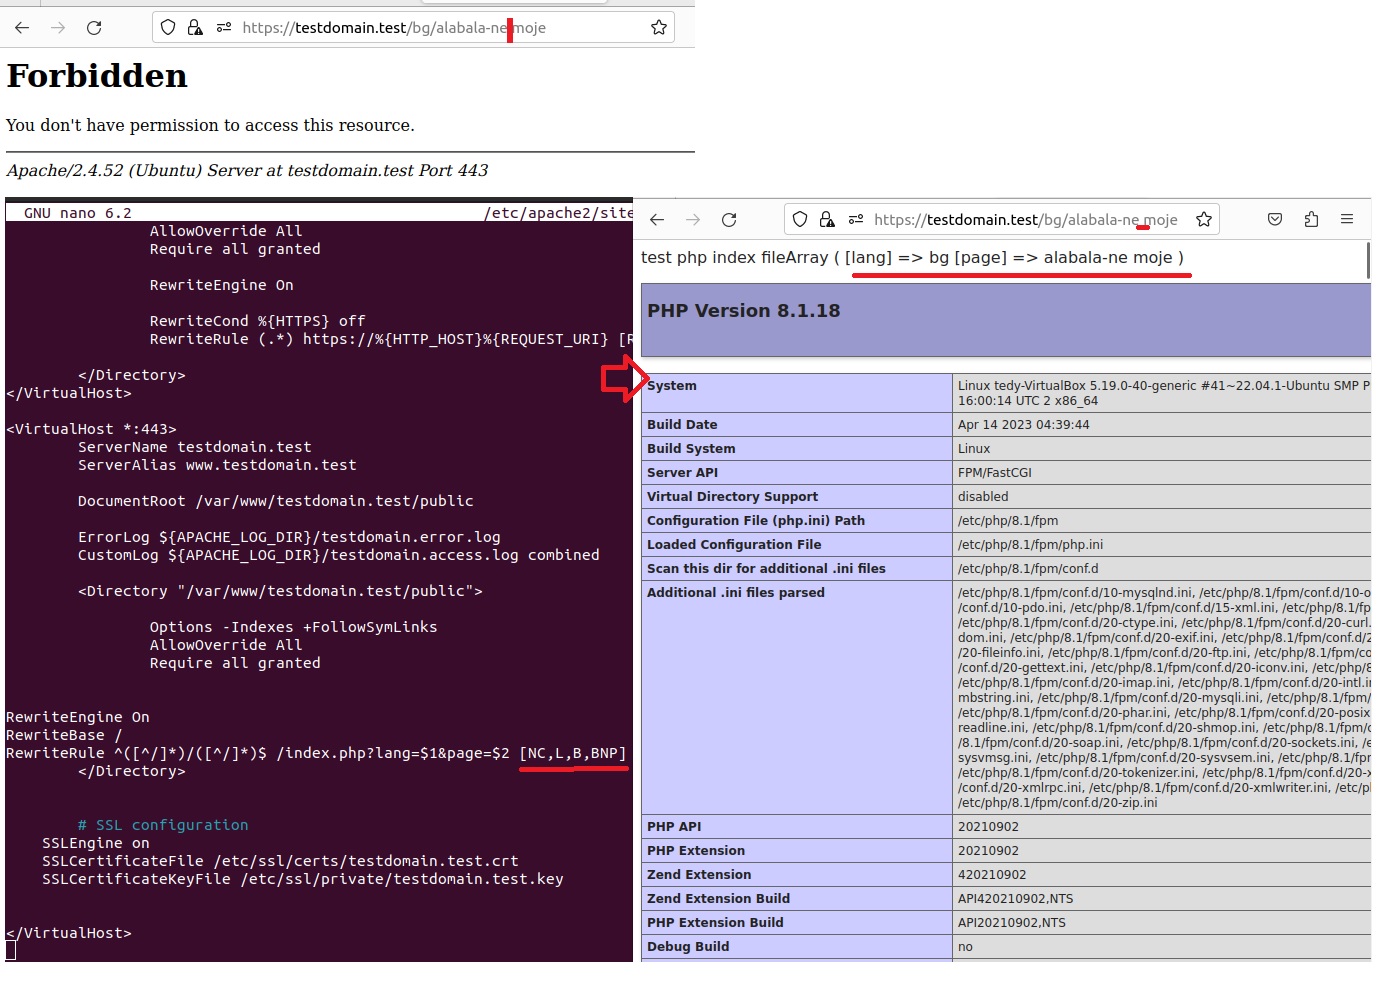 tbachvarova/linux-apache-fix-mod_rewrite-spaceinurl
Fix URL containing SPACES after Apache upgrade CVE-2023-25690
 danielmadsendk/servicenow-cve-2025-11449-cve-2025-11450-mitigation-script
Automated detection and remediation of ServiceNow UI Macro vulnerabilities (CVE-2025-11449, CVE-2025-11450) by encoding sysparm_ parameters to…
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 melonlonmeo/cve-2025-49132
Poc - CVE-2025-49132
 tanarchytan/cve-2021-1675
Fix without disabling Print Spooler
 woltage/cve-2014-6271
Ansible playbook to test remote servers for CVE-2014-6271 (Shellshock) bash vulnerability, enabling automated scanning and verification across…
 rshosting/apache-cve-2026-23918-fix
Upgrade to Apache 2.4.67 to fix CVE-2026-23918 vulneribility
 shoucheng3/asf__karaf_cve-2022-22932_4-3-5
Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 toohau/cve-2025-32462-32463-detection-script-
Critical Sudo Vulnerabilities Let Local Users Gain Root Access on Linux, Impacting Major Distros
 jmaddington/drmm-cve-2020-1350-response
Registry-based mitigation script for CVE-2020-1350 Windows DNS Server RCE vulnerability, applying Microsoft's recommended workaround without server…
 adnansiyat/how-to-patch-cve-2025-32709
Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…
 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…








