
 #1
Tools for reviewing system and application configurations for security weaknesses and compliance.
Kitploit recommended

 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 schnied/cve-2026-98432-mitigation-iptables
Shell scripts that check Linux hosts for CVE-2026-98432 and apply a temporary iptables u32 rule dropping IPv4 TCP packets with IP options, with…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696

 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
 sqzer-x/cve-2026-99999-scanner
Shell script that checks whether a Linux host is affected by CVE-2026-99999 (PwnEscape) and prints or applies the distribution-specific kernel fix.
 omniversetr/omnicheck_cve-2026-98432
Non-destructive checker for CVE-2026-98432 (Linux kernel TCP use-after-free): patch status, exposed listeners and mitigation verification. By…
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
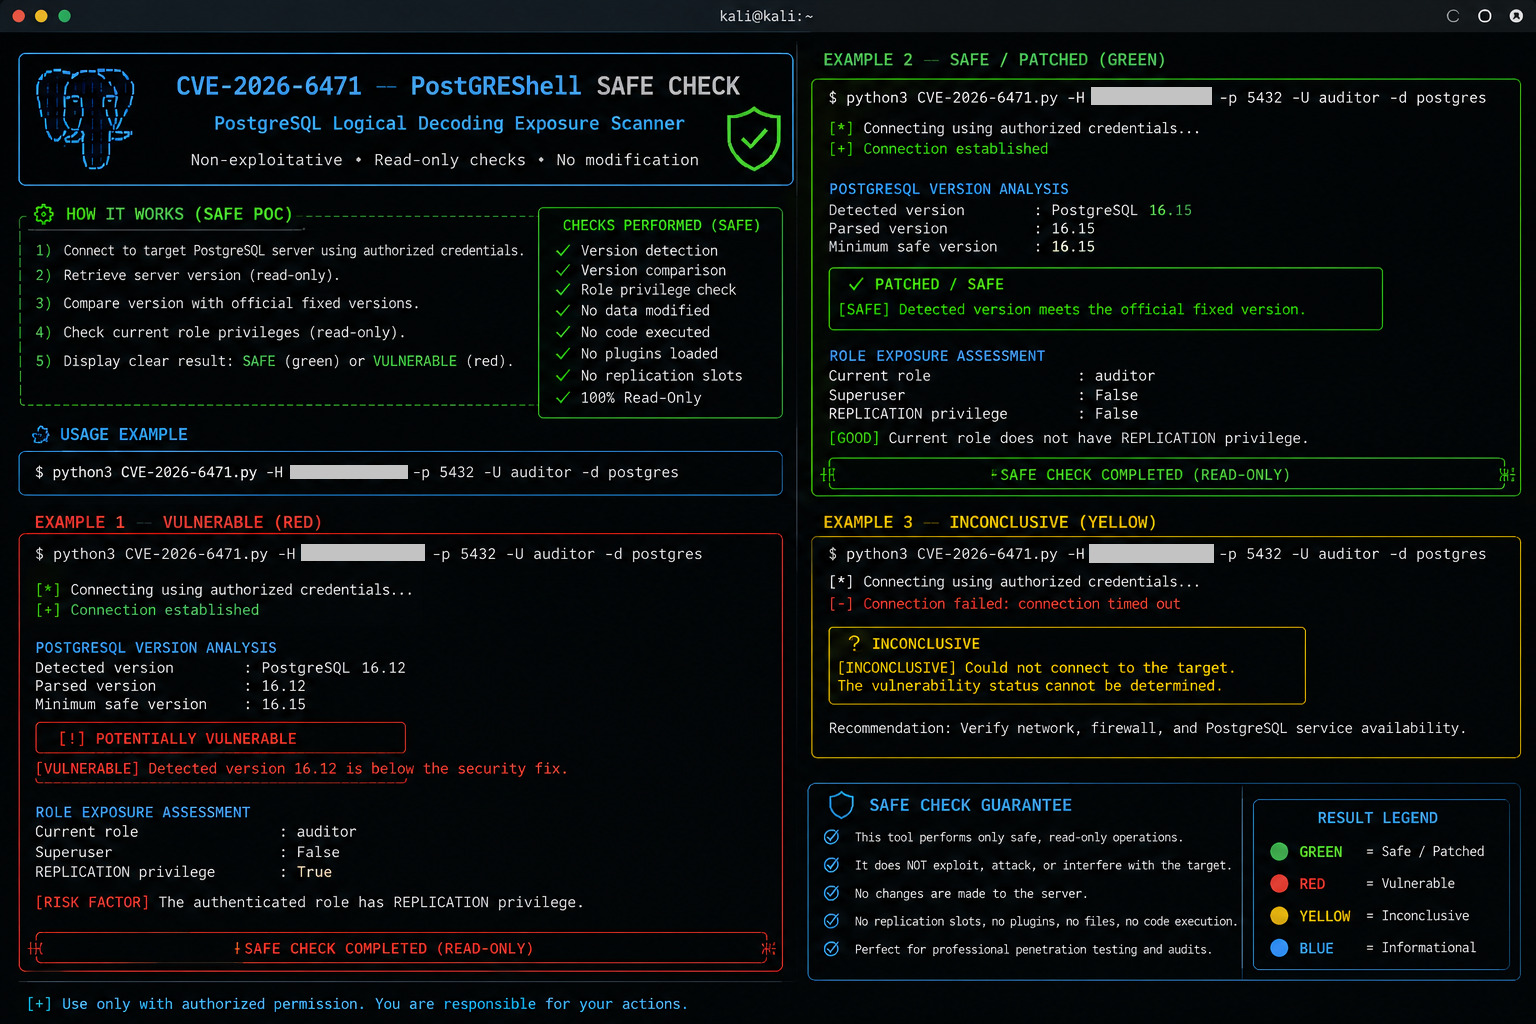 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 xiaoqimikko/log4j-check
log4j 2025/2026 年 7 条「配置静默失效」CVE 自查:按 CVE×模块 判定 4 个模块,结构化解析 log4j2 配置做 applicability 降噪,并算出该升到哪个版本才一次到位(6 条写 2.25.4,但有一条要 2.25.5,而它 Dependabot 报不出来)…
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 konstruktoid/prescryb
MCP server for CVE/config remediation orchestration: SSH inventory, OSV/NVD lookups, CIS/DISA STIG-mapped Ansible playbook suggestions.
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 cybercondor/fix-winverifytrustsignaturevalidationvuln
Fix WinVerifyTrust Signature Validation Vulnerability, CVE-2013-3900, QID-378332
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 mikesplain/cve-2015-0235-cookbook
A chef cookbook to test the GHOST vulnerability
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…








