
 #1
Tools for reviewing system and application configurations for security weaknesses and compliance.
Kitploit recommended
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 tarraschk/cve-2023-36884-checker
Script to check for CVE-2023-36884 hardening
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 eugexo/security-baseline-ubuntu
Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 gquere/cve-2019-6693
Decrypts FortiGate configuration secrets (CVE-2019-6693) for versions below 6.2.0, extracting encrypted passwords and keys from dumped configs using…
 nocoderrandom/sunsetscan
Local-network security auditing with EOL, CVE, device identity, and HTML reports
 penteraio/cve-2022-22948
Scanner for CVE-2022-22948 an Information Disclosure in VMWare vCenter
 synacktiv/cve-2020-9289
Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…
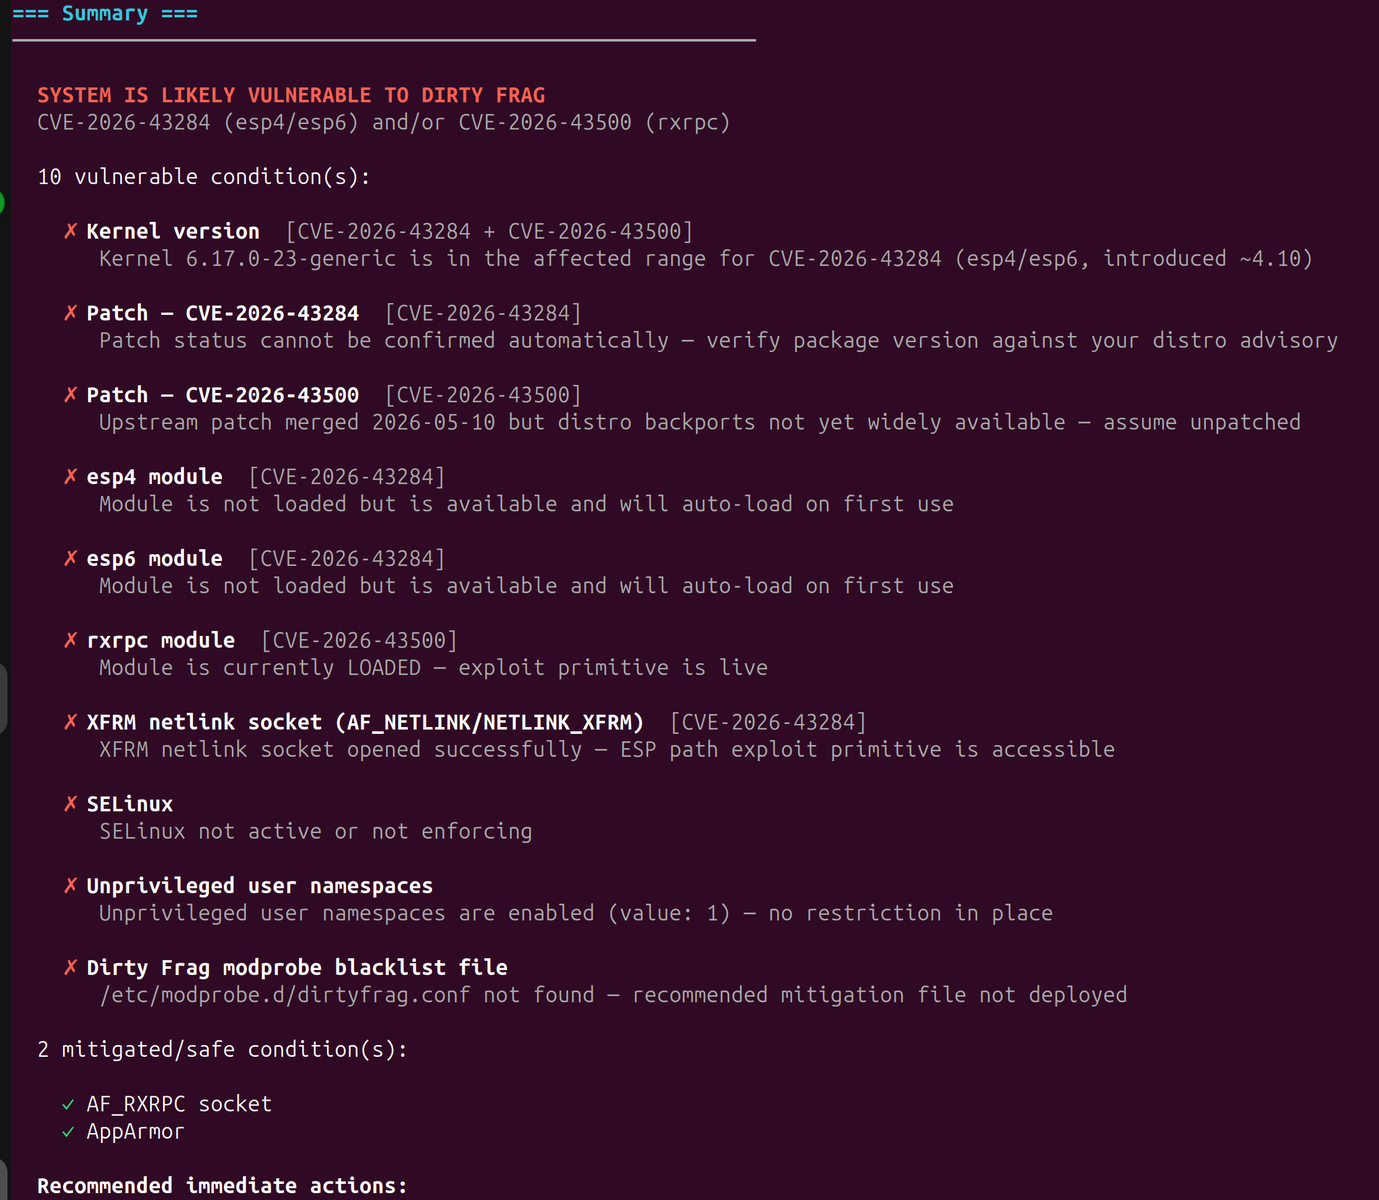 liamromanis101/dirtyfrag-detector
CVE-2026-43284/CVE-2026-43500 'DirtyFrag' Benign patch & mitigation detection script
 nu11secur1ty/linux_hardening_and_security
Collection of Linux hardening scripts and security configurations for system auditing, access control, and defensive posture improvement. Includes…
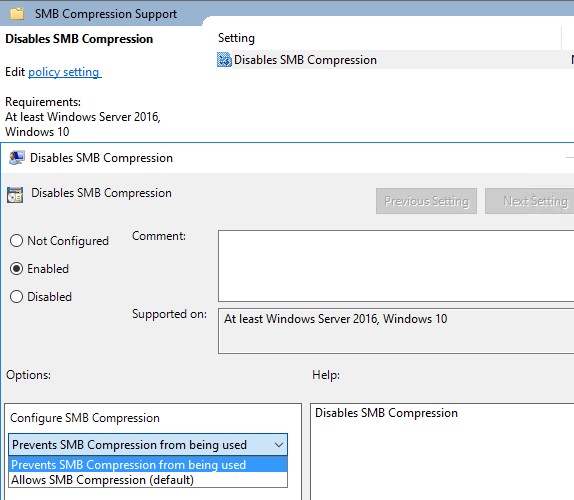 technion/disablesmbcompression
CVE-2020-0796 Flaw Mitigation - Active Directory Administrative Templates
 yandex-cloud-examples/yc-mk8s-copy-fail-mitigation
DaemonSet для митигации уязвимости CVE-2026-31431 (Copy Fail)
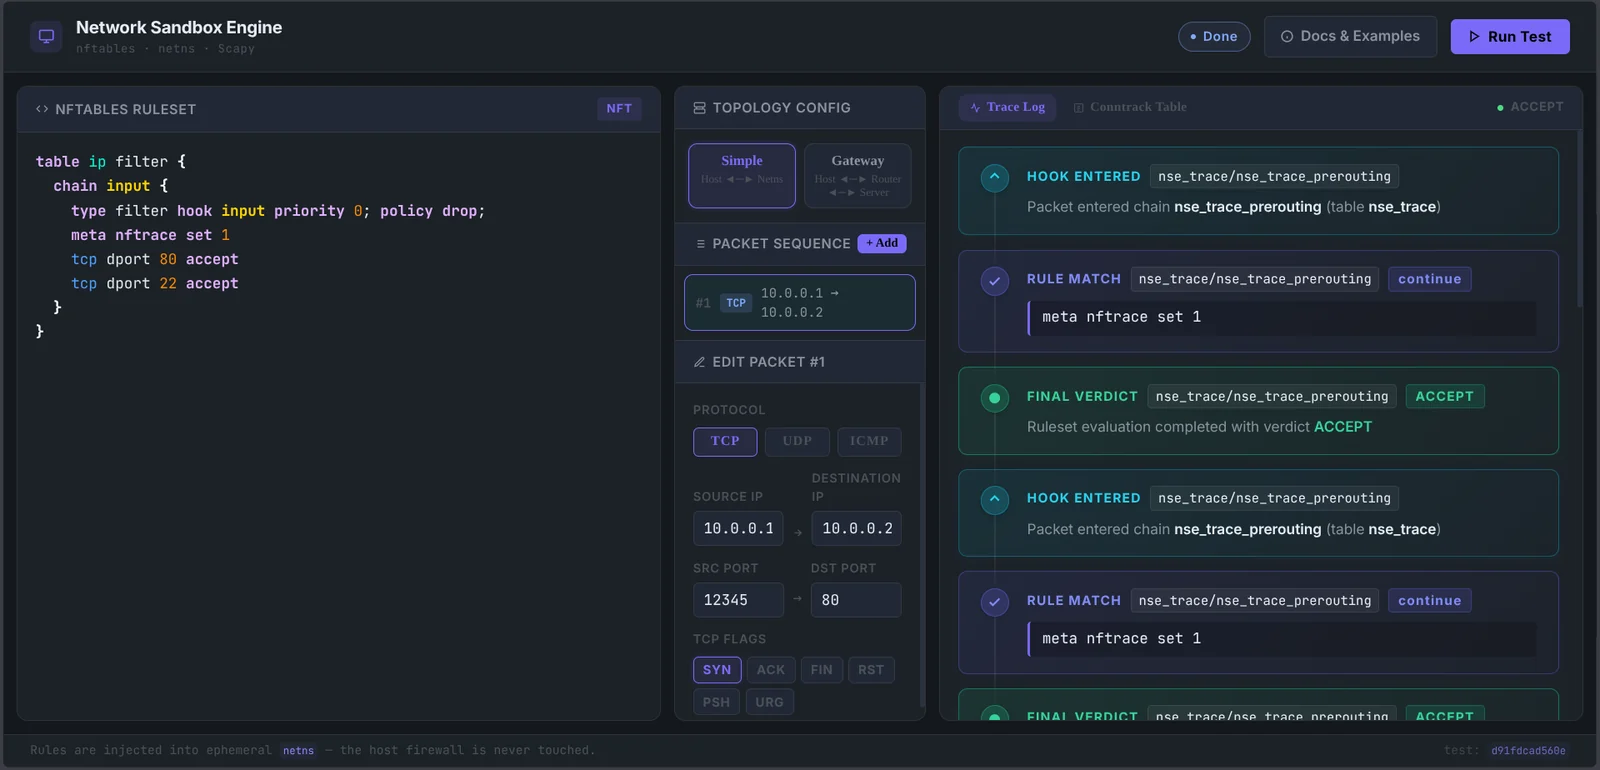 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
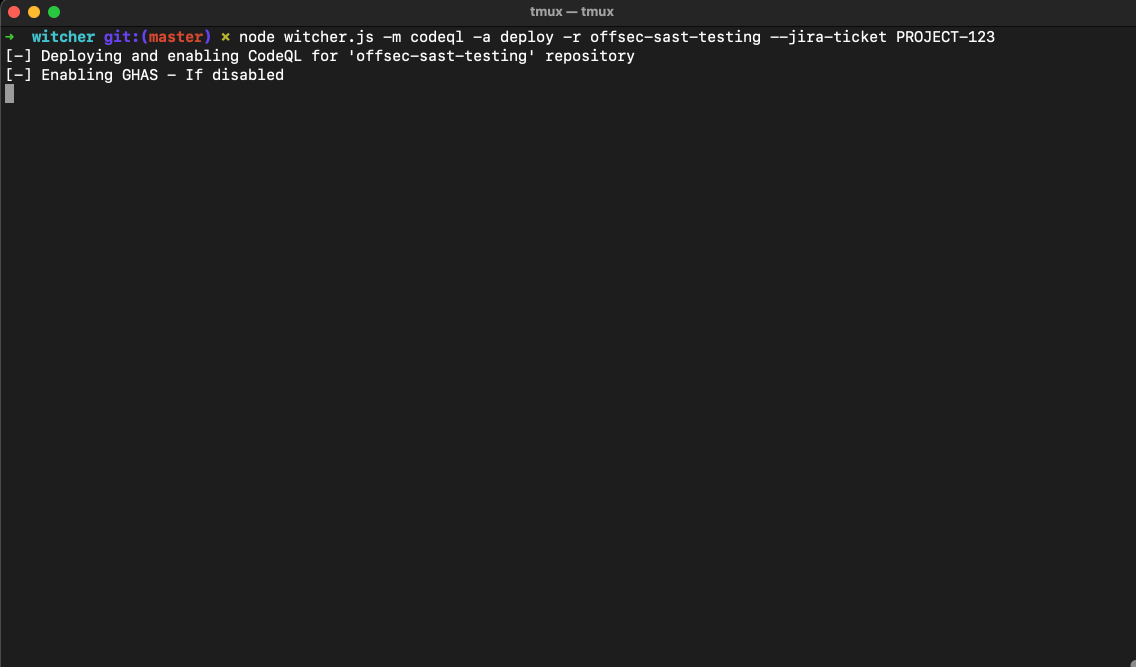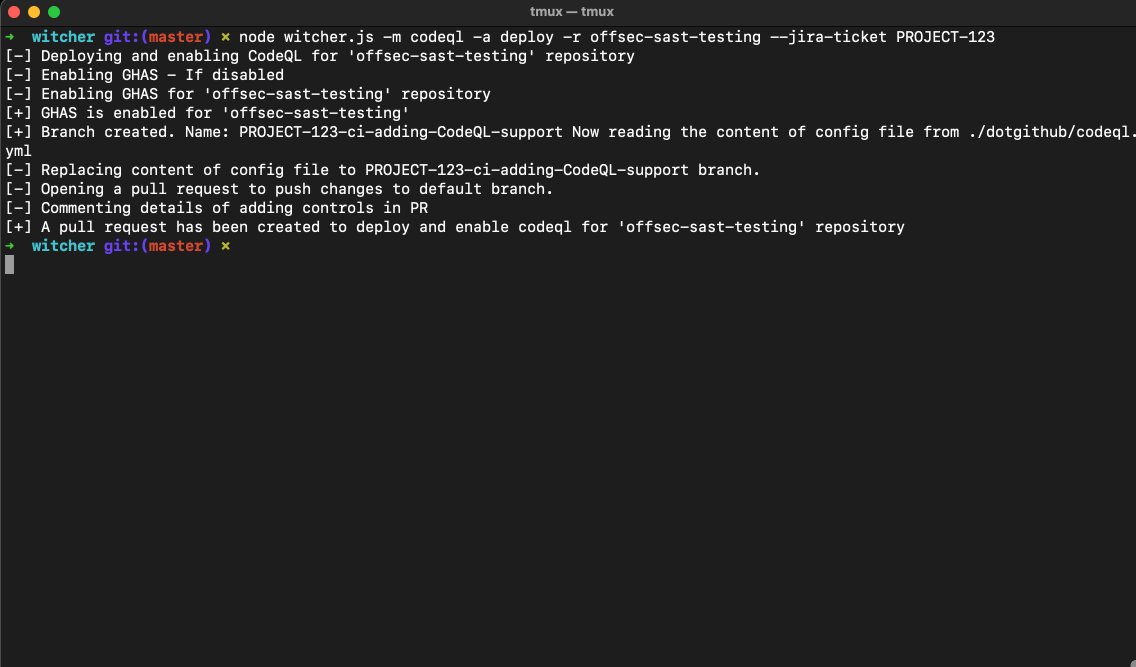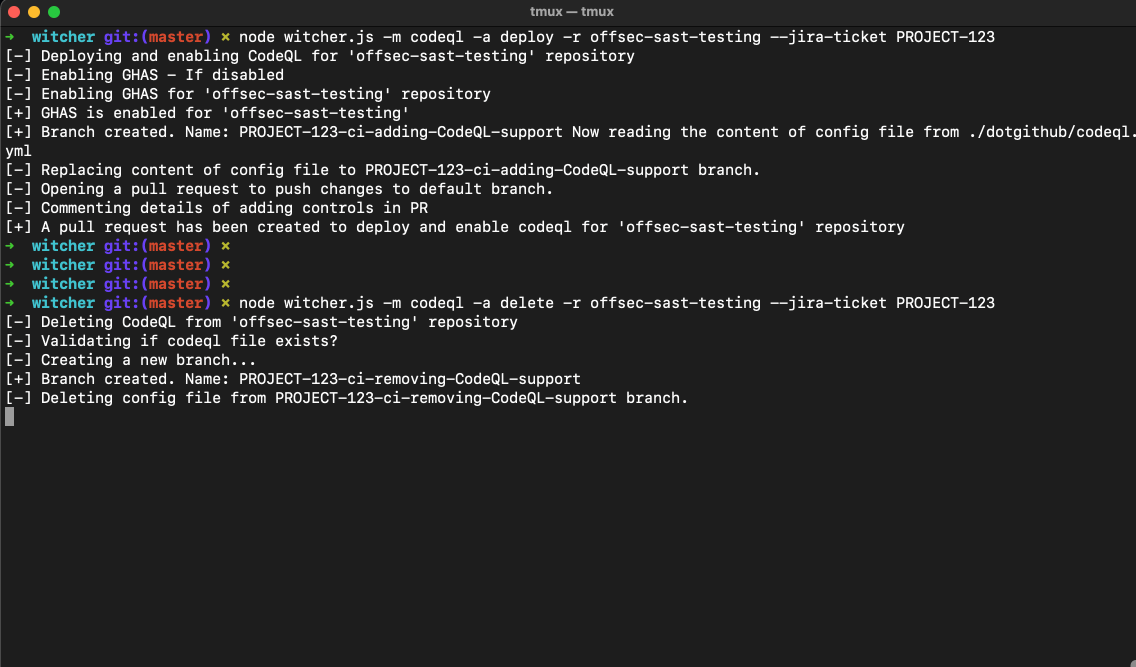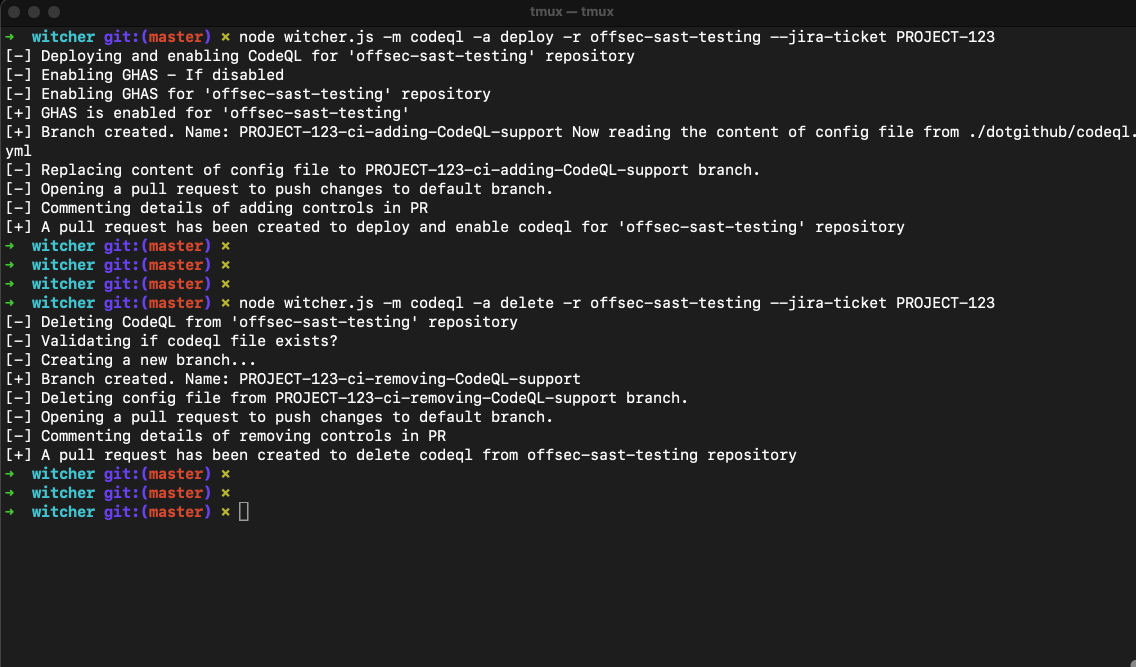 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 adriyansyah-mf/centralizedfirewall
provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations








