
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
 weaselsec/godpotato-aggressor-script
Cobalt Strike Aggressor script that automates Windows service-account-to-SYSTEM privilege escalation via GodPotato during red team operations.
 machine1337/win-rat
A Fully Undectable RAT for Windows that bypass every kind of Antivirus Protections and will give u a CMD shell in your terminal
 icyguider/newpowerdns
Updated version of PowerDNS by @domchell. Adds support for transfers over DNS A records and a few other useful features.
 mr-xn/cve-2024-36401
Remote Code Execution (RCE) Vulnerability In Evaluating Property Name Expressions with multies ways to exploit
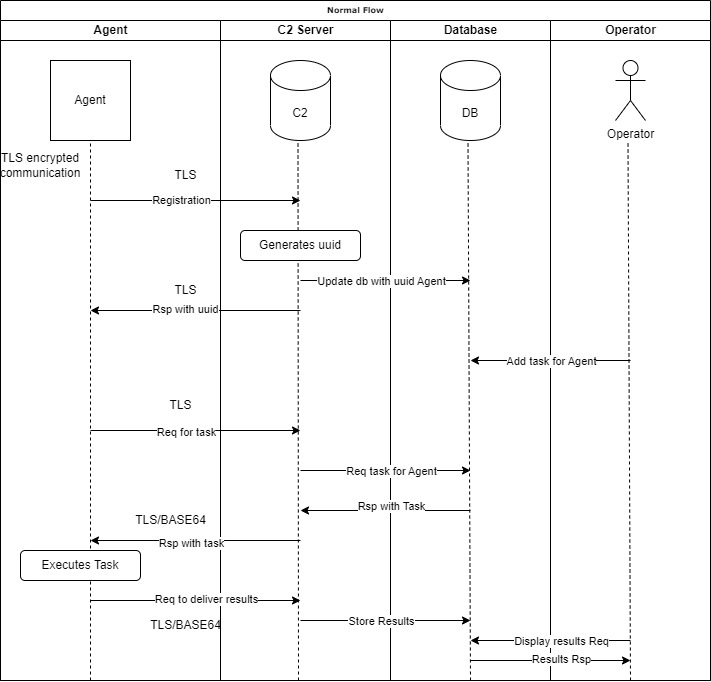 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 vikramaditya015/samsung-android-lpe
Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 i5n0rth/cve-2023-33246
Exploit for CVE-2023-33246 in Apache RocketMQ. Modifies configuration properties to execute arbitrary commands on vulnerable servers, enabling remote…
 forcefledgling/cve-2023-22518
Improper Authorization Vulnerability in Confluence Data Center and Server
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 1135/solr_exploit
Apache Solr远程代码执行漏洞(CVE-2019-0193) Exploit
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 vin01/poc-proxycommand-vulnerable
Proof of conept to exploit vulnerable proxycommand configurations on ssh clients (CVE-2023-51385)
 bishopfox/joro
A collaborative web exploitation framework.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 nopbrick/seeproxy
Golang reverse proxy with CobaltStrike malleable profile validation.








