
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended

 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 flatpak/flatpak
Linux application sandboxing and distribution framework
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
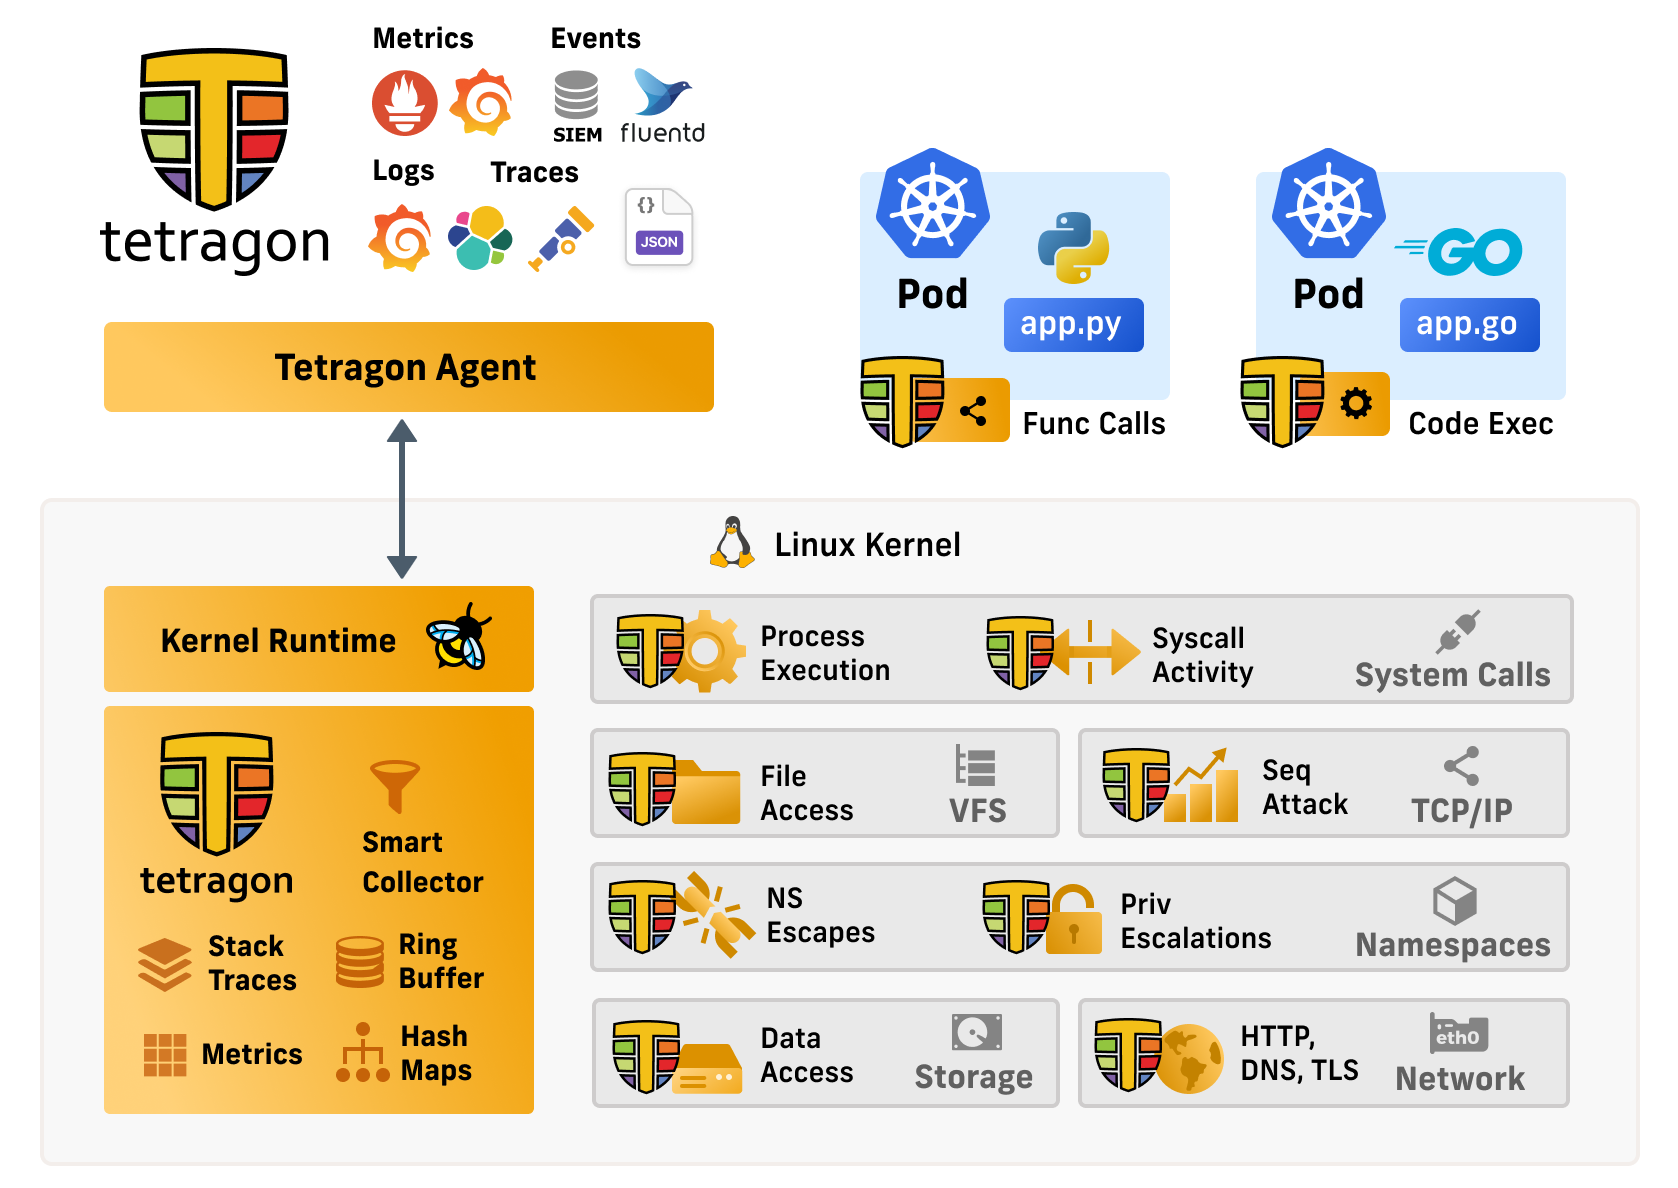 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
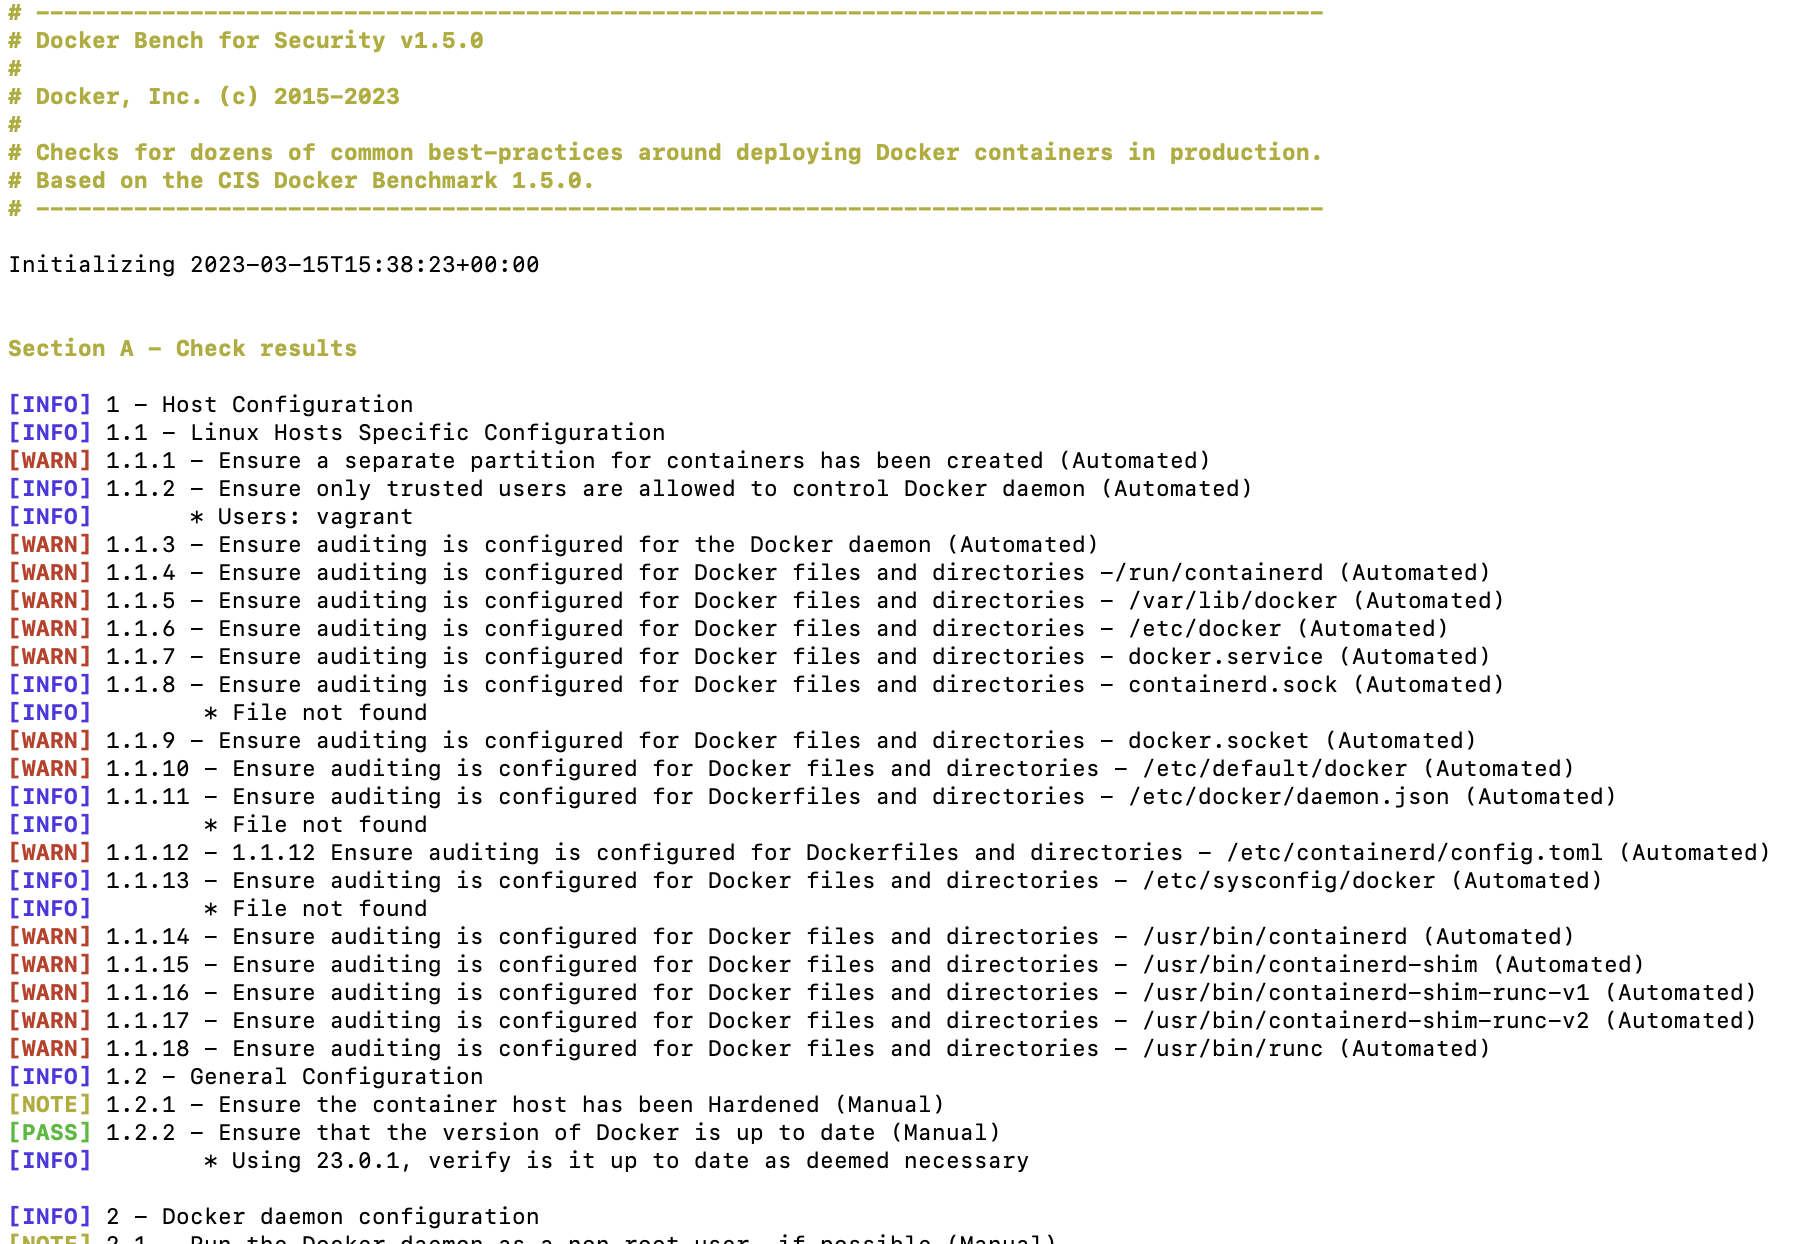 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
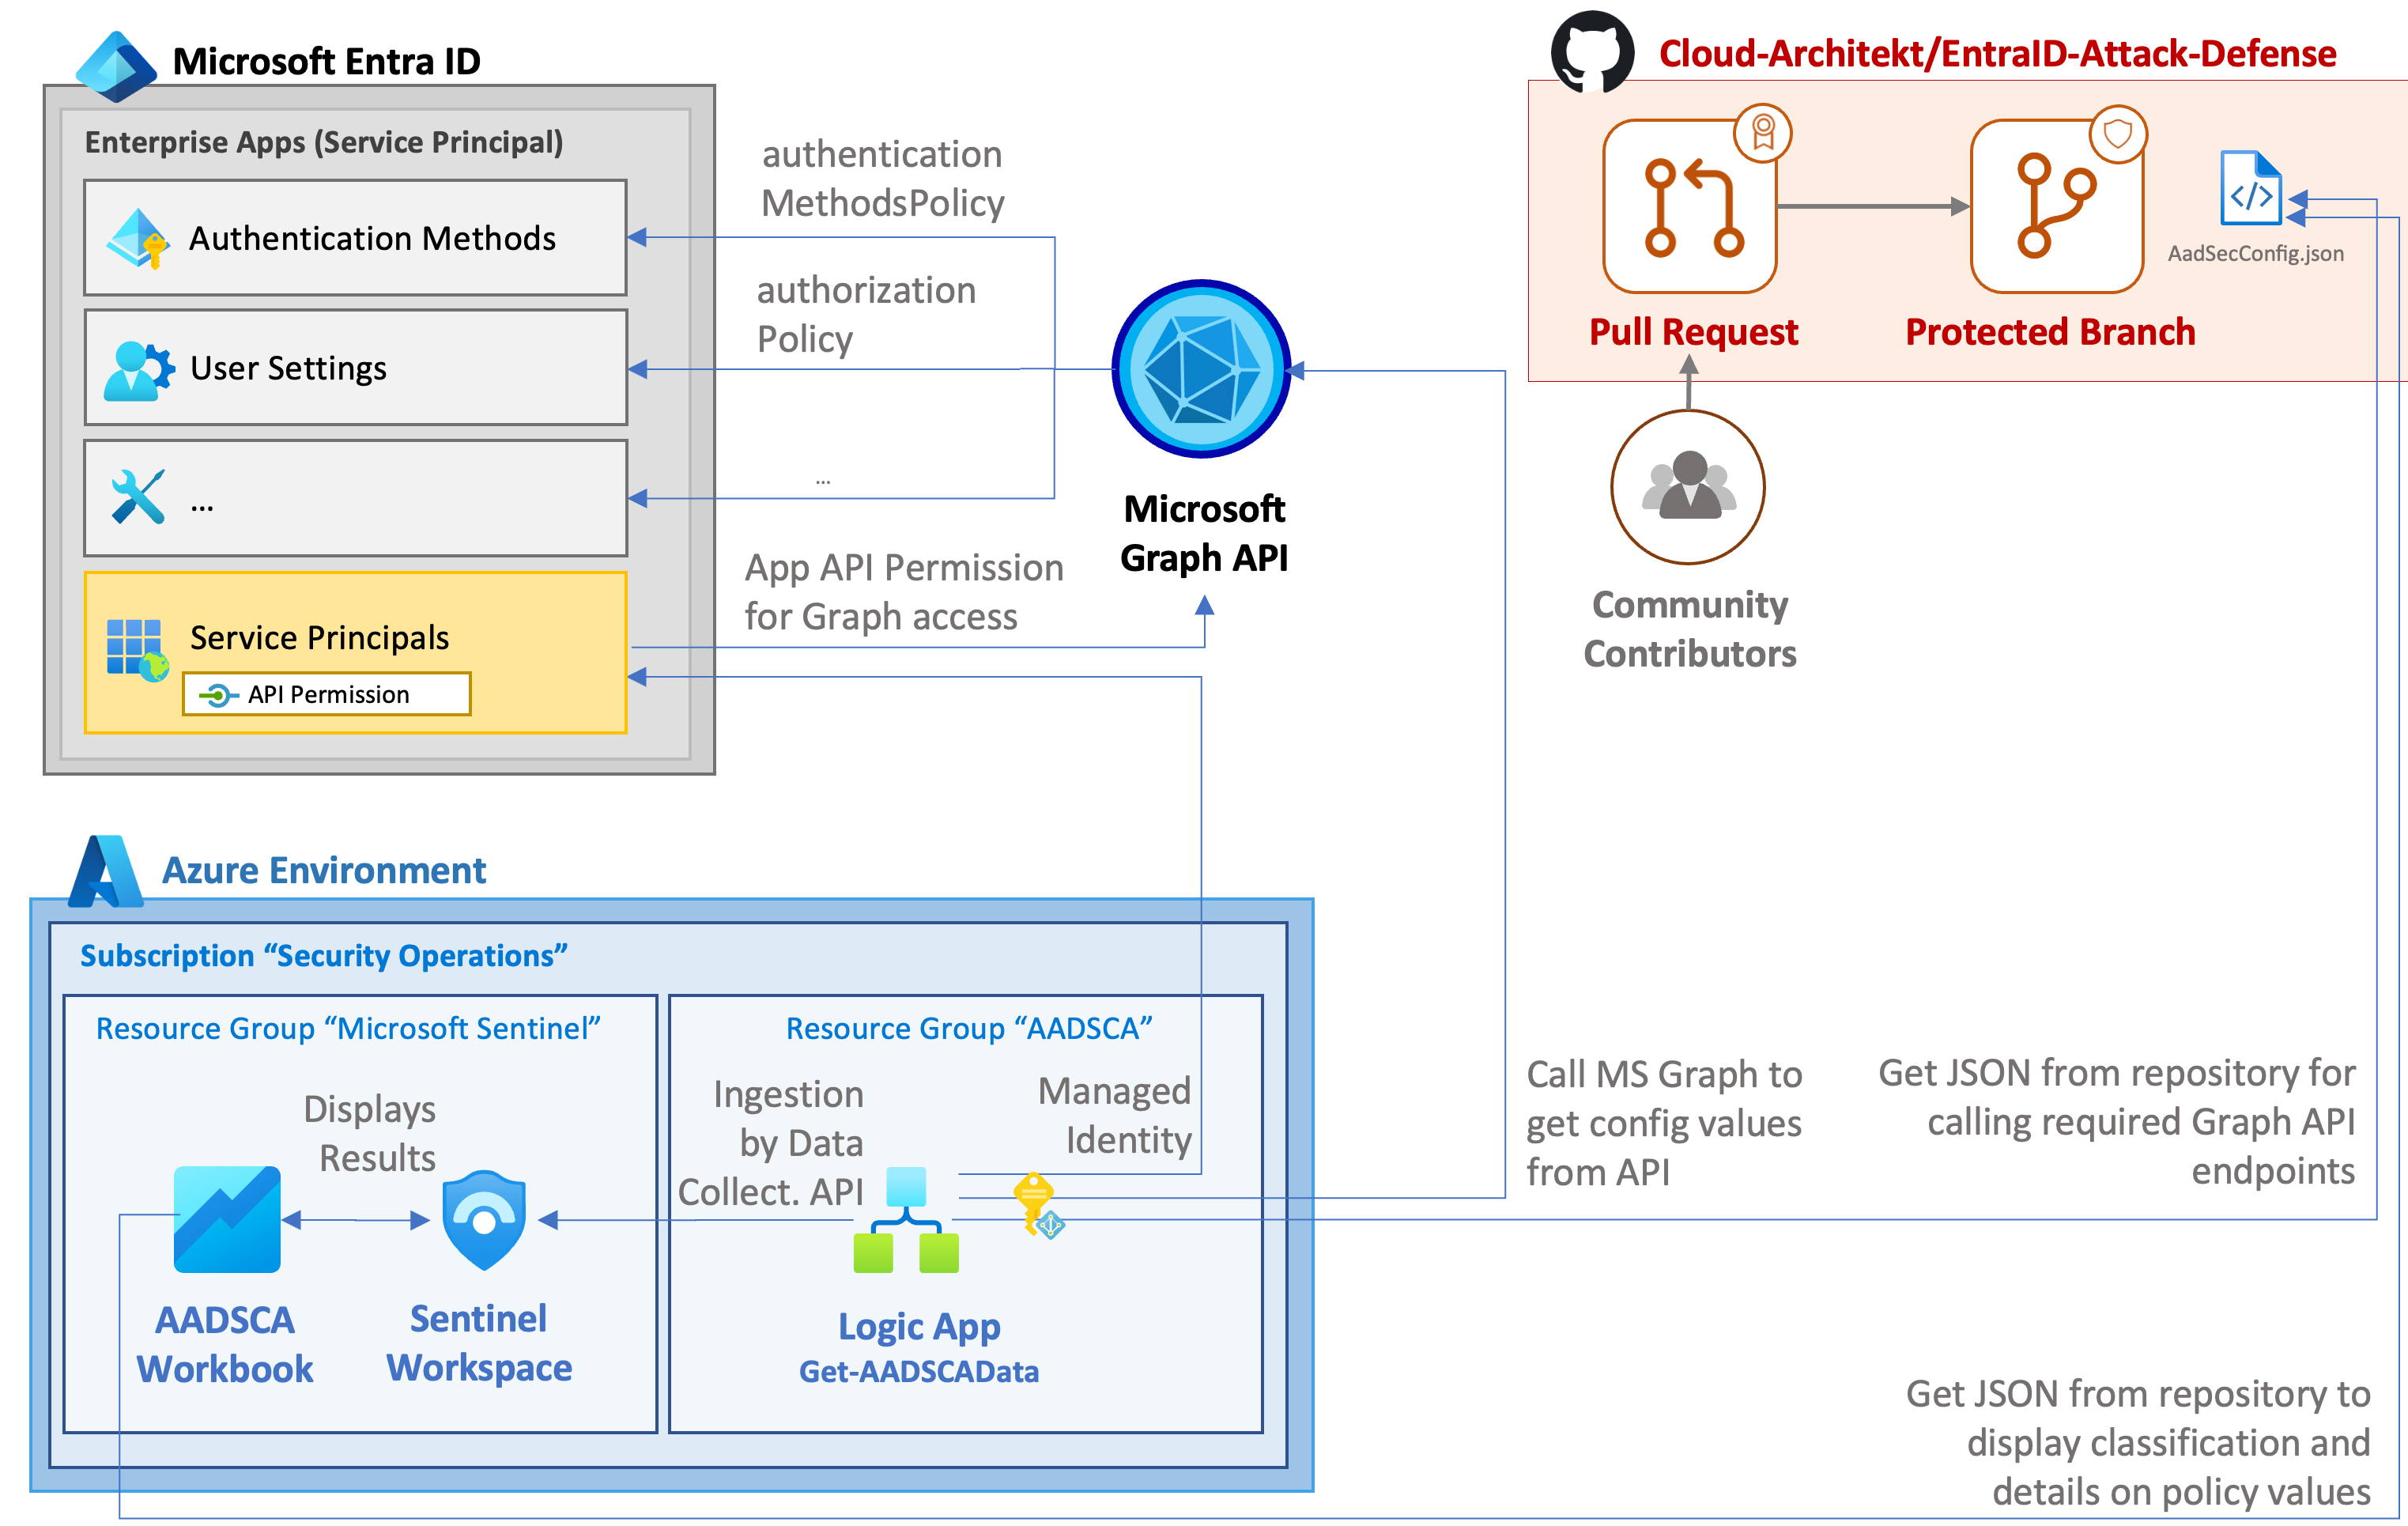 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 aquasecurity/tracee
Linux Runtime Security and Forensics using eBPF
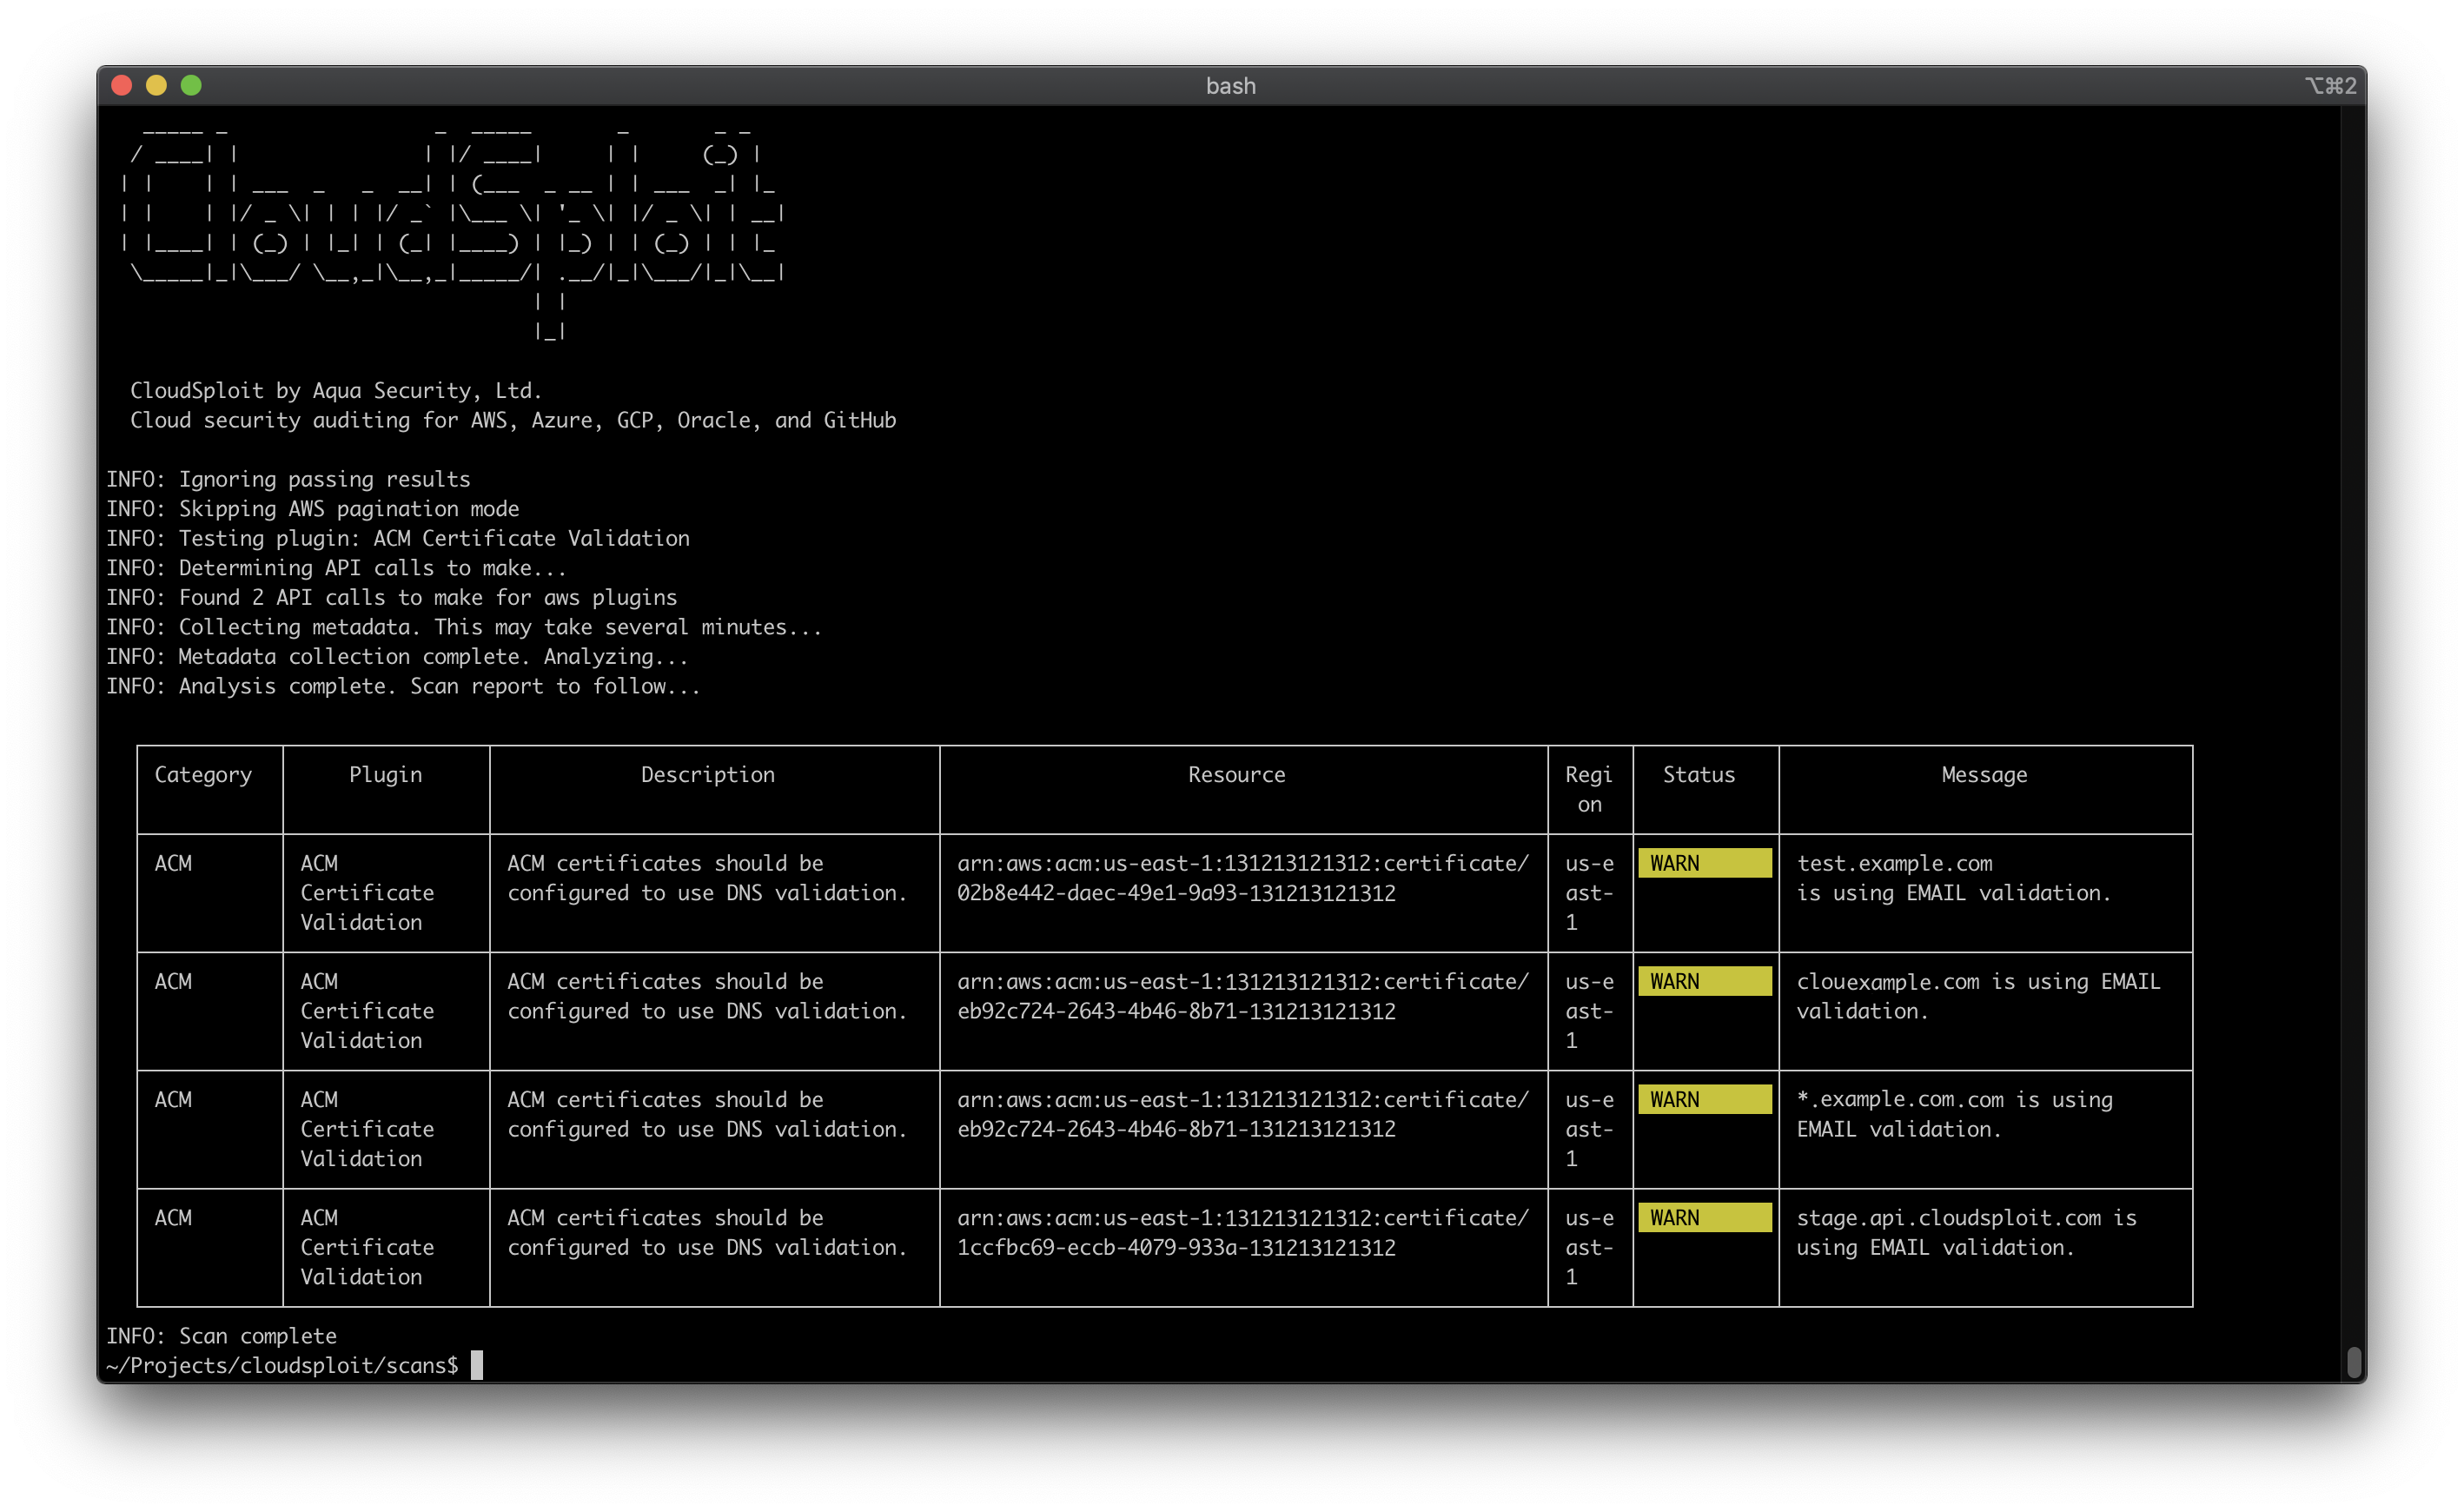 aquasecurity/cloudsploit
Multi-cloud security posture scanner that audits AWS, Azure, GCP, and OCI for misconfigurations, compliance violations (HIPAA, PCI, CIS), and…
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…








