
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554
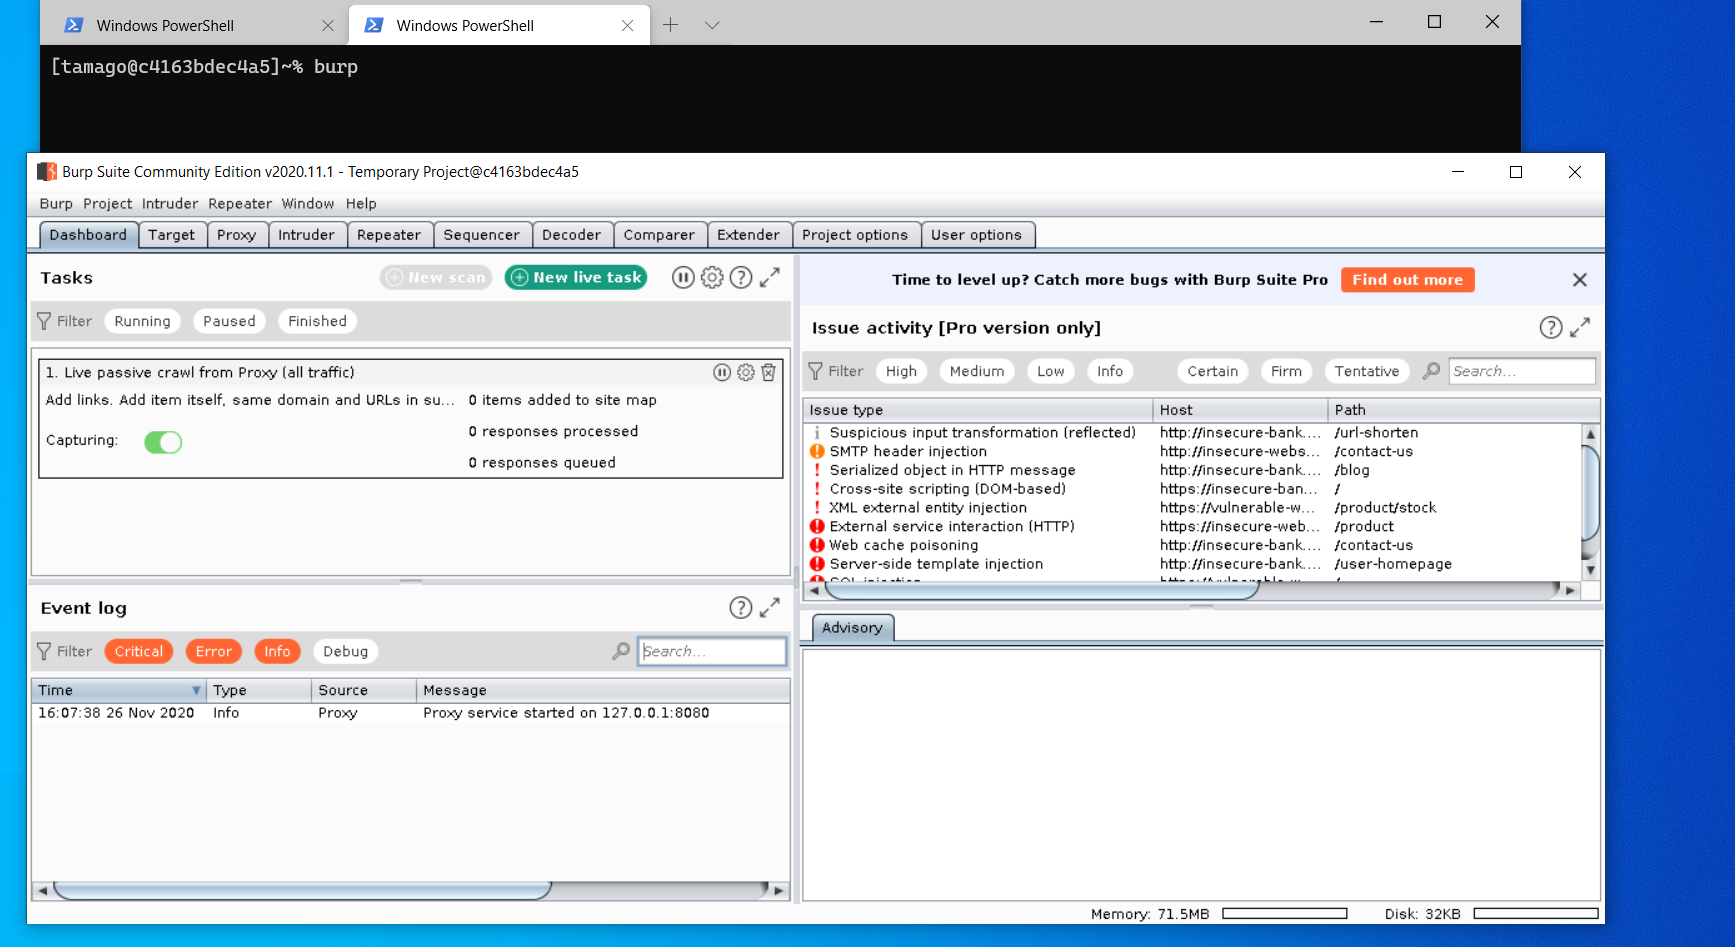 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
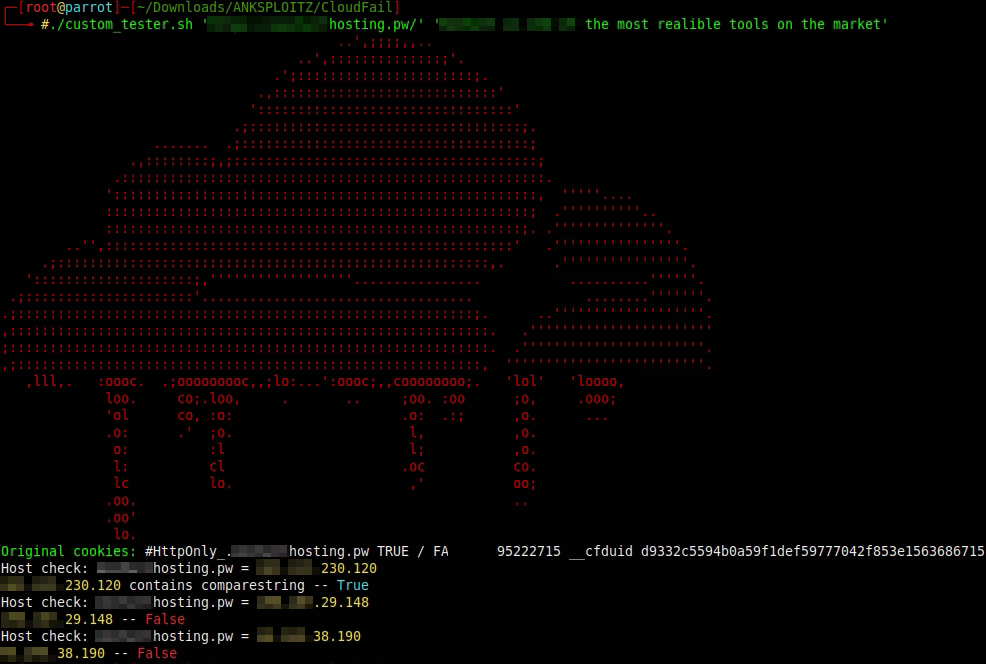 ank1036official/cloudcheck
Checks using a test string if a Cloudflare DNS bypass is possible using CloudFail.
 cashwilliams/cve-2019-14287-demo
This is a container built for demonstration purposes that has a version of the sudo command which is vulnerable to CVE-2019-14287
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.
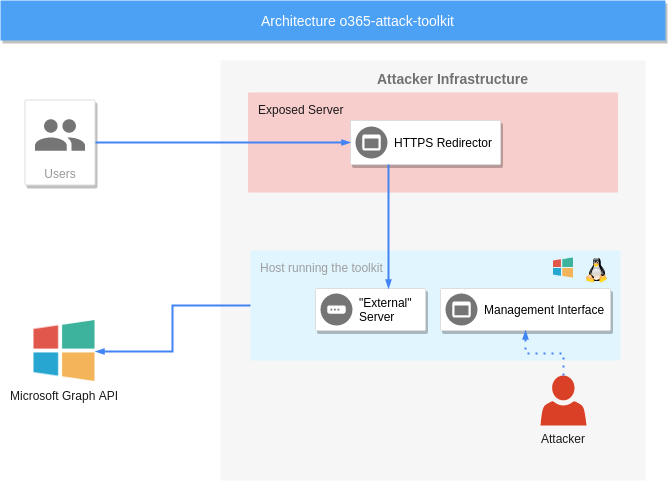 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
 medicean/vulapps
快速搭建各种漏洞环境(Various vulnerability environment)
 rosehgal/dockerent
The only open-source tool to analyze vulnerabilities and configuration issues with running docker container(s) and docker networks.
 securityftw/cs-suite
Cloud Security Suite - One stop tool for auditing the security posture of AWS/GCP/Azure infrastructure.
 nccgroup/sfpoldevchk
Salesforce Policy Deviation Checker
 tmobile/pacbot
PacBot (Policy as Code Bot)
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 cyberharsh/shellbash-cve-2014-6271
Docker-based lab environment for exploiting Shellshock (CVE-2014-6271) via CGI scripts, demonstrating remote command injection through crafted HTTP…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 summitroute/aws_exposable_resources
Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…








