
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 taroballzchen/cve-2023-28432-metasploit-scanner
MinIO Information Disclosure Vulnerability scanner by metasploit
 1w4y/ingressnightmare-rce-poc
PoC for CVE-2025-1974: Critical RCE in Ingress-NGINX (<v1.12.1) via unsafe config injection. Exploitable from the pod network without credentials,…
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 magpieryl/cve-2024-3094-backdoor-env-container
This is a container environment running CVE-2024-3094 sshd backdoor instance, working with https://github.com/amlweems/xzbot project. IT IS NOT…
 excellencedev/cve-2018-19629
Hyland Perceptive Content Server - Denial of Service
 dima2021/cve-2022-42889-text4shell
Docker-based lab environment to demonstrate and test the CVE-2022-42889 (Text4Shell) remote code execution vulnerability in Apache Commons Text.
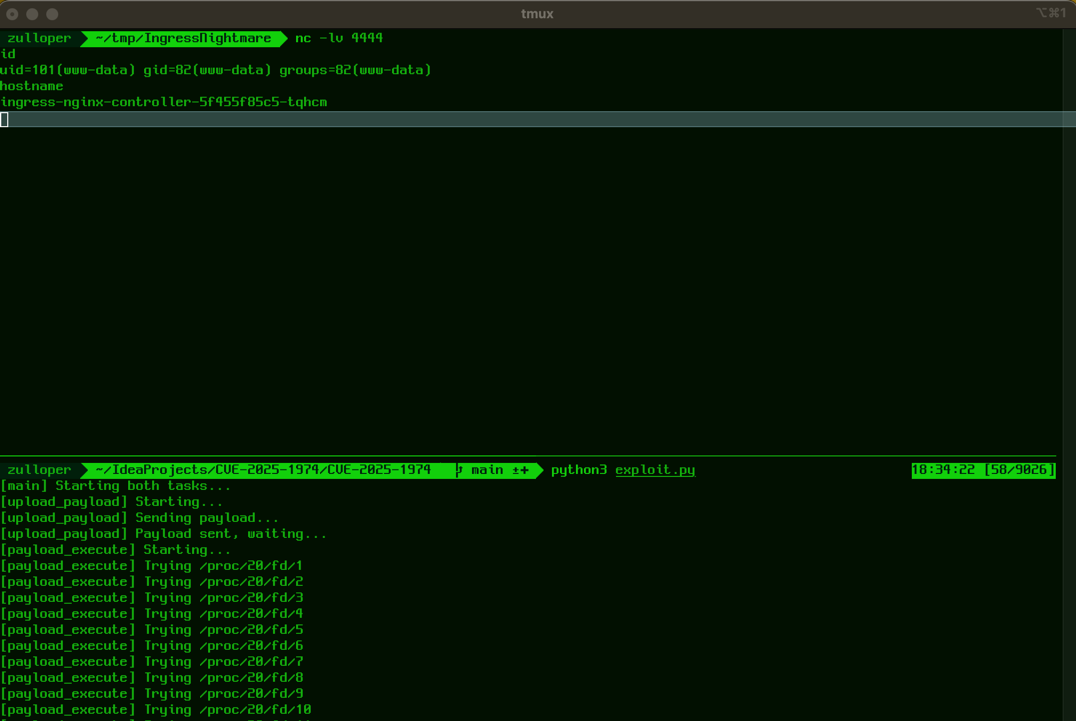 zulloper/cve-2025-1974
CVE-2025-1974 PoC 코드
 shoucheng3/apache__dolphinscheduler_cve-2022-26884_2-0-5
Proof-of-concept exploit for CVE-2022-26884 targeting Apache DolphinScheduler, enabling remote code execution via crafted requests to the workflow…
 rockmelodies/bentoml_cve-2025-54381
Ai相关
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 freshdemo/apachestruts-cve-2018-11776
Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…
 cved-sources/cve-2018-9206
cve-2018-9206
 cved-sources/cve-2018-19207
Docker container providing a vulnerable environment for CVE-2018-19207, designed for practicing exploitation and vulnerability analysis in a…
 cved-sources/cve-2017-1000117
cve-2017-1000117
 cved-sources/cve-2016-8869
Dockerized vulnerable environment for CVE-2016-8869 (Joomla privilege escalation) used for security training and exploitation practice.
 cved-sources/cve-2015-5602
Docker container with CVE-2015-5602 for practicing privilege escalation in a controlled environment. Part of the Cved framework for managing…
 cved-sources/cve-2015-3306
cve-2015-3306








