
 #1
Binary exploitation techniques, ROP chains, heap exploitation, format strings, and memory corruption research.
Kitploit recommended

 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 theofficialflow/h-encore
Fully chained kernel exploit for the PS Vita on firmwares 3.65-3.68
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 externalist/exploit_playground
Analysis of public exploits or my 1day exploits
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 nac-l/mergen
Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.
 lunixbochs/patchkit
binary patching from Python
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 ynwarcs/cve-2024-38063
poc for CVE-2024-38063 (RCE in tcpip.sys)
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 rip1s/cve-2018-8120
CVE-2018-8120 Windows LPE exploit
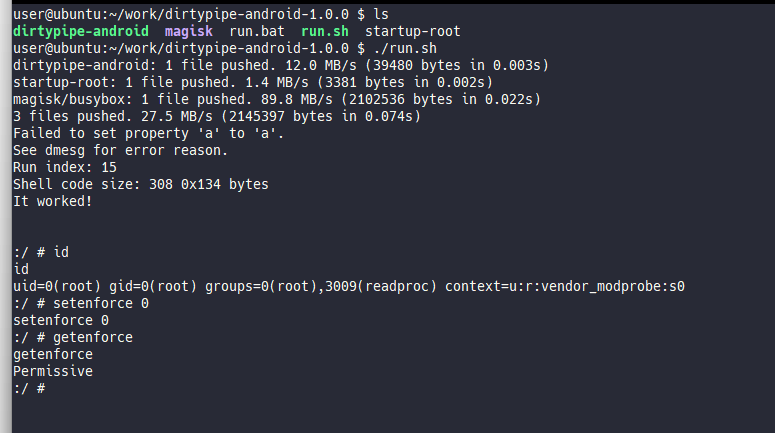 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
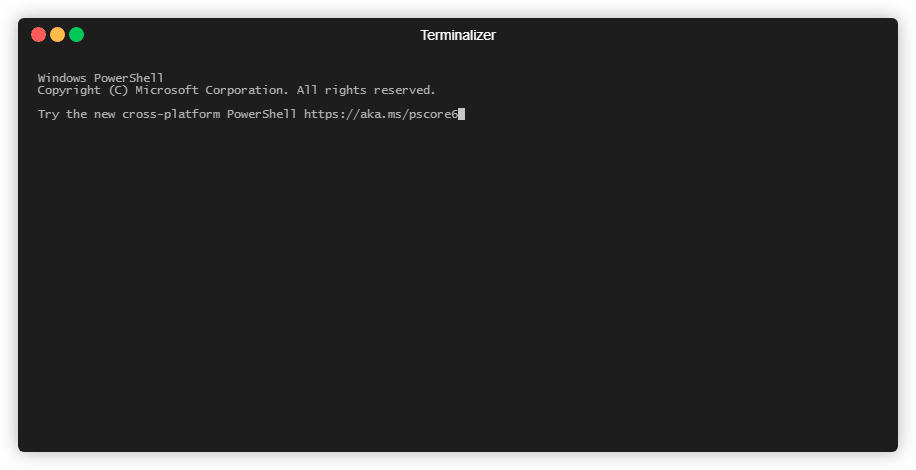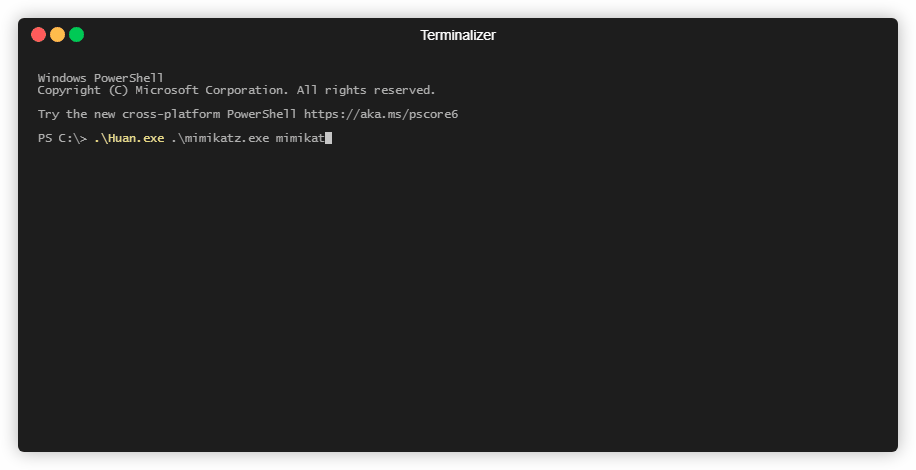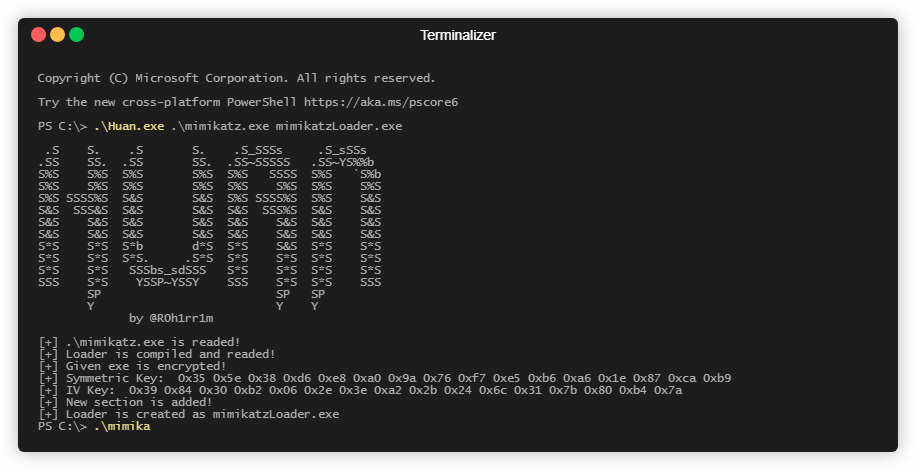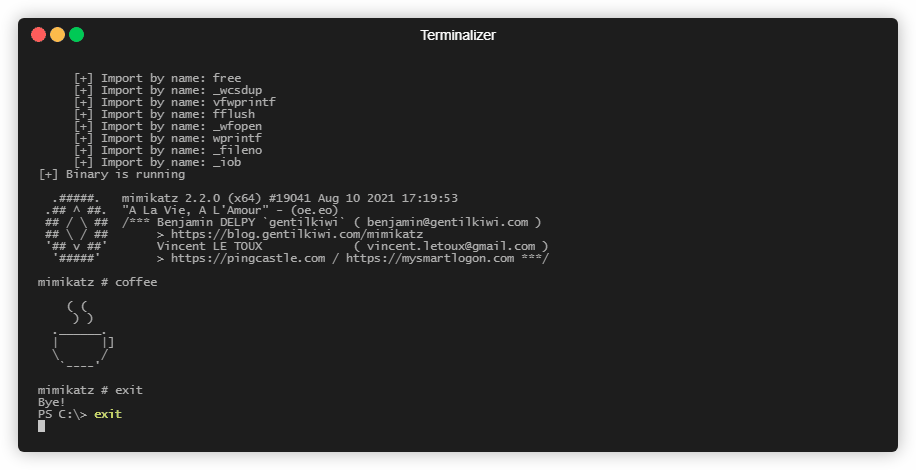 frkngksl/huan
Encrypted PE Loader Generator








