
 #1
Binary exploitation techniques, ROP chains, heap exploitation, format strings, and memory corruption research.
Kitploit recommended
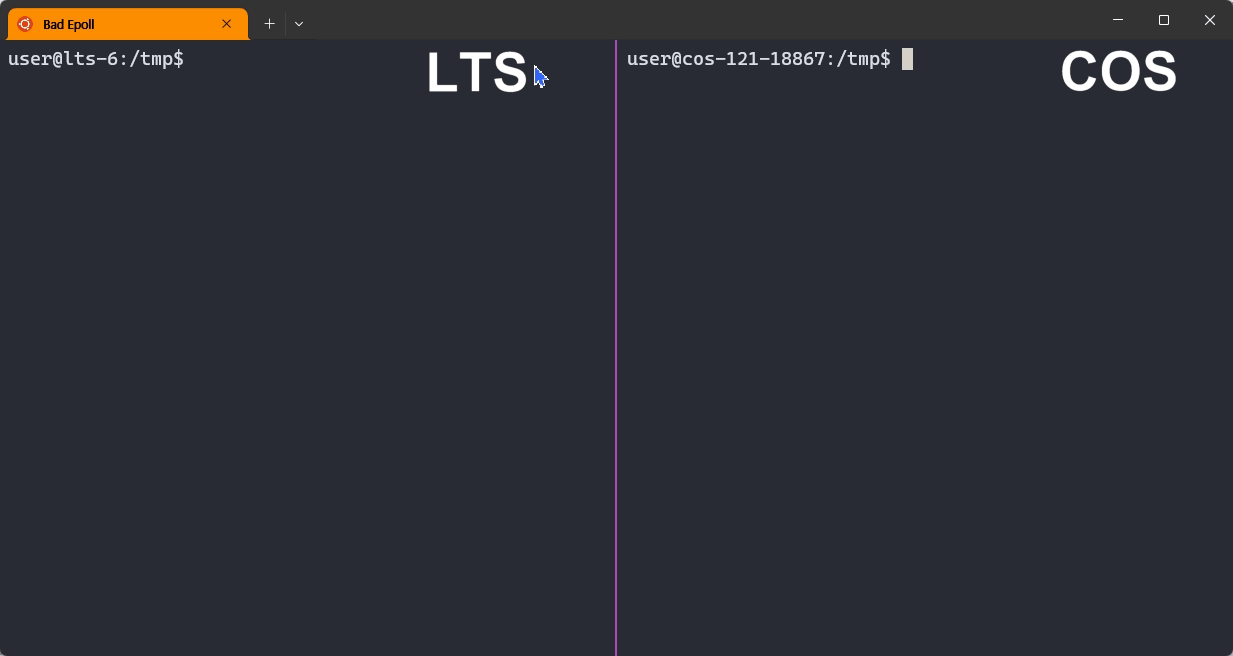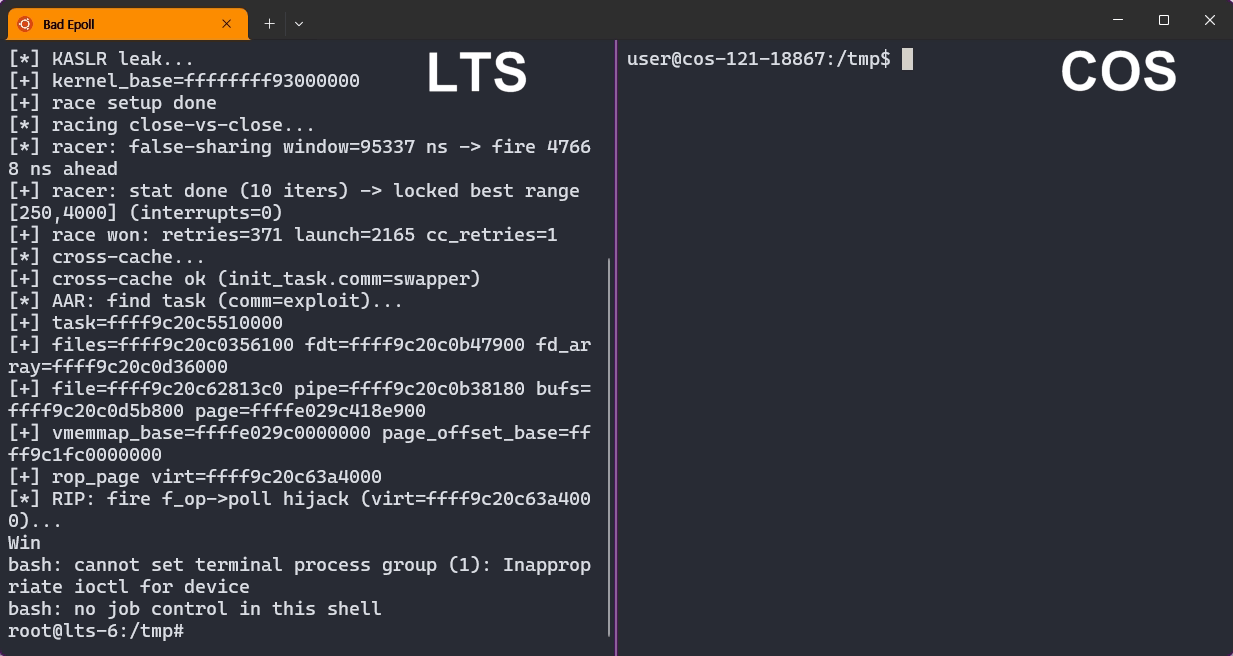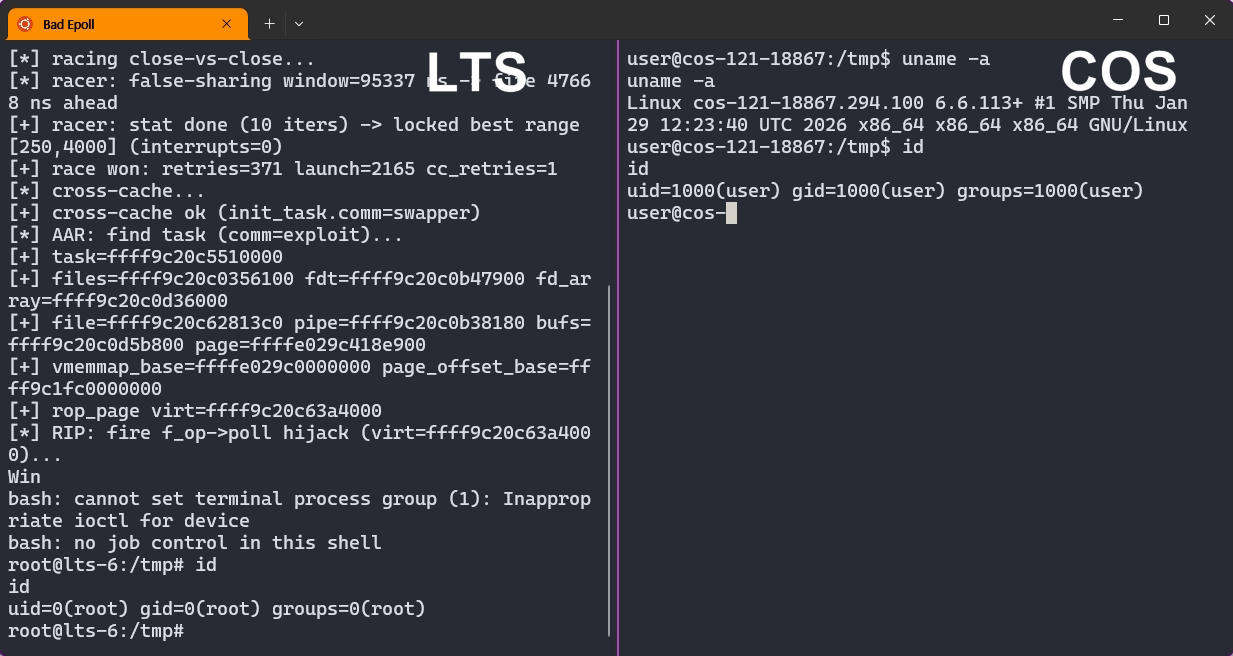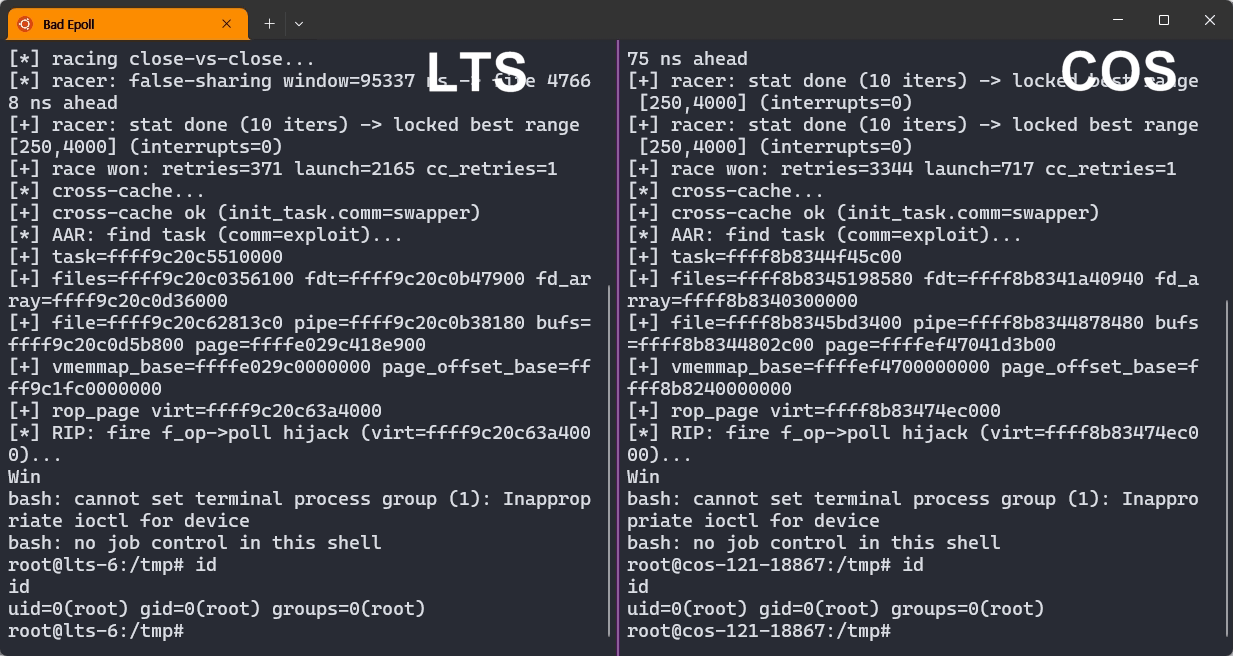
 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 sailay1996/awesome_windows_logical_bugs
collect for learning cases
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 bcoles/kernel-exploits
Various kernel exploits
 danigargu/cve-2020-0796
CVE-2020-0796 - Windows SMBv3 LPE exploit #SMBGhost

 safebreach-labs/pinjectra
Pinjectra is a C/C++ OOP-like library that implements Process Injection techniques (with focus on Windows 10 64-bit)
 worawit/cve-2021-3156
Sudo Baron Samedit Exploit
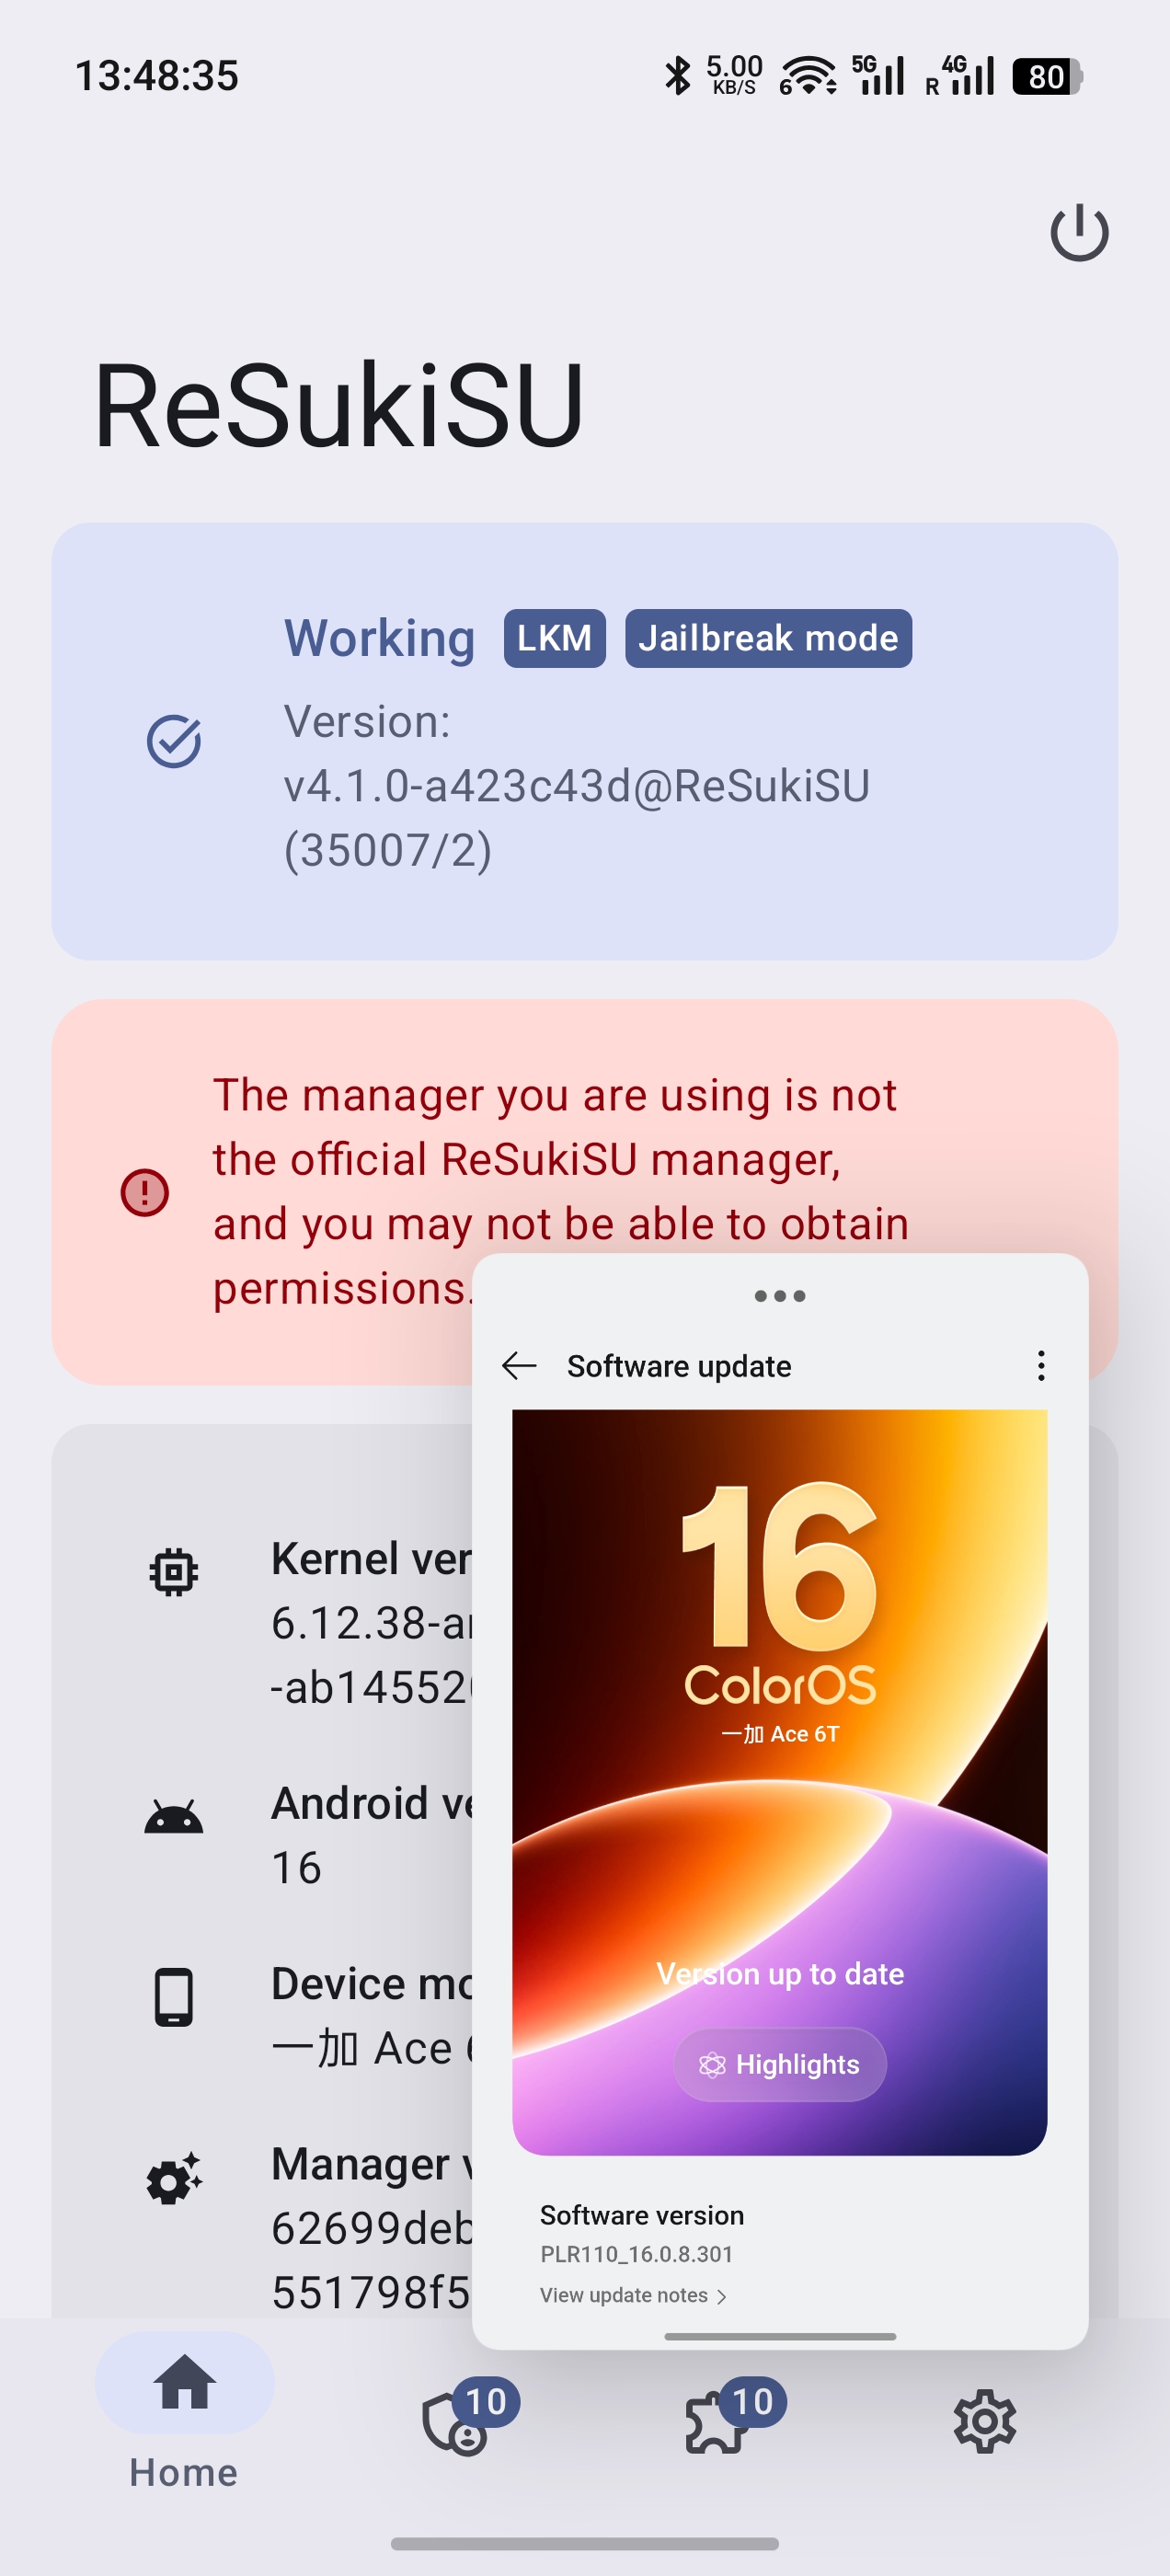 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
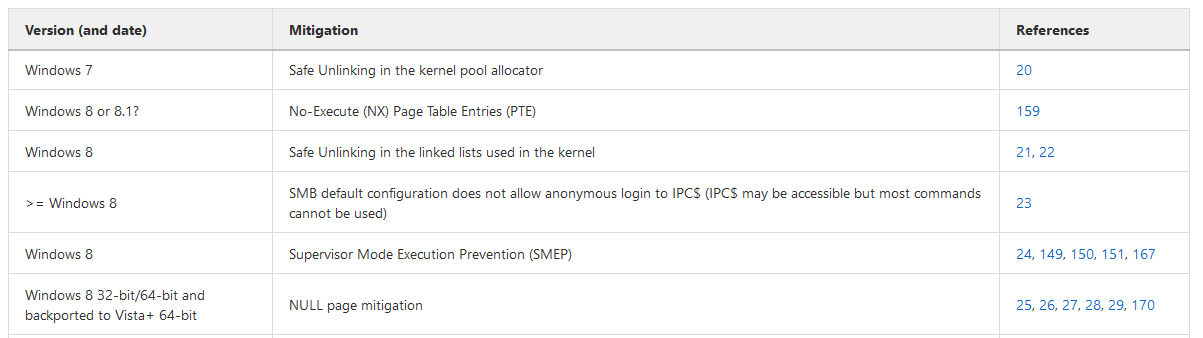 nccgroup/exploit_mitigations
Knowledge base of exploit mitigations available across numerous operating systems, architectures and applications and versions.
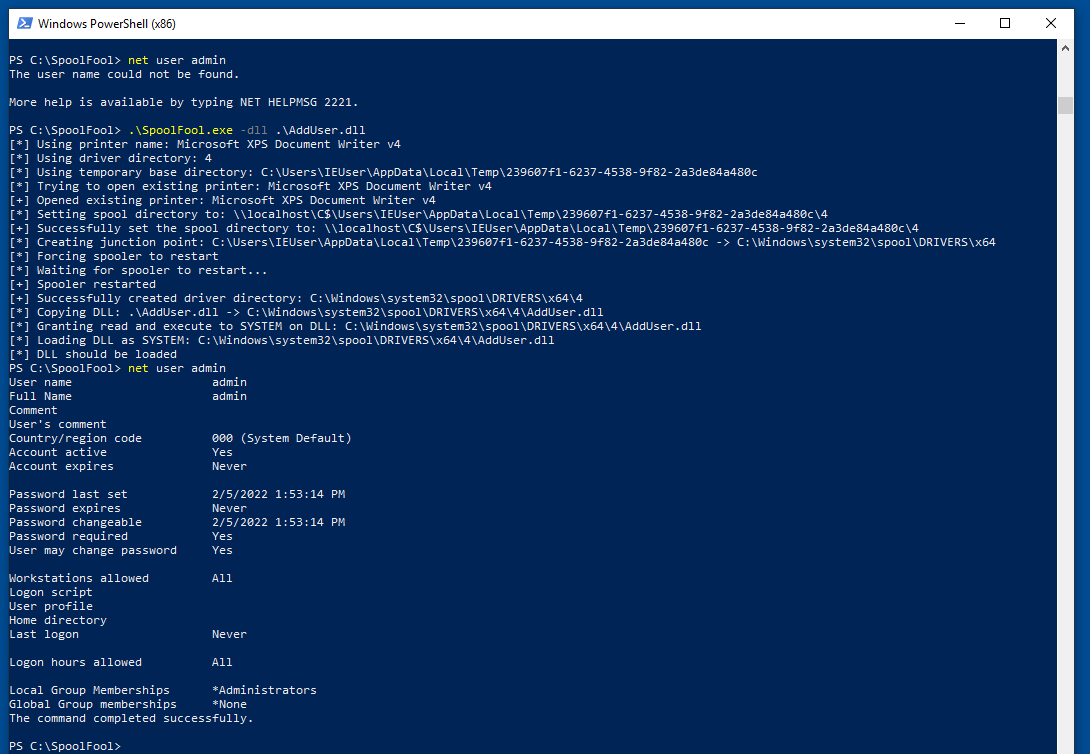 ly4k/spoolfool
Exploit for CVE-2022-21999 - Windows Print Spooler Elevation of Privilege Vulnerability (LPE)
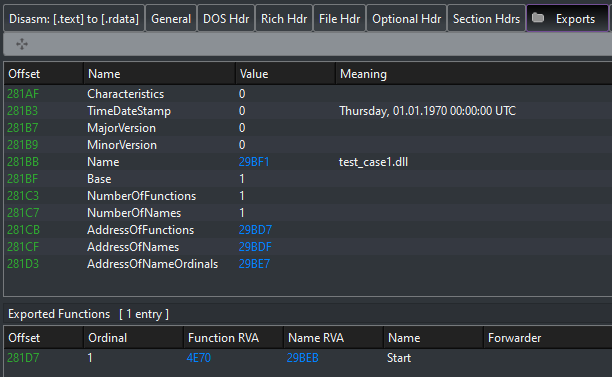 hasherezade/exe_to_dll
Converts a EXE into DLL
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 berabuddies/redis-poc
RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1








