
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended

 omgrant/ft9201-libfprint
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
 vid4l-07/klip
Minimal terminal-based password manager
 ggolawski/cve-2020-1958
Proof-of-concept exploit for CVE-2020-1958, an LDAP injection vulnerability in Apache Druid 0.17.0, enabling user enumeration and LDAP attribute…
 infrastructureservices/vsftpd
Security-focused FTP server daemon designed for resilience against attack, offering high performance and scalability with extensive configuration…
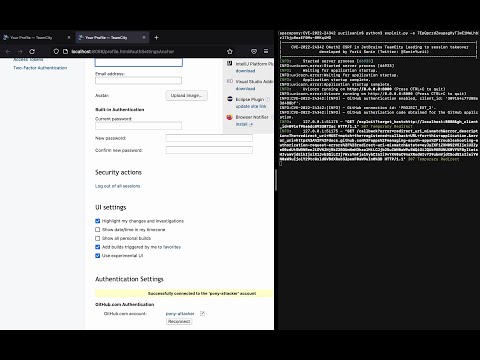 yuriisanin/cve-2022-24342
PoC for CVE-2022-24342: account takeover via CSRF in GitHub authentication
 logisek/huntcyberark
CyberArk Security Audit
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 sensepost/cve-2025-64446
A scanner for the FortiNet vulnerability CVE-2025-64446
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…
 zb3/tiandy-research
This repository contains the results of my August 2020 research of Tiandy's IPC/NVR firmware. I found two vulnerabilities that could be used to…
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 abraxas/pma-5.2.3-webauthn-2fa
phpMyAdmin - High 8.1 - Authenticated POST /index.php - 2FA Bypass
 ricardojoserf/axis-rce
Unauthenticated RCE on Axis Camera Station (chaining CVE‑2025‑30026 and CVE‑2025‑30023)
 sinsinology/cve-2024-29855
PoC for the Veeam Recovery Orchestrator Authentication CVE-2024-29855
 michal-pielka/punchline
Peer-to-peer encrypted messenger in Rust with Noise IK and UDP NAT hole punching
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions








