
 #1
API testing, fuzzing, schema validation, authentication testing, and gateway security tools.
Kitploit recommended
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 tadhglewis/apollo-koa-minimal
GraphQL vulnerability disclosure: CVE-2023-26144
 oh-az/noargs
Windows API hooking tool that dynamically spoofs and conceals process arguments via Detours library and PEB manipulation, enabling stealthy process…
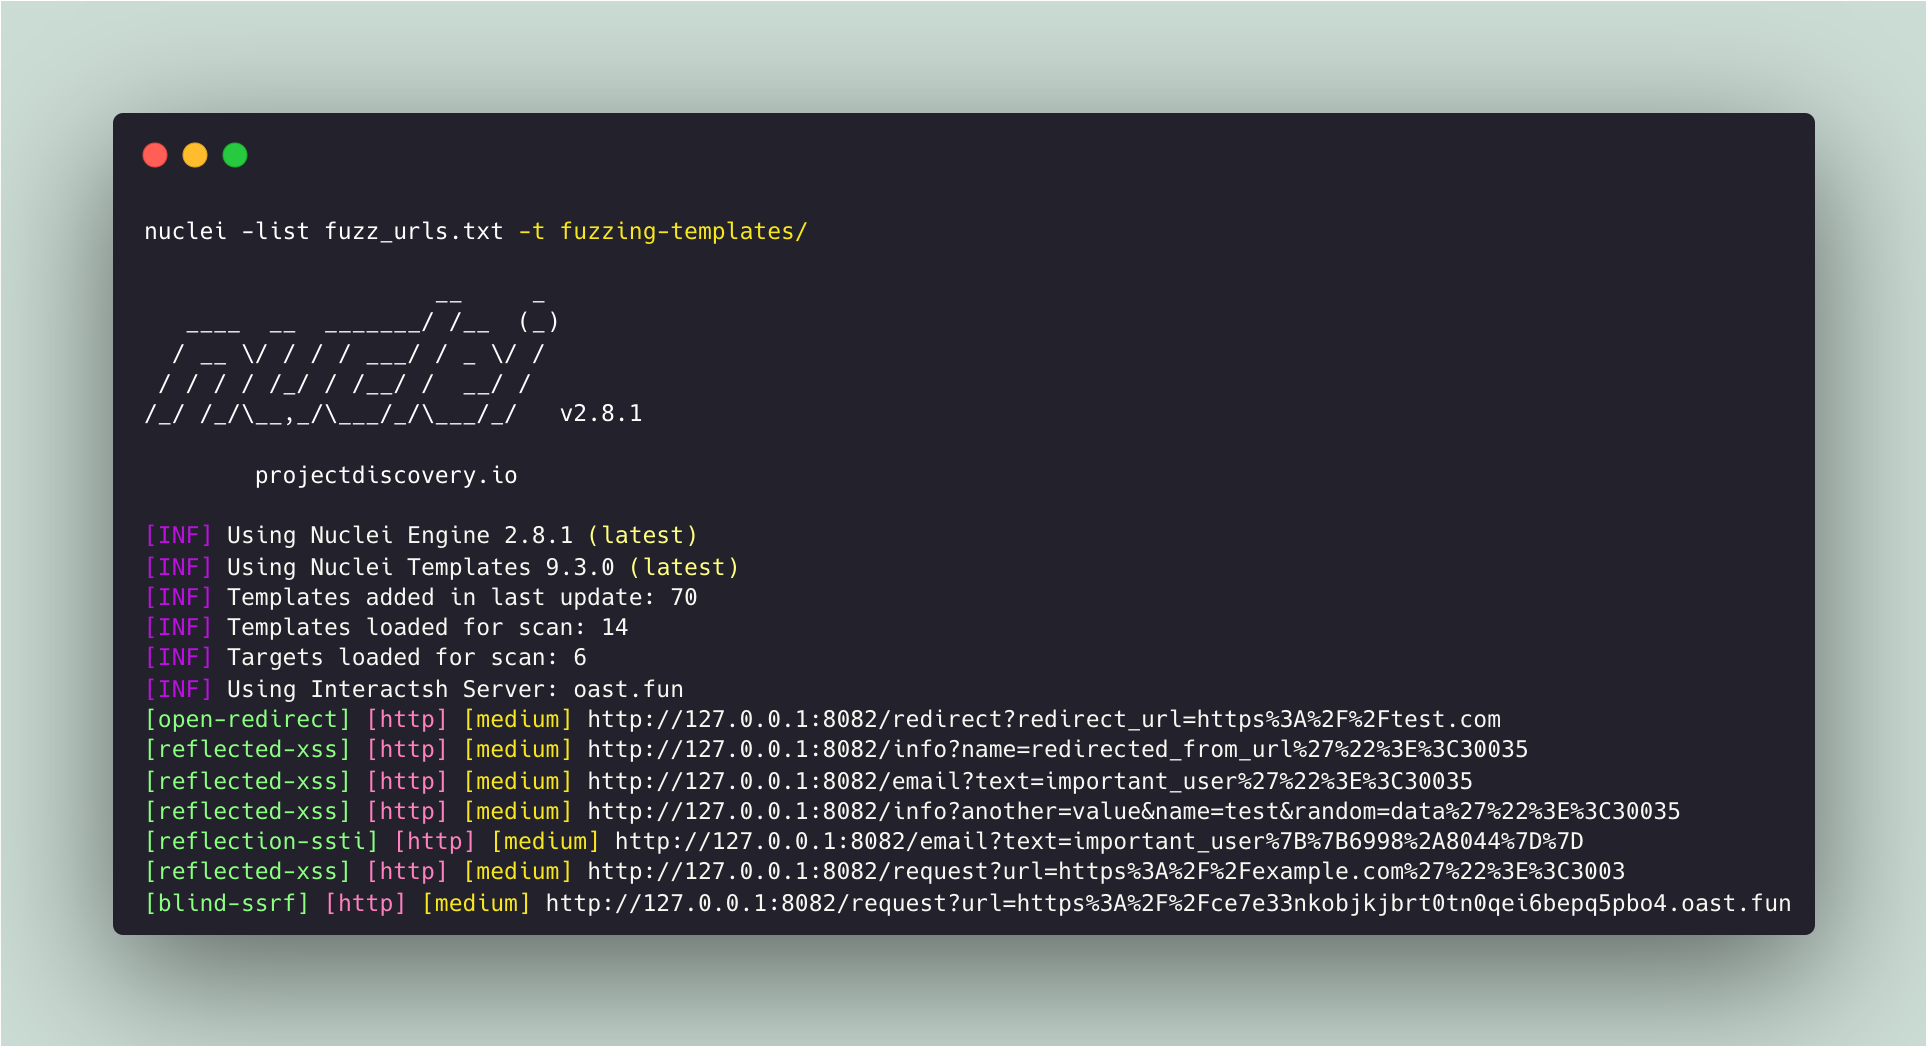 projectdiscovery/fuzzing-templates
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 password123456/about-hmac
HMAC Implementation Example and Explanation
 password123456/some-tweak-to-hide-jwt-payload-values
Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 karlemilnikka/cve-2024-1208-and-cve-2024-1210
Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…
 karlemilnikka/cve-2024-1209
Sensitive Information Exposure via assignments in LearnDash.
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.








