
 #1
Tools for assessing the security of REST, SOAP, and GraphQL APIs.
Kitploit recommended

 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
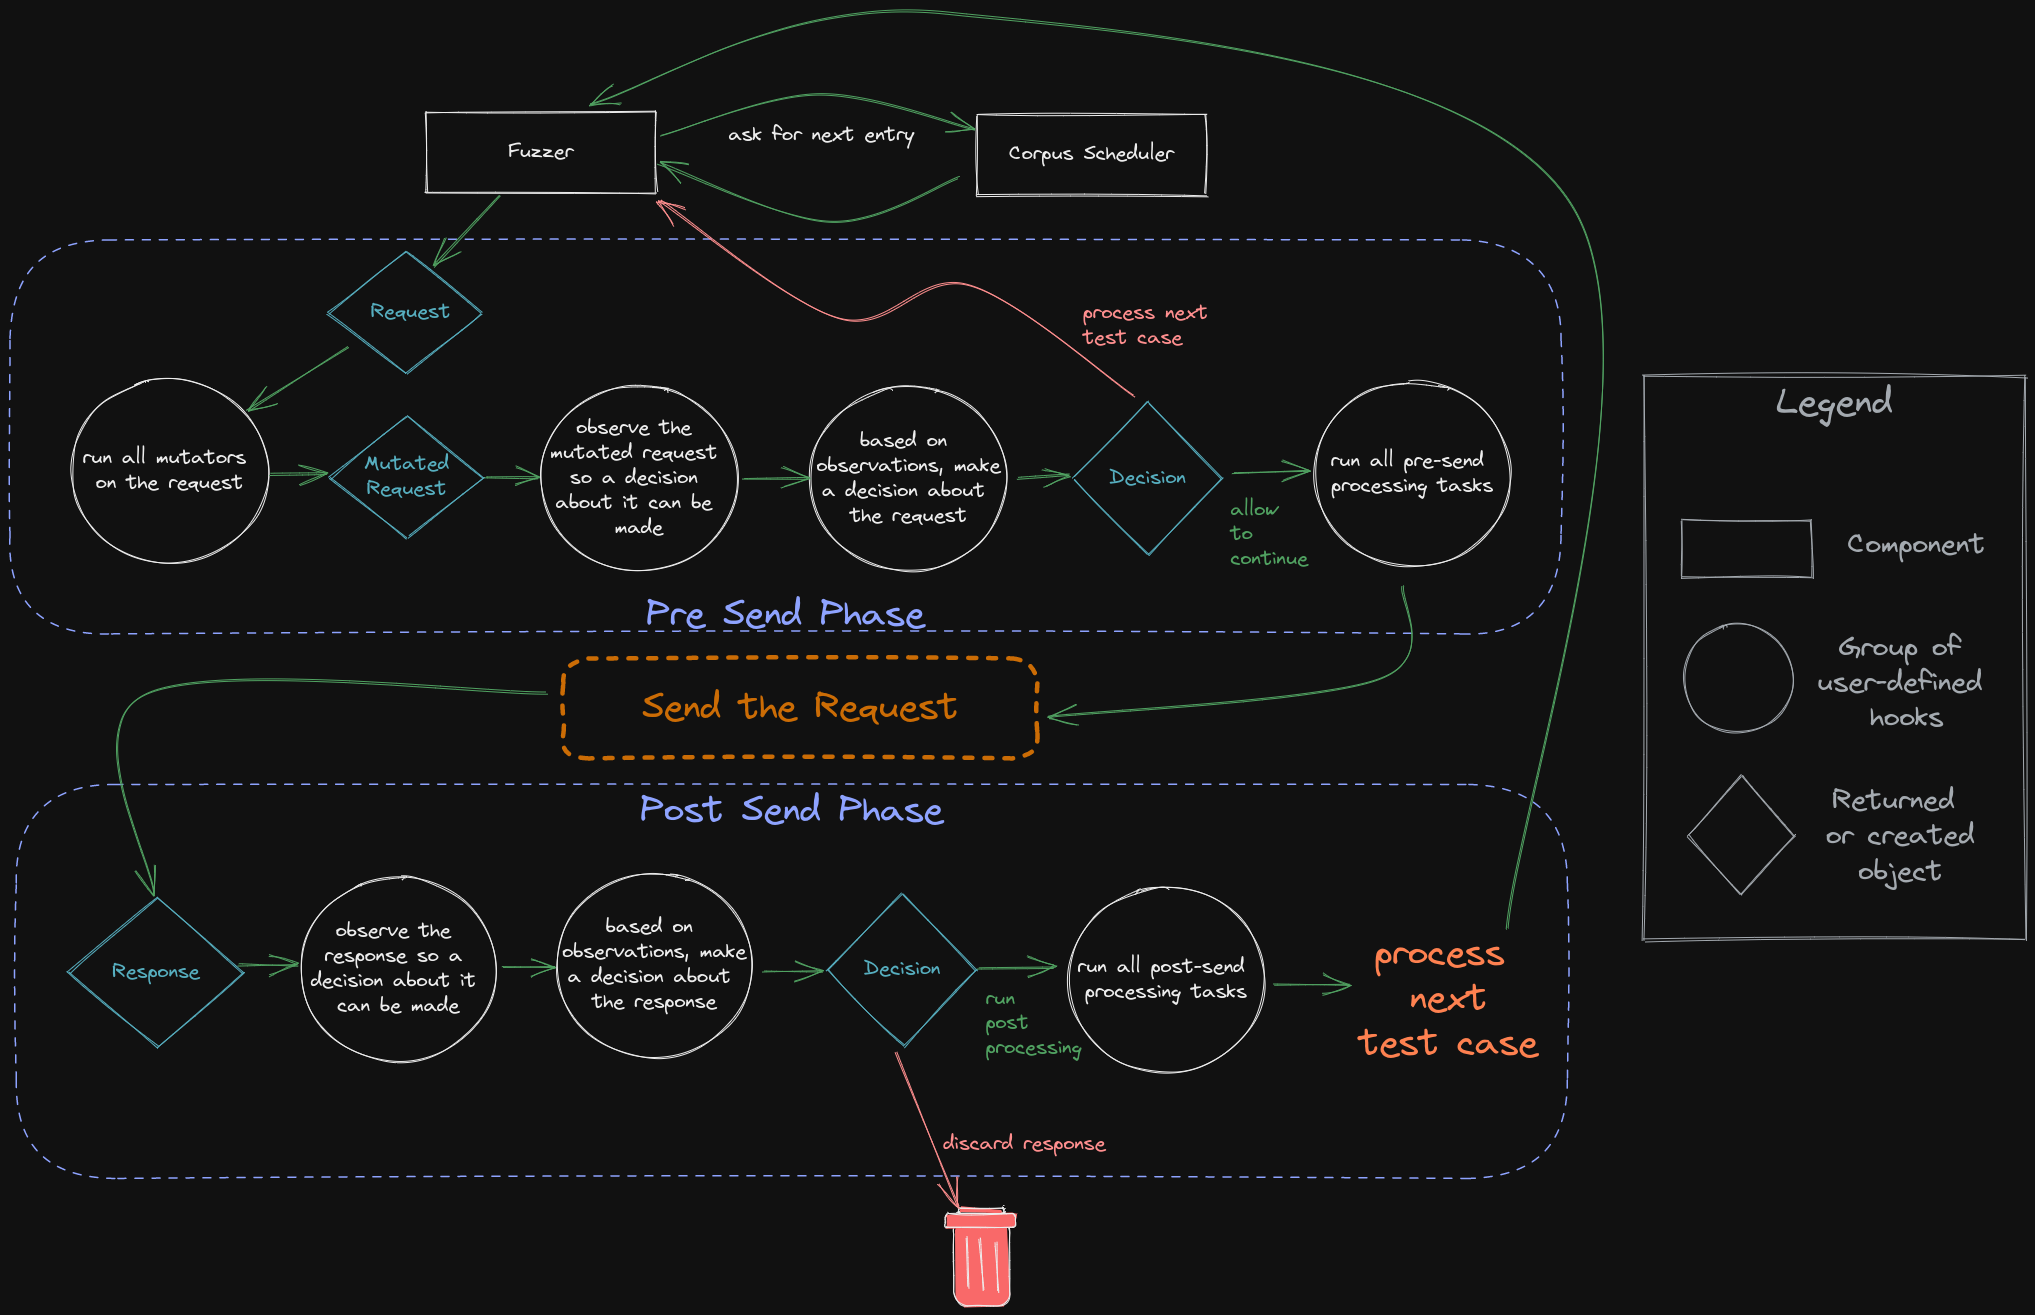 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
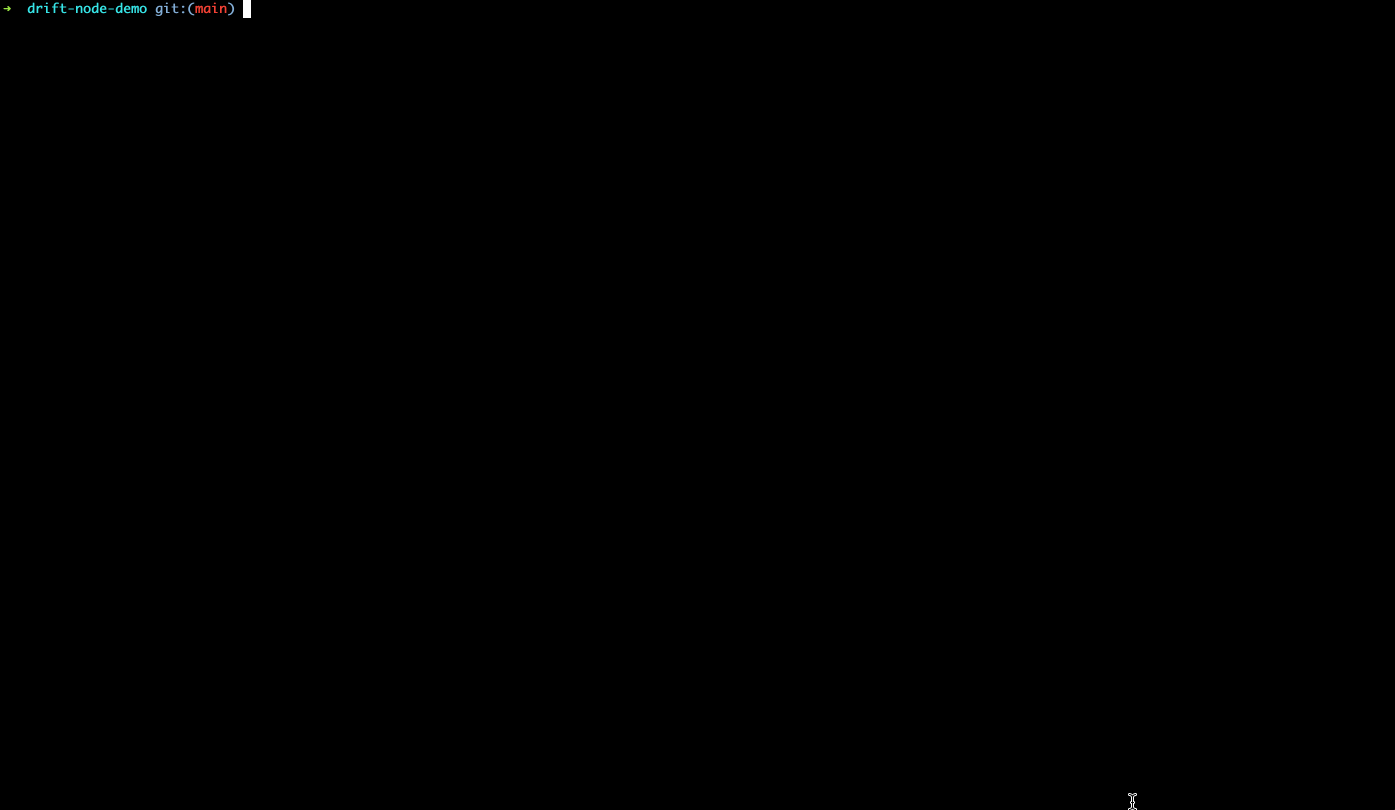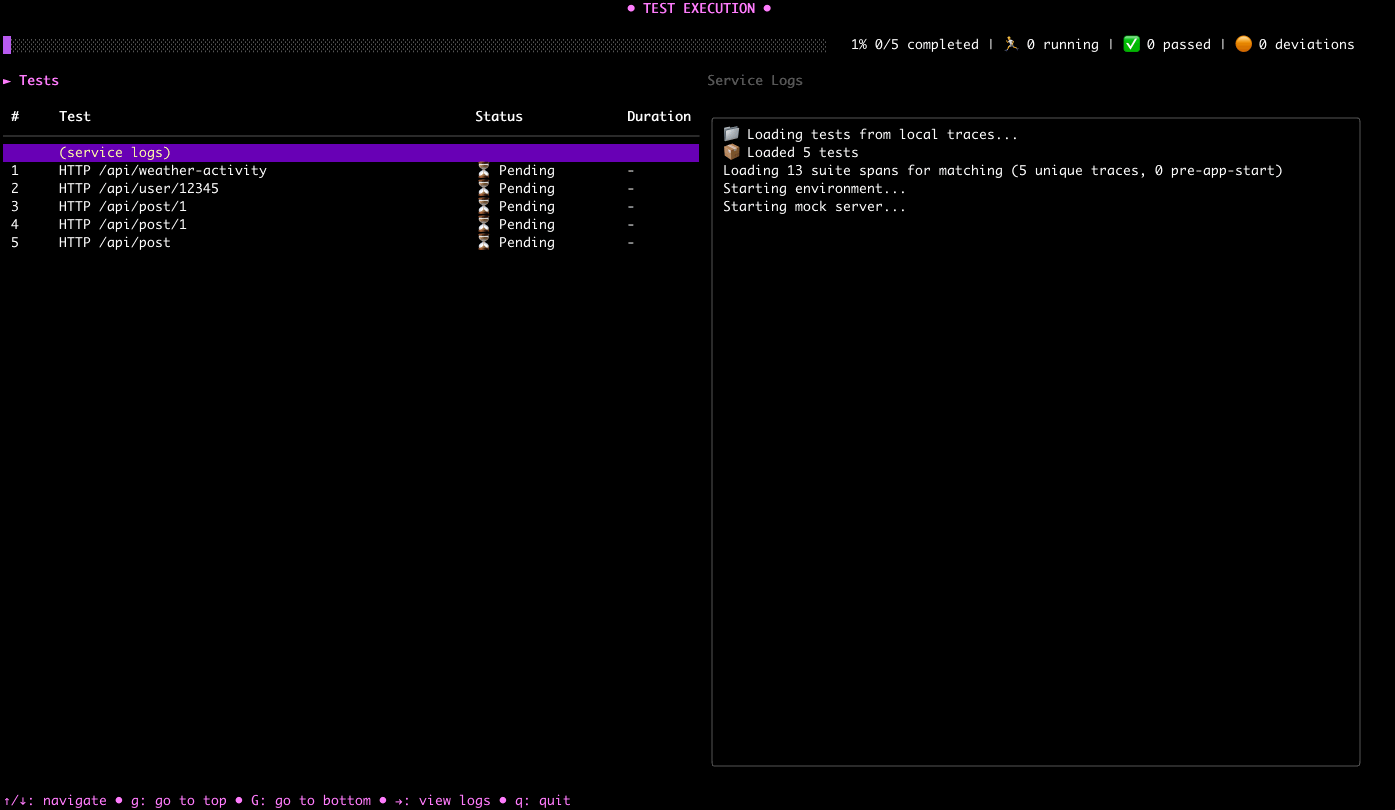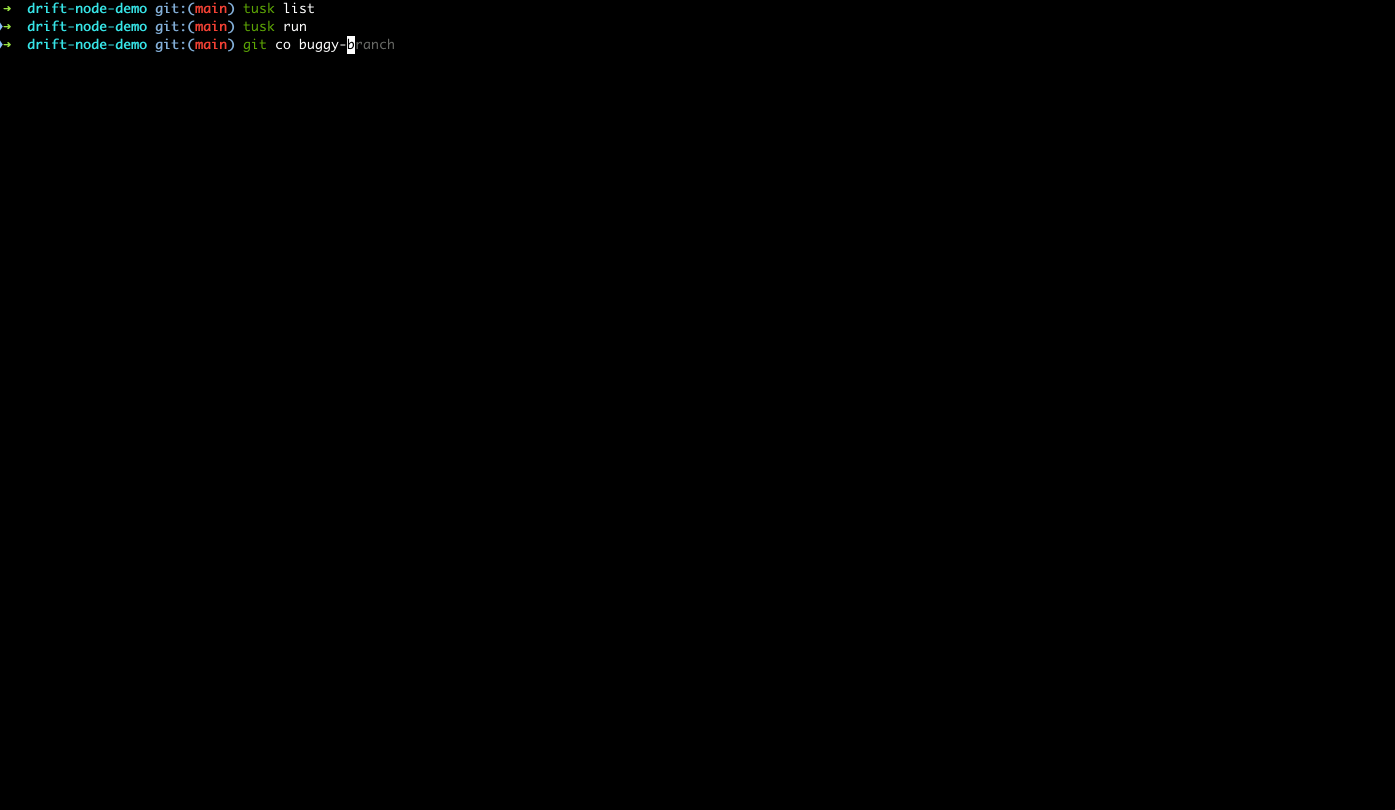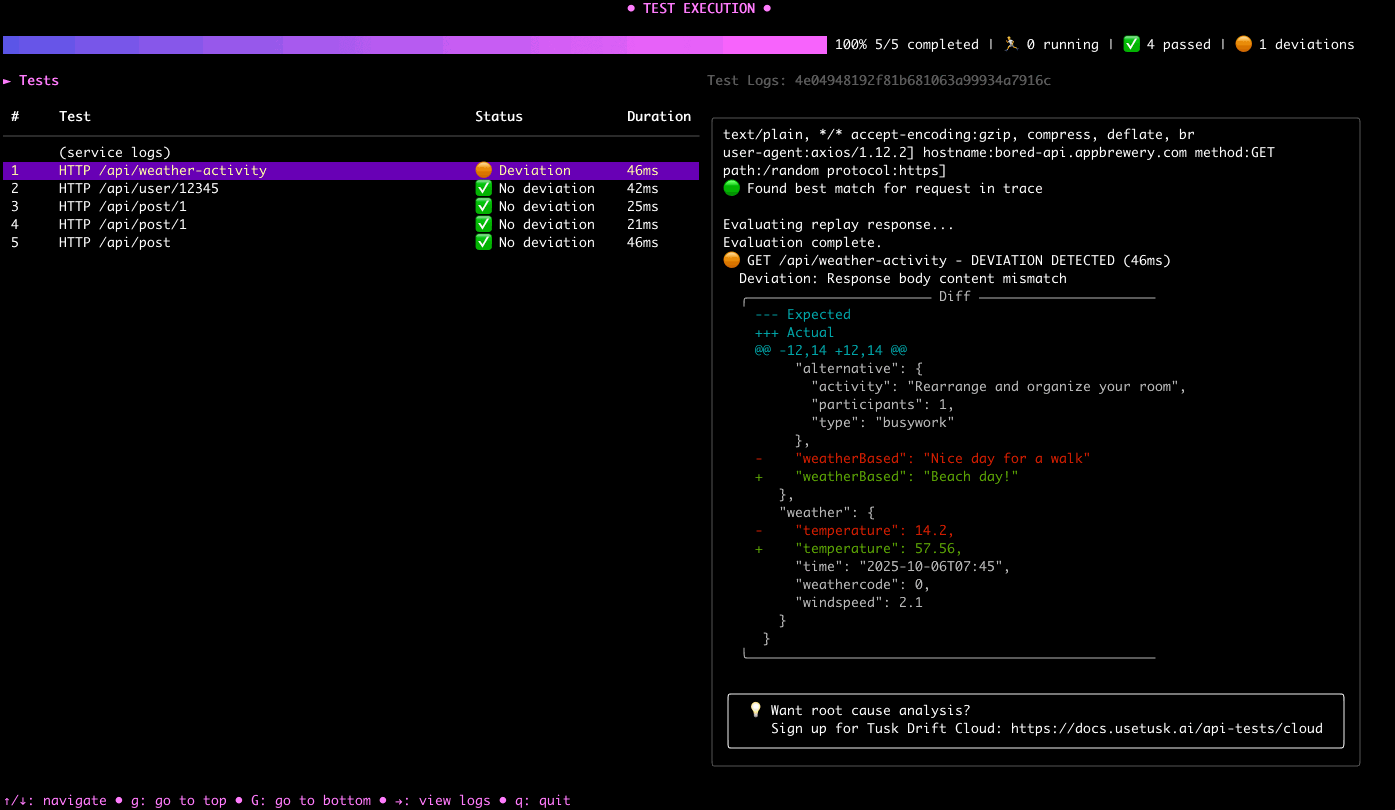 use-tusk/drift-node-sdk
Node.js SDK for capturing and replaying API calls made to/from your service
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
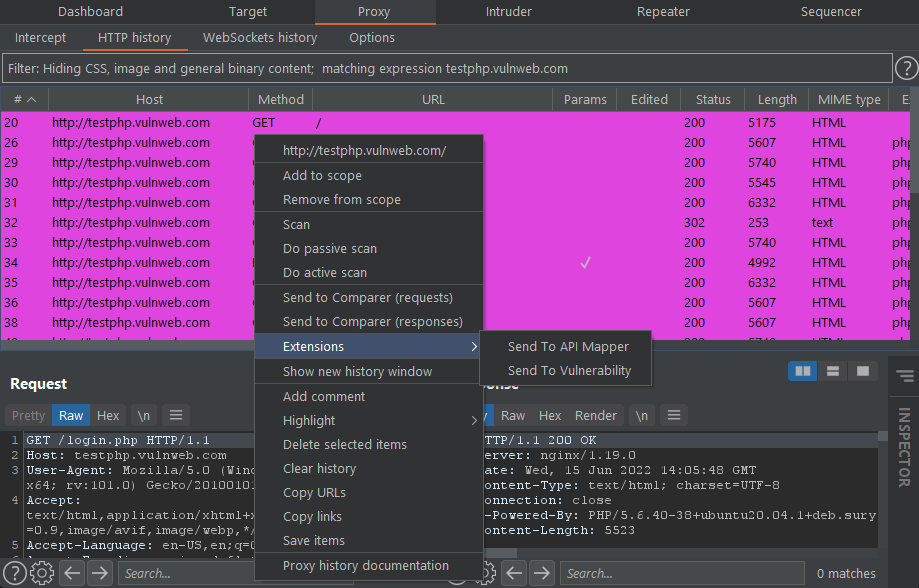 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…








