
 #1
Tools focused on penetration testing, reversing, and securing Android apps and the Android OS.
Kitploit recommended

 hui191/cve-2026-43499-aak-an00
Honor WIN RT (AAK-AN00) CVE-2026-43499 temporary root - research notes
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 janewas/cve-2026-98260-vivo-gki-research
Research notes: porting CVE-2026-98260 to vivo/iQOO GKI 6.6.127 (no exploit code; coordinated disclosure planned)
 tea9/cve-2020-0096-strandhogg2
CVE-2020-0096-StrandHogg2 复现
 datfooldive/ghostlock-emerald
GhostLock (CVE-2026-43499) kernel exploit for Poco M6 Pro (emerald) with locked bootloader
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 nanoturtle1145/cve-2026-98260-uaf
CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…
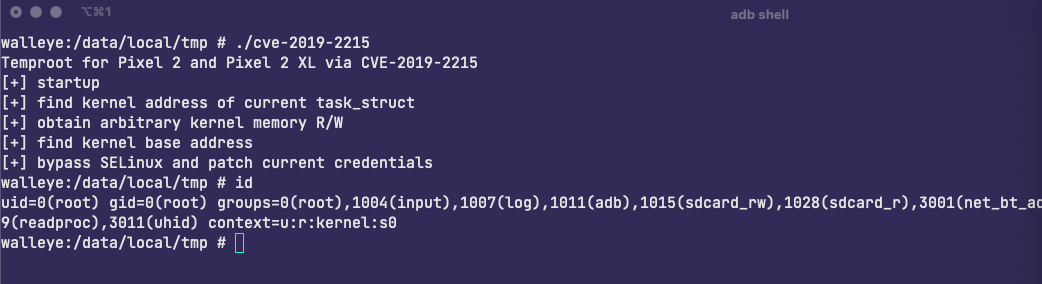 stevejubx/cve-2019-2215
Android Kernel Vulnerability (CVE-2019-2215) temporary root PoC
 no-22-github/unplus
CVE-2026-43499 per-boot root exploit — core logic (arm64 Android GKI 6.6)
 sorrow404null/cve-2026-43499-rmx5200
Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 demining/pixnapping-attack-on-android
Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 wrlu/cve-2023-40130
PoC of CVE-2023-40130
 bartixxx32/cve-2026-43499-oneplus15
Educational proof-of-concept for Android 16 local privilege escalation on OnePlus 15, featuring kernel offset detection, target generation, and…
 qm4rs/cve-2026-0023-update-ownership-poc
Proof-of-concept demonstrating CVE-2026-0023, an Android Update Ownership trust bypass that suppresses the ownership warning during app updates.…
 re13orn/cve-2024-0044-exp
利用 CVE-2024-0044 Android 权限提升下载任意目标App沙箱文件。

 ykupriyanov/bakablocker
Stop Secret Phone Slowdowns & 24/7 Spyware in One Tap — Autonomous Local ADB Debloater & Background Jail (No PC, No Root, 100% Safe)








