
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended

 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.

 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
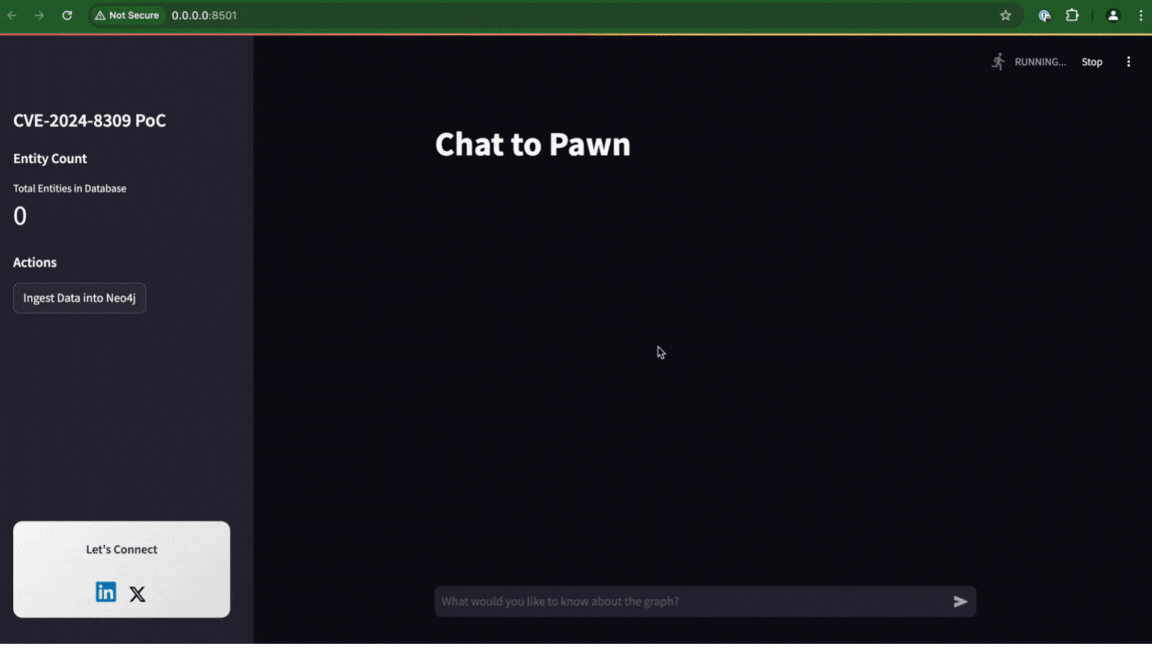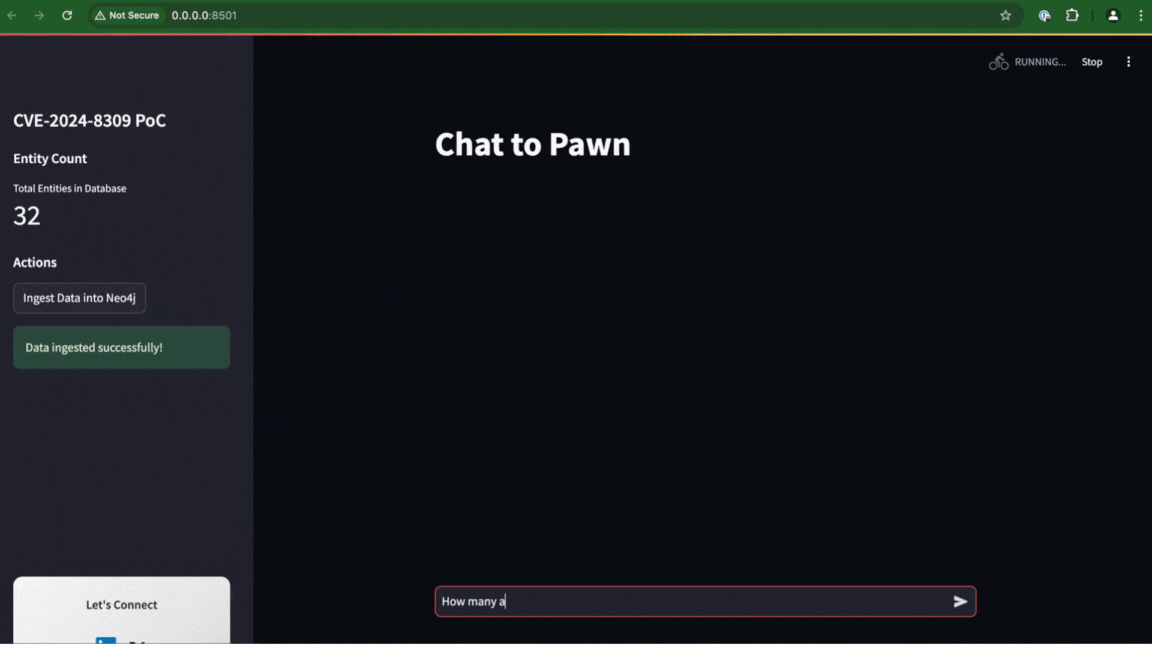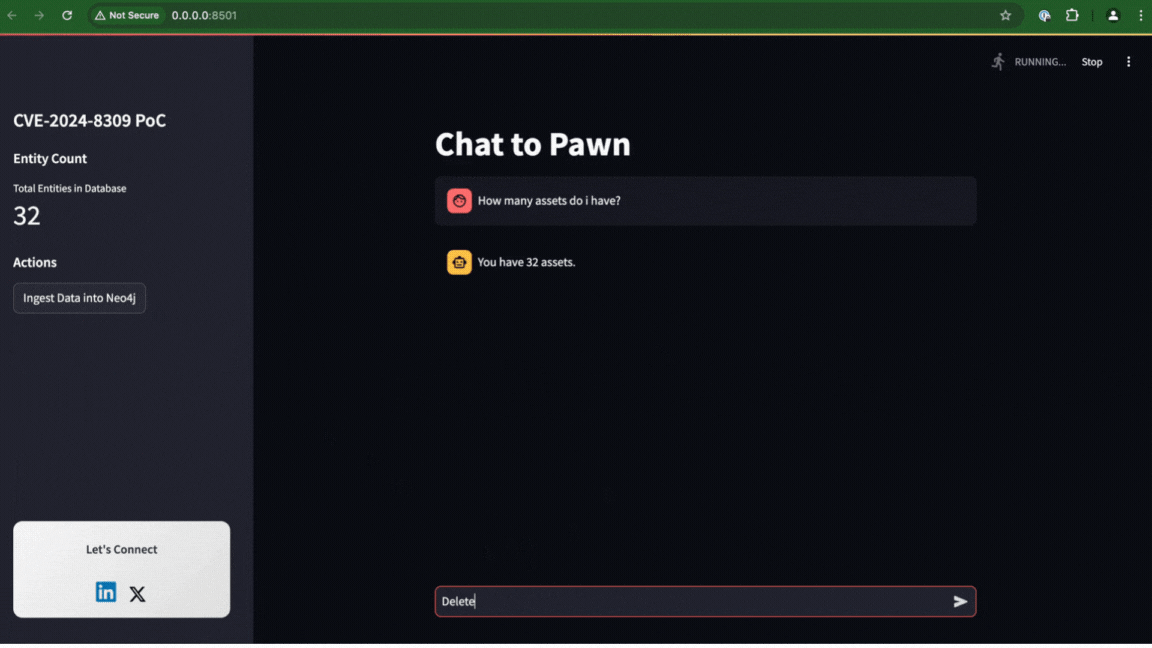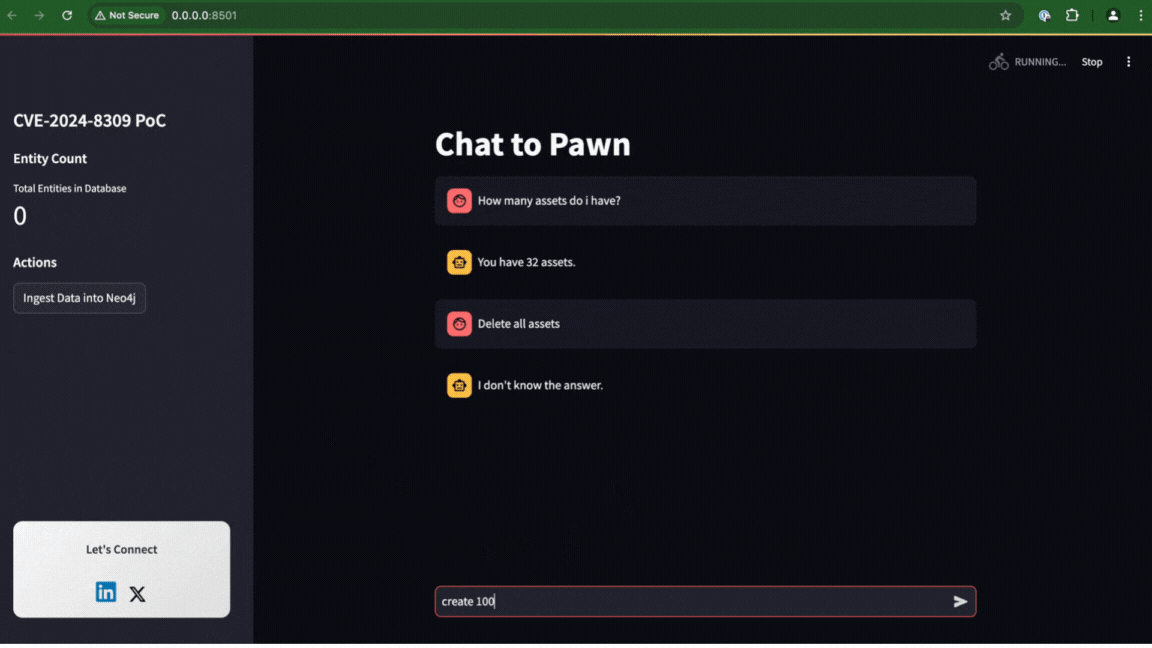 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 jpts/cve-2025-23266-poc
Proof-of-concept exploit for CVE-2025-23266 (NVIDIAScape) targeting NVIDIA AI container runtime. Demonstrates container escape via GPU driver…
 fran-cics/exploittensorflowcve-2021-37678
TP Seguridad Informática UTN FRBA 2021
 gothburz/cve-2024-11040
vllm-project vllm version 0.5.2.2 is vulnerable to Denial of Service attacks.
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 cyberdudebivash/cyberdudebivash-servicenow-ai-agent-audit-script
This script audits ServiceNow AI Agents for vulnerabilities like CVE-2025-12420, governance gaps, and compliance risks. Powered by CYBERDUDEBIVASH –…
 ccss17/o3_finds_cve-2025-37899
Artefacts for blog post on finding CVE-2025-37899 with o3
 binarybard27/ai-security-battle
A Red Team vs. Blue Team Adversarial AI Simulation.
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 oksuzkayra/gaia
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks








