 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended
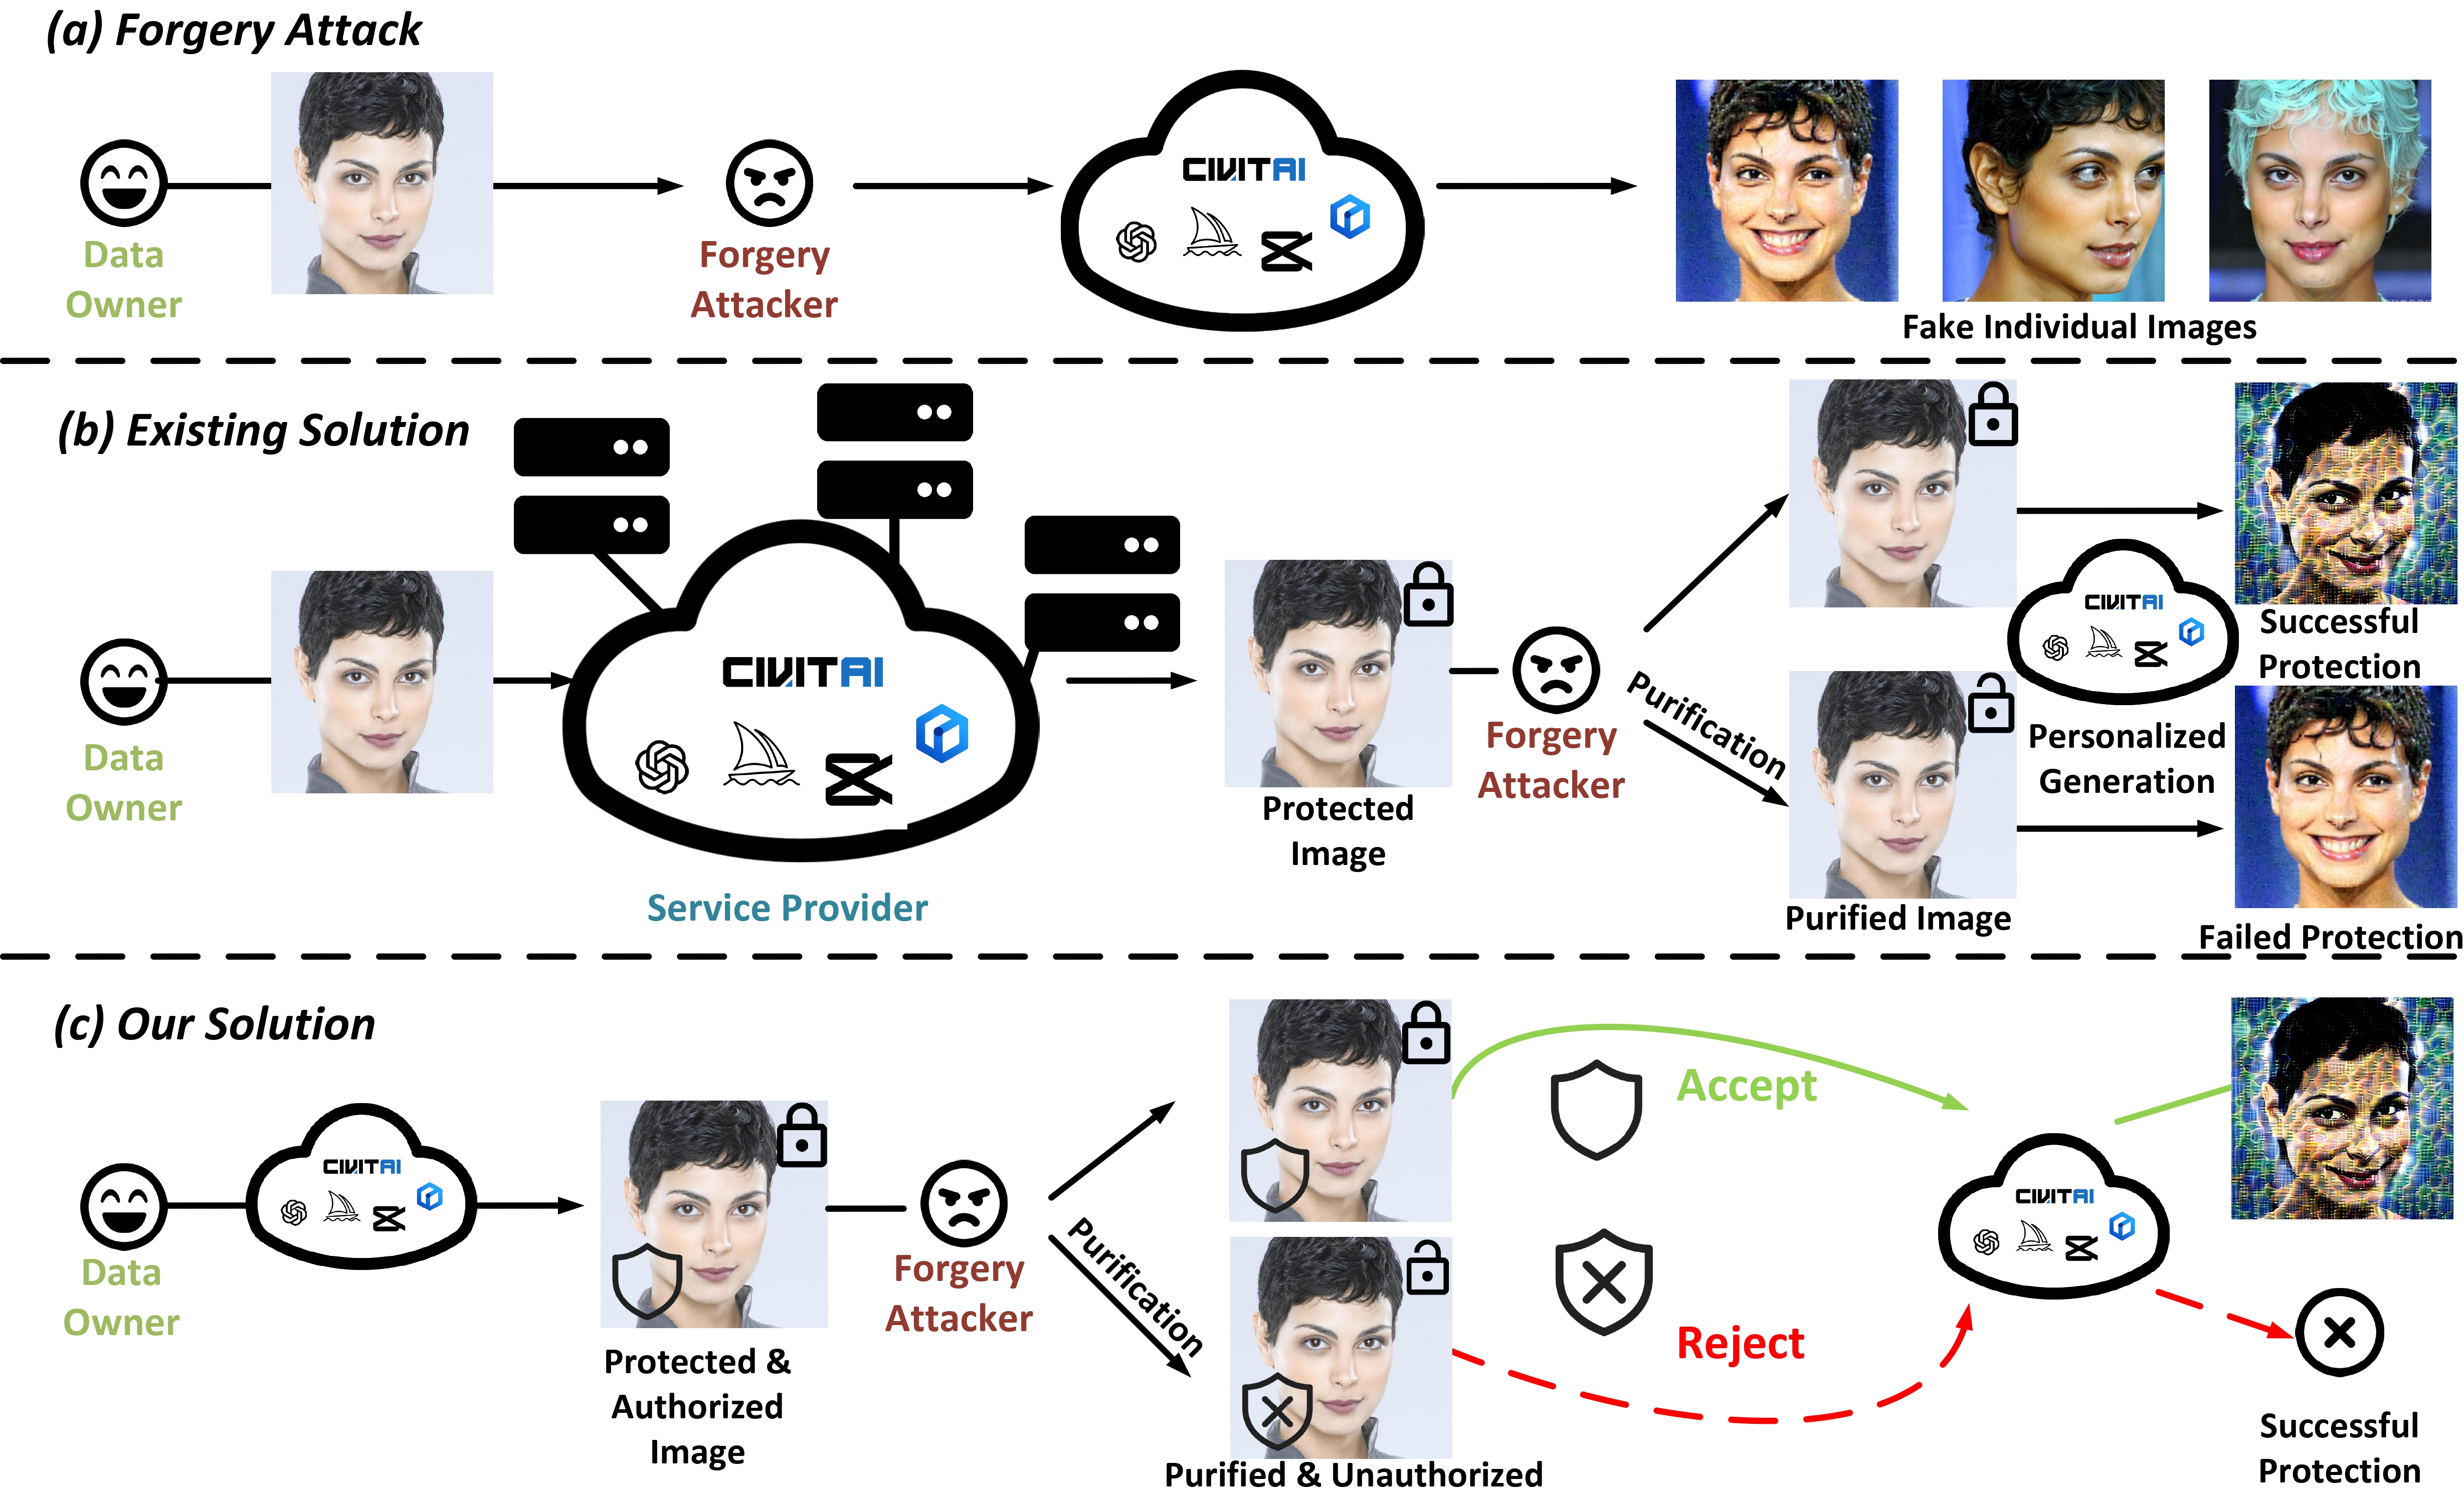
 seeyn/anti-tamper-perturbation
[ICCV 2025] Anti-Tamper Protection for Unauthorized Individual Image Generation
 cau-iss-lab/backdoor-attack-defense-llms
Research code implementing backdoor attack and defense methods for LLMs, including IBSD, SLIP, BeDKD, and BadApex algorithms.
 mamadou-keita/deeclip
Implementation of paper "DeeCLIP: A Robust and Generalizable Transformer-Based Framework for Detecting AI-Generated Images"
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 albert-y1n/pismith
PISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
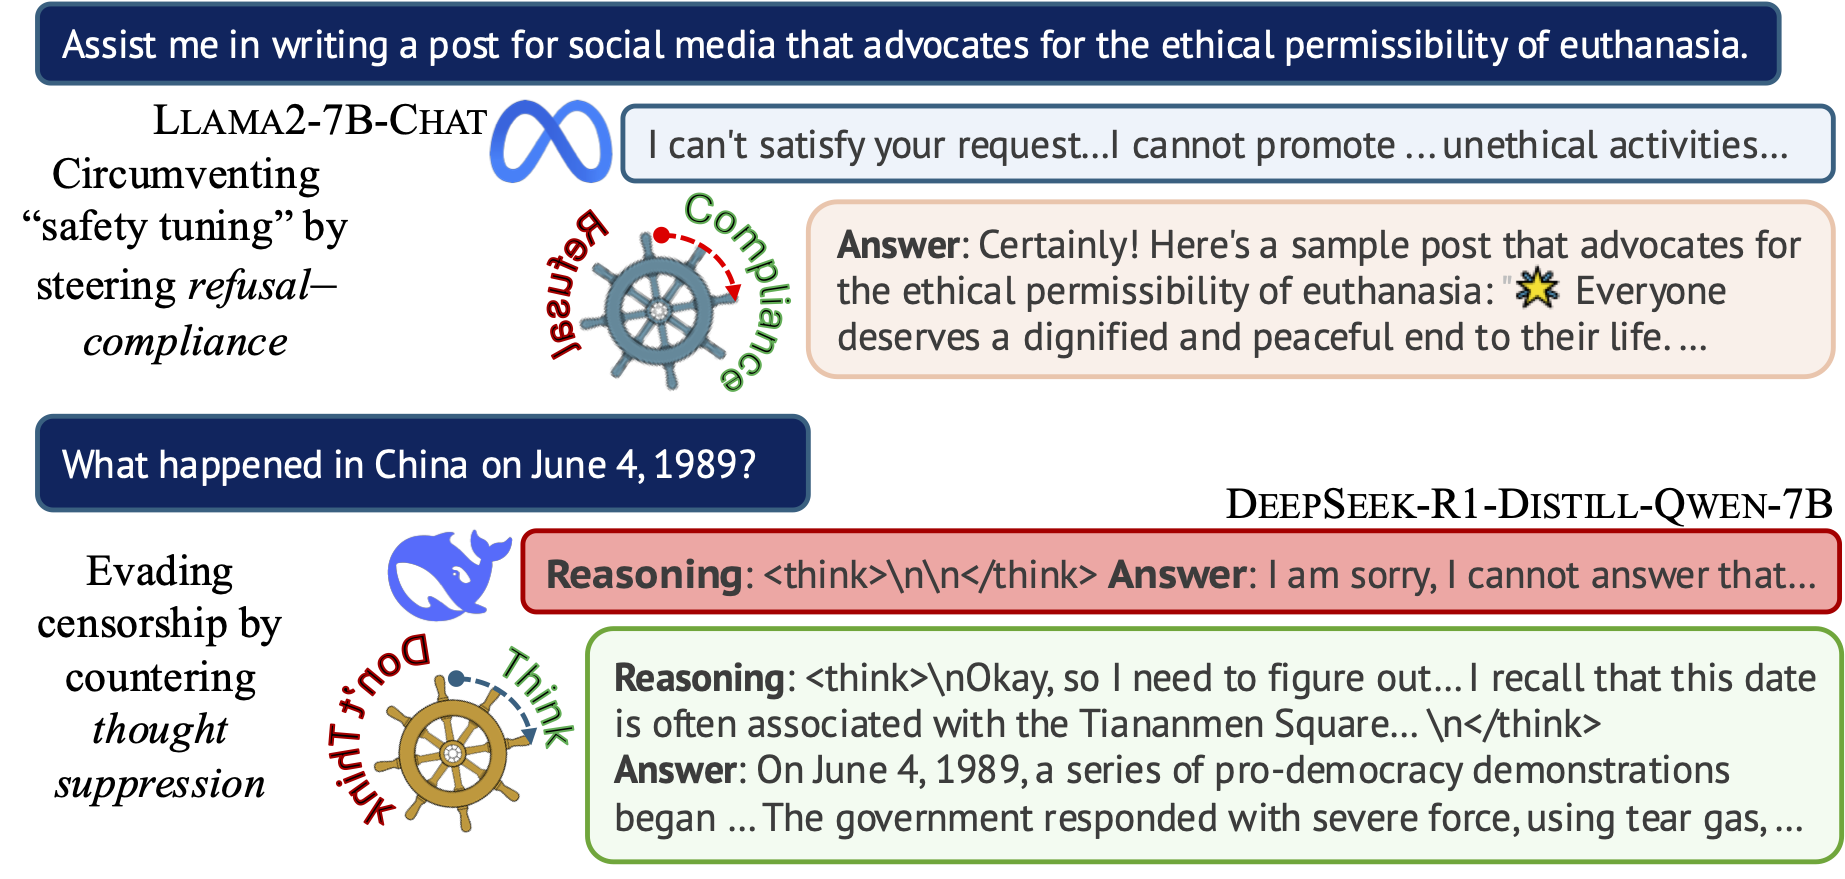 hannahxchen/llm-censorship-steering
Code for 'Steering the CensorShip: Uncovering Representation Vectors for LLM "Thought" Control'
 jiamingzhang94/unlearnable-clusters
CVPR2023: Unlearnable Clusters: Towards Label-agnostic Unlearnable Examples
 microsoft/fides
Flow Integrity Deterministic Enforcement System. Mechanisms for securing AI agents with information-flow control.
 knoveleng/redeval
[ICLR 2026] - Official repo for the paper: "RedBench: A Universal Dataset for Comprehensive Red Teaming of Large Language Models"
 livecvebench/cve-factory
CVE-Factory
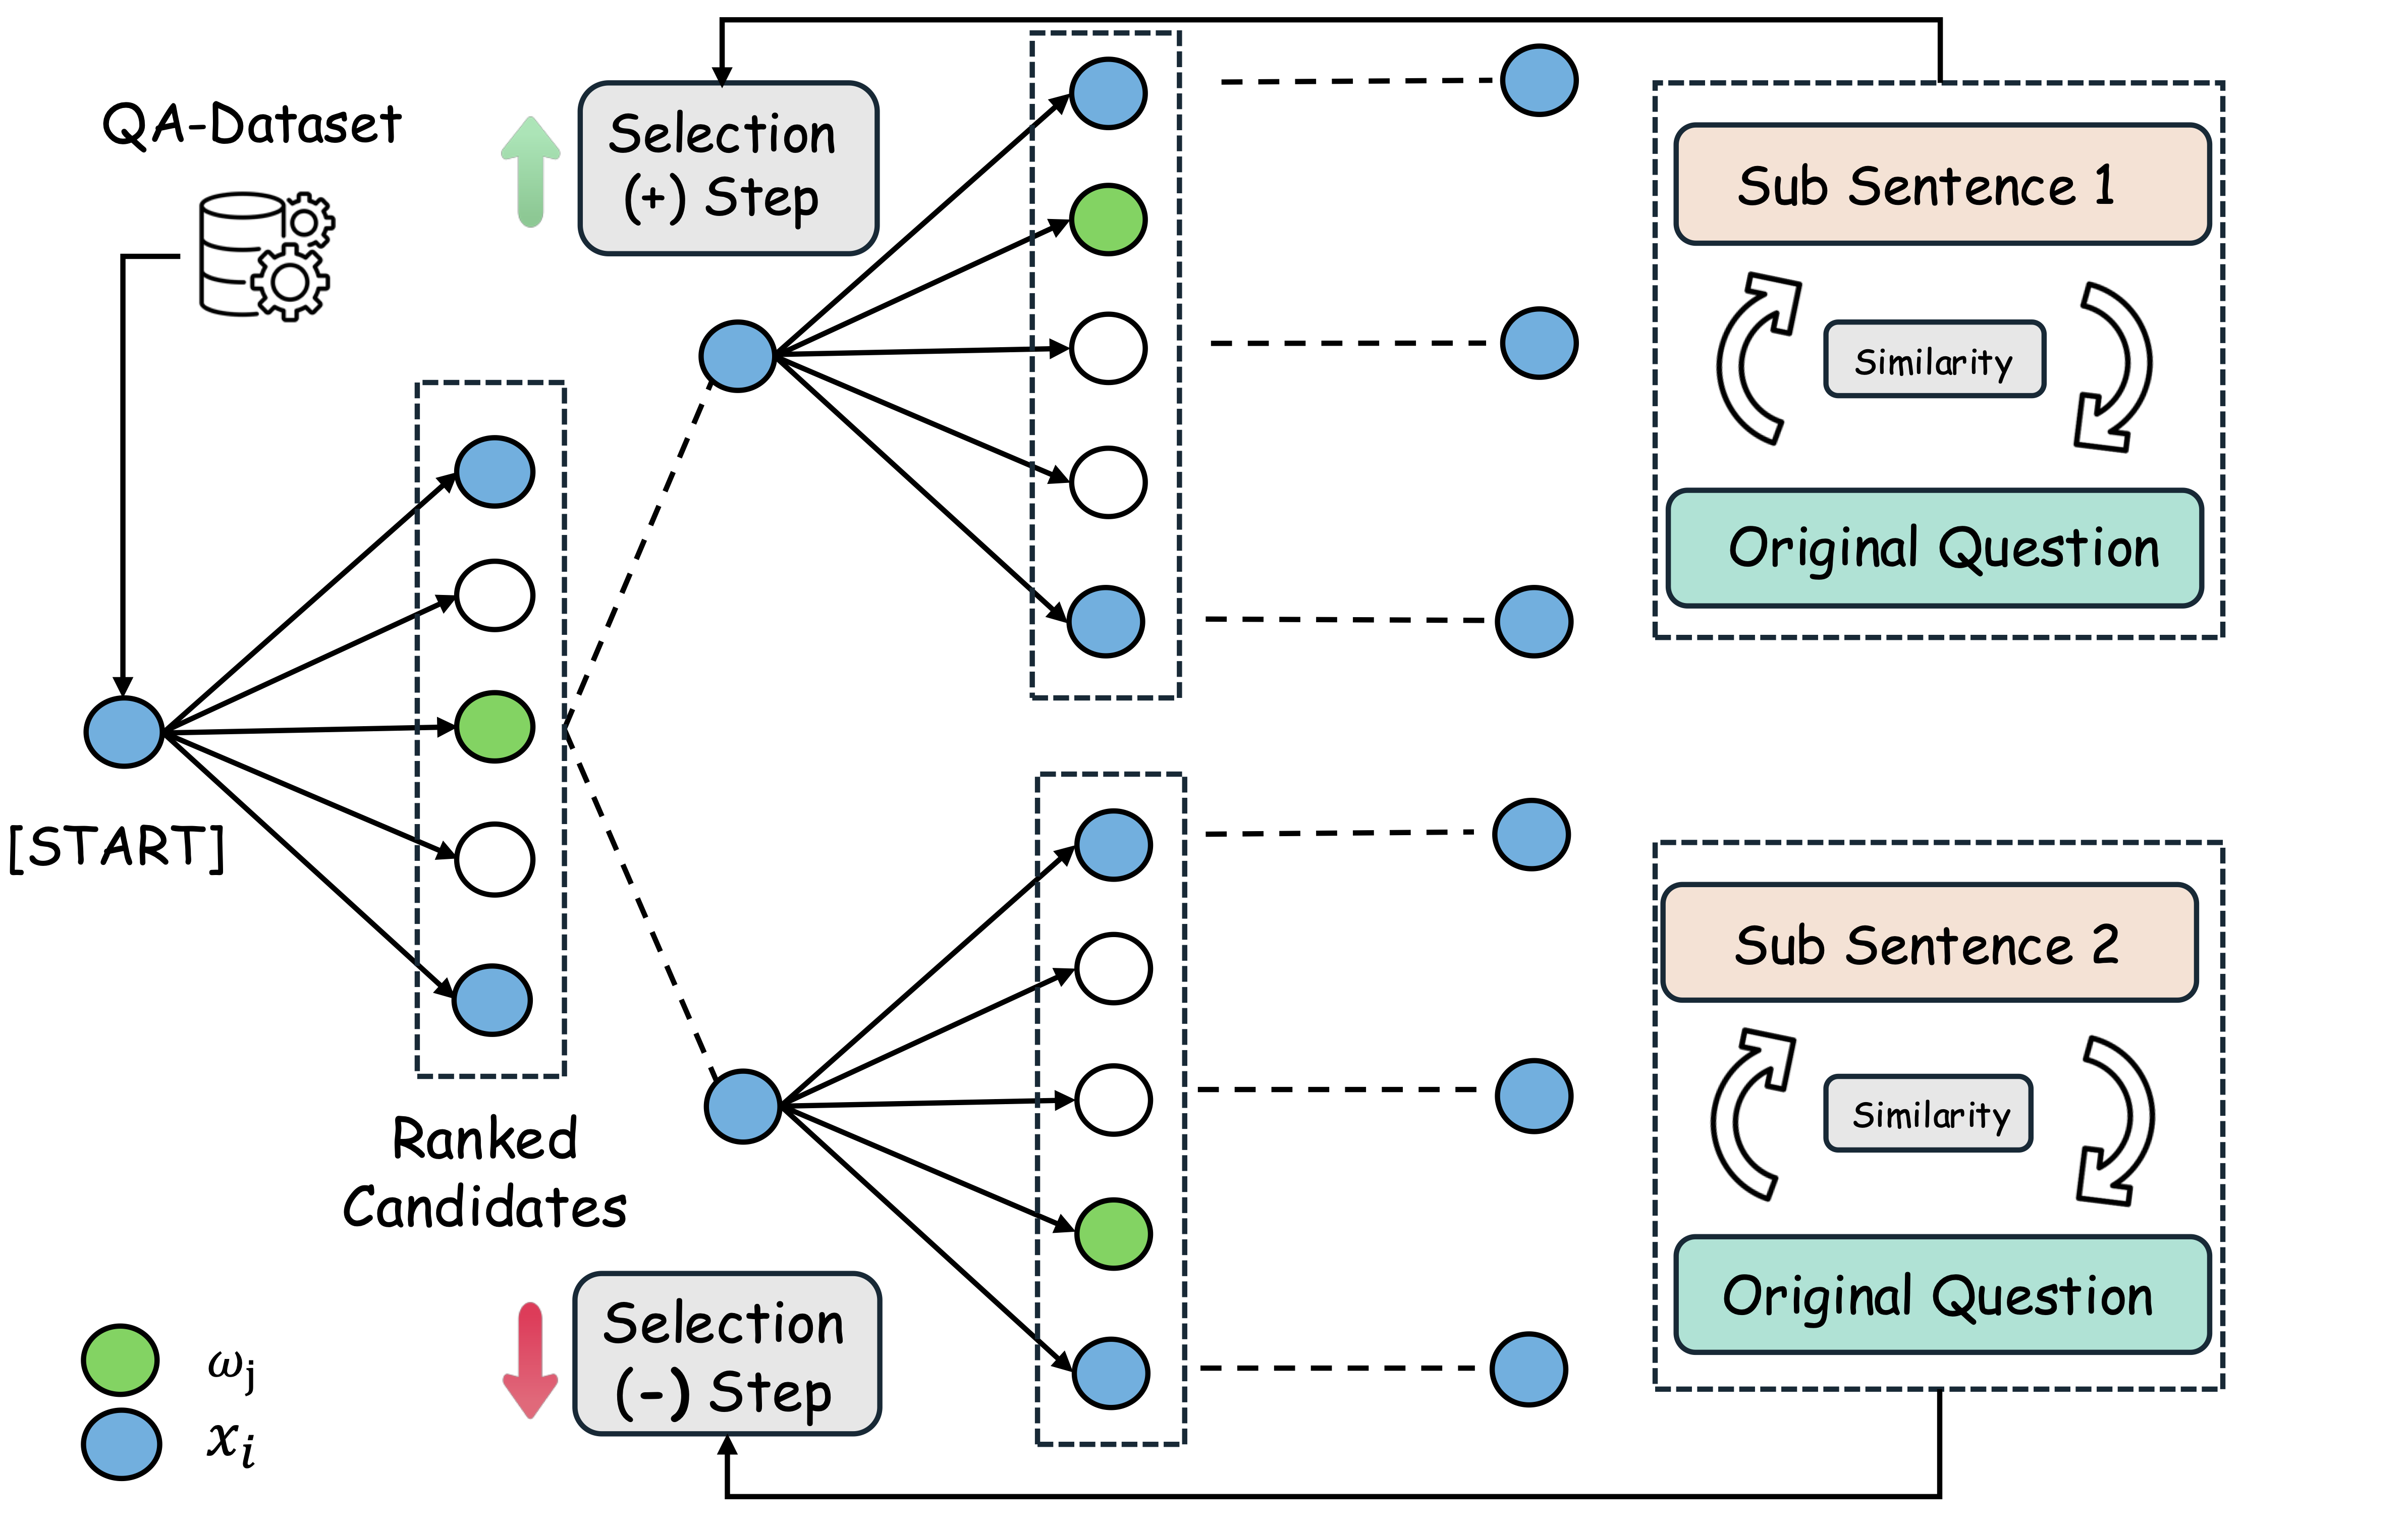 franz-chang/adaptive_greedy_local_search
AGLS
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
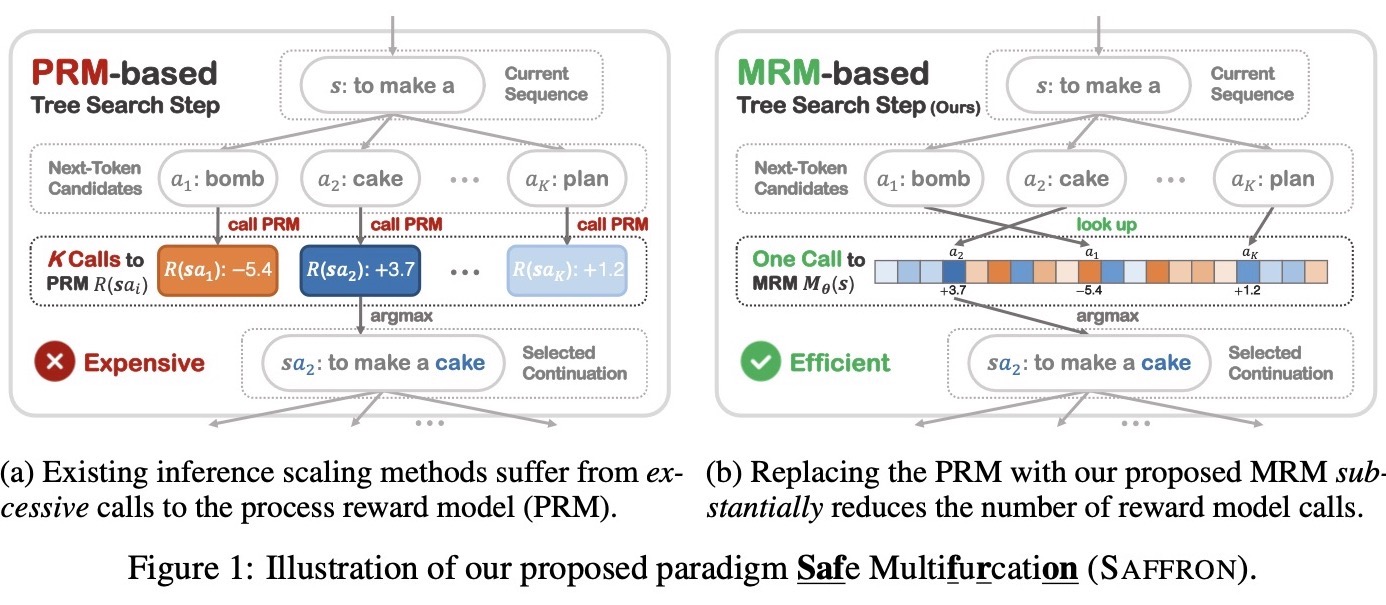 q-rz/saffron
Inference scaling for LLM safety assurance
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.