
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and defenders.

🛡️ AI Security Tool Module
CVE-2026-41096: Windows DNSAPI.dll Heap Overflow (DNS-Mayhem)
Official Security Audit Module for AI Security Tool Ecosystem




🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
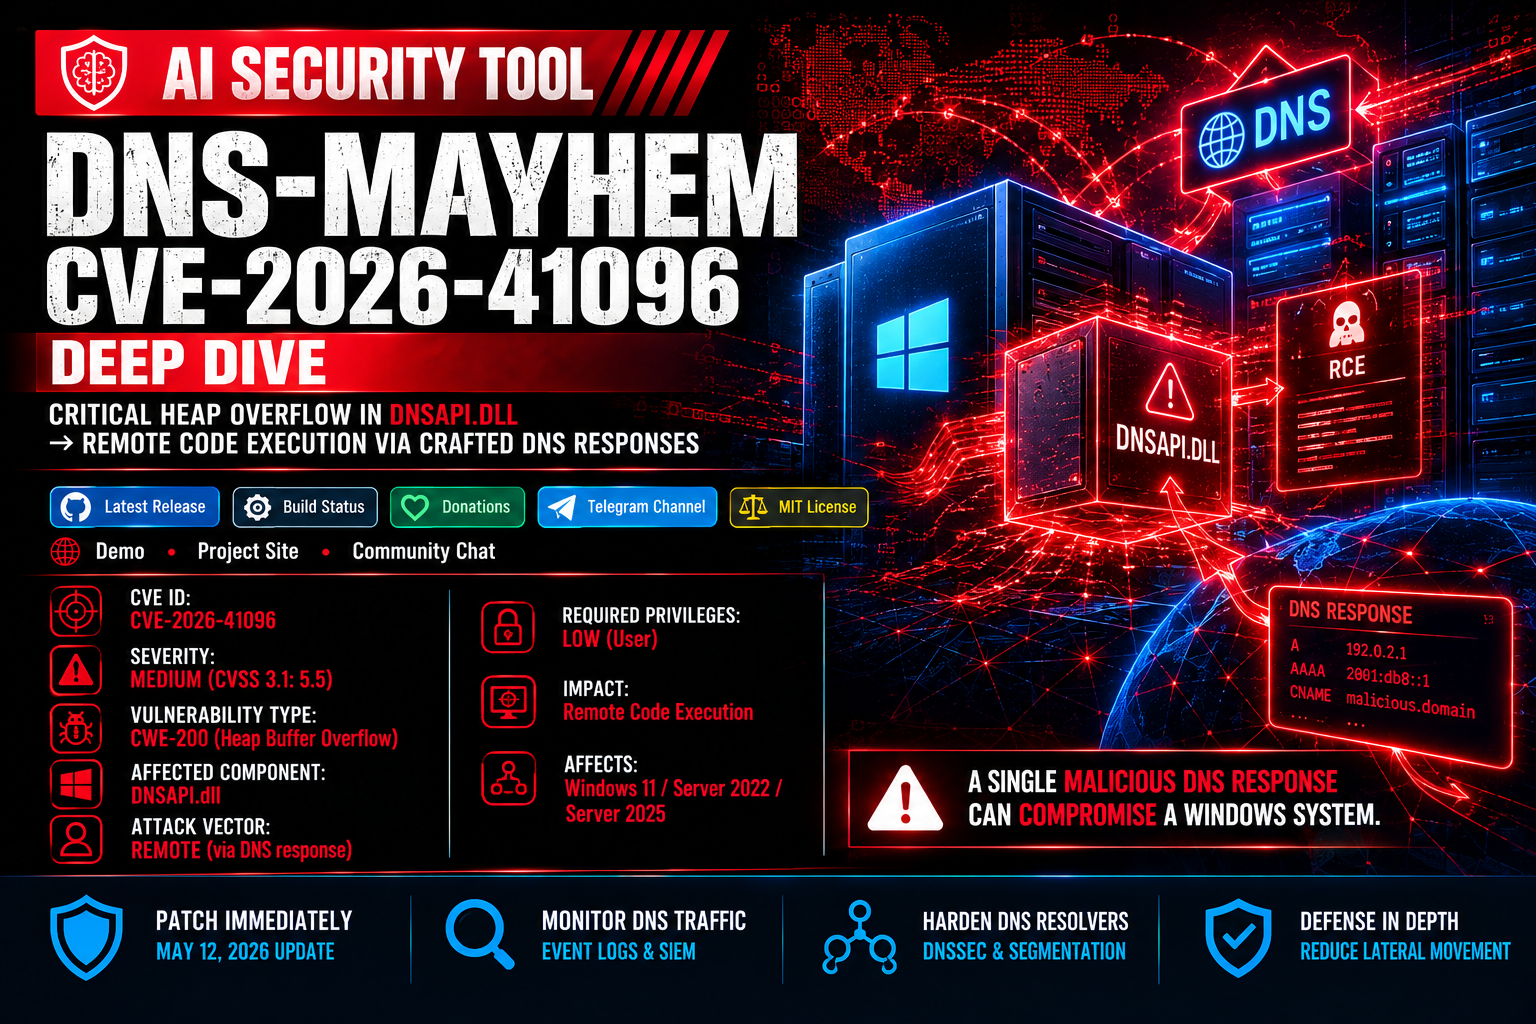
This module provides diagnostic tools and deep technical analysis for CVE-2026-41096, a critical heap-based buffer overflow in DNSAPI.dll, the core Windows system component responsible for parsing incoming DNS responses.
Because background DNS queries are executed continuously across every Windows system, this flaw turns routine network operations into a zero-click Remote Code Execution (RCE) vector. When a target receives a malformed DNS response containing mixed record types (e.g., A/AAAA followed by CNAME or NS), the parser miscalculates the required buffer size, causing a heap write overrun that corrupts adjacent function pointers.
"Control the resolver, control the endpoint."
Because DNS is inherently unauthenticated and executed automatically by the operating system without user intervention, CVE-2026-41096 represents an ideal lateral movement and initial access primitive across enterprise environments.
| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifier | CVE-2026-41096 |
Heap-based Buffer Overflow Vulnerability |
| Severity Rating | Critical (CVSS v3.1: 9.8) | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Vulnerability Type | CWE-122 |
Heap-based Buffer Overflow |
| Affected Component | Windows DNS Client (DNSAPI.dll) |
Universal core DNS resolution library |
| Attack Vector | Network | Unauthenticated remote exploitation via crafted DNS response |
| Privileges Required | None | Zero user interaction or authentication required |
graph TD
    A[Malicious Actor / Rogue DNS] -->|Send Crafted DNS Response| B[Target Endpoint DNSAPI.dll]
    B -->|Size Miscalculation in Answer Parser| C[Trigger Heap Overflow]
    C -->|Corrupt Function Pointer in Heap| D[Hijack Execution Flow]
    D -->|Execute Arbitrary Shellcode| E[Full System Endpoint Compromise]
#include <winsock2.h> #include <windows.h>#pragma pack(push,1) typedef struct { BYTE name[255]; } DNS_RESPONSE;
typedef struct { DWORD dwCallbackPtr; /* attacker-controlled function pointer / DWORD dwDataSize; / size of shellcode payload */ } DNS_API_DATA; #pragma pack(pop)
void __declspec(naked) exploit_dns_response(void) { /* 1. Build malformed A record payload */ DNS_RESPONSE *ans = malloc(sizeof(DNS_RESPONSE)); memcpy(ans, "\xC0\x00", 2);
/* 2. Boundary miscalculation trigger */ DWORD dwSize = 4; DWORD dwPayload = 0x100 + dwSize; /* 3. Overwrite callback pointer */ DNS_API_DATA *dnsApiData = malloc(sizeof(DNS_API_DATA)); dnsApiData->dwCallbackPtr = (DWORD)&exploited_code;
}
Splunk Enterprise Query:
stream_dns
| spath "query_type{}"
| eval qtype=mvjoin('query_type{}', ",")
| search protocol_stack="ip:tcp:dns"
| where bytes_out > 65000
| search qtype IN ("A","AAAA","SIG","KEY","RRSIG","TKEY")
| stats count, values(qtype) AS qtypes, max(bytes_out) AS max_bytes_out, values(query) AS queries, values(src_ip) AS src_ips, values(dest_ip) AS dest_ips by flow_id
| where count >= 1
| sort - max_bytes_out
Microsoft Sentinel Query:
CommonSecurityLog
| where DeviceVendor =~ "Microsoft" or DeviceProduct has "DNS"
| where Protocol =~ "tcp"
| where DestinationPort == 53
| where SentBytes > 65000 or ReceivedBytes > 65000
| summarize Events = count(), MaxBytes = max(max_of(SentBytes, ReceivedBytes)), SrcIPs = make_set(SourceIP, 10), DstIPs = make_set(DestinationIP, 10) by bin(TimeGenerated, 5m)
| where Events > 0