 fr0gger/iatelligence
IATelligence ist ein Python-Skript, das den IAT einer PE-Datei extrahiert und GPT anfragt, um weitere Informationen über die API und die damit verbundene ATT&CK-Matrix zu erhalten.

IATelligence ist ein Python-Skript, das die Import Address Table (IAT) aus einer PE-Datei extrahiert und das GPT-3-Modell von OpenAI verwendet, um Details zu jeder von der Datei importierten Windows-API bereitzustellen. Das Skript sucht außerdem nach verwandten MITRE ATT&CK-Techniken und erklärt, wie die API potenziell von Angreifern verwendet werden könnte.
Es zeigt auch die Hashes der Datei an und schätzt die Kosten der GPT-3-Anfragen. IATelligence ist ein Proof of Concept für die Verwendung von GPT-3 zur Malware-Analyse und zur schnellen Bewertung des Verhaltens einer Malware anhand ihrer IAT.
Im Folgenden finden Sie ein kurzes Beispiel für das Ergebnis. Beachten Sie, dass die Anfrage je nach Größe der IAT länger dauern kann.
Um dieses Tool auszuführen, benötigen Sie Zugriff auf die OpenAI-API. Anschließend müssen Sie das Skript ändern, um Ihren eigenen API-Schlüssel hinzuzufügen.
# Authenticate with the OpenAI API
openai.api_key = ""
Sie müssen außerdem die Abhängigkeiten installieren.
pip install -r requirements.txt
Um das Tool auszuführen, geben Sie einfach eine PE-Datei als Argument für das Skript an.
python iatelligence.py sample.exe
Das Skript berechnet außerdem die Hashes sowie die geschätzten Kosten der Anfrage.
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
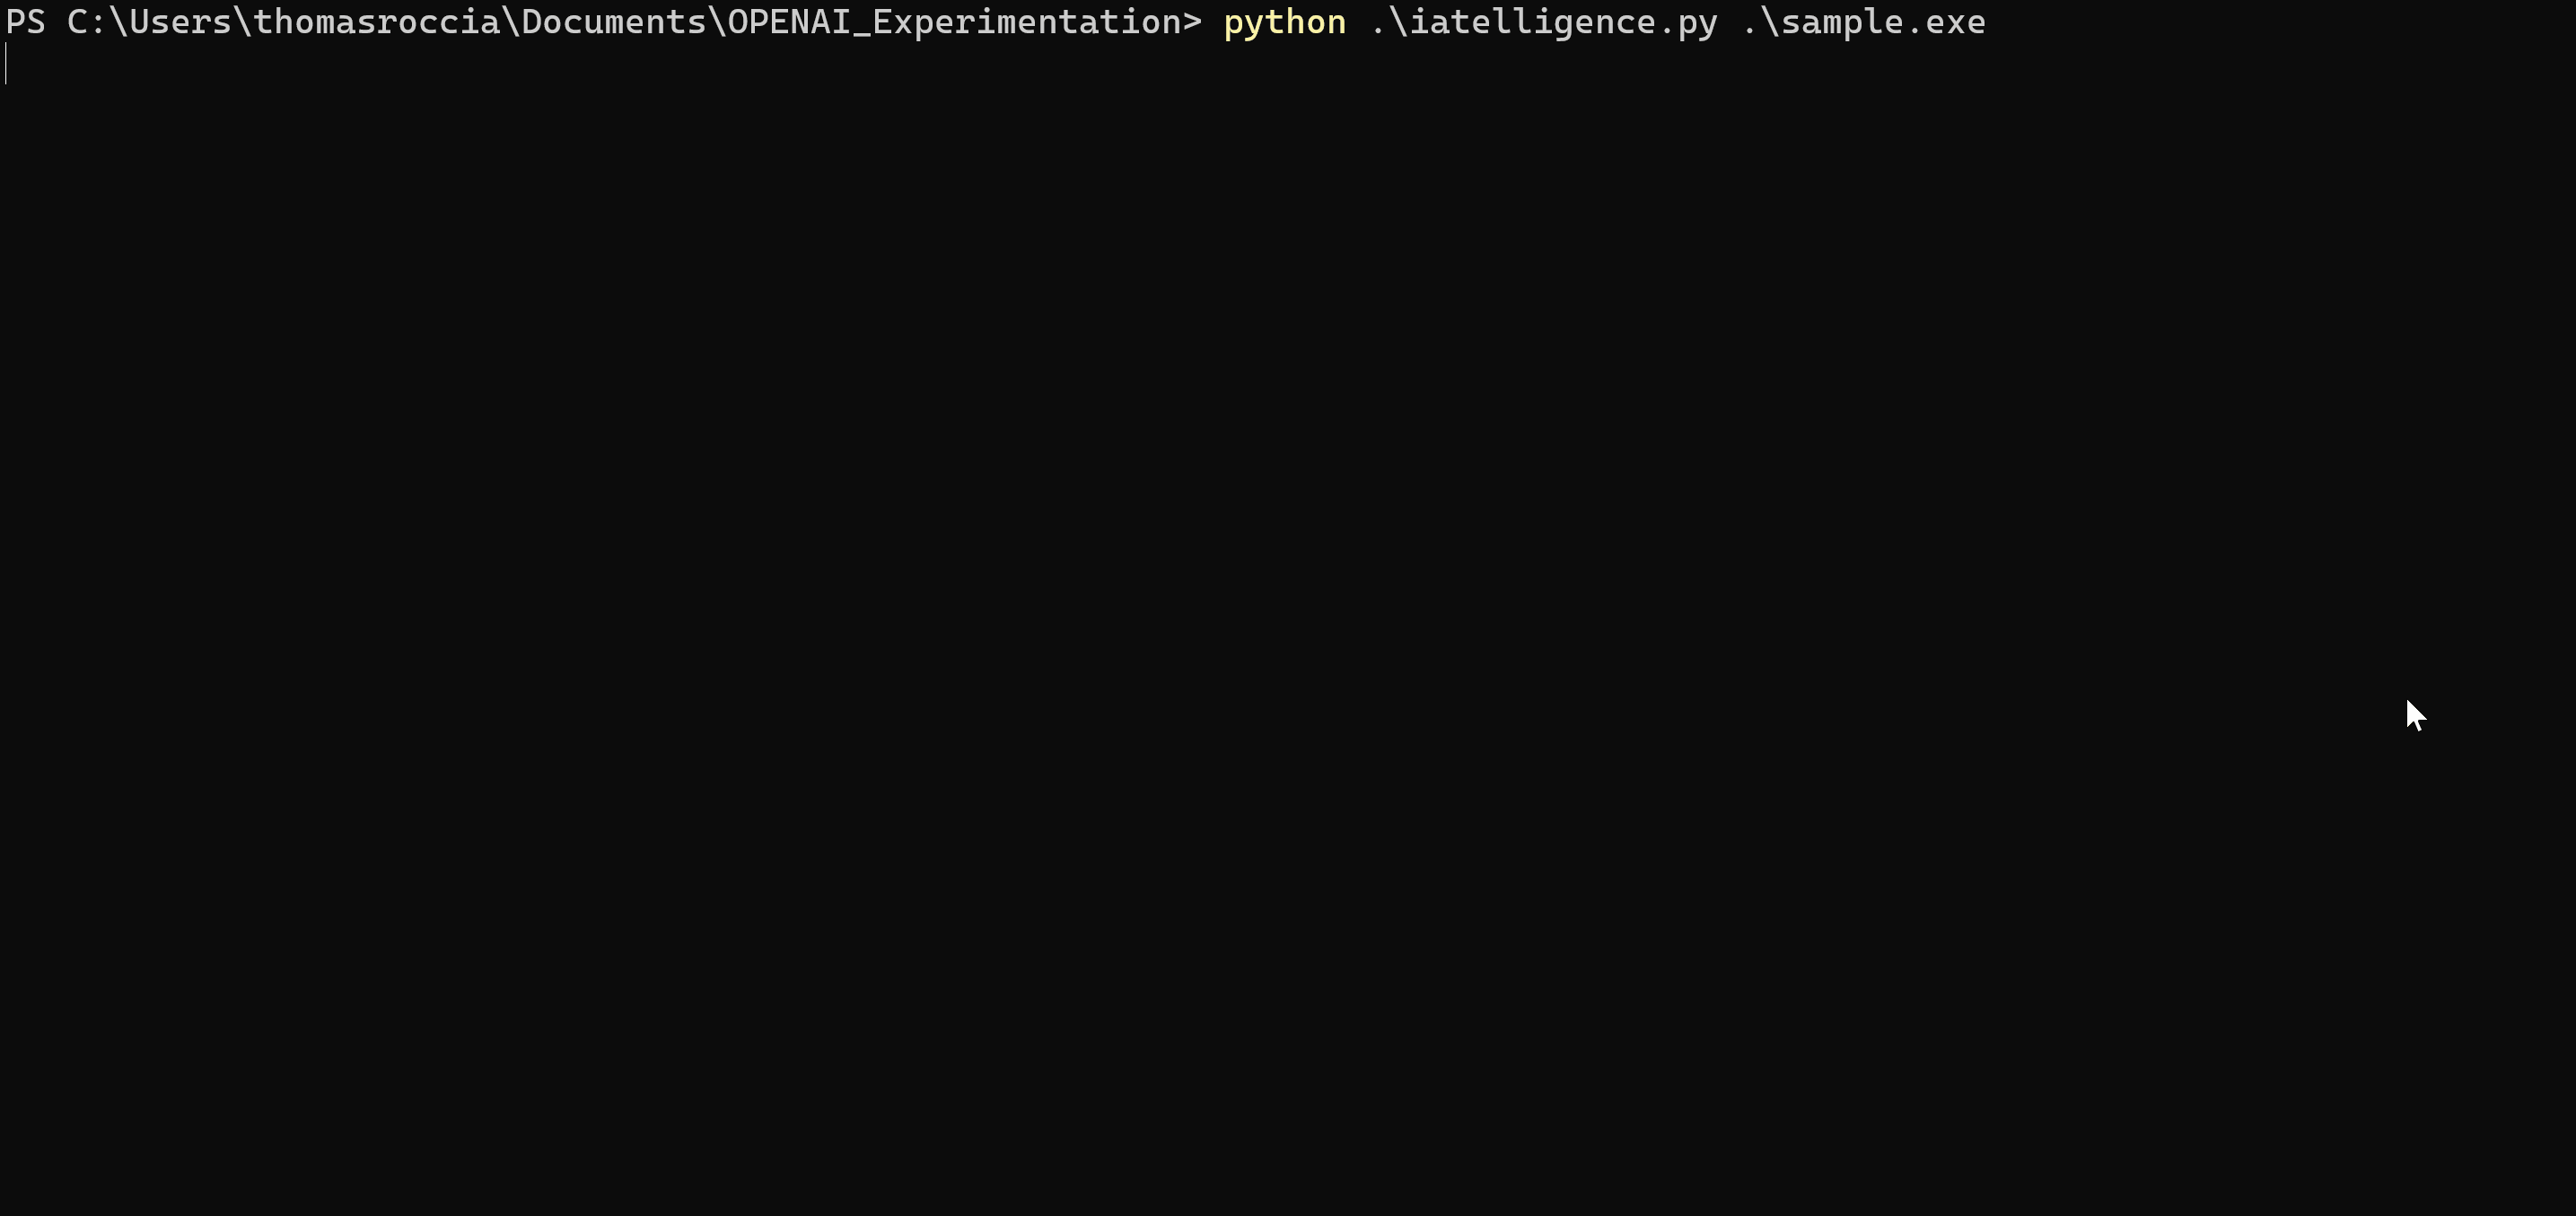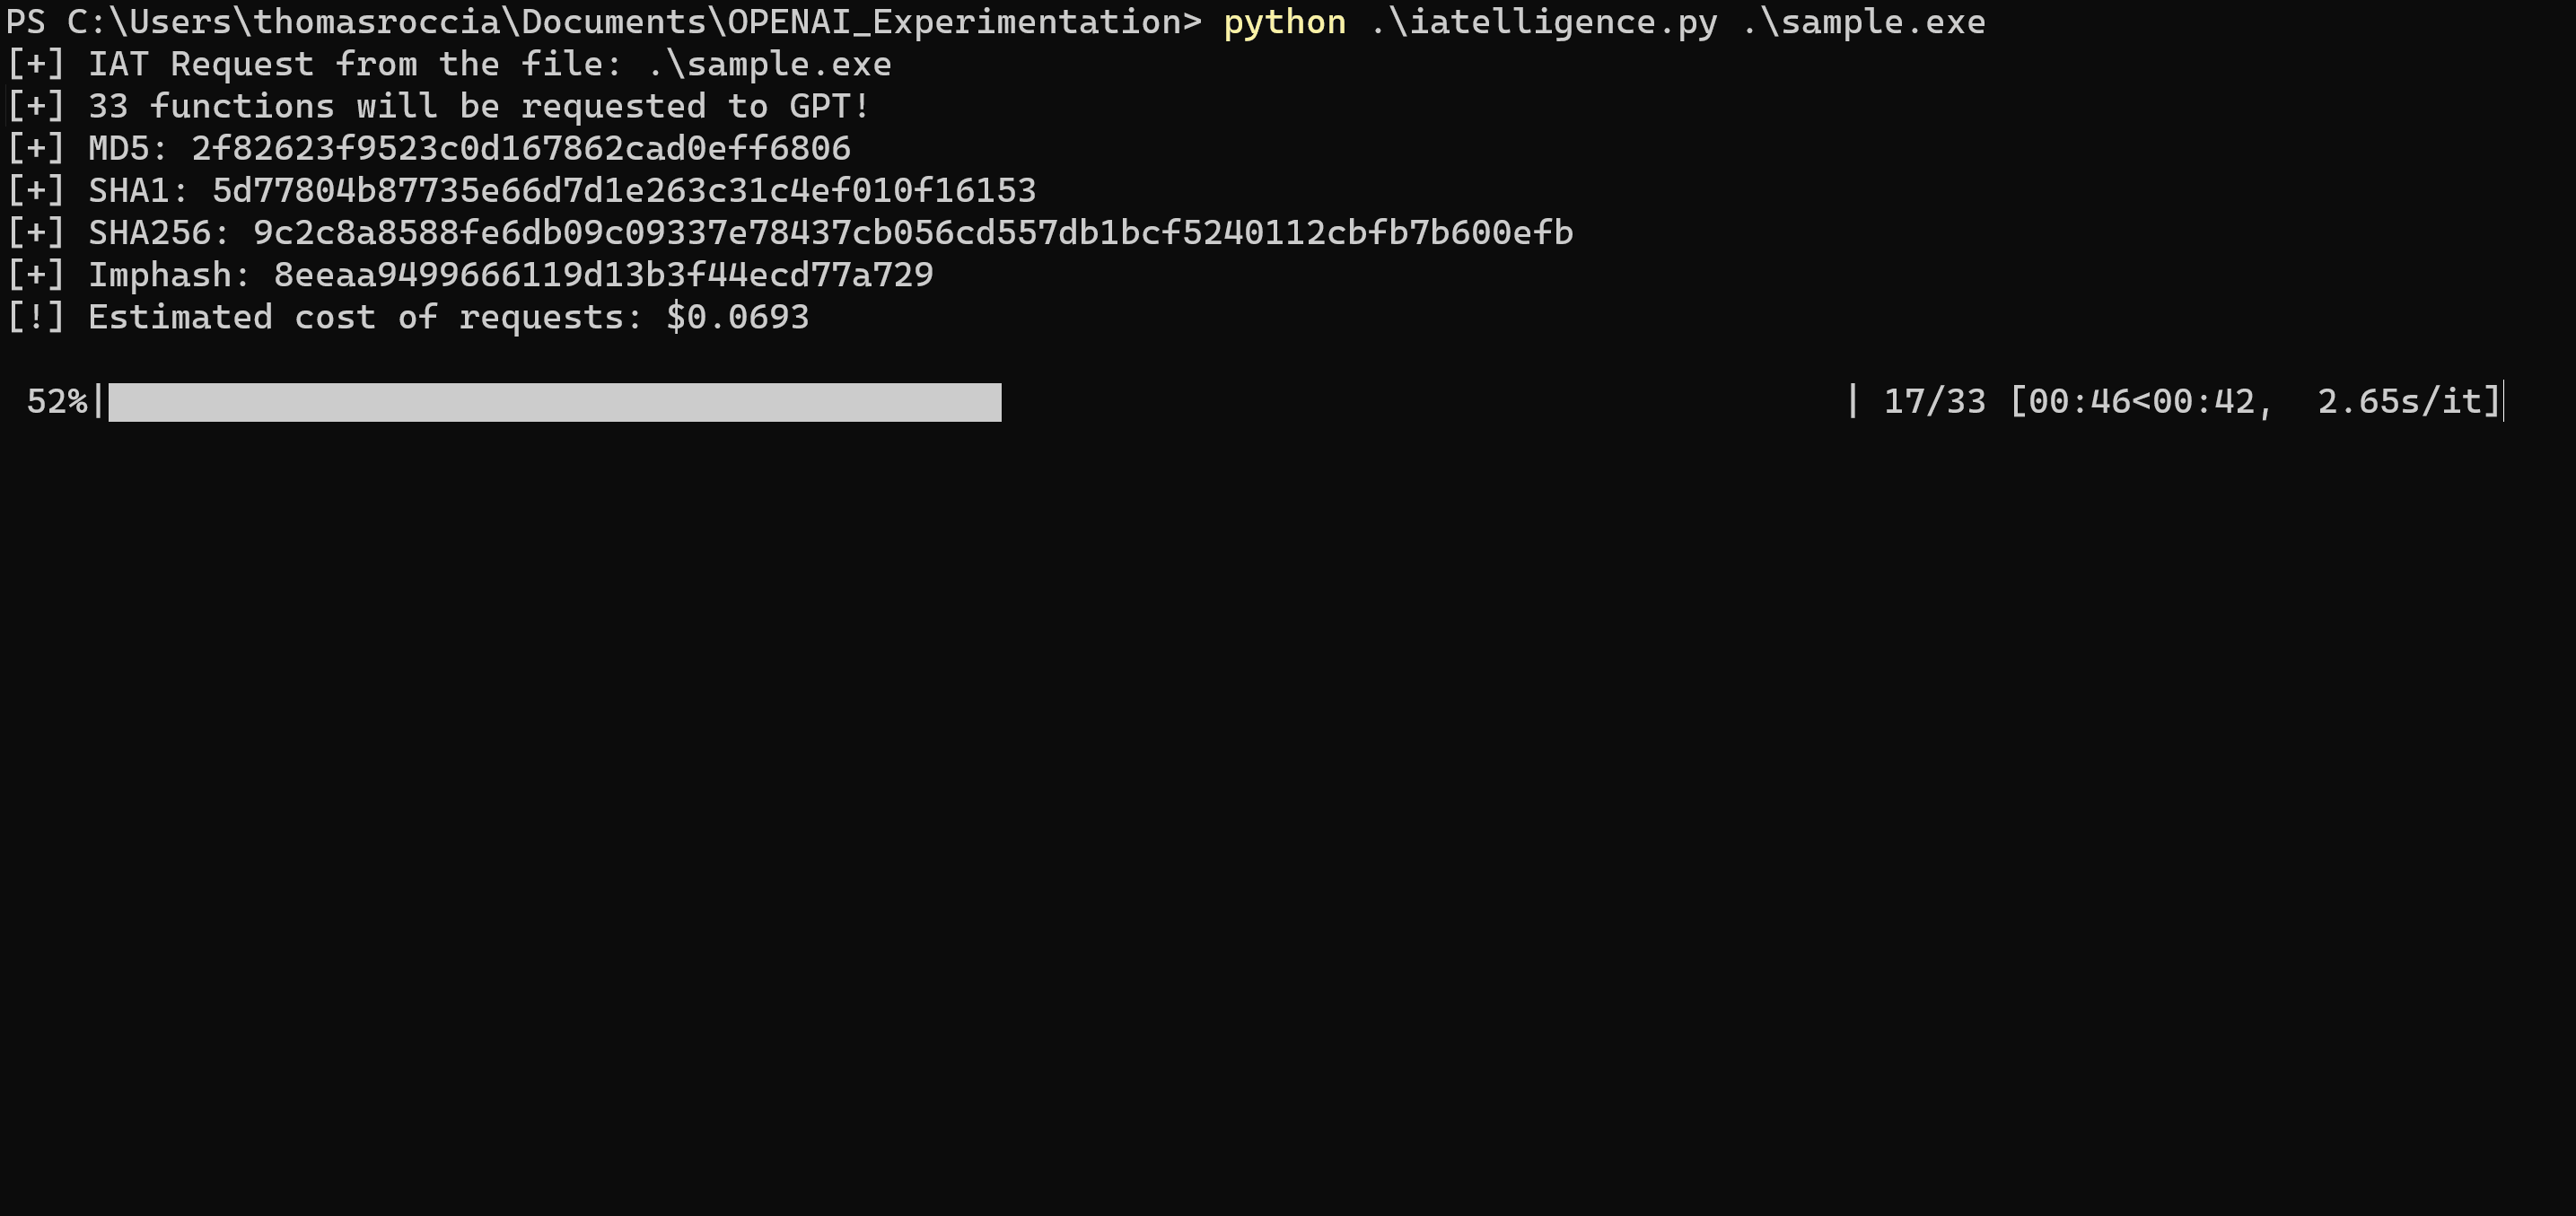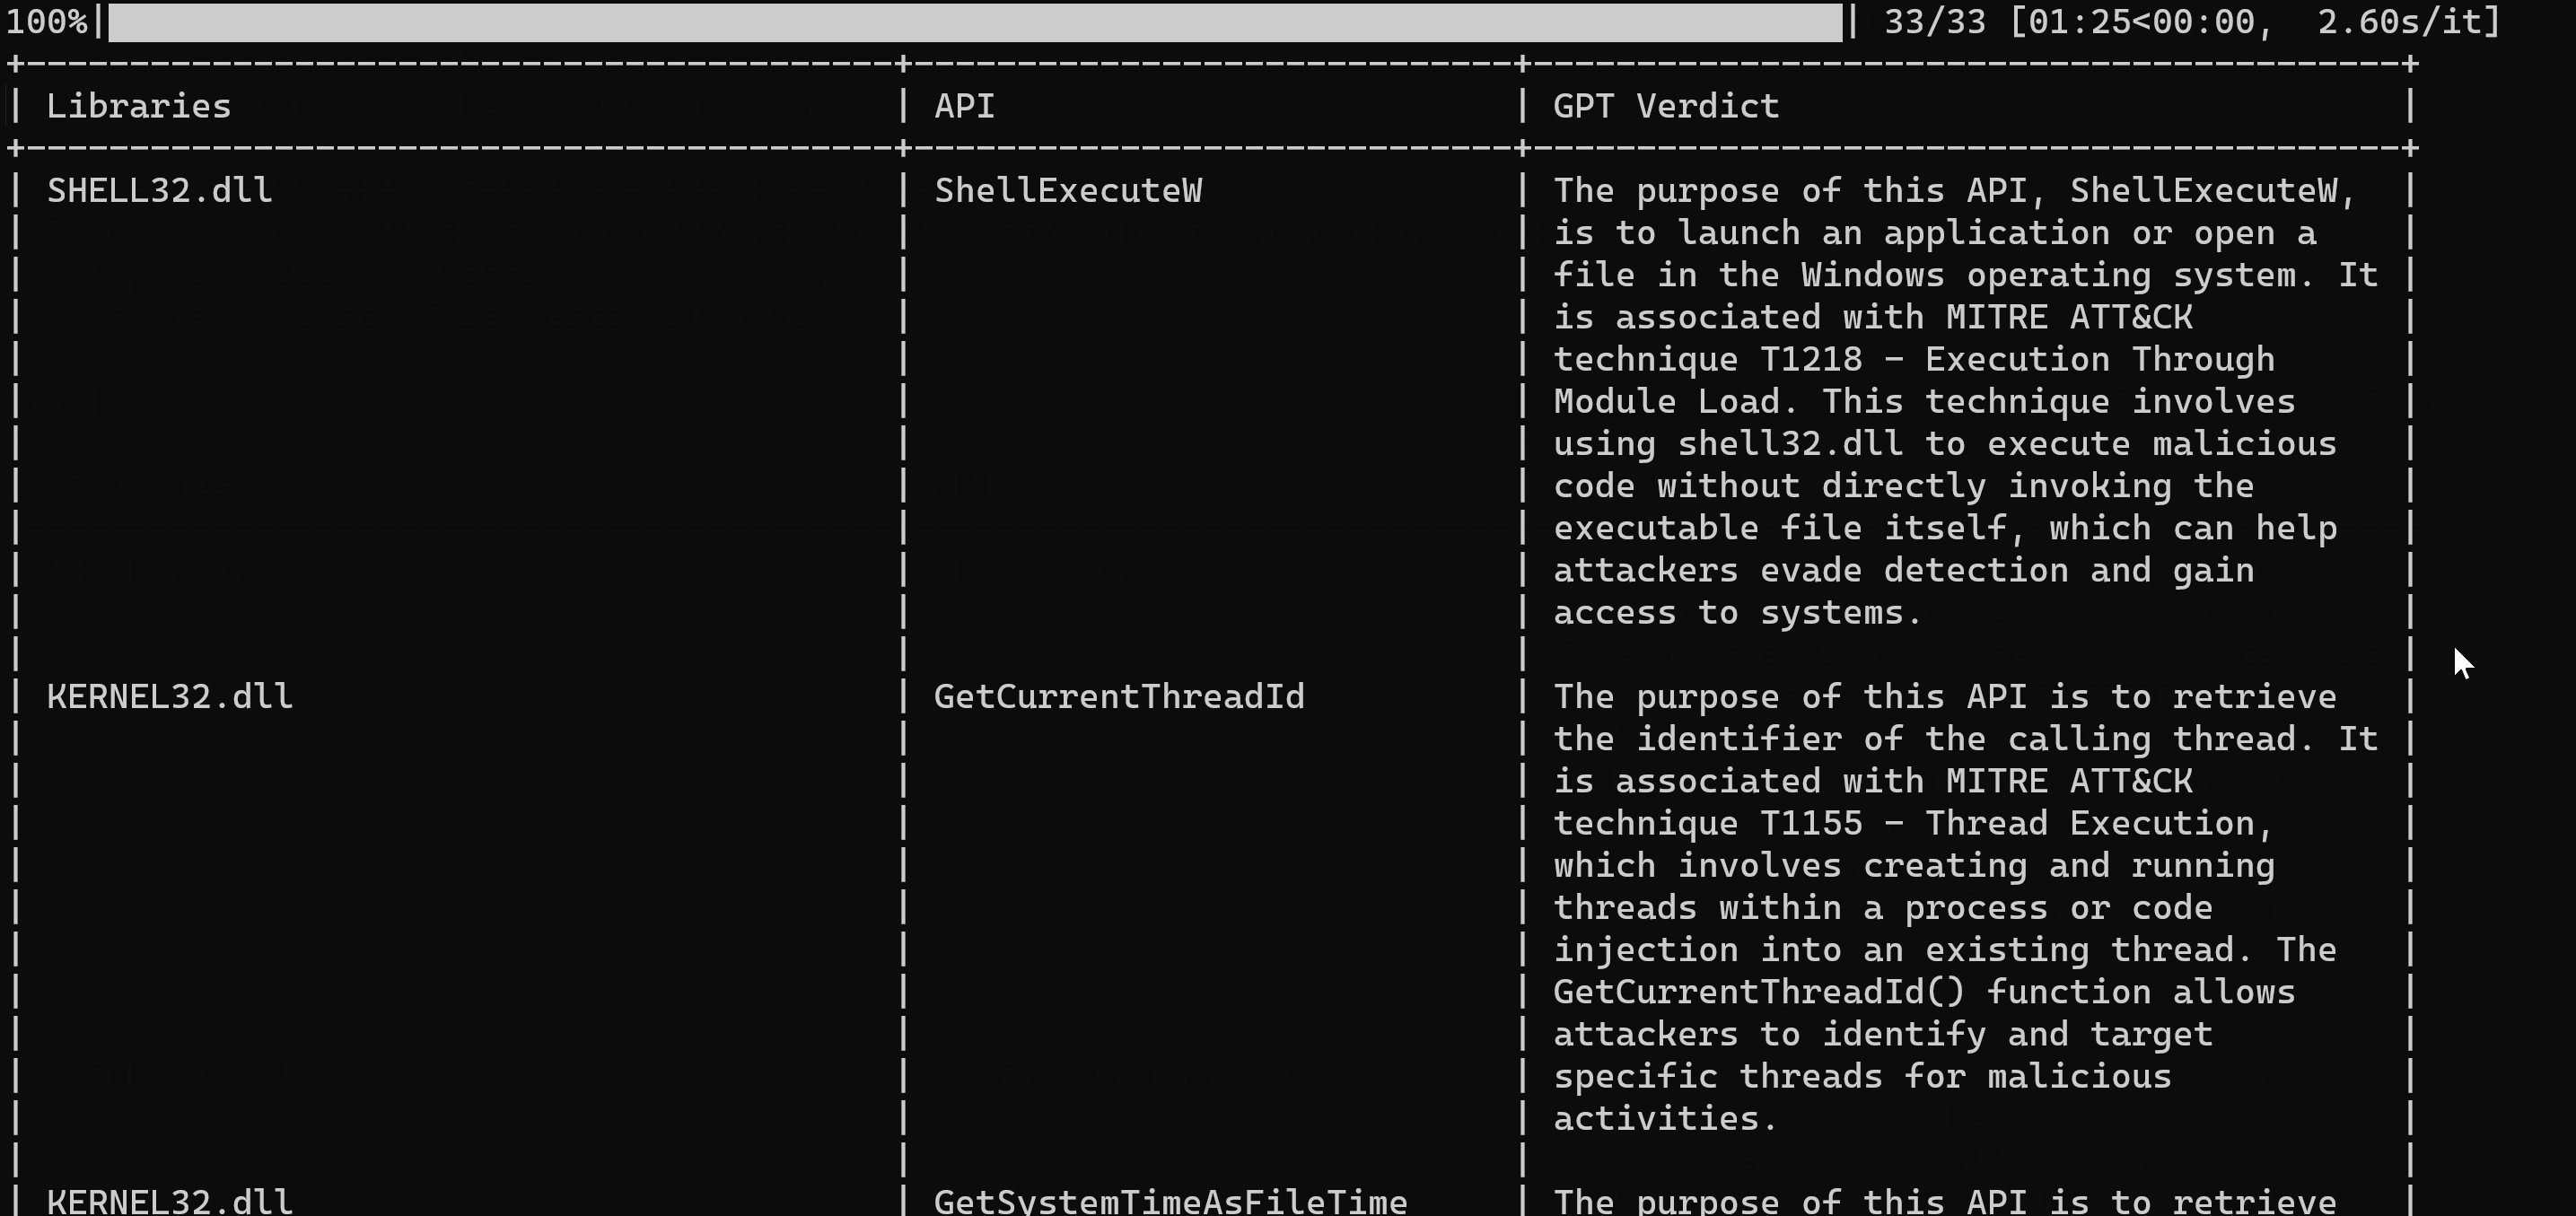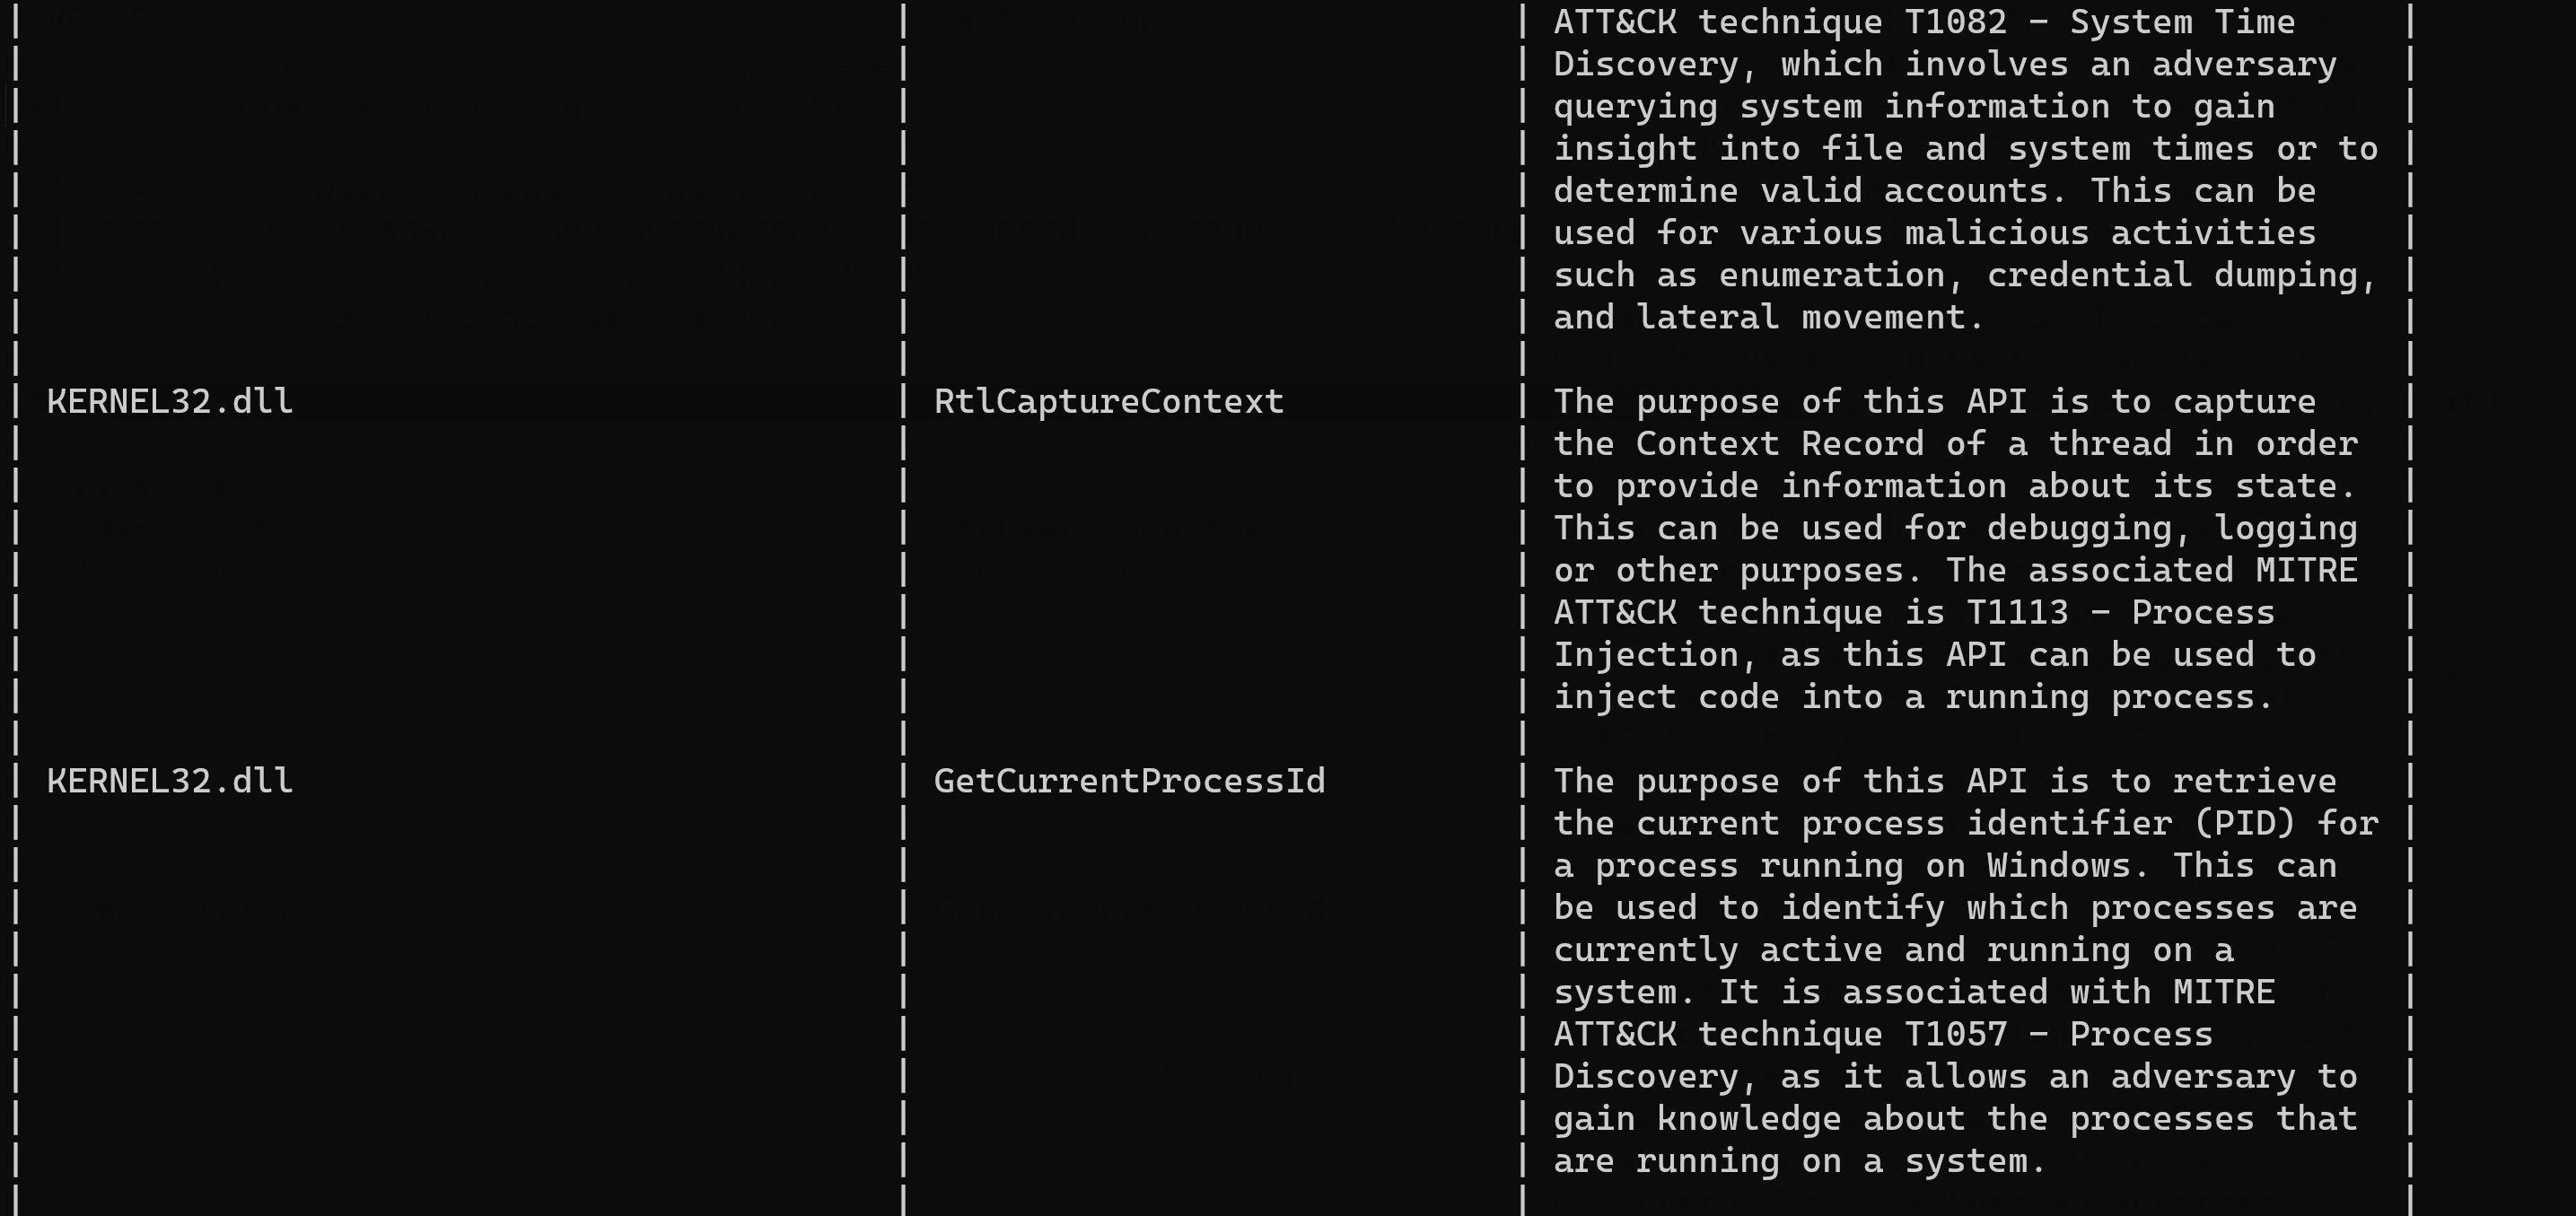
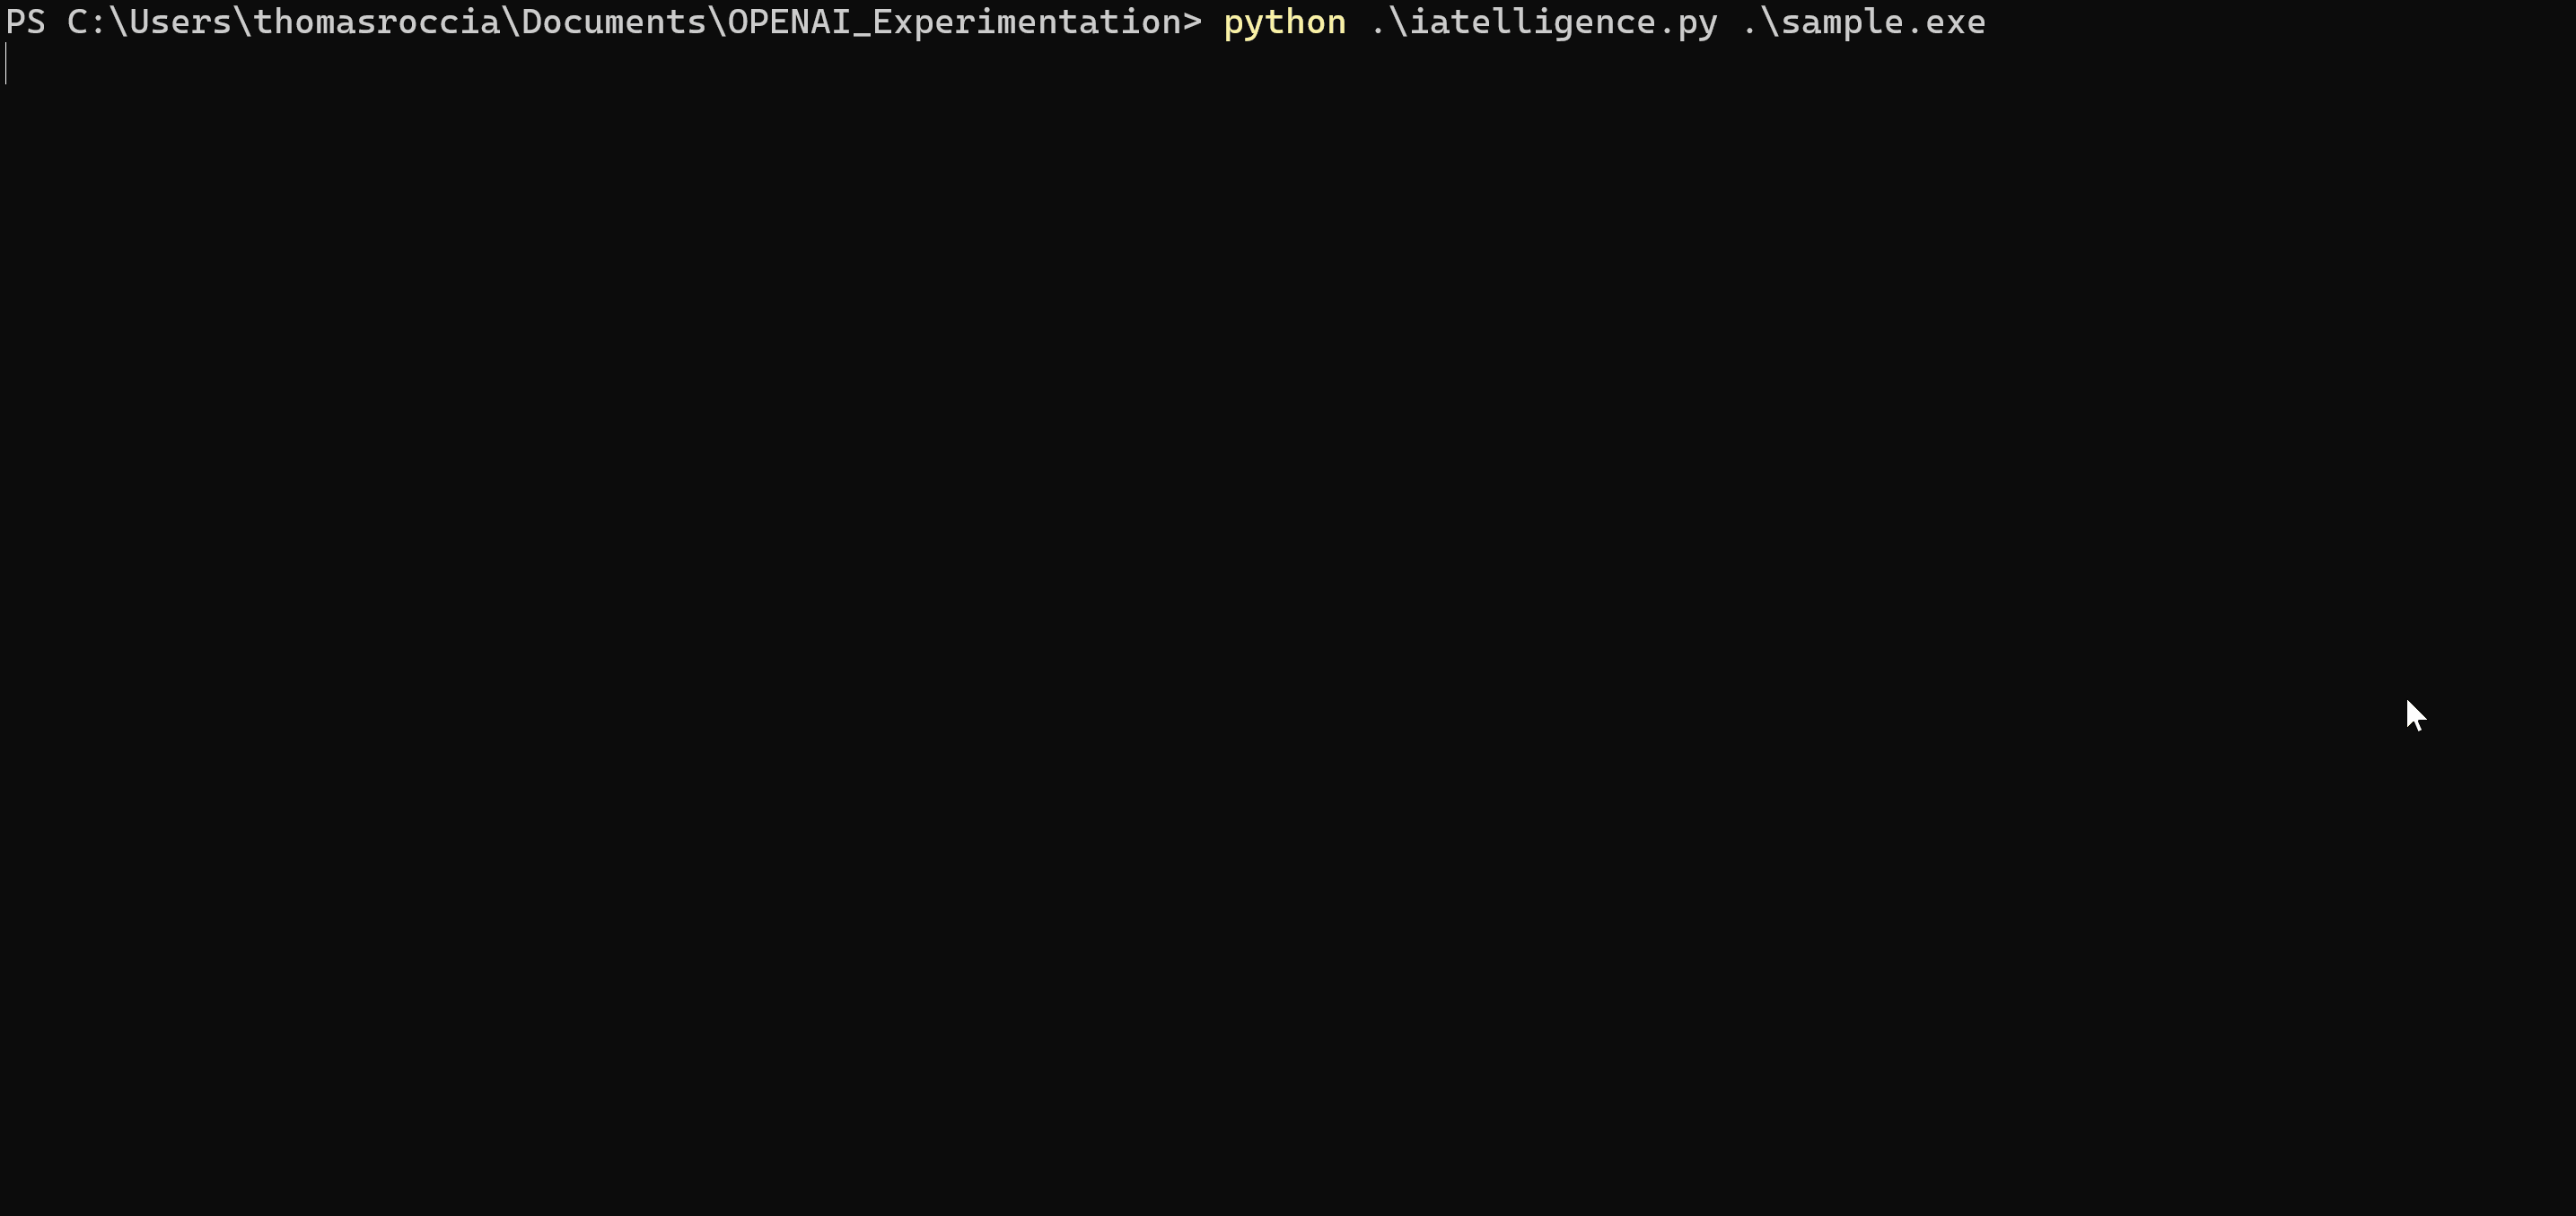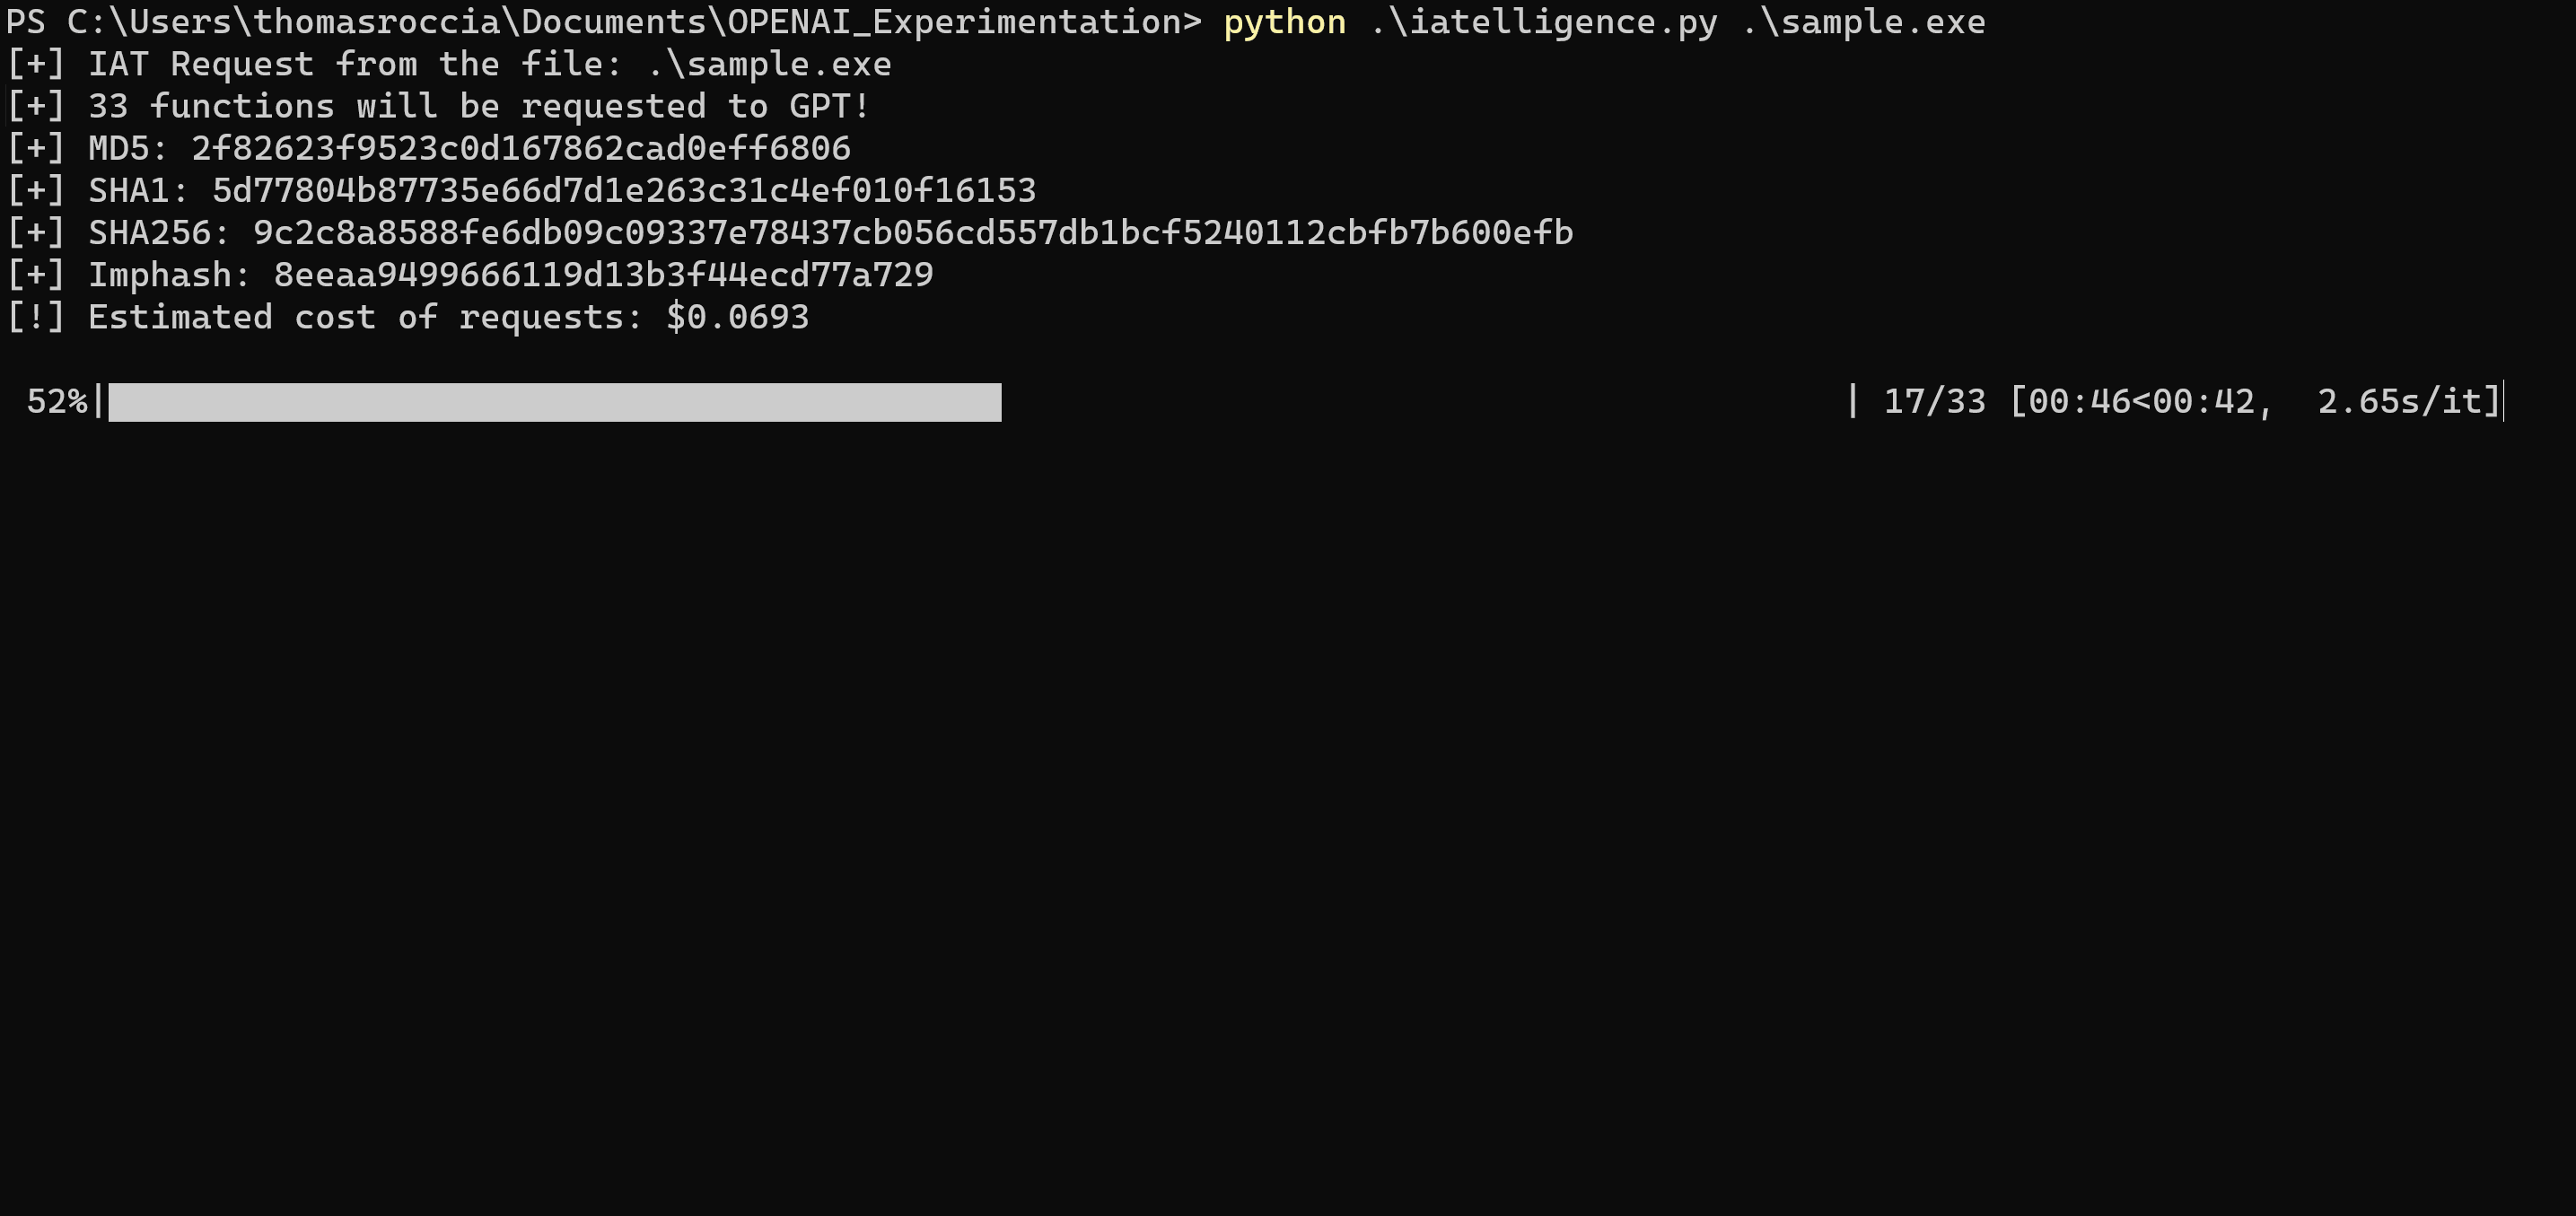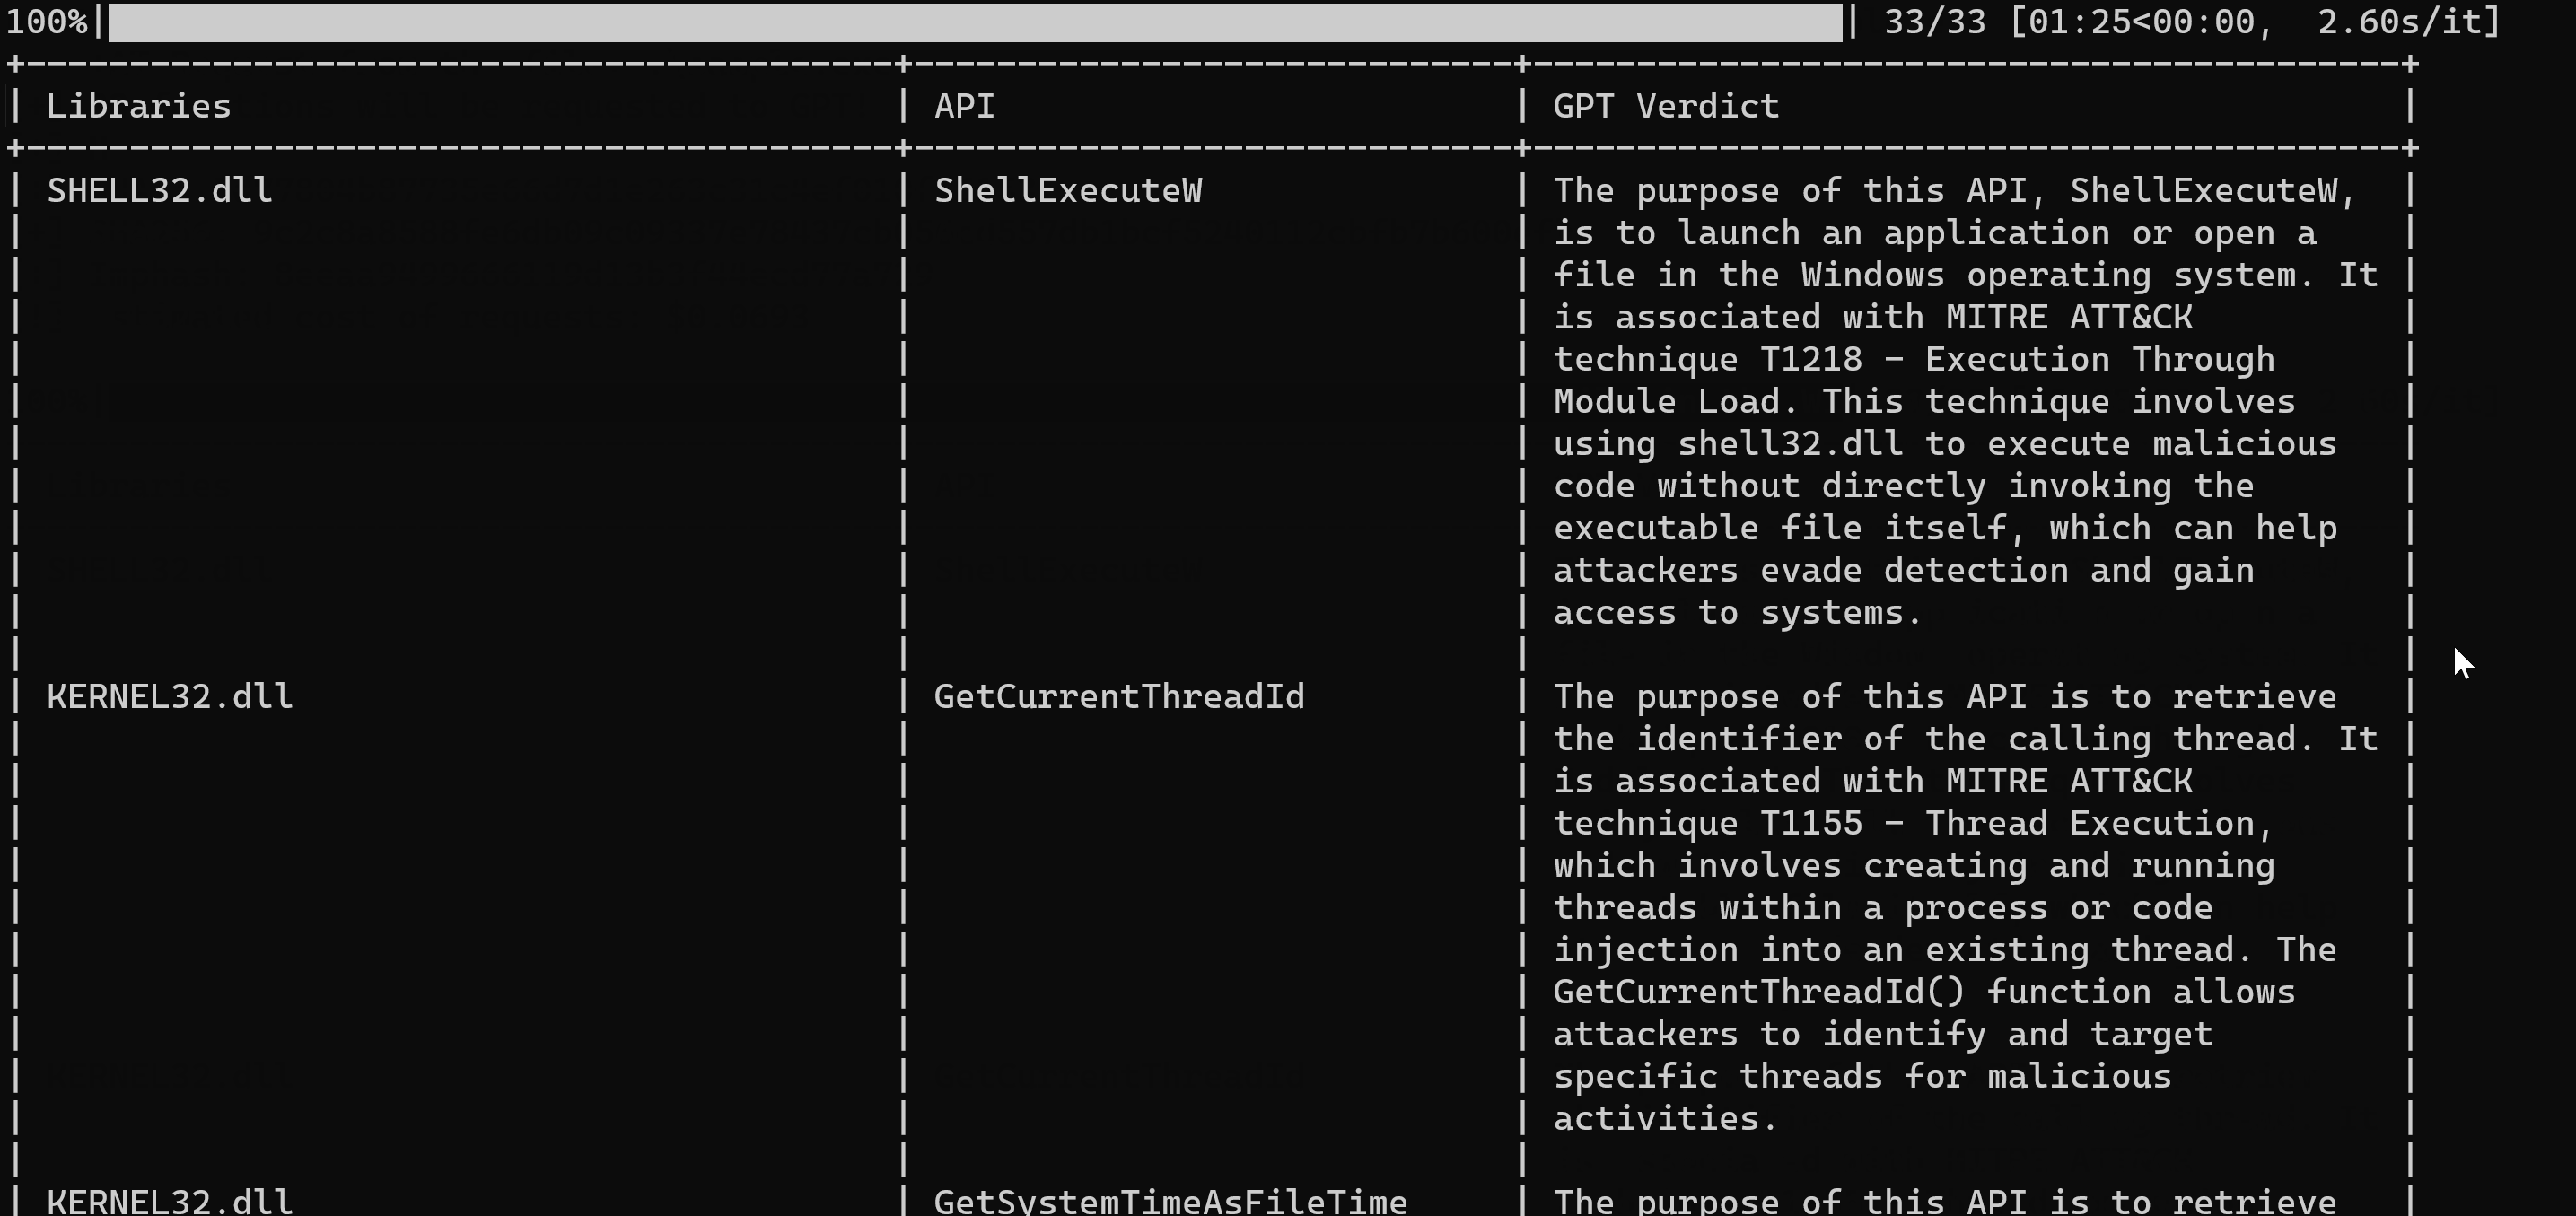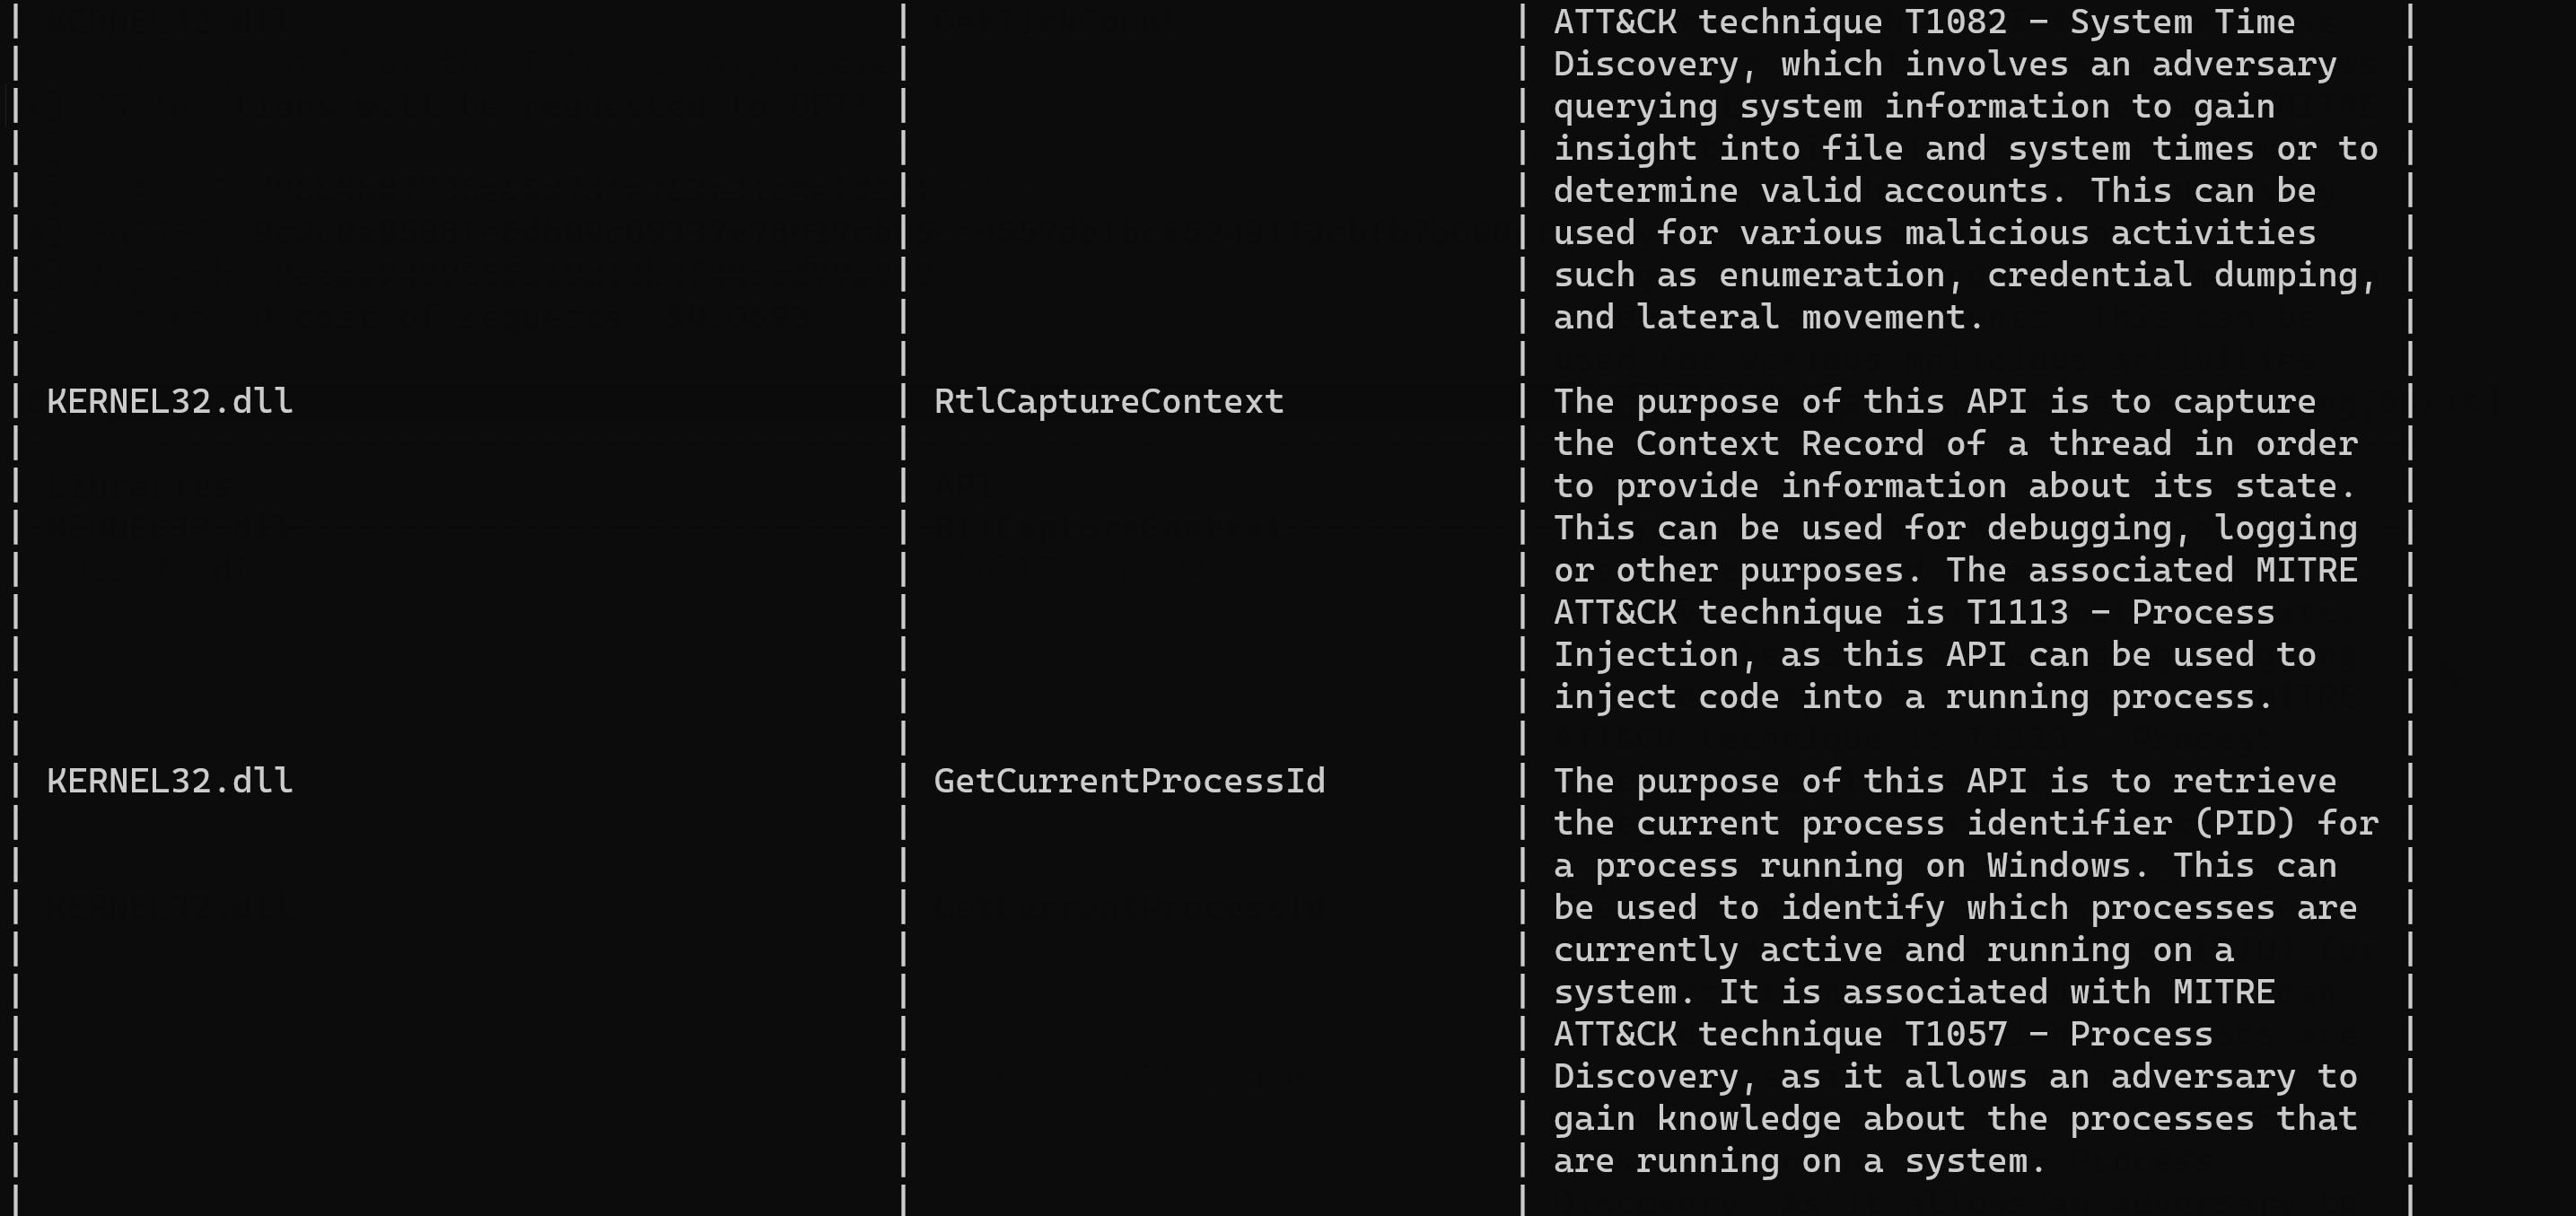
Das Ergebnis kann in einer Tabelle dargestellt werden. Nachfolgend ein gekürzter Auszug.
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
